

Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
Des sources sélectionnées à une fiche d’outil Dépôts, flux, communautés et index passent par la sélection, la classification, l’enrichissement et la traduction pour former une fiche d’outil illustrative. ISC License Copyright (c) 2026 Lucide Icons and Contributors Permission to use, copy, modify, and/or distribute this software for any purpose with or without fee is hereby granted, provided that the above copyright notice and this permission notice appear in all copies. THE SOFTWARE IS PROVIDED "AS IS" AND THE AUTHOR DISCLAIMS ALL WARRANTIES WITH REGARD TO THIS SOFTWARE INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS. IN NO EVENT SHALL THE AUTHOR BE LIABLE FOR ANY SPECIAL, DIRECT, INDIRECT, OR CONSEQUENTIAL DAMAGES OR ANY DAMAGES WHATSOEVER RESULTING FROM LOSS OF USE, DATA OR PROFITS, WHETHER IN AN ACTION OF CONTRACT, NEGLIGENCE OR OTHER TORTIOUS ACTION, ARISING OUT OF OR IN CONNECTION WITH THE USE OR PERFORMANCE OF THIS SOFTWARE. --- The following Lucide icons are derived from the Feather project: airplay, alert-circle, alert-octagon, alert-triangle, aperture, arrow-down-circle, arrow-down-left, arrow-down-right, arrow-down, arrow-left-circle, arrow-left, arrow-right-circle, arrow-right, arrow-up-circle, arrow-up-left, arrow-up-right, arrow-up, at-sign, calendar, cast, check, chevron-down, chevron-left, chevron-right, chevron-up, chevrons-down, chevrons-left, chevrons-right, chevrons-up, circle, clipboard, clock, code, columns, command, compass, corner-down-left, corner-down-right, corner-left-down, corner-left-up, corner-right-down, corner-right-up, corner-up-left, corner-up-right, crosshair, database, divide-circle, divide-square, dollar-sign, download, external-link, feather, frown, hash, headphones, help-circle, info, italic, key, layout, life-buoy, link-2, link, loader, lock, log-in, log-out, maximize, meh, minimize, minimize-2, minus-circle, minus-square, minus, monitor, moon, more-horizontal, more-vertical, move, music, navigation-2, navigation, octagon, pause-circle, percent, plus-circle, plus-square, plus, power, radio, rss, search, server, share, shopping-bag, sidebar, smartphone, smile, square, table-2, tablet, target, terminal, trash-2, trash, triangle, tv, type, upload, x-circle, x-octagon, x-square, x, zoom-in, zoom-out The MIT License (MIT) (for the icons listed above) Copyright (c) 2013-present Cole Bemis Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software. THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
Dépôts
GitHub & GitLab
Veille sécurité
Blogs, RSS et Atom
Communautés
Reddit, X et contributions
Index sélectionnés
Listes et tendances
Trier et sélectionner
Classification
Enrichissement
Traduction
Outil et dépôt fictifs. Description, catégories, étoiles, forks et vues sont des exemples, pas des données réelles ou vérifiées. Outil et dépôt fictifs. Description, catégories, étoiles, forks et vues sont des exemples, pas des données réelles ou vérifiées. {"fictional":true,"name":"Tool","version":"1.0.1","repository":"owner/tool","live_metrics":false,"example_metrics":{"stars":1200,"forks":128,"views":8600}}
Outil
v1.0.1 owner/tool
Découvrez les actifs et
vérifiez les en-têtes HTTP.
Reconnaissance
Sécurité web
1,200 étoiles — Exemple fictif1.2k 128 forks — Exemple fictif128 8,600 vues — Exemple fictif8.6k

Outils

ToutSécurité AndroidAuthentification et AutorisationSécurité de l'Infrastructure CloudOutils DéfensifsCriminalistique DisqueSécurité des Systèmes EmbarquésUtilitaires GénérauxGestion des Indicateurs de Compromission (IOC)OSINT (Renseignement de Sources Ouvertes)Sniffing et Analyse de PaquetsCassage de Mots de PasseFrameworks de Tests d'IntrusionOutils de PhishingEscalade de PrivilègesReconnaissanceAnalyse StatiqueScanners de VulnérabilitésScanners de Vulnérabilités WebAudit Wi-FiSécurité BluetoothSécurité des ConteneursAnalyse Dynamique (Sandboxing)Outils de Chiffrement/DéchiffrementFrameworks d'ExploitationGestion des IdentitésSécurité iOSSécurité IoTCriminalistique MémoireCartographie RéseauOSINT pour l'Ingénierie SocialeAttaques de Mots de PasseGénération de PayloadsMécanismes de PersistanceScan de PortsAnalyse Statique de Code (SAST)Flux et Agrégateurs de MenacesAnalyse des VulnérabilitésProxies Web et InterceptionAnalyse de CodeÉnumération DNS et Sous-domaineAnalyse Dynamique de Code (DAST)ExploitationAnalyse de HachageÉvasion IDS/IPSOutils d'ImpersonationMouvement LatéralPentesting d'Applications MobilesCriminalistique RéseauRétro-ingénierieOutils RFID/NFCSécurité SCADA/ICSScripting et AutomatisationSécurité ServerlessShellcodeExploitation d'Applications WebTests de Sécurité des APIAudit de ConfigurationExfiltration de DonnéesDébogueursAnalyse ForensiqueCollecte d'InformationsCriminalistique MobileContrôle d'Accès RéseauPost-ExploitationVirtualisation de SécuritéHameçonnageContournement de WAFSécurité WebFuzzingSécurité RéseauStéganographieSécurité Sans FilRécupération de DonnéesAnalyse de MalwareCriminalistique NumériqueHacking MatérielCryptographieCTFTests d'IntrusionSécurité CloudDevSecOpsSécurité MobileProtection de la Vie PrivéeCommandement et ContrôleIngénierie SocialeSécurité MatérielleUtilitaires et FrameworksSécurité Matériel et IoTDétection de SecretsAnalyse de BinairesRenseignement sur les MenacesGestion des Identités et des Accès (IAM)Sécurité de la Chaîne LogistiqueAuthentificationApprentissage AutomatiqueDétection d'IntrusionArticles et RechercheMauvaise ConfigurationÉnumération de Sous-domainesCollecte d'EmailsApprentissage et ÉducationRétro-Ingénierie Assistée par IAFuzzing DNSRed TeamingRéponse aux IncidentsCrawlerRessources OrganiséesOutil d'Accès à DistanceGénération de ShellcodeDéveloppement de Charges UtilesCheval de Troie d'Accès à DistanceSécurité des APIAnti-BotUsurpation d'Empreinte NumériqueContournement de CAPTCHASécurité des EmailsAnalyse DNSIngénierie du ChaosParcours et CoursÉvasion de ConteneurSécurité de l'IASécurité des Bases de DonnéesAnalyse de MicrologicielDétection d'AnomaliesAnalyse de JournauxAttaque AdversarialeExploitation de BinairesLabs et Pratique
Plus récentsPertinencePlus populairesMis à jour récemment
262 résultats
react2shell-scanner preview

react2shell-scanner

GitHubshield-cyber/react2shell-scanner

Scanner pour détecter la présence de CVE-2025-55182 & CVE-2025-66478 sur les services web ciblés.
vulnerability-scannersweb-vulnerability-scannersexploitation+3
1
il y a 11 mois
RscScan-cve-2025-55182 preview

RscScan-cve-2025-55182

GitHubveilvulp/rscscan-cve-2025-55182

RscScan: Scanneur de vulnérabilités professionnel multiplateforme pour les Server Actions de Next.js (CVE-2025-55182). Détecte les failles RCE…

vulnerability-scannersweb-vulnerability-scannersexploitation+3
3il y a 11 mois
BurpAPISecuritySuite preview

BurpAPISecuritySuite

GitHubteycir/burpapisecuritysuite

Extension Burp Suite pour les tests de sécurité des API avec 15 types d'attaques, 108+ payloads, fuzzing intelligent, détection BOLA/IDOR,…

web-vulnerability-scannersvulnerability-analysisweb-application-exploitation+4
75il y a 3 mois
OmniScan preview

OmniScan

GitHubd3ckx1/omniscan

Scanner de vulnérabilités multi-moteur avec les moteurs intégrés Nuclei Lite, Afrog et XRay. Fonctionnalités de découverte d'actifs via FOFA/Shodan,…

osintreconnaissancevulnerability-scanners+6
9il y a 10 mois
burpfox preview

burpfox

GitHubhalilkirazkaya/burpfox

Une extension Burp Suite qui intègre le scanner XSS Dalfox directement dans votre flux de travail.

web-vulnerability-scannersdynamic-analysis-sandboxingvulnerability-analysis+3
23il y a 9 mois
wpx preview

wpx

GitHubgreg-randall/wpx

Scanner de sécurité WordPress asynchrone avec contournement de WAF via un navigateur sans tête. Énumère les plugins, thèmes, utilisateurs et…

reconnaissanceweb-vulnerability-scannersvulnerability-analysis+6
10il y a 7 mois
VulnScan preview

VulnScan

GitHubtorchiachristian/vulnscan

Scanner de vulnérabilités web en Python: injection SQL, XSS , path traversal, en-têtes de sécurité. Crawler, tableau de bord Flask, rapport en PDF.

static-analysisvulnerability-scannersweb-vulnerability-scanners+5
2il y a 3 mois
Log4j_scan_Advance preview

Log4j_scan_Advance

GitHubrk-000/log4j_scan_advance

Un scanner entièrement automatisé, précis et complet pour trouver la RCE log4j CVE-2021-44228
vulnerability-scannersweb-vulnerability-scannersexploitation+3
1il y a 4 ans
GETROBARB preview

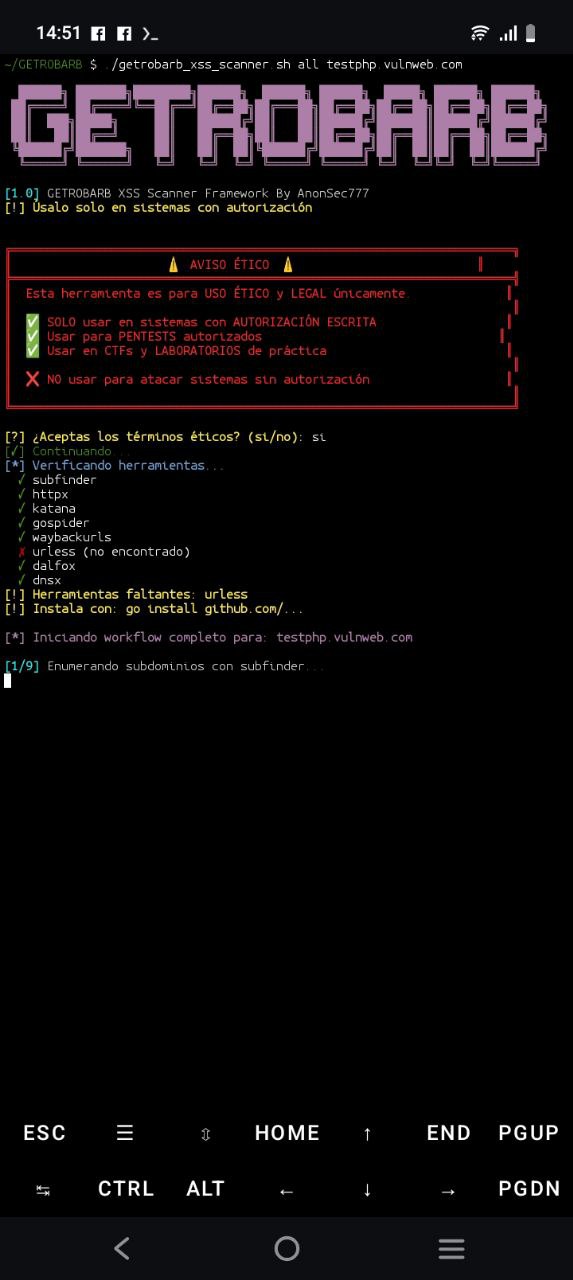
GETROBARB

GitHubhackingteamoficial/getrobarb

Cadre automatisé de reconnaissance et de détection XSS intégrant subfinder, httpx, katana, gospider, waybackurls et dalfox en un pipeline à 9 étapes…
reconnaissanceweb-vulnerability-scannersvulnerability-analysis+7
9il y a 2 mois
sqlifinder preview

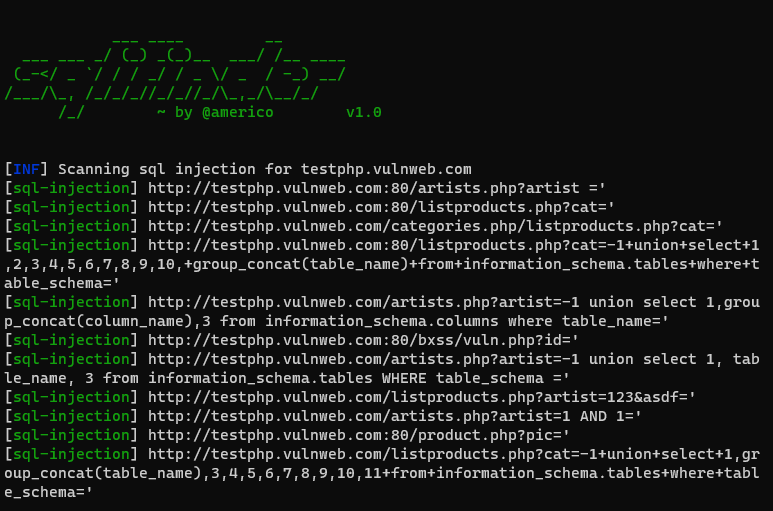
sqlifinder

GitHubamerico/sqlifinder

Scanner de vulnérabilités d'injection SQL réalisé avec Python

vulnerability-scannersweb-vulnerability-scannersweb-security
395il y a 7 mois
EasY_HaCk preview

EasY_HaCk

GitHubsabri-zaki/easy_hack

Hackez le monde avec Termux

password-crackingpenetration-testing-frameworksweb-vulnerability-scanners+4
2.5kil y a 1 an
ffuf preview

ffuf

GitHubffuf/ffuf

Fuzzer web rapide écrit en Go.
reconnaissanceweb-vulnerability-scannersvulnerability-analysis+12
16.5kil y a 1 mois
vulmap preview

vulmap

GitHubzhzyker/vulmap

Scanner de vulnérabilités web et outil d'exploitation avec modes POC/EXP pour des CVE connues dans des applications web telles que Weblogic, Shiro,…

web-vulnerability-scannersvulnerability-analysisexploitation+1
3.5kil y a 4 ans
kaboom preview

kaboom

GitHubleviathan36/kaboom

Un outil pour automatiser les tests d'intrusion

vulnerability-scannersweb-vulnerability-scannersexploit-frameworks+4
382il y a 6 ans
sqlmap preview

sqlmap

GitHubsqlmapproject/sqlmap

Outil automatique d'injection SQL et de prise de contrôle de base de données

penetration-testing-frameworksvulnerability-scannersweb-vulnerability-scanners+12
38.2kil y a 1 jour
zaproxy preview

zaproxy

GitHubzaproxy/zaproxy

Scanner de sécurité d'application web open-source pour la détection automatisée des vulnérabilités, les tests de pénétration manuels et les tests de…

android-securityphishing-toolsvulnerability-scanners+15
15.6kil y a 1 jour
httpx preview

httpx

GitHubprojectdiscovery/httpx

Boîte à outils HTTP rapide et multi-sonde pour la reconnaissance et la collecte d'informations. Sonde TLS, CSP, en-têtes, pile technologique et CDN.…

general-purpose-utilitiesosintreconnaissance+18
10.3kil y a 21h 55m
barrido preview

barrido

GitLabzer1t0/barrido

Outil pour découvrir des chemins dans les applications web.

reconnaissanceweb-vulnerability-scannersinformation-gathering+2
2il y a 3 ans
Précédent1…8910…15Suivant
Des sources sélectionnées à une fiche d’outil Dépôts, flux, communautés et index passent par la sélection, la classification, l’enrichissement et la traduction pour former une fiche d’outil illustrative. ISC License Copyright (c) 2026 Lucide Icons and Contributors Permission to use, copy, modify, and/or distribute this software for any purpose with or without fee is hereby granted, provided that the above copyright notice and this permission notice appear in all copies. THE SOFTWARE IS PROVIDED "AS IS" AND THE AUTHOR DISCLAIMS ALL WARRANTIES WITH REGARD TO THIS SOFTWARE INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS. IN NO EVENT SHALL THE AUTHOR BE LIABLE FOR ANY SPECIAL, DIRECT, INDIRECT, OR CONSEQUENTIAL DAMAGES OR ANY DAMAGES WHATSOEVER RESULTING FROM LOSS OF USE, DATA OR PROFITS, WHETHER IN AN ACTION OF CONTRACT, NEGLIGENCE OR OTHER TORTIOUS ACTION, ARISING OUT OF OR IN CONNECTION WITH THE USE OR PERFORMANCE OF THIS SOFTWARE. --- The following Lucide icons are derived from the Feather project: airplay, alert-circle, alert-octagon, alert-triangle, aperture, arrow-down-circle, arrow-down-left, arrow-down-right, arrow-down, arrow-left-circle, arrow-left, arrow-right-circle, arrow-right, arrow-up-circle, arrow-up-left, arrow-up-right, arrow-up, at-sign, calendar, cast, check, chevron-down, chevron-left, chevron-right, chevron-up, chevrons-down, chevrons-left, chevrons-right, chevrons-up, circle, clipboard, clock, code, columns, command, compass, corner-down-left, corner-down-right, corner-left-down, corner-left-up, corner-right-down, corner-right-up, corner-up-left, corner-up-right, crosshair, database, divide-circle, divide-square, dollar-sign, download, external-link, feather, frown, hash, headphones, help-circle, info, italic, key, layout, life-buoy, link-2, link, loader, lock, log-in, log-out, maximize, meh, minimize, minimize-2, minus-circle, minus-square, minus, monitor, moon, more-horizontal, more-vertical, move, music, navigation-2, navigation, octagon, pause-circle, percent, plus-circle, plus-square, plus, power, radio, rss, search, server, share, shopping-bag, sidebar, smartphone, smile, square, table-2, tablet, target, terminal, trash-2, trash, triangle, tv, type, upload, x-circle, x-octagon, x-square, x, zoom-in, zoom-out The MIT License (MIT) (for the icons listed above) Copyright (c) 2013-present Cole Bemis Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software. THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
Dépôts
GitHub & GitLab
Veille sécurité
Blogs, RSS et Atom
Communautés
Réseaux et contributions
Index sélectionnés
Listes et tendances
Trier et classer
Enrichir et traduire
Outil et dépôt fictifs. Description, catégories, étoiles, forks et vues sont des exemples, pas des données réelles ou vérifiées. Outil et dépôt fictifs. Description, catégories, étoiles, forks et vues sont des exemples, pas des données réelles ou vérifiées. {"fictional":true,"name":"Tool","version":"1.0.1","repository":"owner/tool","live_metrics":false,"example_metrics":{"stars":1200,"forks":128,"views":8600}}
Outil
owner/tool v1.0.1
Découvrez les actifs et vérifiez les en-têtes HTTP.
Reconnaissance
Sécurité web
1,200 étoiles — Exemple fictif1.2k 128 forks — Exemple fictif128 8,600 vues — Exemple fictif8.6k