

PIIHunter
 owasp/piihunter
使用正则表达式、NER/ML 以及可选的自托管 LLM 检测,扫描 PostgreSQL 数据库和 Jira 问题中的 PII,并提供脱敏报告和审计日志。
defensive-toolsvulnerability-analysisdata-exfiltration+6
 owasp/secretsifter
OWASP 孵化项目:检测浏览器传输内容(JavaScript、配置响应、实时流量)中暴露的凭据。
 hilmiazizi/oorecon
用于攻击面发现的终端 UI:DNS 侦察、子域枚举、端口扫描、反向 IP、泄露的登录 URL 以及 JavaScript 密钥挖掘。
 m14r41/scan4secrets
使用170多条规则在源代码、Web URL和CI/CD中查找凭据和密钥,对照供应商API进行验证,并生成SARIF、JSONL、HTML、PDF或Excel报告。
 gmh5225/llm-guard-service
一项用于在与 AI 服务交互时提供针对提示注入、越狱攻击和有害内容防护的服务。

 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 matijamiki/ranwhat
Flight recorder and secret scanner for AI coding agents. Reads what Claude Code, Codex, Gemini CLI and 17 more ran, and flags risky actions and…
 safedep/gryph
AI 编码代理的安全层。适用于 Claude Code、Cursor、Windsurf、Gemini CLI、OpenCode、Pi Agent 等。
 praetorian-inc/caeruleus
用于Linux/BlueZ上蓝牙低功耗安全测试的单一Go二进制文件:扫描、枚举GATT、读/写/通知、模糊测试特征,并通过JSON输出运行结构化评估。
 99designs/aws-vault
一个用于在开发环境中安全存储和访问 AWS 凭据的保险库
 piratesshield/apiharvester
一次性 API 攻击工具 - 从给定的根 URL 中发现 API 地址并模拟自动化攻击
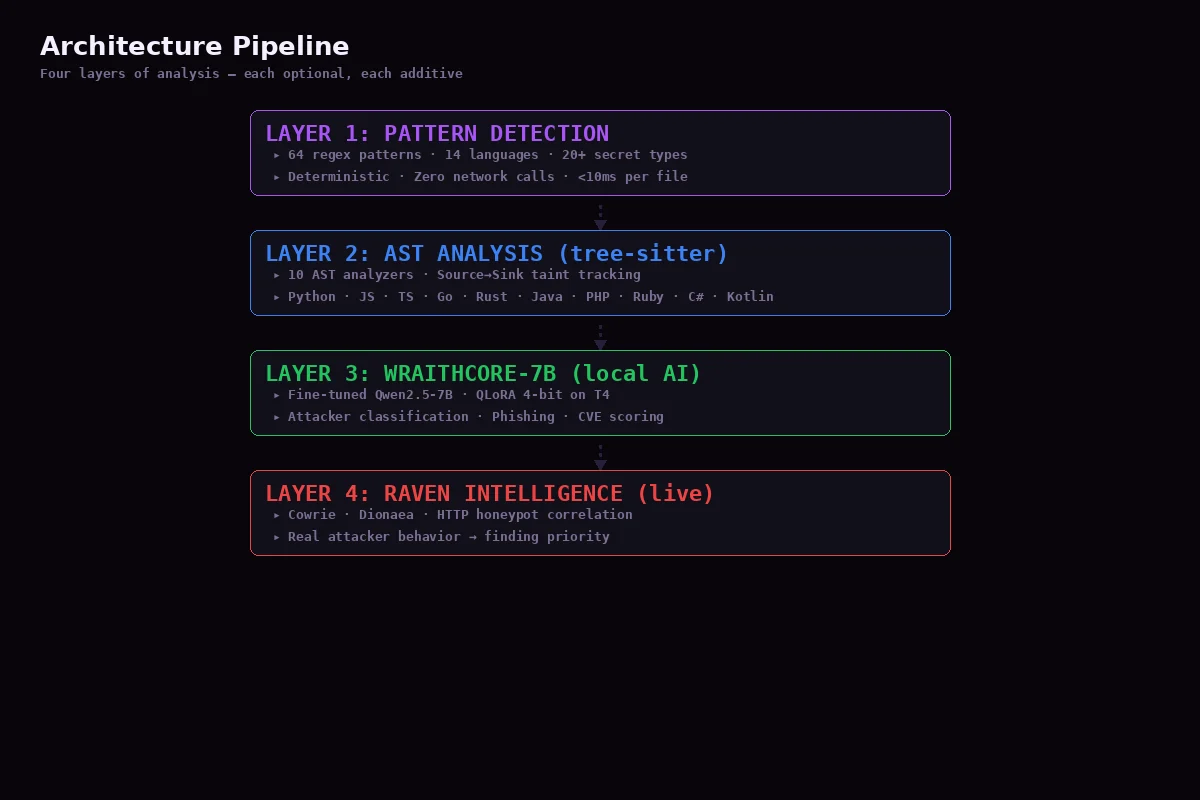 niffyhunt/codeguard-copilot
AI 驱动的安全副驾驶,在您编码时捕捉漏洞。为开发者提供实时安全扫描、教学式解释和自动修复。
 dmdhrumilmistry/security-harness
面向 AI 编码代理的多代理静态应用安全审查框架:映射代码库、搜寻漏洞类别、串联并验证发现结果,并输出 SARIF、JSON 和 PDF 报告。
 renich/genclave
Centralized, TPM 2.0 hardware-backed cryptographic identity enclave and multi-protocol bridge for Linux (FIDO2/CTAP2 WebAuthn Passkeys, OpenSSH…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
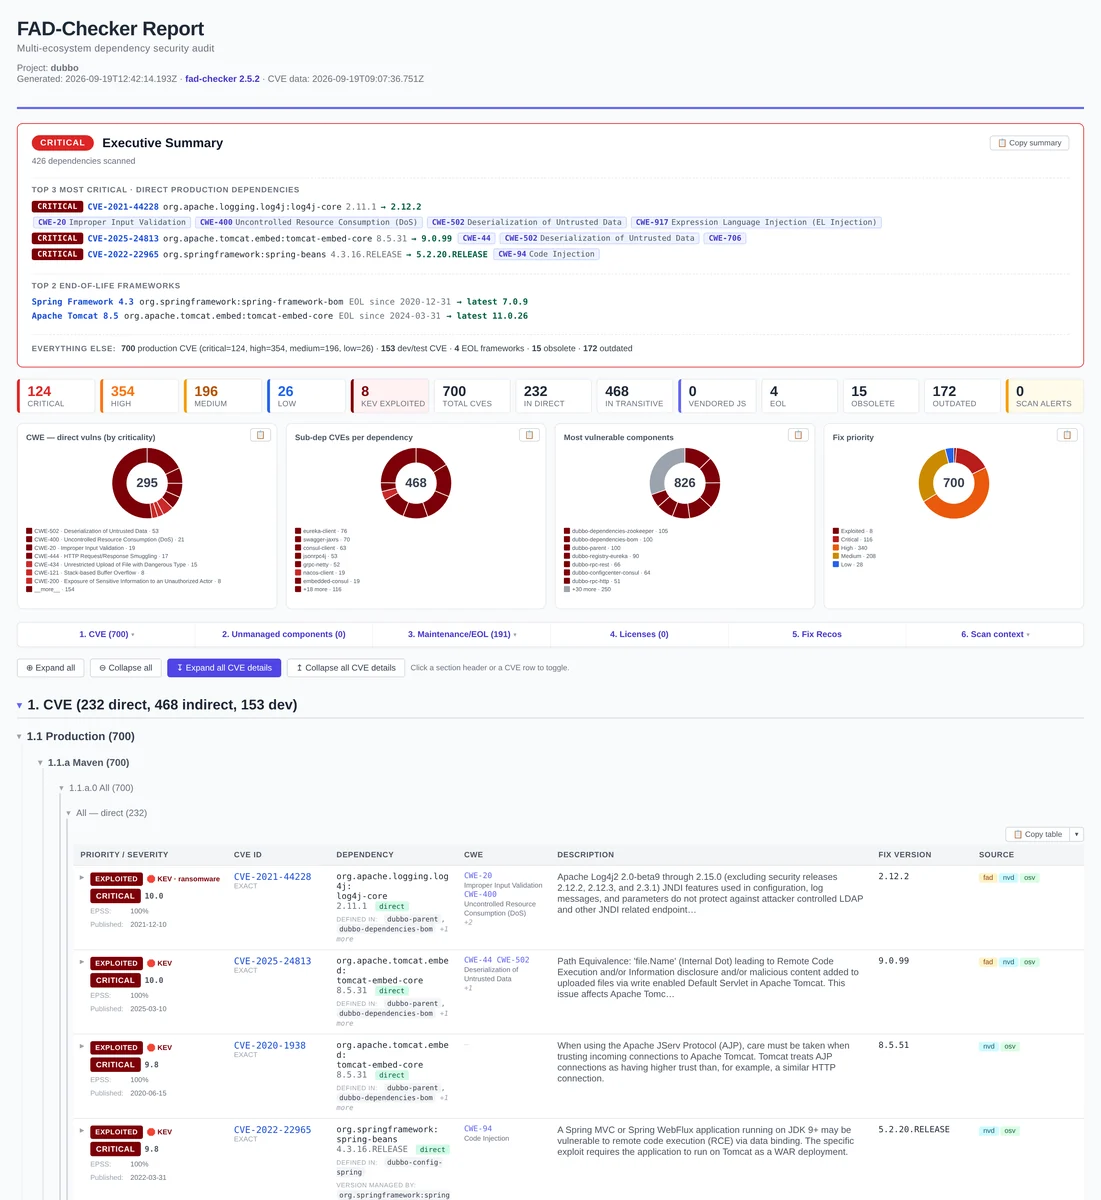 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…