

TornadoC2
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
penetration-testing-frameworkspersistence-mechanismsids-ips-evasion+9
2
 rapid7/metasploit-payloads
Metasploit Framework 不同载荷的统一仓库
 g13net/lockjaw
模块化 Windows C2 框架,包含 Rust teamserver、Zig 植入体、间接系统调用、AMSI 绕过、反射式/PoolParty 注入、内存中 BOF 执行以及 HTTP/DNS 传输。
 mythicagents/xenon
一个用 C 编写的 Windows Mythic 代理
 x3r0day/fud-c2-framework
一个无文件反向 shell 和 C2 框架,利用直接系统调用、代理隧道和 ChaCha20 加密来规避 AV。
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 voidsecsoftwares/voidsyscall
跨平台系统调用驱动的植入程序与 C2 —— 直接系统调用(Windows)、原始系统调用(Linux)、HTTPS/DNS/ICMP 通道。无 winapi 层。
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
 pr0xylife/qakbot
专注于银行木马和僵尸网络的威胁情报与恶意软件分析仓库,提供入侵指标(IOCs)、C2 指标以及用于检测和防御的行为研究。
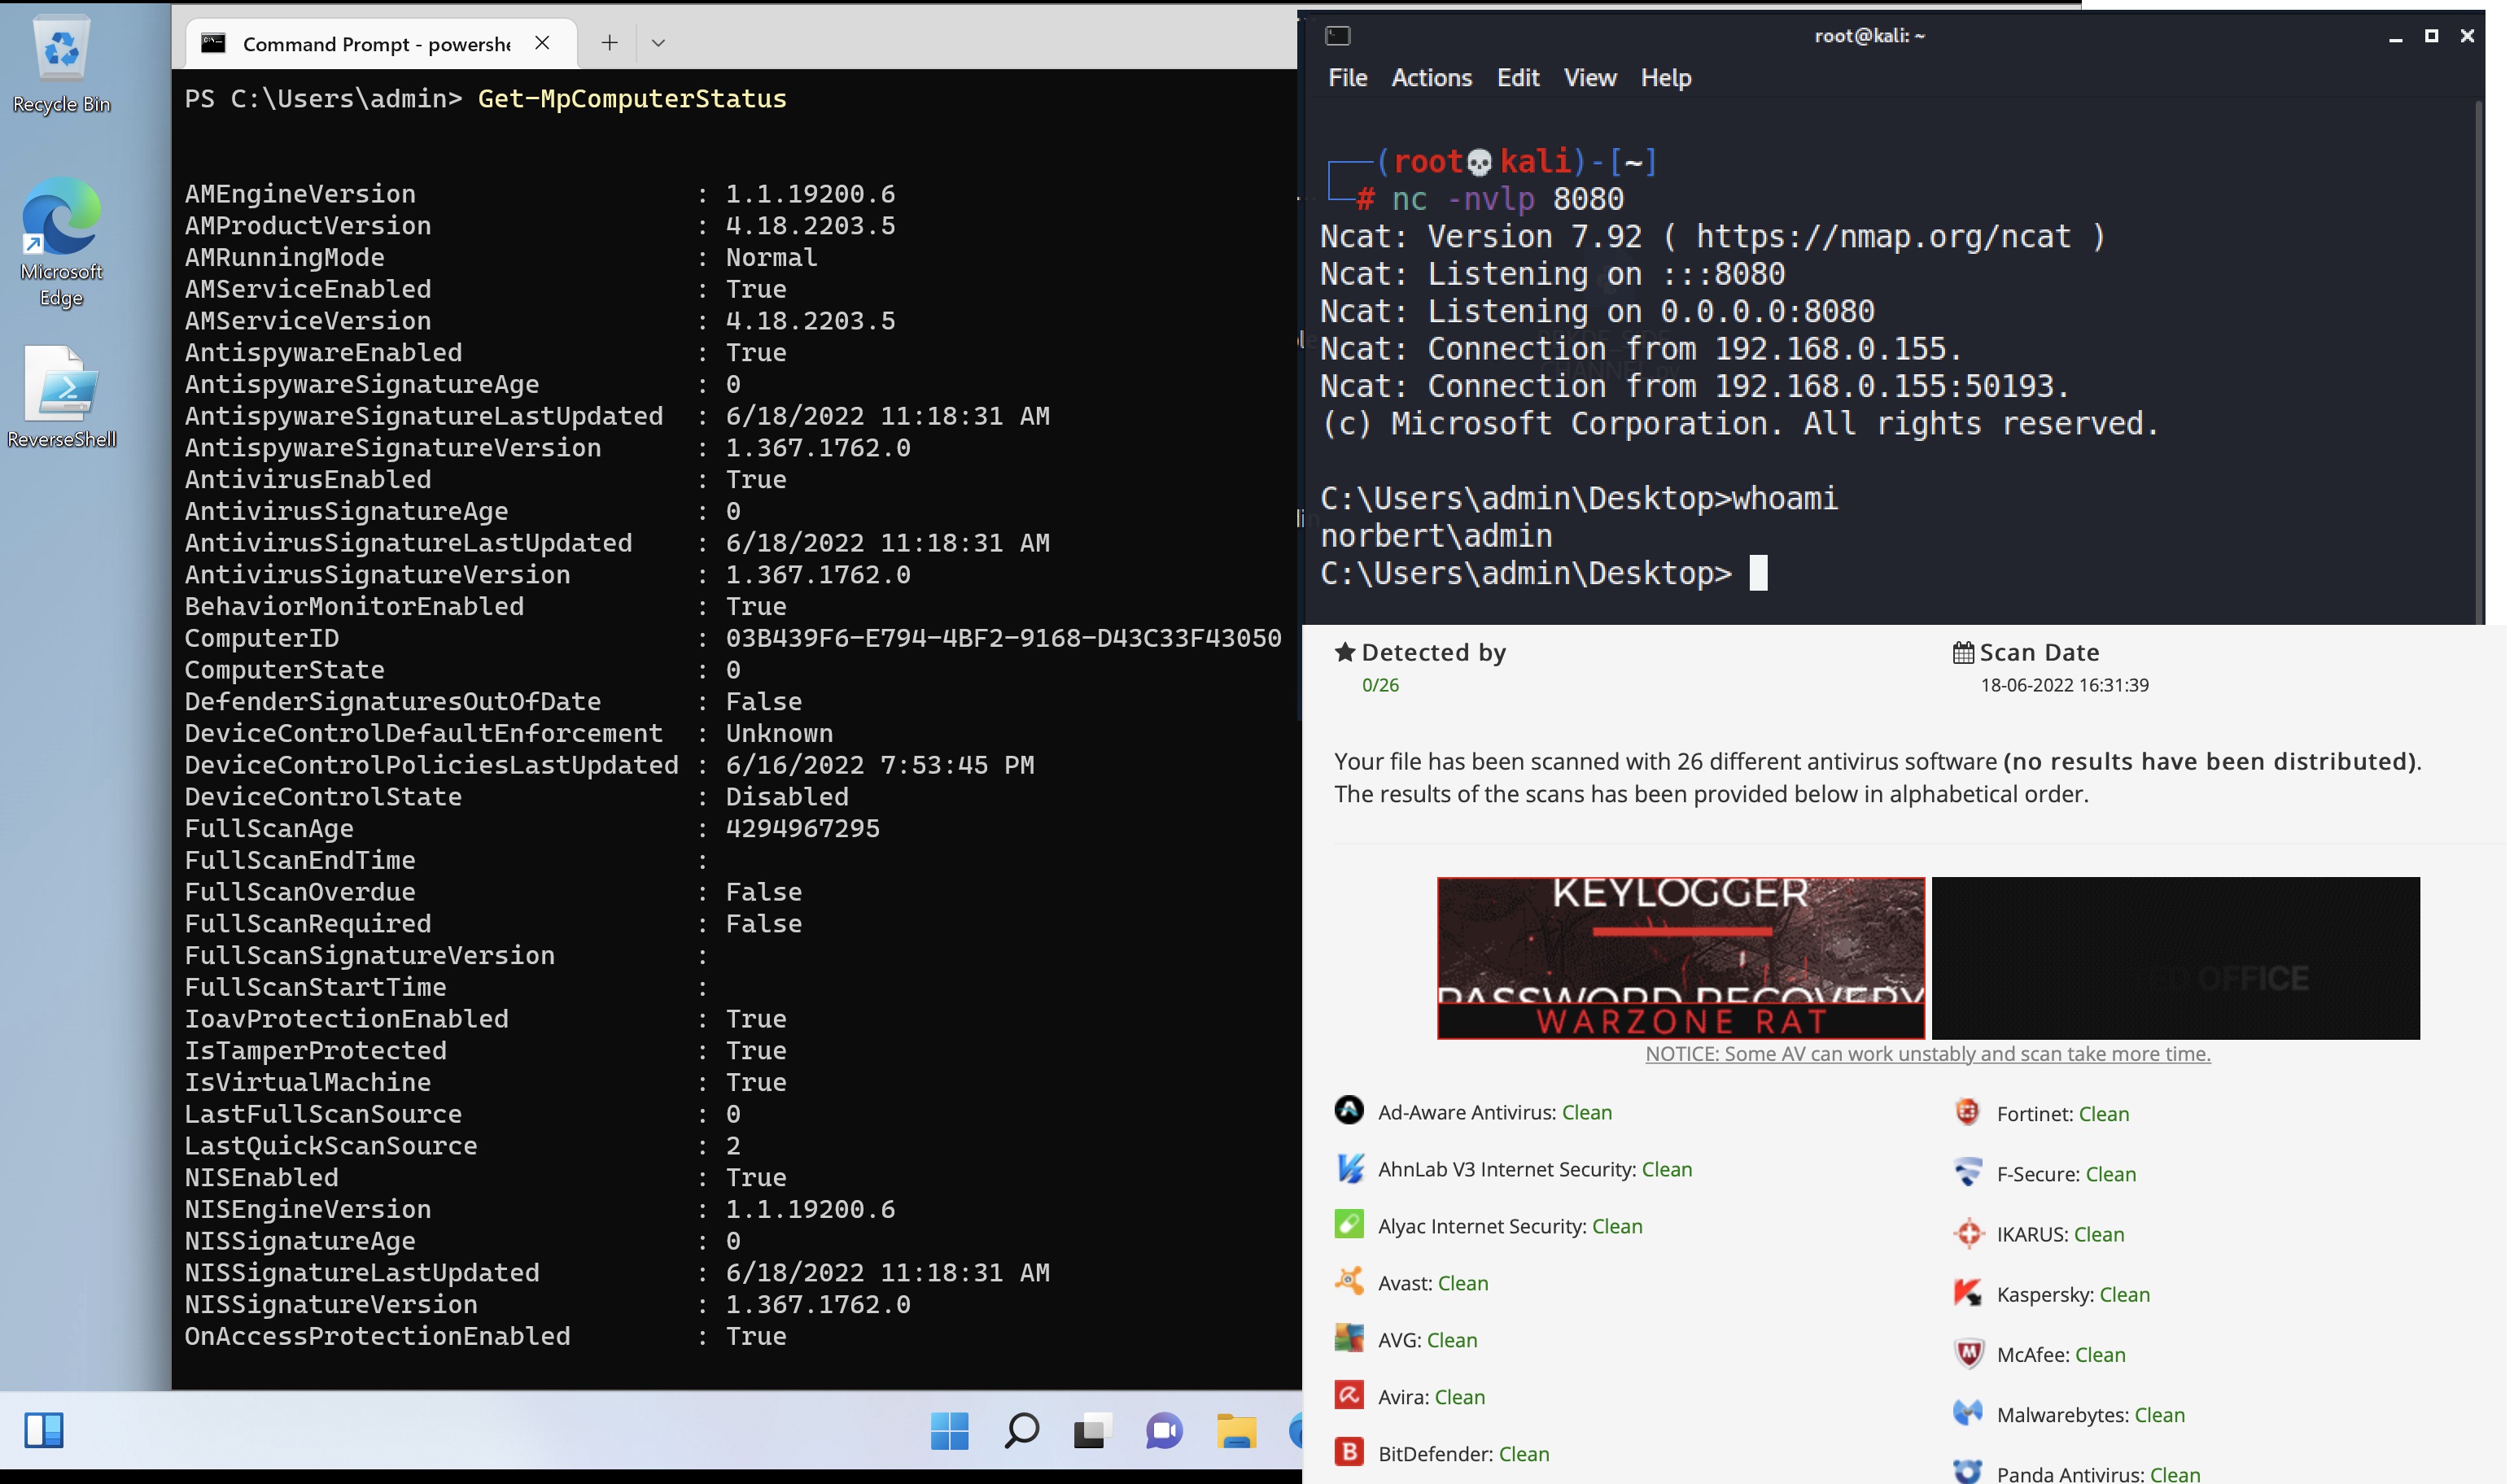 tihanyin/pssw100avb
一系列有用的 PowerShell 脚本,100% 免杀(在发布时)。
 bc-security/empire
Empire 是一个后渗透与对手模拟框架,用于协助红队和渗透测试人员。
 pr0xylife/gozi
具备浏览器注入和命令与控制功能的银行木马,用于窃取凭据和财务数据;与恶意软件分析、检测和威胁情报相关。
 darkcodersc/subseven
SubSeven 遗留官方源代码仓库
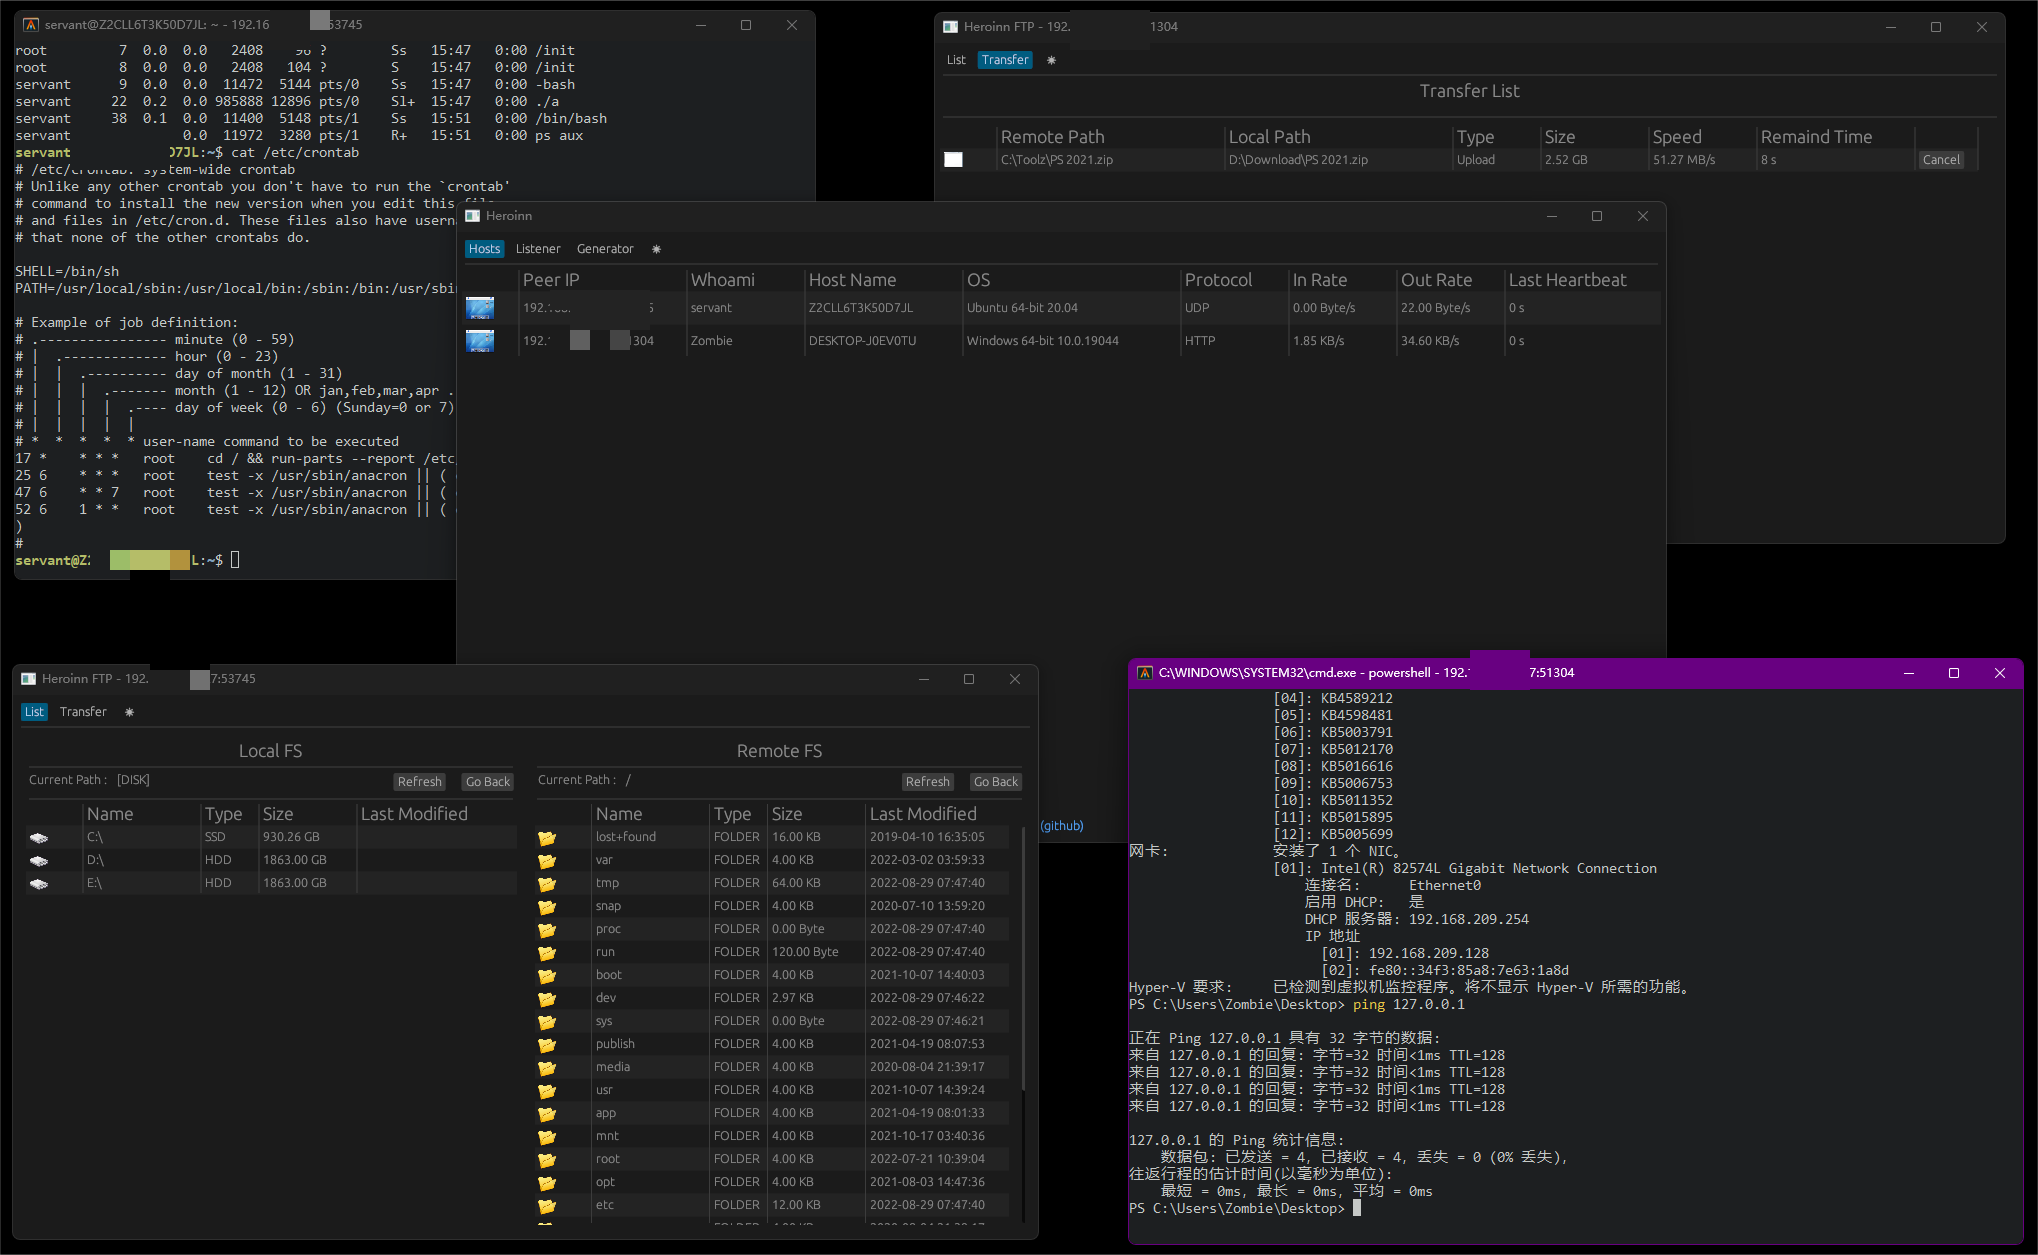 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 rvrsh3ll/rendezvousrat
自我修复型RAT,利用libp2p实现
 demon-i386/zoshrinkc2
DNS over HTTPS 针对性恶意软件(仅运行一次)