
Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
fad-checker — Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed keys, and binaries with SBOM and SARIF exports. | Kitploit
工具/GitHubGitHub/9pings/fad-checker
Defensive ToolsStatic AnalysisVulnerability ScannersVulnerability AnalysisCode AnalysisConfiguration AuditingDevSecOpsSecret DetectionSupply Chain Security
GitHub9pings/fad-checker

fad-checker

Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed keys, and binaries with SBOM and SARIF exports.

116616天前尚未审核

最受欢迎

查看全部 →

发现我们社区最常用的工具。

探索所有工具

浏览我们的工具集合

查看所有工具 →
分享
查看仓库
内容在请求的语言中不可用。显示英文版本。

fad-checker

npm version npm downloads license node CI

AKA Formidable Auditor's Dependency Checker
AKA Fuckin' Autonomous Dependency Checker

fad-checker is a polyglot dependency auditor built for professional code audits.

It scans 10 ecosystems + 9 CMS/Frameworks (WordPress, Drupal, Symfony, Laravel…) in one pass, with no build tools, support air-gapped workflows using transferred caches, private package detection, committed binaries & certificates, then produces clean HTML reports + json baseline + (DOC/XLSX/SARIF/CycloneDX/etc) .
🌐 Project site & docs →

fad-checker animated terminal demo: an offline Maven audit — dependencies absent from Maven Central flagged as private/internal, the compact single-line vulnerability-database progress, then findings coloured by severity

Features

  • 10 ecosystems in one pass; Maven, Gradle, npm/Yarn/pnpm, Composer, PyPI, NuGet, Go, Ruby — plus vendored JS, committed native binaries (identified by checksum) and embedded JARs (fat-jars/war/ear, opened in-memory).
  • No build tools; No mvn/gradle/npm/pip/dotnet/go, no node_modules/ → how
  • CVE from multiple sources, merged & prioritised; CVEProject + OSV.dev + Packagist security advisories + NVD, ranked CISA KEV → EPSS → CVSS.
  • Beyond CVEs; Report EOL and out-of-active-support frameworks, deprecated/abandoned/yanked, outdated, SPDX licenses, and private/internal packages
  • CMS & frameworks audited as instances; Symfony, Laravel, WordPress, Drupal, Joomla, PrestaShop, TYPO3, Magento/Adobe Commerce and SPIP with per-instance inventory (core, plugins, themes, bundles, components) → the dedicated guide
  • Crypto material; committed certificates, private vs public keys across PEM/OpenSSH/PuTTY/PGP and JKS/PKCS#12 keystores.
  • Air-gapped flow; zero network under --offline → Benchmark · Air-gapped
  • Shared cache for a scanner fleet; fad-checker serve-cache + --proxy-cache → cache usage
  • Supply-chain risk; known-malicious advisories and suspected typosquats (--typosquat).
  • Audit-grade; every report carries a provenance manifest and a Methodology & limitations chapter; a SHA256SUMS;
  • Differential audits diff against a prior run (--baseline) and CI can gate on new findings only.
  • Reports in English or French (--lang fr)
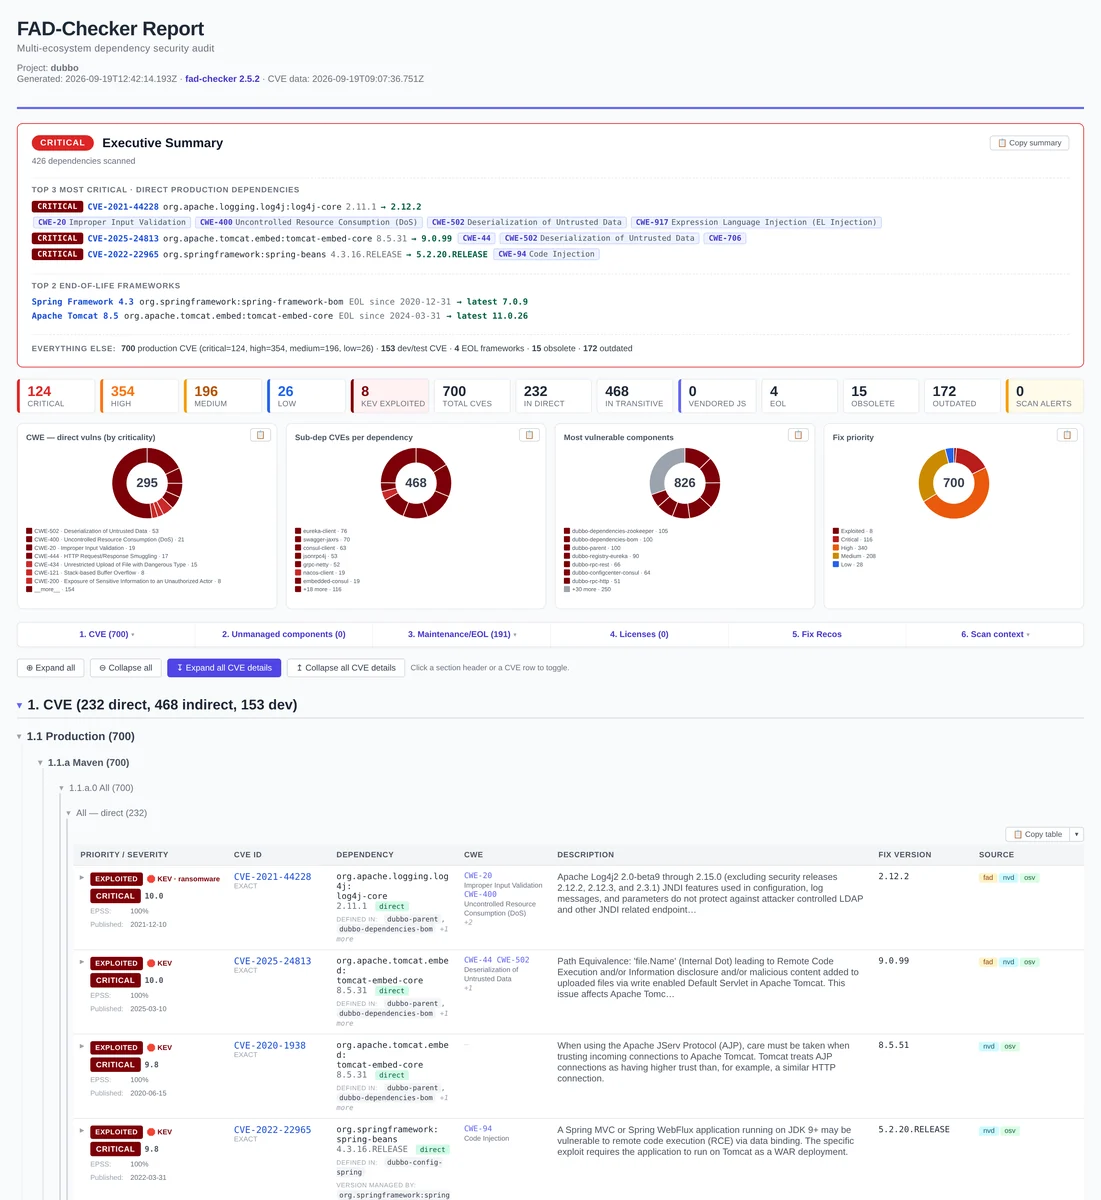
  • Outputs & CI; Pro HTML report + JSON baseline by default + Word, Excel, CycloneDX 1.6 SBOM, CSAF 2.0 VEX, SARIF 2.1.0, JSON; gate with --fail-on, triage with --ignore/--vex.
  • Report made for productivity; every table / chart has a Copy for word button.

📖 Usage & all flags · Architecture · Comparison vs other tools · Data sources

Quick start

npm install -g fad-checker
fad-checker -s ./my-project          # → ./fad-checker-report/cve-report.html

A free NVD API key (instant) gives 10× faster enrichment: fad-checker --set-nvd-key YOUR_KEY. A few common runs; full list via fad-checker --help or docs/USAGE.md

Interactive HTML samples

  • Apache Dubbo 2.7.8 — open the report: the project used for the screenshot above, rescanned with v2.7.1; 105 Maven descriptors, direct/transitive CVEs, KEV/EPSS, EOL and fix recommendations.
  • Multi-instance CMS & frameworks — open the report: WordPress 6.4.2, Drupal 8.5.0, Symfony Demo (Symfony 7.1.1) and BookStack v24.10 (Laravel 10.48.22), with findings attributed to each instance.

These are standalone reports from real source scans, frozen on 2026-09-24. The CMS sample focuses on PHP dependencies; WordPress advisory coverage is explicitly incomplete without a Wordfence feed. Sample scope, sources and reproduction commands.

[!WARNING] fad-checker is new and may still contain ( rare ) bugs. Treat its output as a strong first pass, double-check anything critical, and please report issues; they get fixed fast.

Why use fad-checker for code audits?

What it does for an audit that the others don't. Same column set and sourcing discipline as docs/COMPARISON.md — ⚠️ is partial and says how, cells are meant to be checkable.

下载工具