
ipsw-diffs
 blacktop/ipsw-diffs
Publishes per-build diffs of iOS, iPadOS, and macOS IPSW firmware releases, enabling binary-level comparison of system components across versions and…
ios-securityvulnerability-analysisreverse-engineering+6
896
blacktop/ipsw-diffsPublishes per-build diffs of iOS, iPadOS, and macOS IPSW firmware releases, enabling binary-level comparison of system components across versions and…
 fkie-cad/sandroid_dexray-intercept
一款Android恶意软件分析工具,通过挂钩应用程序在密码学、文件系统、数据库、网络通信和进程操作方面的行为,创建全面的运行时配置文件。
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 jtsylve/lime
用于从 Linux 和 Android 设备获取易失性内存的内核模块,可生成具备取证可靠性的内存捕获,并保存到磁盘或通过网络传输。
 log2timeline/plaso
数字取证引擎,可解析日志、文件和系统工件以构建超级时间线,从而实现调查中的时间顺序事件关联。
 google/timesketch
用于摄取、搜索和注释事件日志的协作式取证时间线分析平台,以支持事件响应和 DFIR 调查。
 mvt-project/mvt
面向 Android 和 iOS 设备的取证收集与分析工具包,利用公开和私有的入侵指标(IOC)识别由已知间谍软件造成的潜在入侵。
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 realitynet/android-forensics-references
精选的 Android 取证产物与日志路径参考,附有 CTF 题解、研究论文及移动设备分析工具的链接。
 andrewrathbun/dfirartifactmuseum
该仓库的目标是归档各种操作系统所有版本的工件(artifacts),并按类型进行分类。这将有助于工件验证流程,同时提高对可能已不再容易获取的工件的访问能力。
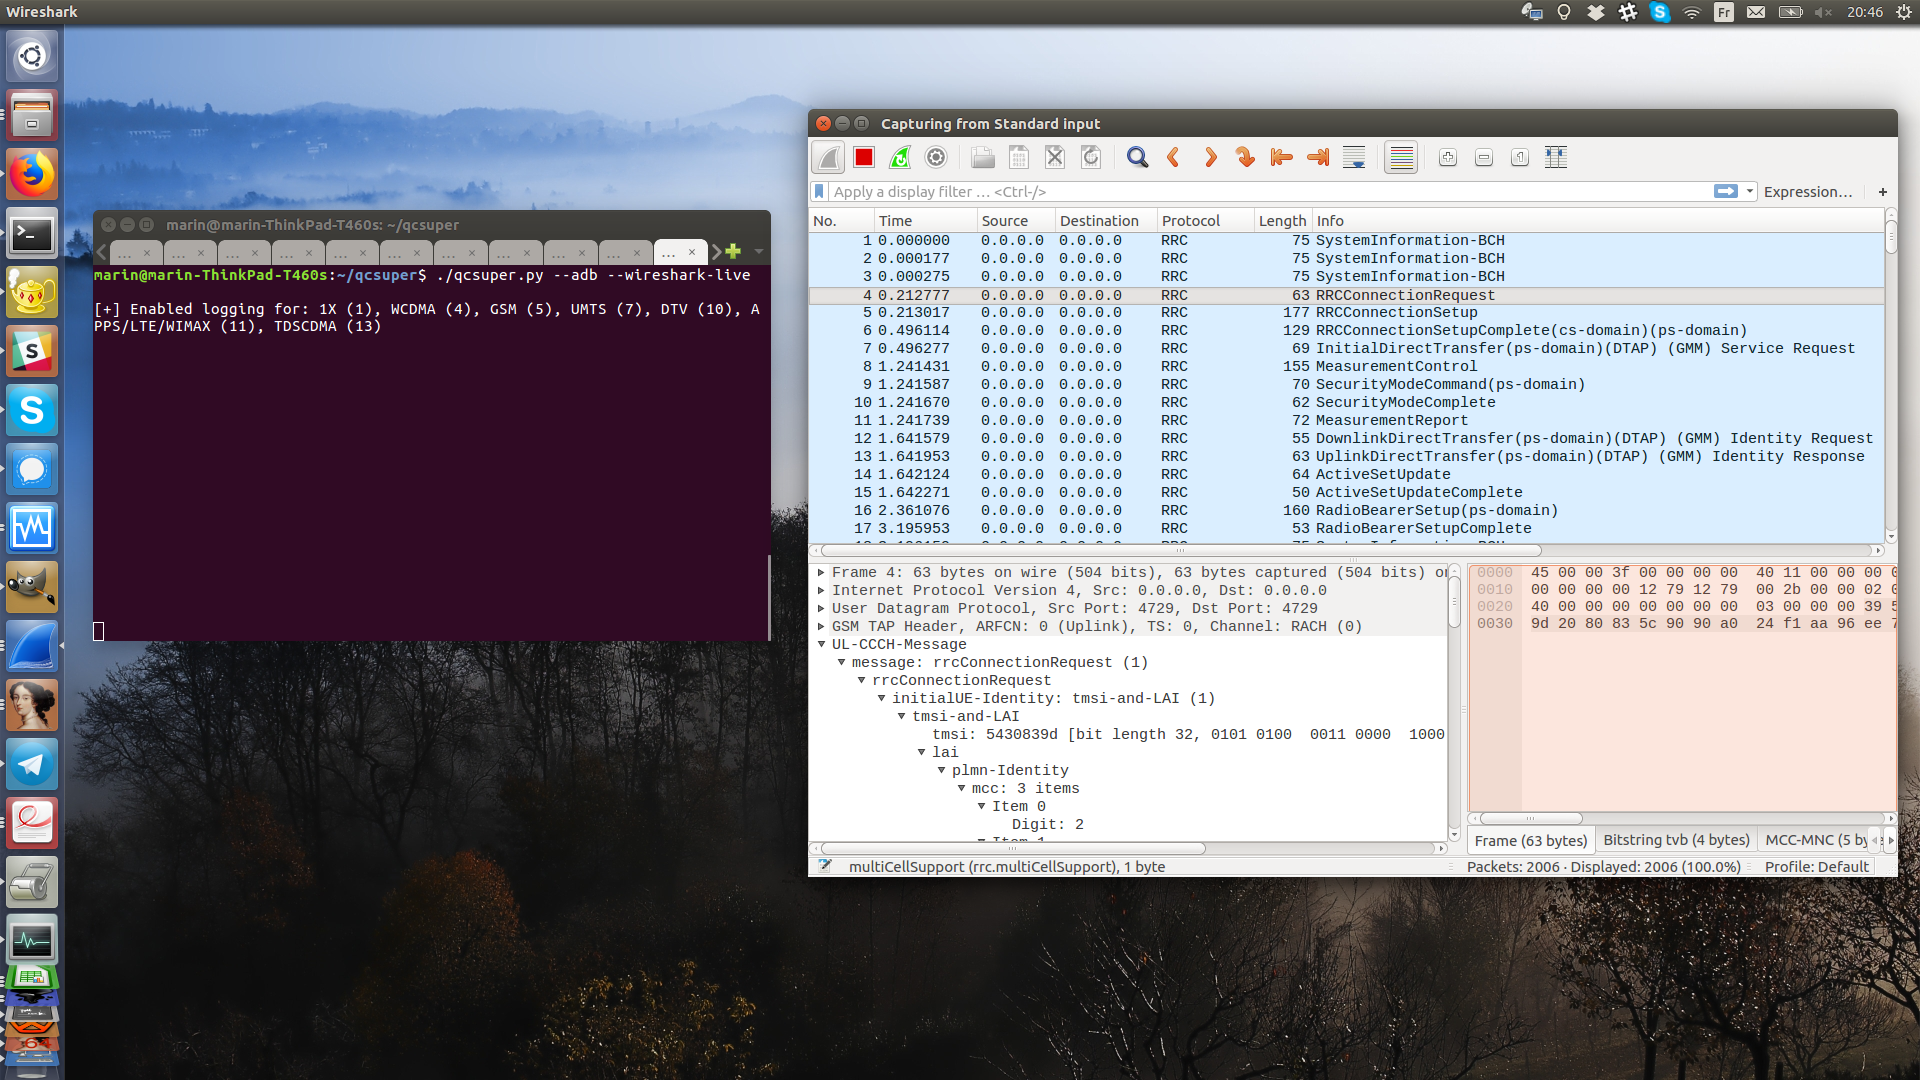 p1sec/qcsuper
QCSuper 是一款与基于高通(Qualcomm)芯片的手机和调制解调器通信的工具,除其他功能外,它还能捕获原始的 2G/3G/4G 无线电帧。
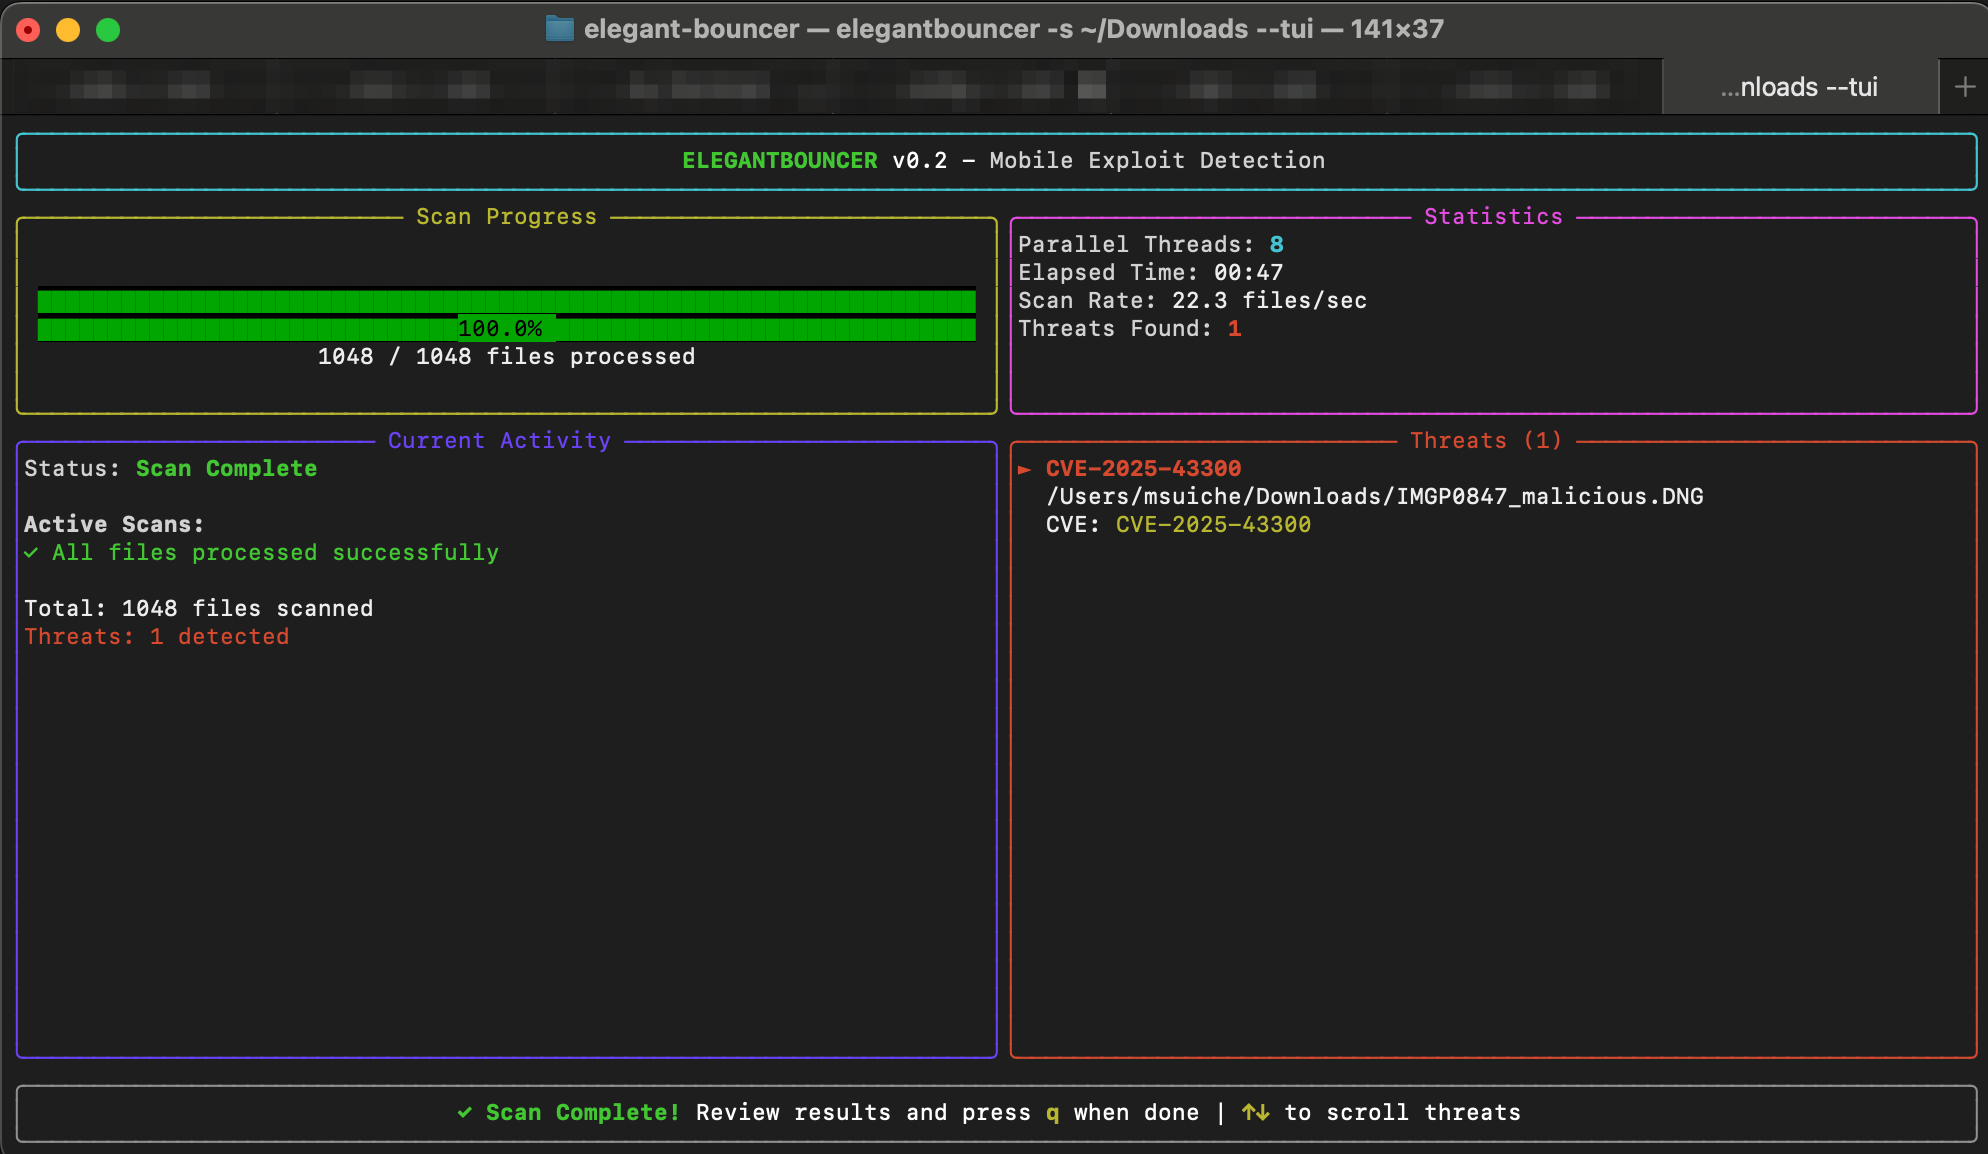 msuiche/elegant-bouncer
ELEGANTBOUNCER 是一款用于检测基于文件的移动端漏洞利用的工具。
 sleuthkit/autopsy
Autopsy® 是一个数字取证平台,也是 The Sleuth Kit® 及其他数字取证工具的图形界面。执法部门、军方和企业检查人员均可使用它来调查计算机上发生的事件。你甚至可以用它来恢复相机存储卡中的照片。
 eldavoo/wa-crypt-tools
管理 WhatsApp 的 .crypt12、.crypt14 和 .crypt15 文件。
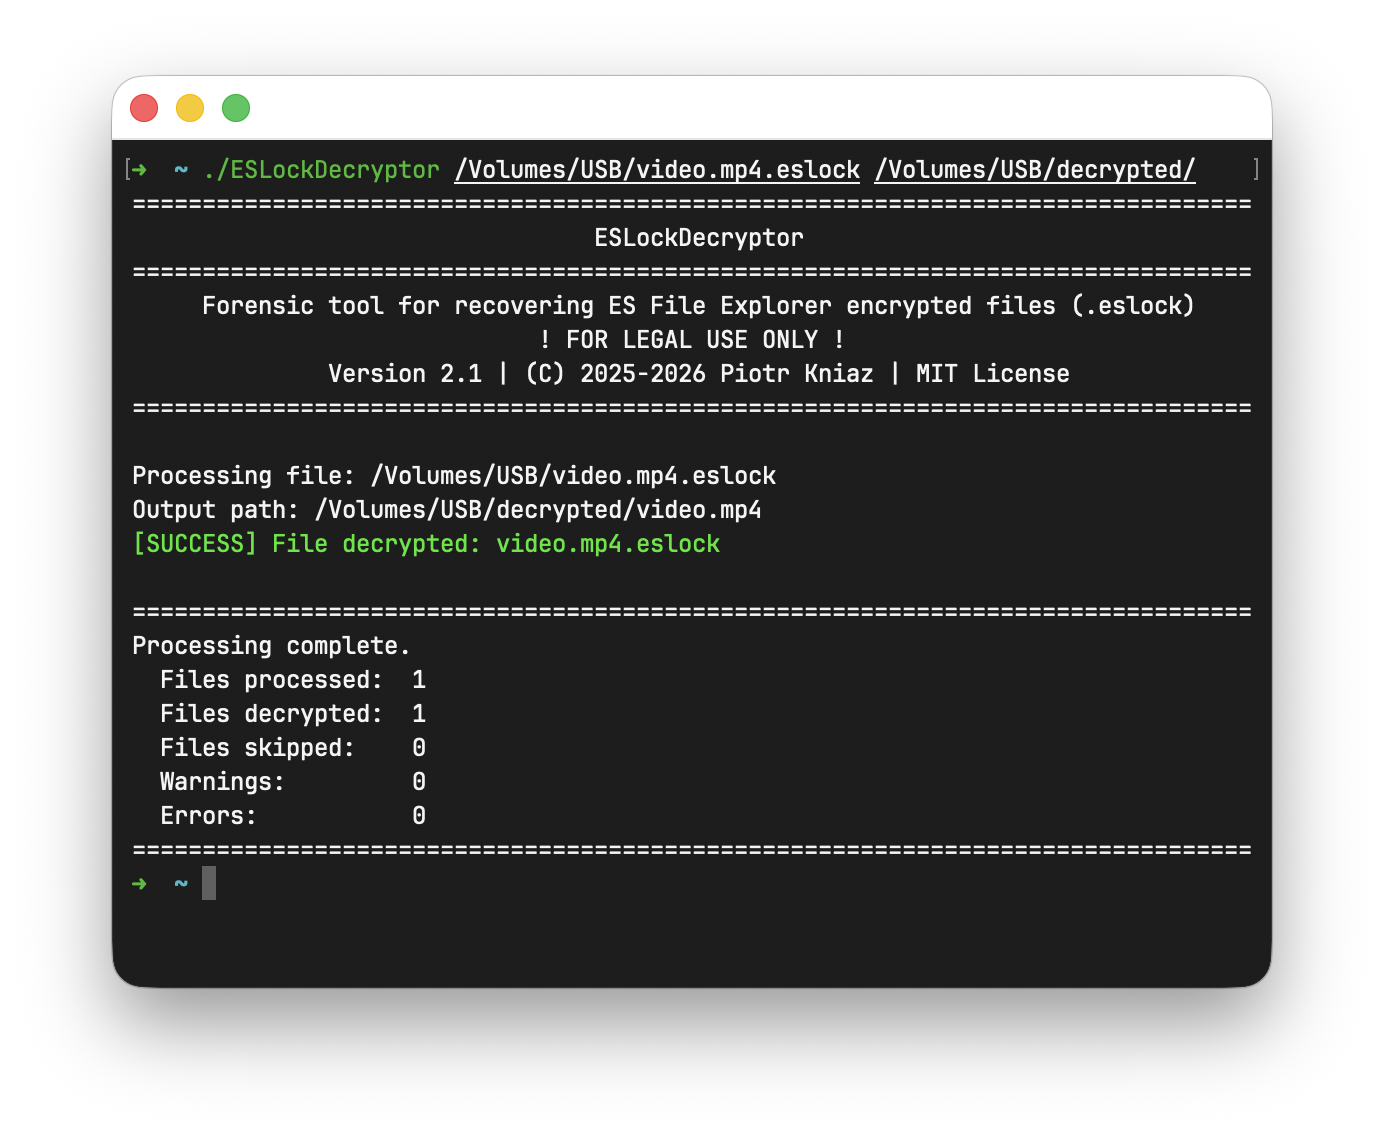 piotr-kniaz/eslockdecryptor
Tool for recovering and decrypting ES File Explorer encrypted files (.eslock)