

TornadoC2
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
penetration-testing-frameworkspersistence-mechanismsids-ips-evasion+9
2
 nawaralseelawi/pvbrf-id
用于私有、可验证、拜占庭鲁棒的联邦入侵检测协议的仿真代码和结果,该协议使用秘密共享、Merkle 审计和 Pedersen 承诺。

 rdelasierra-uy/portfolio
专业展示平台:Hack The Box 的 writeup、报告、GRC 案例研究(ISO 27001/27002/27005/27035、ISO 31000 + MAGERIT)、加固脚本以及 eJPT -> ISO 27001 Lead Auditor -> CISA 路线图。
 jihoonjang98/hqc-x86-simd
面向AVX2和AVX-512(含GFNI)的优化HQC后量子KEM实现,以及面向x86物联网网关的统一基准测试与NIST KAT套件。
 cyrusimap/cyrus-sasl
Cyrus SASL API 实现,依据 RFC 4422 通过可插拔的 SASL 机制提供客户端和服务端身份验证与授权服务。
 luftwaffe66/gobfuscator
通过 AES-256 字符串加密及运行时解密、标识符重命名和注释移除来混淆 Go 源代码,以阻碍逆向工程,同时保持运行时行为不变。
 wolfssl/wolfssh
Small, portable embeddable SSHv2 client and server library in C with SCP, SFTP, port forwarding, and post-quantum key exchange for embedded and IoT…
 animeshshaw/pqc-cost-of-delay
Cost-of-delay prioritisation for post-quantum migration: classical and harvest-now-decrypt-later risk in one unit (USD per year). Code, proofs, case…
 slowmist/knowledge-base
Curated knowledge base of blockchain security research, audit reports, guides, and translations covering smart contracts, cryptography, and AI…
 linnemanlabs/glimmer
用于安全研究的对手模拟与C2框架
 abraxas/gatex
FortinetHunter(@YogSoth0)二进制破解应用。FortinetHunter CTF 的一部分。ELF 门:一个经过剥离的 Nuitka onefile、一个 XOR 混淆的 Argon2id 验证器、AES-GCM 完整性校验。
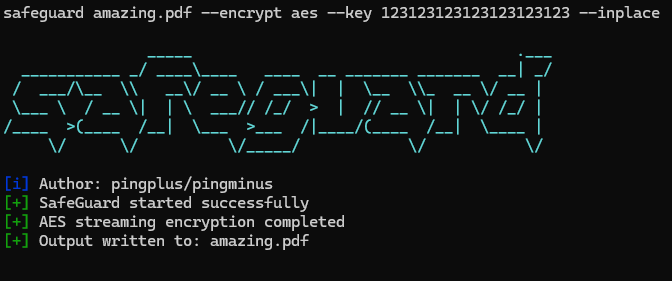 pingpongplus/safeguard
仅用于学习目的的 Go 语言 CLI 加密工具
 gmh5225/kli-ex
面向 Windows 驱动程序的扩展内核延迟导入器,可在运行时解析 API,并使用加密、缓存的导入名称来隐藏内核函数的使用,从而规避静态分析。
 saml-toolkits/ruby-saml
Ruby 库,实现 SSO 的 SAML 服务提供方端,处理认证请求、响应验证、XML 签名检查以及 IdP 元数据解析。
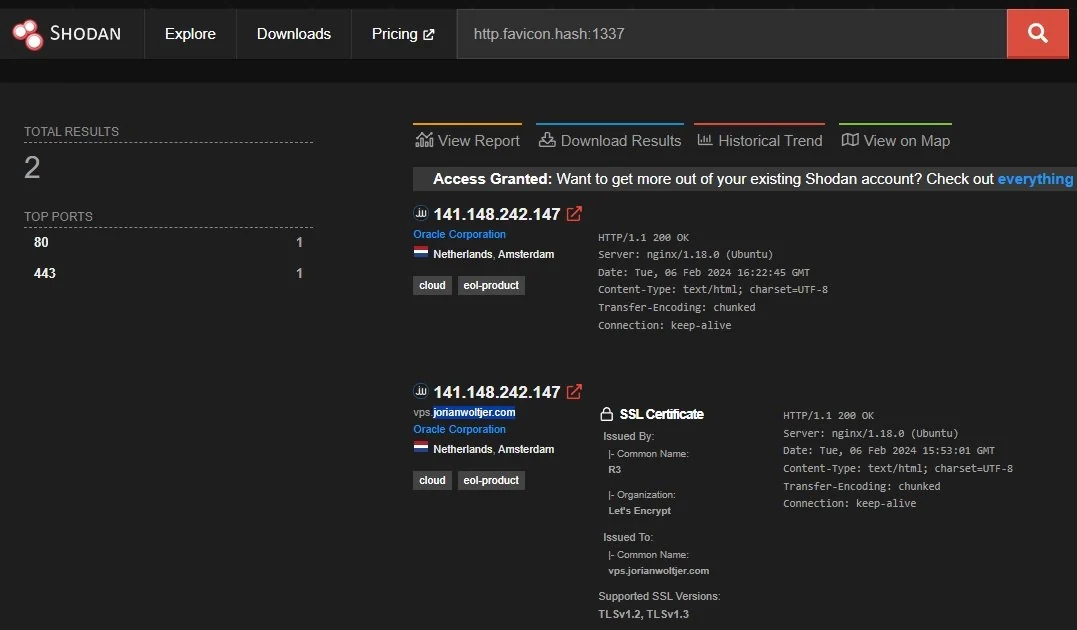 jorianwoltjer/shodan-favicon-preimage
生成一个在 Shodan 上可得到任意目标哈希的 favicon
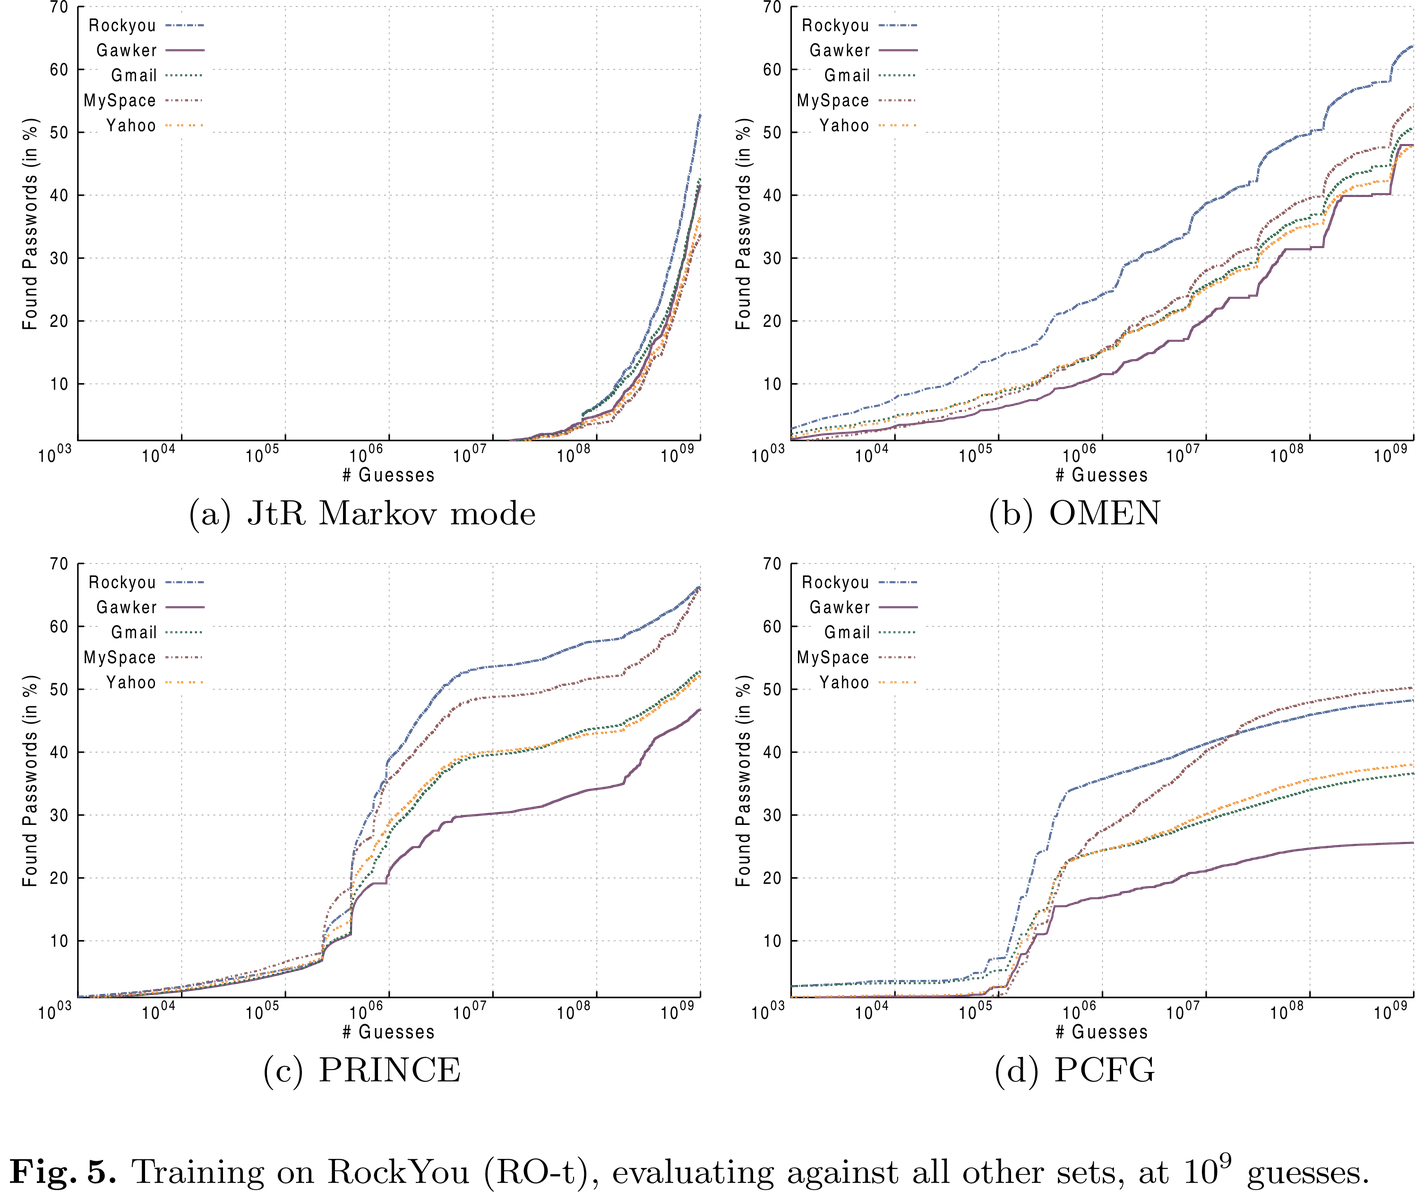 rub-syssec/omen
基于马尔可夫模型的 C 语言密码猜测器,按概率枚举候选密码,优先生成最可能的密码,用于通过 Hashcat 或 John 进行哈希破解。
 karaaslanlabs/kl-security-key
Experimental RP2040 FIDO2/WebAuthn authenticator with packed attestation and documented Windows/Entra interoperability
 soufianecyber/quantum-safe-migration
Enterprise-grade toolkit to audit and migrate legacy infrastructure to hybrid post-quantum cryptography (PQC).