

OshoosiClaw
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
defensive-toolsnetwork-securitymalware-analysis+8
oyesanyf/oshoosiclawAutonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 gmh5225/maldec-edr
基于内核级机制的 Unix 端点检测与响应解决方案,用于实时检测异常和恶意软件攻击。
 nawaralseelawi/pvbrf-id
用于私有、可验证、拜占庭鲁棒的联邦入侵检测协议的仿真代码和结果,该协议使用秘密共享、Merkle 审计和 Pedersen 承诺。
 yxf203/defense-as-skill
运行时防护技能,用于检测并阻止技能增强型智能体中由技能引发的恶意攻击,并采用MCTS循环,根据推演反馈演化防护策略。
 perplexityai/numbat
对端点上 AI 代理活动的可见性,具备设备端检测、可选的操作前阻断以及取证重建能力。
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
 gmh5225/llm-guard-service
一项用于在与 AI 服务交互时提供针对提示注入、越狱攻击和有害内容防护的服务。
 trustedsec/artillery
开源蓝队工具,通过多种主机和网络防御与检测方法保护 Linux 和 Windows 系统。
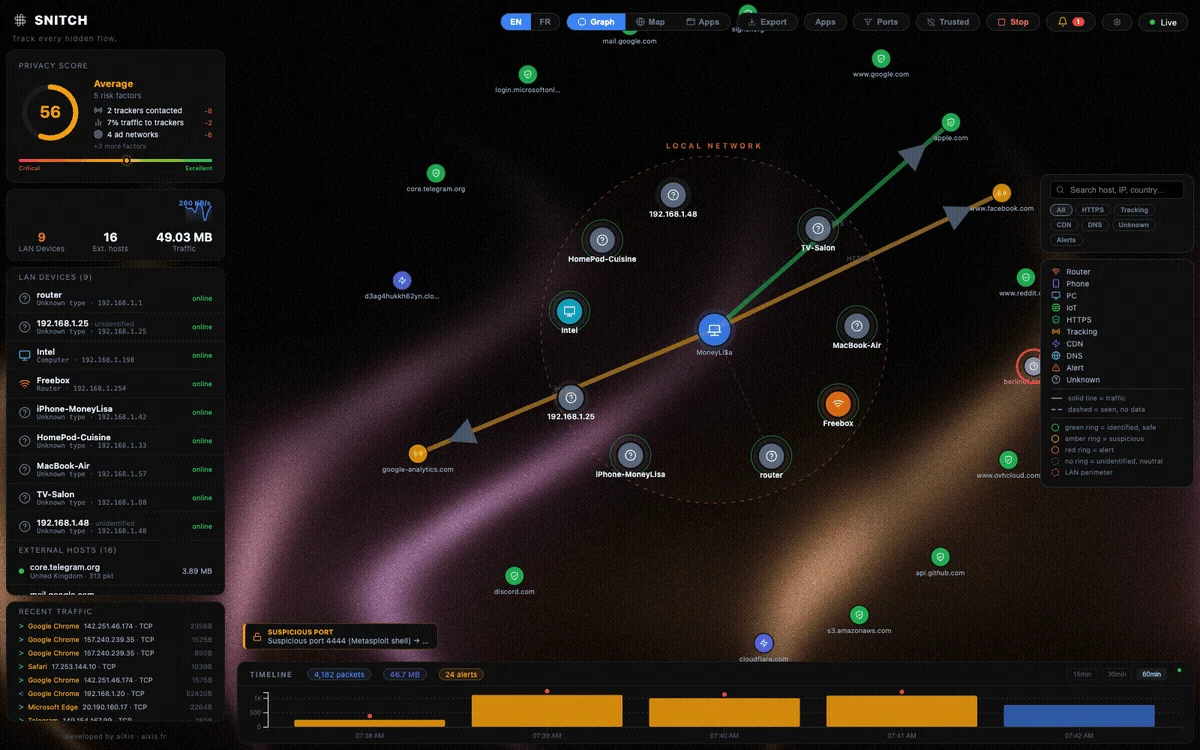 aixisstudio/snitch
实时网络流量可视化工具——查看你计算机建立的每一个连接。隐私优先,100% 本地运行。
 modzero/burp-responseclusterer
Burp 插件,用于对响应进行聚类,以展示已接收响应的概览
 pentagridsec/pentagridresponseoverview
BurpSuite 响应概览扩展 - 通过对响应正文进行分组来发现异常响应
 rbidou/pyrasp
面向 Python Web 服务器、无服务器函数和 MCP 服务器的运行时应用自我保护,无需签名即可检测攻击、提示注入和数据泄露。
 liuz233/harde
HARDE 的研究代码,这是一个 agent harness,用于探测并自适应优化组件,以在各类 agent 安全基准测试中实现运行时风险检测与执行控制。
 microlaser/dns_watchdog_windows2
PowerShell 脚本,通过 pktmon 监控 Windows DNS 流量,以检测投毒、欺骗、恶意解析器响应和网关 MAC 地址变更,并记录警报。
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
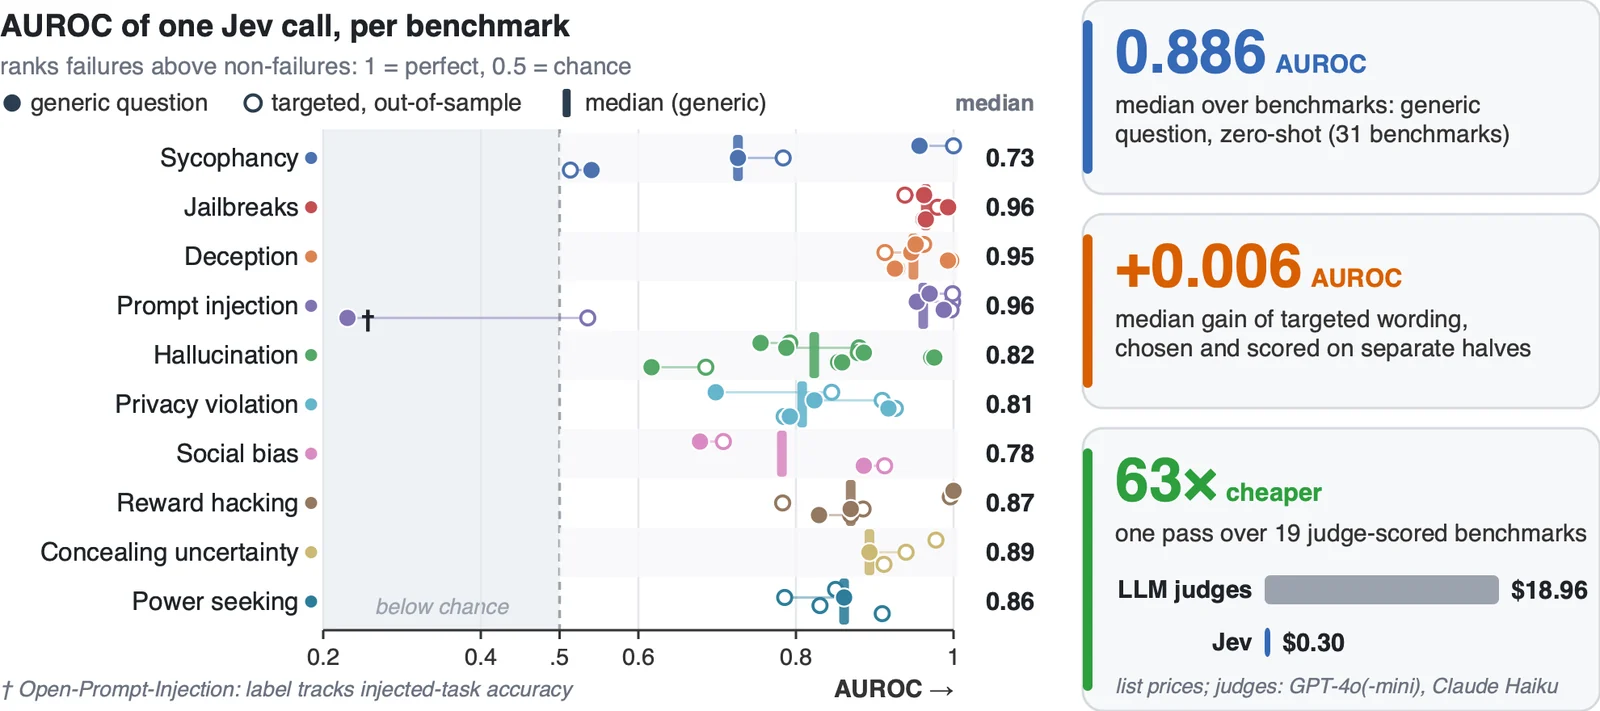 sumleo/rlcdalignbench
Benchmark suite and code for detecting AI alignment failures, with 44 benchmarks across ten failure types and a zero-shot RLCD detector evaluated on…
 cbuijs/sdproxy
简单快速的 DNS 代理,具备并不简单的功能。专注于路由 DNS 转发、过滤和家长控制。
 pushkarreddyy/radioguard
面向 Android 的零信任蜂窝防御子服务(IMSI-Catcher、2G SMS Blaster 和 4G aLTEr 检测与安全路由)