

MCP-God-Mode
 gmh5225/mcp-god-mode
你是否曾希望它能包办一切?在单个 MCP 服务器上集成 148 款强大的信息安全/管理工具。
packet-sniffing-analysisport-scanningrfid-nfc-tools+9
11年前
gmh5225/mcp-god-mode你是否曾希望它能包办一切?在单个 MCP 服务器上集成 148 款强大的信息安全/管理工具。
 hilmiazizi/oorecon
用于攻击面发现的终端 UI:DNS 侦察、子域枚举、端口扫描、反向 IP、泄露的登录 URL 以及 JavaScript 密钥挖掘。
 tegal1337/pocketpentester
离线优先的 Android 攻击性安全工具包,包含 21 个模块,用于侦察、端口扫描、子域名枚举、SQLi/XSS/JWT 利用、载荷生成和哈希分析。
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
 vqkro/higernes
a passive OSINT toolkit in python and c++ usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 ankhcorp/nuke.sh
基于 Bash 的被动侦察 + 攻击面测绘脚本,仅使用公共 API + 标准 Linux 工具(curl、dig、openssl、nmap、python3)。
 mmarting/unwaf
Go 工具,通过多个 OSINT 来源被动发现 WAF/CDN 背后的真实源站 IP,然后通过 HTML 相似度、SSL 证书指纹和 HTTP 头验证候选 IP。
 simplifaisoul/osiris
开源全球情报平台 - 实时 OSINT 仪表盘 - Palantir 的替代方案 - 2nZNHm3Lr9umG3DVrzYwHgktwkuKuJRXqqRqs3ewpump

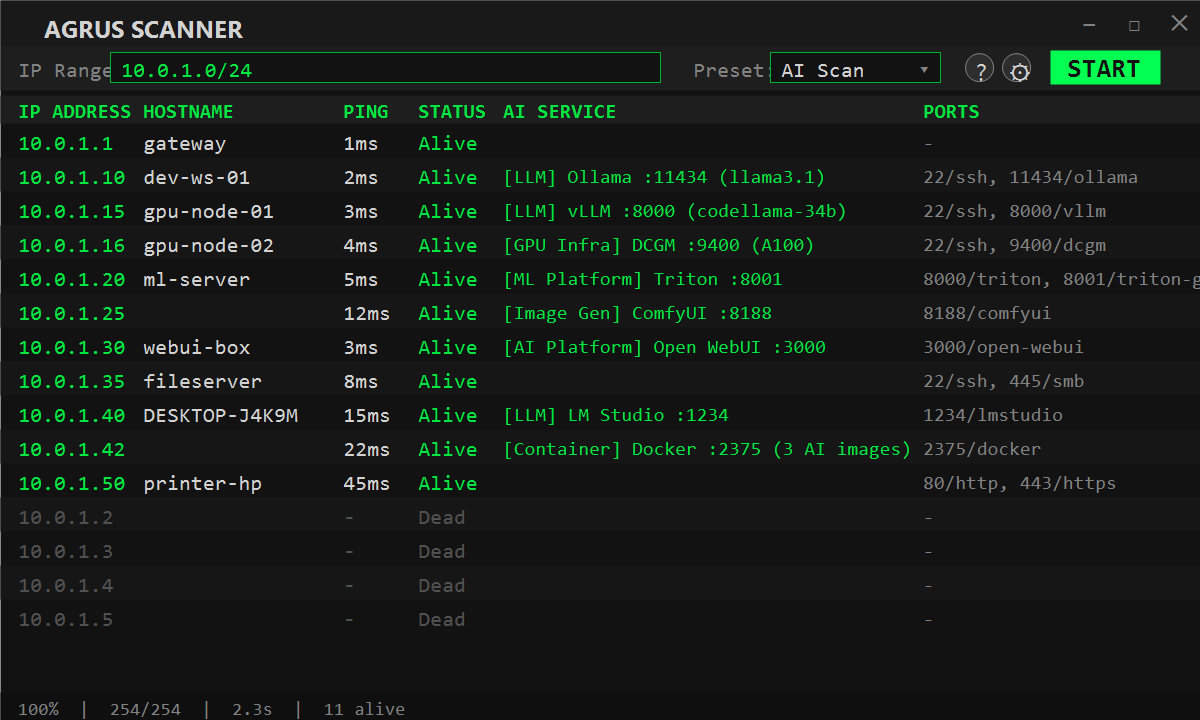 nybaywatch/agrusscanner
Windows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…
 vighnesh91/omnisec-hex
浏览器本地安全 monorepo,包含六个模块,用于移动端 APK/IPA 分诊、客户端 DAST 模糊测试、OSINT 目录、离线 AI 威胁评分以及网络端口/CSP 审计。
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 sakispat/simple-pentesting
一个用于授权渗透测试的教育性 Python 工具包:线程化端口扫描器、子域名与目录枚举、横幅抓取和主机发现,并配有功能丰富的 CLI。
 voidsecsoftwares/voidsec-proxy
用于SOCKS5代理链、端口扫描、DNS枚举、哈希破解、反向shell生成、隐写术和匿名化的多模块攻击性安全工具包。
 yeee3642/edu-recon
面向授权教育行业的侦察与分类编排工具(nmap/dirsearch/sqlmap/hydra + CVE-2024-4577、密钥/API密钥泄露、XSS、wp2shell),带Web控制面板