
ELEGANTBOUNCER 是一款针对基于文件的移动端漏洞利用的检测工具。
它采用创新方法进行高级的基于文件的威胁识别,无需依赖在野样本,并且优于基于正则表达式或 IOC 的传统方法。目前,它主要针对移动端漏洞的识别,例如 FORCEDENTRY(CVE-2021-30860)、BLASTPASS(CVE-2023-4863、CVE-2023-41064)和 TRIANGULATION(CVE-2023-41990)。
| 威胁名称 | CVE | 支持 |
|---|---|---|
| FORCEDENTRY | CVE-2021-30860 | ✅ |
| BLASTPASS | CVE-2023-4863, CVE-2023-41064 | ✅ |
| TRIANGULATION | CVE-2023-41990 | ✅ |
| CVE-2025-43300 | CVE-2025-43300 | ✅ |
| CVE-2025-21043 | CVE-2025-21043 | ✅ |
| CVE-2026-32741 | CVE-2026-32741 | ✅ |
| HEIF mask underfill | 无 CVE(libheif <= 1.21.2) | ✅ |
| CVE-2026-32882 | CVE-2026-32882, CVE-2025-68431 | ✅ |
| CVE-2026-86950 | CVE-2026-86950 | ✅ |

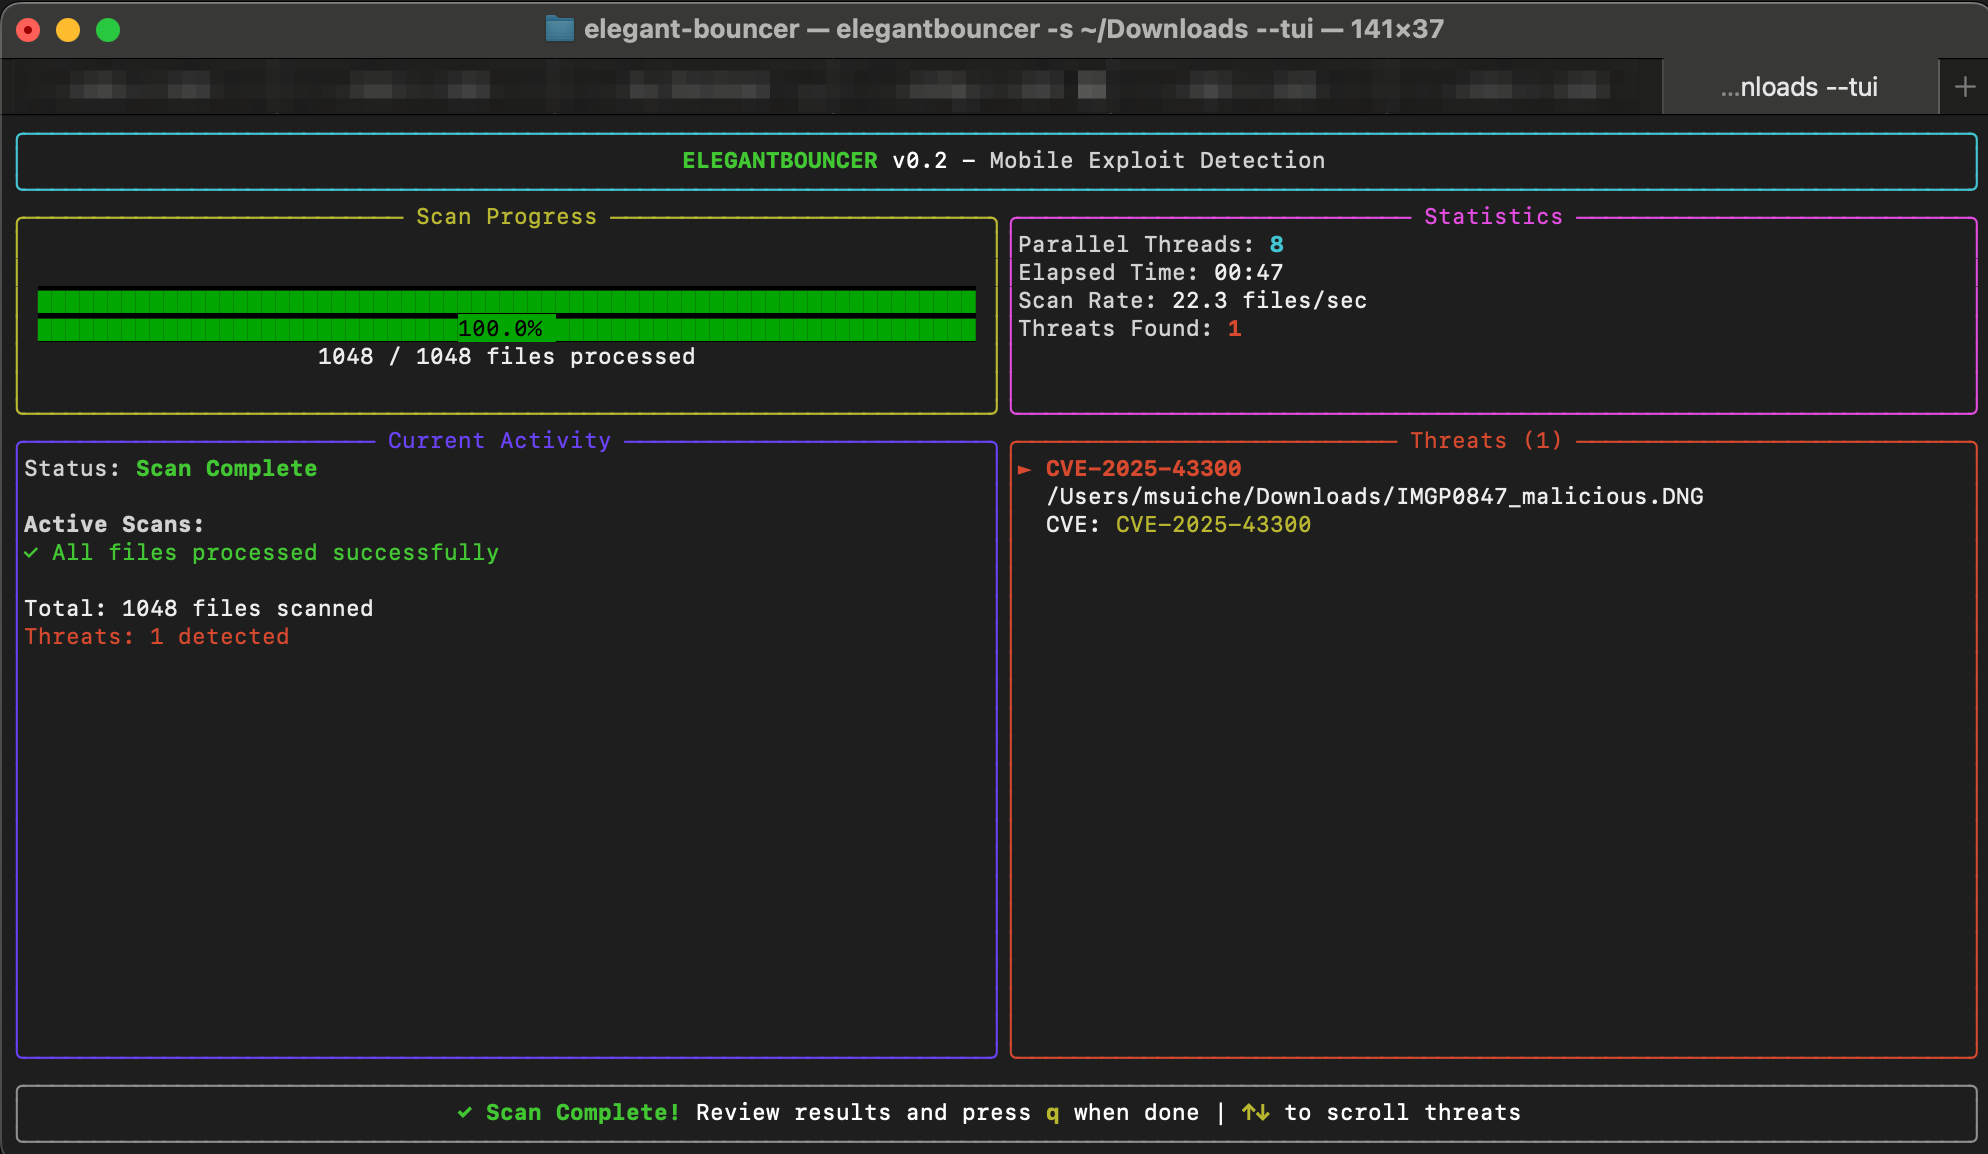
TUI 模式可实时可视化并行扫描操作,同时显示所有活动的工作线程。在扫描目录时使用 --tui 标志启用它。
elegant-bouncer v0.2
ELEGANTBOUNCER Detection Tool
Detection tool for file-based mobile exploits.

A utility designed to detect the presence of known mobile APTs in commonly distributed files.

Usage: elegant-bouncer [OPTIONS] <Input path>

Arguments:
  <Input path>
          Path to the input file or folder

Options:
  -v, --verbose
          Print extra output while parsing

  -s, --scan
          Assess a given file or folder, checking for known vulnerabilities

  -c, --create-forcedentry
          Create a FORCEDENTRY-like PDF

  -r, --recursive
          Recursively scan subfolders

  -m, --messaging
          Scan messaging app databases for attachments (iOS backup format)

  --ios-extract
          Extract/reconstruct iOS backup to readable folder structure

  -o, --output <OUTPUT>
          Output directory for iOS backup extraction

  -f, --force
          Force overwrite of output directory if not empty

  -e, --extensions <EXTENSIONS>
          File extensions to scan (comma-separated, e.g., "pdf,webp,ttf")
          Default: pdf,gif,webp,jpg,jpeg,png,tif,tiff,dng,heic,heif,hif,avif,ttf,otf

  -h, --help
          Print help information (use `-h` for a summary)

  -V, --version
          Print version information
使用 --scan 评估单个文件是否存在已知漏洞:
elegantbouncer --scan suspicious_file.pdf
扫描目录中所有受支持的文件:
elegantbouncer --scan /path/to/folder
使用 -r 标志递归扫描所有子目录:
elegantbouncer --scan /path/to/folder -r
使用 -e 标志指定要扫描的文件类型:
# Scan only PDF and DNG files
elegantbouncer --scan /path/to/folder -e pdf,dng

# Scan only image files recursively
elegantbouncer --scan /path/to/folder -r -e jpg,jpeg,png,webp,gif
默认情况下,该工具会扫描具有以下扩展名的文件:
扫描目录时,该工具会提供:
[+] Scanning directory: /path/to/documents
[+] Recursive mode enabled
[+] Extensions: pdf, gif, webp, jpg, jpeg, png, tif, tiff, dng, heic, heif, hif, avif, ttf, otf

[1] Scanning: /path/to/documents/invoice.pdf
[2] Scanning: /path/to/documents/photo.jpg
[3] Scanning: /path/to/documents/malicious.webp
  └─ THREAT found: BLASTPASS
[4] Scanning: /path/to/documents/report.pdf
  └─ THREAT found: FORCEDENTRY

[+] Scanned 4 files

[+] Summary Results:
╭────────────────┬───────────────────────────────┬──────────────────────────────────────────────────────────────────────────┬──────────╮
│ name           │ cve_ids                       │ description                                                              │ detected │
├────────────────┼───────────────────────────────┼──────────────────────────────────────────────────────────────────────────┼──────────┤
│ FORCEDENTRY    │ CVE-2021-30860                │ Malicious JBIG2 PDF shared over iMessage                                 │ Yes      │
│ BLASTPASS      │ CVE-2023-4863, CVE-2023-41064 │ Malicious WebP presumably shared over iMessage and other mediums         │ Yes      │
│ TRIANGULATION  │ CVE-2023-41990                │ Maliciously crafted TrueType font embedded in PDFs shared over iMessage  │ No       │
│ CVE-2025-43300 │ CVE-2025-43300                │ Malicious DNG with JPEG Lossless compression exploiting RawCamera.bundle │ No       │
╰────────────────┴───────────────────────────────┴──────────────────────────────────────────────────────────────────────────┴──────────╯

[!] Infected Files Details:
╭────────────────────────────────┬─────────────┬───────────────────────────────╮
│ path                           │ threat_name │ cve_ids                       │
├────────────────────────────────┼─────────────┼───────────────────────────────┤
│ /path/to/documents/report.pdf  │ FORCEDENTRY │ CVE-2021-30860                │
│ /path/to/documents/malicious.webp │ BLASTPASS   │ CVE-2023-4863, CVE-2023-41064 │
╰────────────────────────────────┴─────────────┴───────────────────────────────╯
将 iOS 备份重建为可读的文件夹结构:
# Extract backup to default location (creates _reconstructed folder)
elegantbouncer --ios-extract /path/to/ios/backup

# Extract to specific output directory
elegantbouncer --ios-extract /path/to/ios/backup -o /path/to/output

# Force overwrite if output directory exists
elegantbouncer --ios-extract /path/to/ios/backup -o /path/to/output --force
扫描 iOS 备份中即时通讯应用里的恶意附件:
# Scan messaging databases (iMessage, WhatsApp, Viber, Signal, Telegram)
elegantbouncer --scan --messaging /path/to/ios/backup

# Combine with extraction for complete analysis
elegantbouncer --ios-extract /path/to/ios/backup -o /tmp/extracted
elegantbouncer --scan --messaging /tmp/extracted
此功能可检测来自以下来源的附件中的威胁:
使用 --create-forcedentry 从头生成一个旨在利用 CVE-2021-30860 的 PDF。仍在开发中。
注意:预置样本可在 samples/ 目录中找到。
如果你认为自己可能是被关注的目标,请使用 锁定模式 来减少你的攻击面。









