

N0xis
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
static-analysisdynamic-analysis-sandboxingmemory-forensics+7
2
 habanada/nativepe
Object Pascal (Delphi) 库,用于解析、映射、加载和转储 Windows PE 文件,支持重定位、导入、TLS 以及远程进程内存读取。
 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
 pdb333/cortex
一个Windows运行时分析工具包,结合了内存扫描、调试、自动化和AI友好的API。
 liuz233/harde
HARDE 的研究代码,这是一个 agent harness,用于探测并自适应优化组件,以在各类 agent 安全基准测试中实现运行时风险检测与执行控制。
 akatorich/kernelflirt
Windows 内核级调试器,具有 OllyDbg/IDA 风格的 UI、软件和硬件断点、PDB 符号、反编译器,以及 17 个用于在虚拟机中进行逆向工程和恶意软件分析的插件。
 ejfkdev/jd
Go CLI,用于反混淆 javascript-obfuscator (obfuscator.io) 的输出,并通过 AST 转换、静态解码和 goja 沙箱回退来反压缩 JavaScript。
 gmh5225/hooktools
用于分析规避型恶意软件行为的基础注入工具
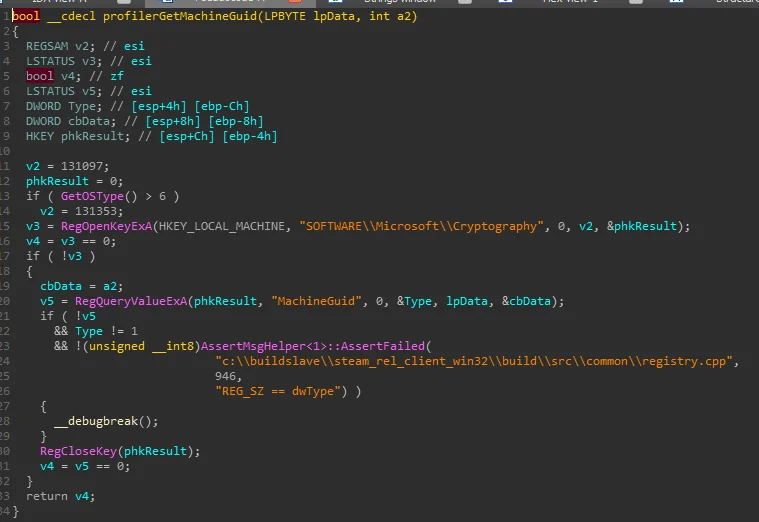 gmh5225/hwid-steamspywareterminator
正在开发中的库,注入 Steam 以阻止隐藏的 CFillMachineInfoThread,该线程会收集 HWID、磁盘、网络适配器和注册表指纹数据。
 ejfkdev/dae
基于配置驱动的 Dart AOT 快照分析器,可导出与 blutter 兼容的符号和结构体,供 IDA、radare2 和 Frida 使用,并能将函数反编译为 dart-analyze-clean Dart,无需 Dart SDK。
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 iterat0r/cnaemulator
用于 Cobalt Strike Aggressor Scripts(.cna)的独立仿真与测试框架,可在没有 teamserver 的情况下验证语法、模拟 Beacon API,并通过 COFFLoader 执行 BOF。
 sunghoojung/reverse-engineering-browser
基于自定义 Brave 构建的本地优先 macOS 研究浏览器,可捕获网络流量、指纹、脚本和运行时证据,用于对 Web 应用进行逆向工程。
 fkie-cad/sandroid_dexray-intercept
一款Android恶意软件分析工具,通过挂钩应用程序在密码学、文件系统、数据库、网络通信和进程操作方面的行为,创建全面的运行时配置文件。
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
 githubsecuritylab/seclab-taskflows-fuzzing
一个由 GitHub Security Lab Taskflow Agent 驱动的 LLM 驱动模糊测试流水线
 alex66366/odpure
黑盒输入阶段净化防御,通过损坏、扩散重建和DBSCAN共识投票来中和针对目标检测器的后门攻击。