

RXScan
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…
defensive-toolsosintreconnaissance+8
1
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 albertrg99/redditosint
按用户名进行 Reddit OSINT。发现已索引的帖子、评论、已删除和实时内容、活动模式、暴露的标识符以及总体暴露评分。
 star-sg/random-scripts
用于解析恶意 LNK 样本、从 MHTML 中提取 OLE 对象以及对 favicon 进行哈希以追踪钓鱼站点的 DFIR 和 OSINT Python 脚本集合。
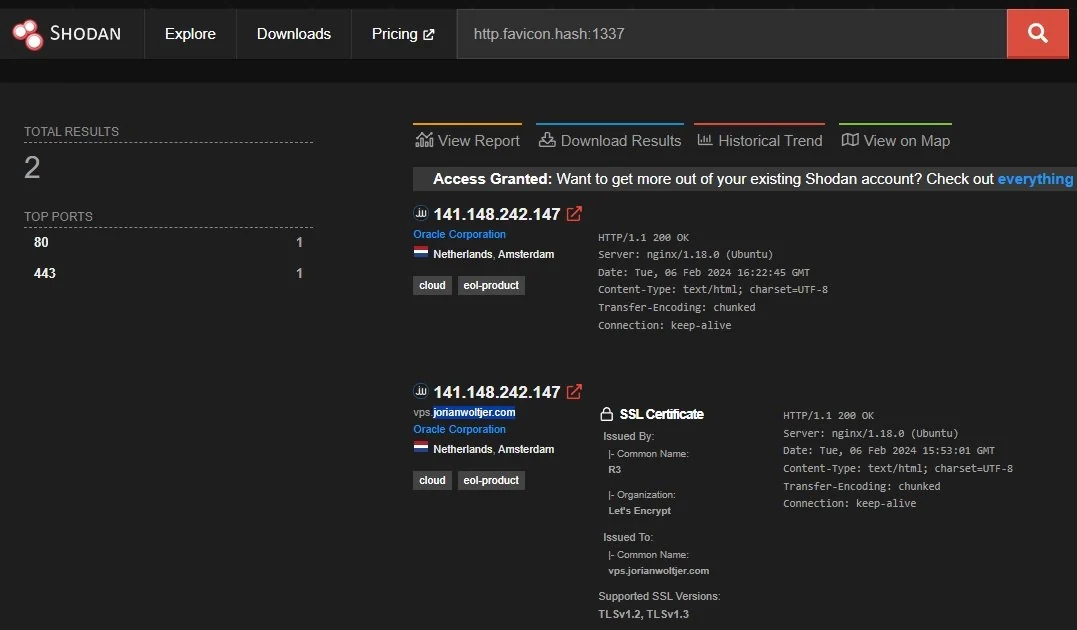 jorianwoltjer/shodan-favicon-preimage
生成一个在 Shodan 上可得到任意目标哈希的 favicon

 vqkro/higernes
a passive OSINT toolkit in python and c++ usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 ankhcorp/nuke.sh
基于 Bash 的被动侦察 + 攻击面测绘脚本,仅使用公共 API + 标准 Linux 工具(curl、dig、openssl、nmap、python3)。
 ejfkdev/oss
Cross-cloud S3-compatible object storage CLI to list, export, and download buckets across AWS, Aliyun, Tencent, Huawei and more, with anonymous…
 ejfkdev/dj
通过静态分析网站 HTML 和 JS,检测 webpack 分块、import() 懒加载和源映射,动态提取动态加载的 JavaScript 文件以进行侦察。
 ooafa/bucketbuster
扫描 Yandex、VK、Selectel、Sber、Alibaba、Tencent、Huawei 和 Baidu 的公共云对象存储端点,以查找可列出存储桶和暴露的对象。
 emrekybs/socmintelligence
一个模块化的 OSINT 与 SOCMINT 框架,用于社交媒体情报、调查和公开数据分析。
 rix4uni/wordlist
用于模糊测试、DNS枚举、参数发现和默认凭据的自定义字典精选集合,以及用于nuclei技术字典的Go生成器。
 mmarting/unwaf
Go 工具,通过多个 OSINT 来源被动发现 WAF/CDN 背后的真实源站 IP,然后通过 HTML 相似度、SSL 证书指纹和 HTTP 头验证候选 IP。
 cisagov/findcdn
通过指纹识别 HTTPS 头、CNAME 记录和 WHOIS 数据来扫描域名,以识别其使用的内容分发网络 (CDN),支持 JSON 输出和模块扩展。
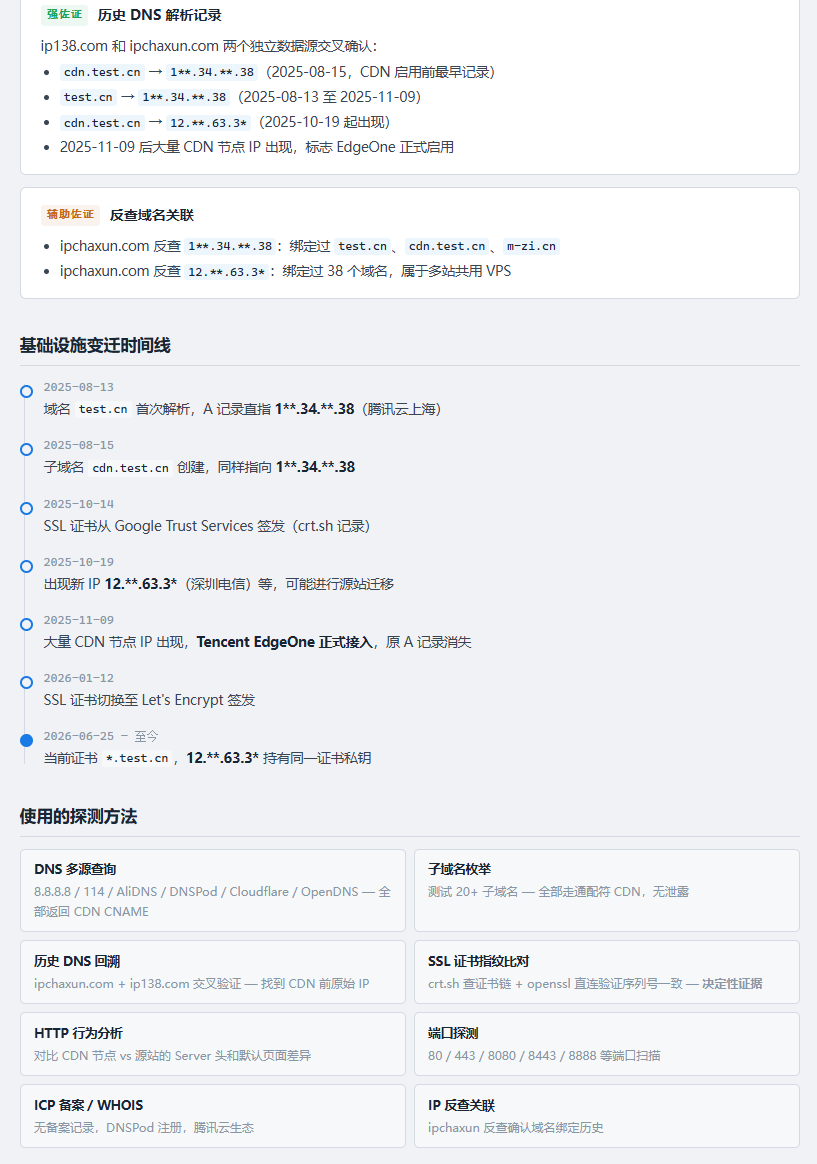 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
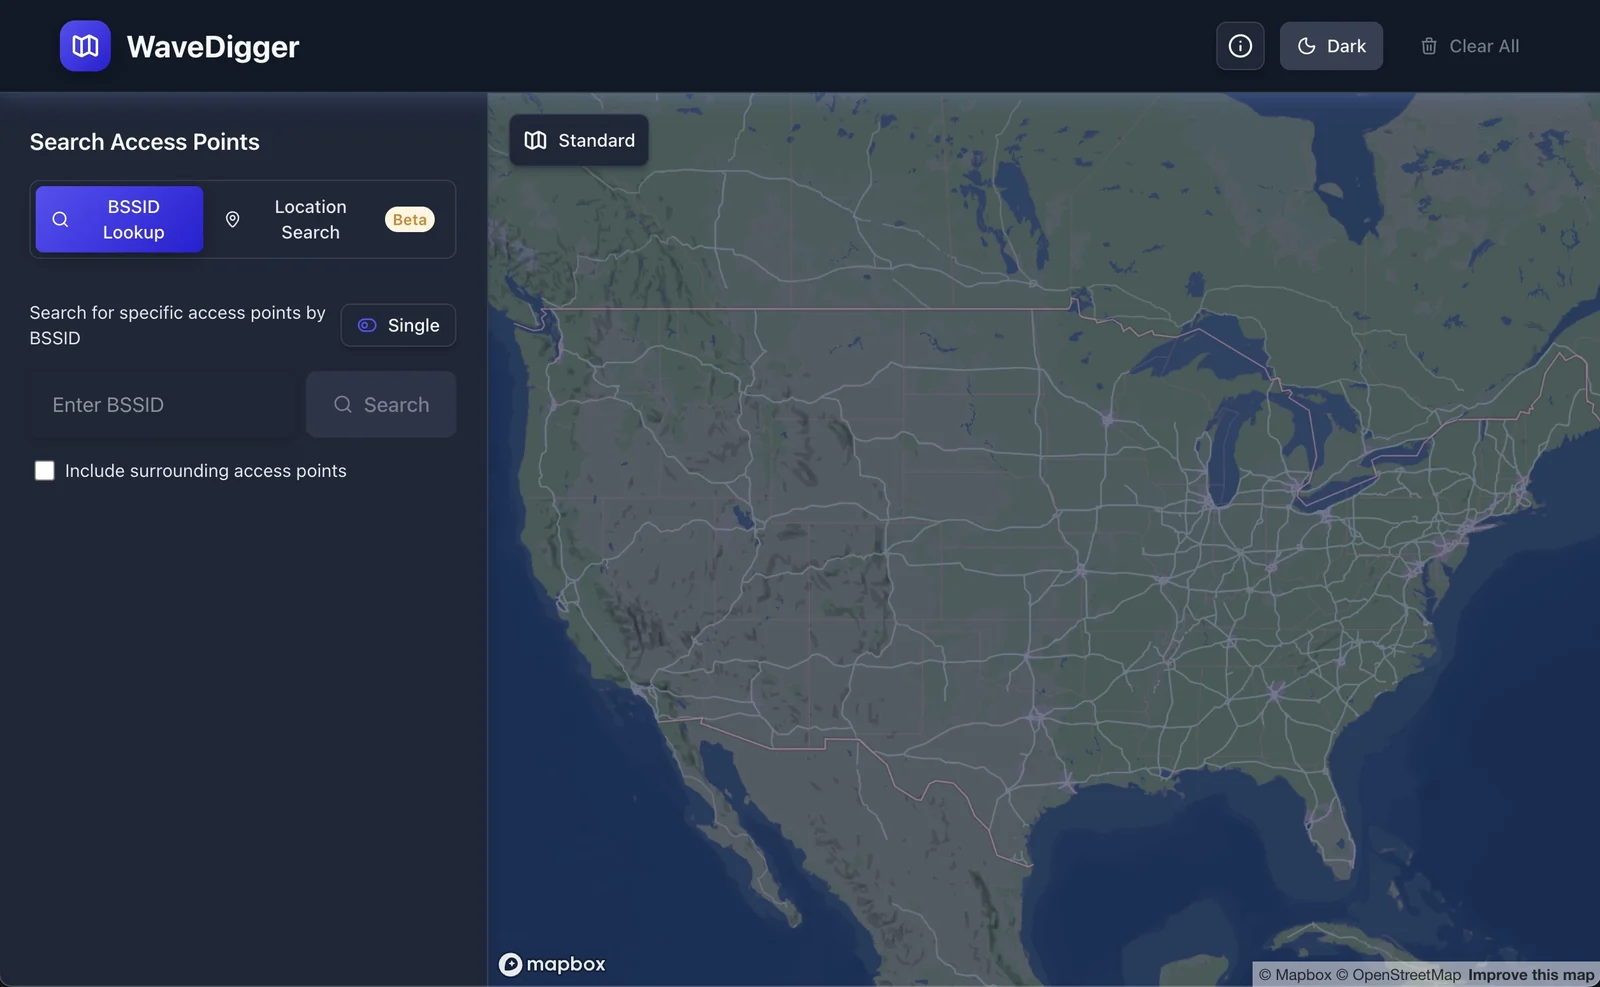 christianrowlands/wavedigger
在 Apple 公共 WPS 服务中搜索 BSSID
 m4elstr0m/gophoner
同时检查一个电话号码是否在热门应用和网站上注册,无需任何前提条件 📞