

CanoP
 openbreach/canop
静态分析CLI,用于扫描AI生成的代码中的漏洞,如SQL注入、不安全反射和硬编码密钥,并支持SARIF导出和CI/CD门禁。
defensive-toolsstatic-analysisvulnerability-scanners+7
 gmh5225/enigma-
Ghidra 分析核心的 C++ 重新实现,不依赖 JVM,提供可嵌入的二进制分析、Pcode/Sleigh 基础以及面向逆向工程的 AI 就绪接口。
 gavmor/x86-cpp-reversing-skill
用于逆向工程32位小端x86 C++二进制文件(虚表、RTTI、继承关系恢复)的Claude Code技能
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 martian56/redcell
AI 红队平台。自主 LLM 智能体在 Kali 容器内端到端执行渗透测试并撰写报告。LangGraph 计划/执行引擎,通过 LiteLLM 实现提供商无关的模型,输出 PDF/JSON/SARIF。FastAPI + React。
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 offensive360/mcp-server
MCP 服务器,可在本地代码库上运行 SAST 扫描,并返回带有严重级别和修复建议的发现结果,使 AI 助手能够执行安全分析和修复。
 lgranadoi/sift-hardened
# 针对 CVE-2026-85625 的 sift 17.1.3 安全加固分支。与 crcn/sift.js 无关联。
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 safeagent-beihang/clawguard
Enterprise AI agent security toolkit providing pre-flight auditing, configuration hardening, runtime threat detection, and active defense against…
 geeksikhsecurity/ai-tool-poisoning-guard
Free security-baseline rule for Claude Code, Codex, and Cursor: treats MCP tool descriptions as untrusted input (OWASP MCP Top 10 MCP03,…
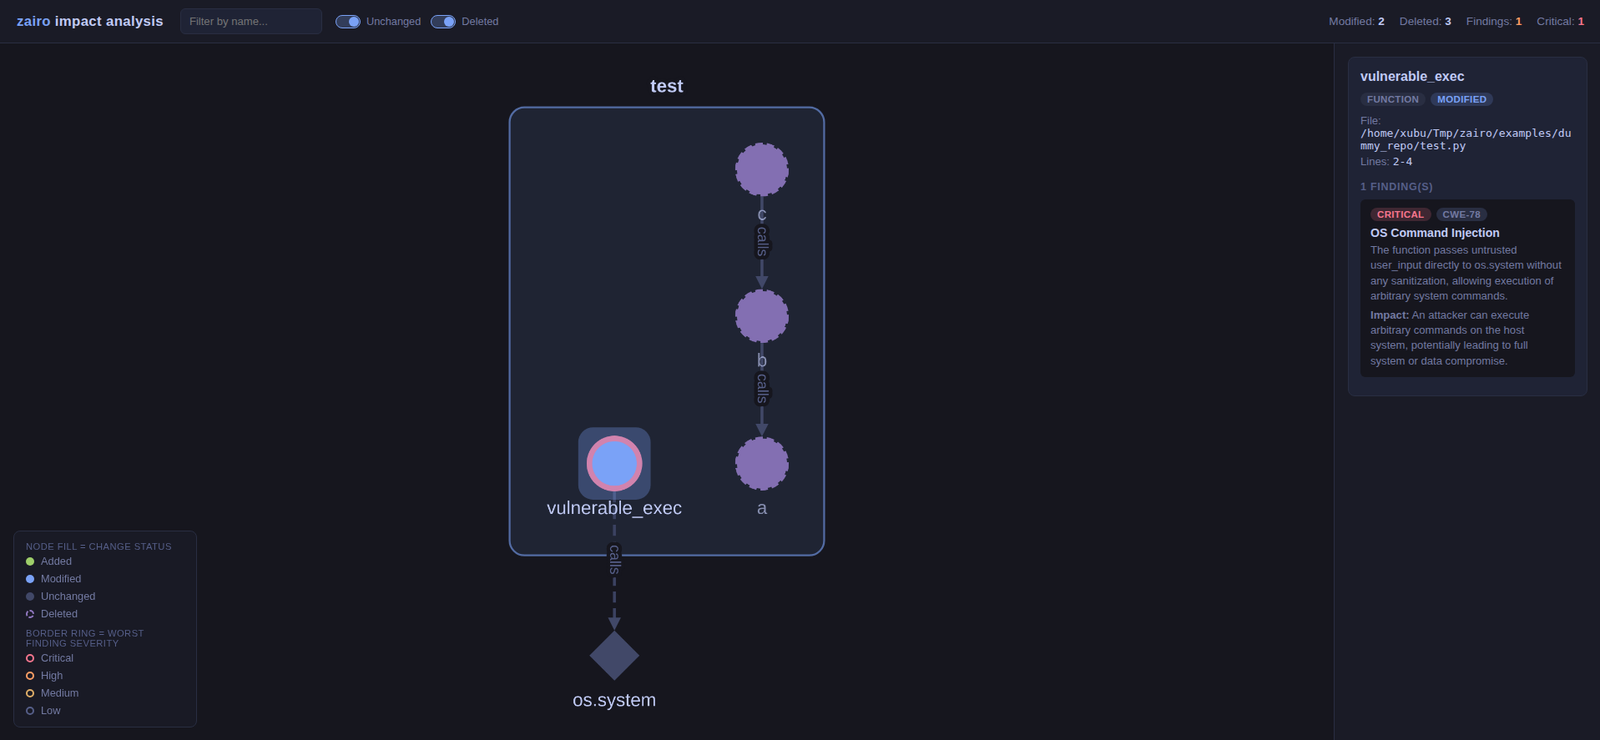 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 dannydoodlesstory/evm-audit-helpers
智能合约安全审计的 Solidity 代码片段与 Foundry 脚本合集
 javascript-obfuscator/javascript-obfuscator
混淆JavaScript和Node.js代码,通过变量重命名、字符串加密、控制流扁平化和反调试技术,保护源代码免受逆向工程。