ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…

基于 Rust 的 HTTP 请求走私扫描器。

Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100

针对 21 个端点验证 Google Maps API 密钥,揭示暴露的服务及其 PoC URL,支持代理,并提供安静模式以进行聚焦审计。

发现 Caido 中的隐藏参数

一个 Burp Extender 插件,它将使用 Xtream 库将反序列化的 AMF 对象编码为 XML。

一个用于识别参数注入漏洞的 Burp 扩展。

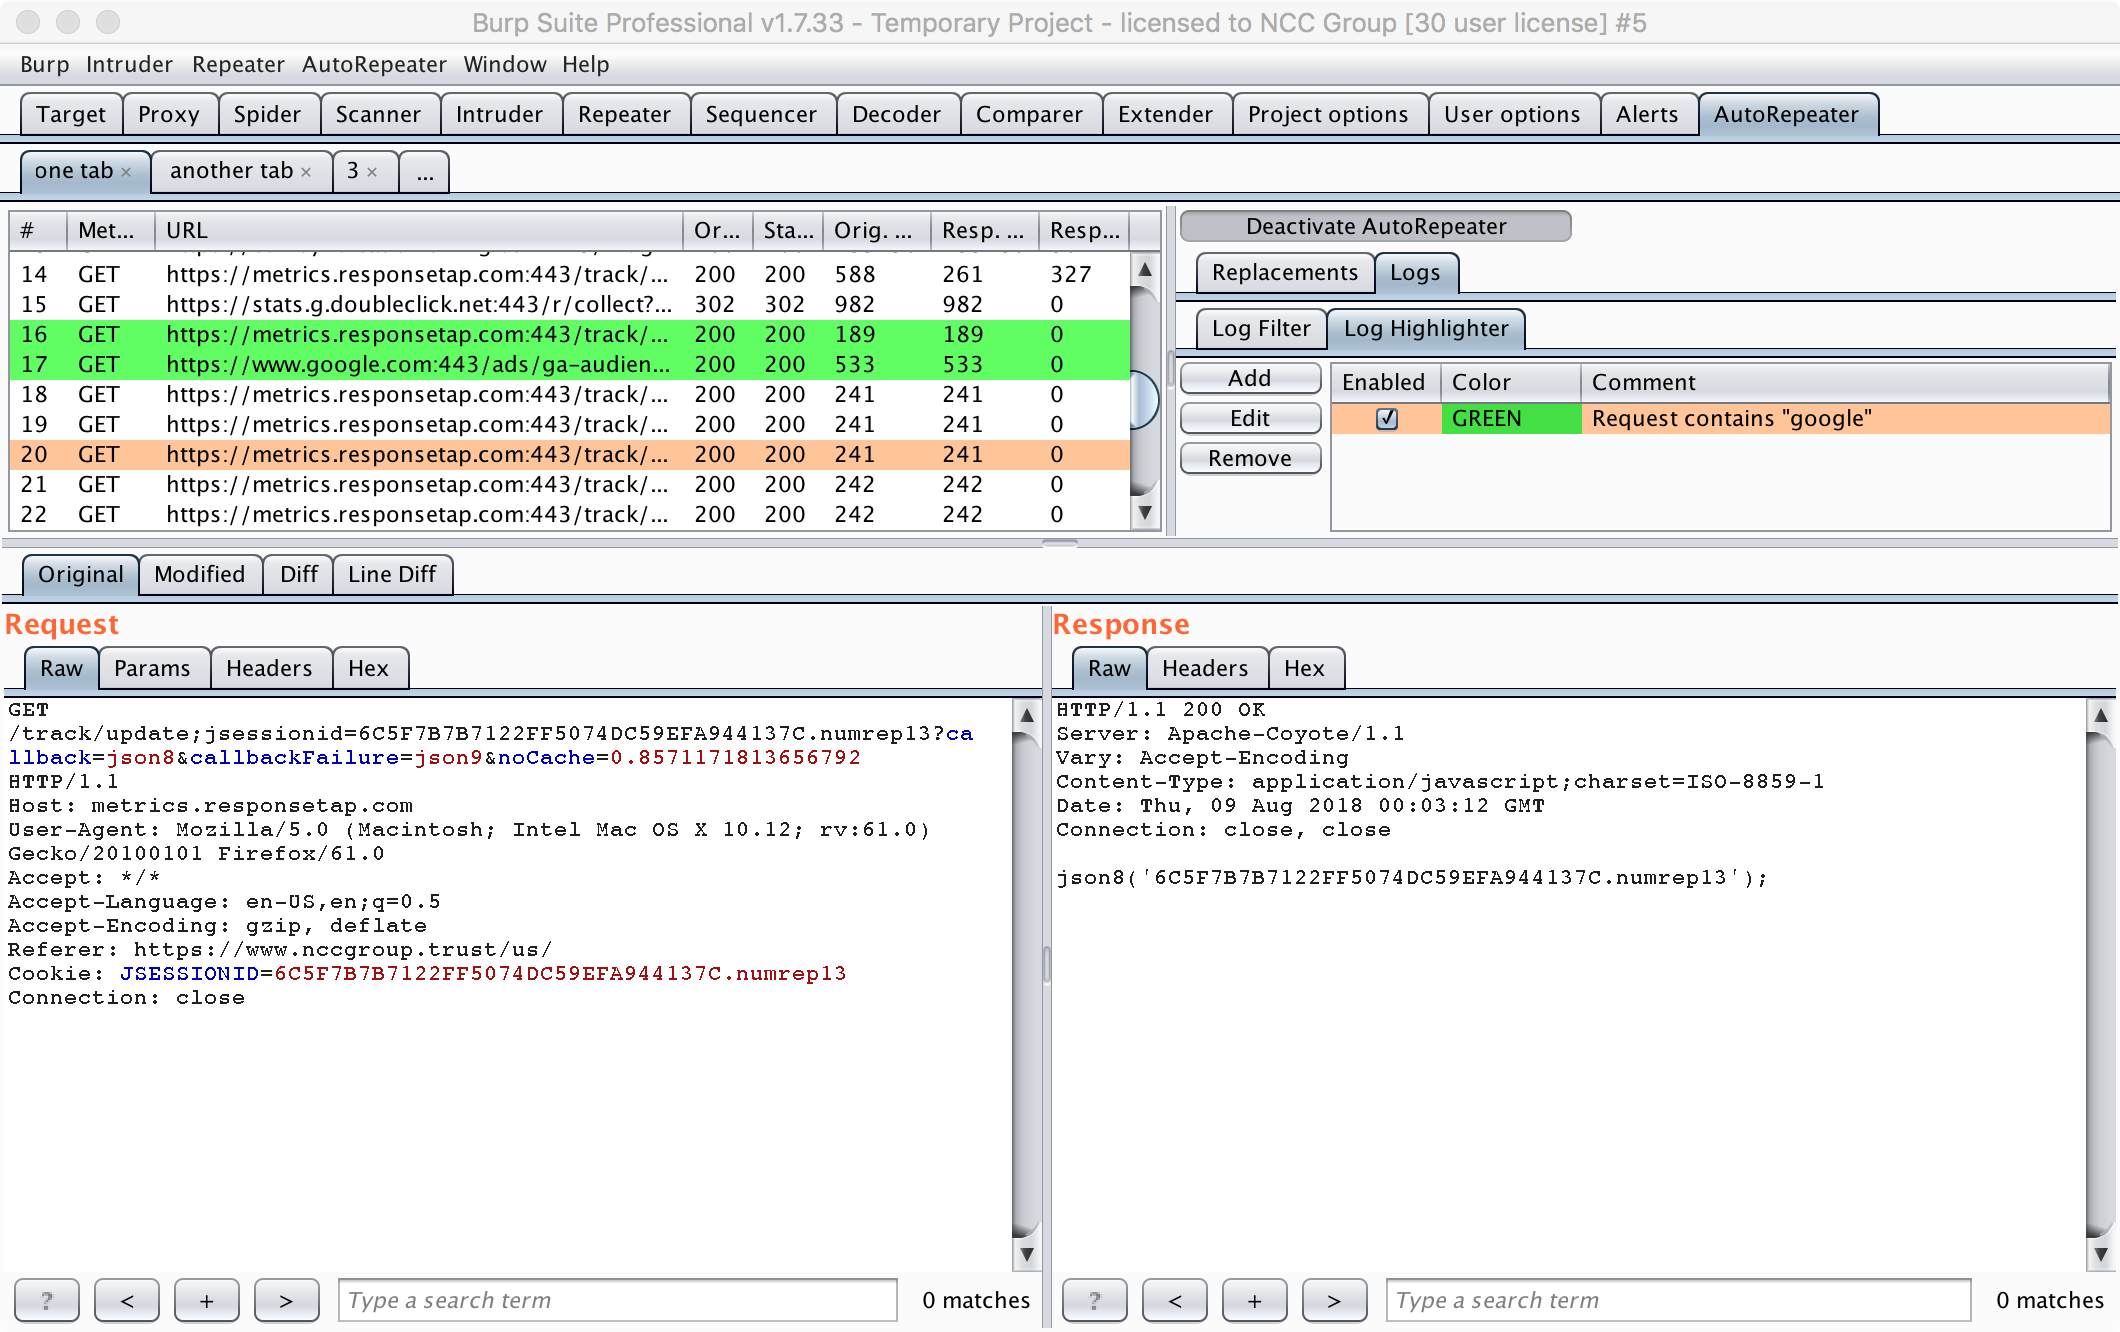
使用 Burp Suite 自动重放 HTTP 请求

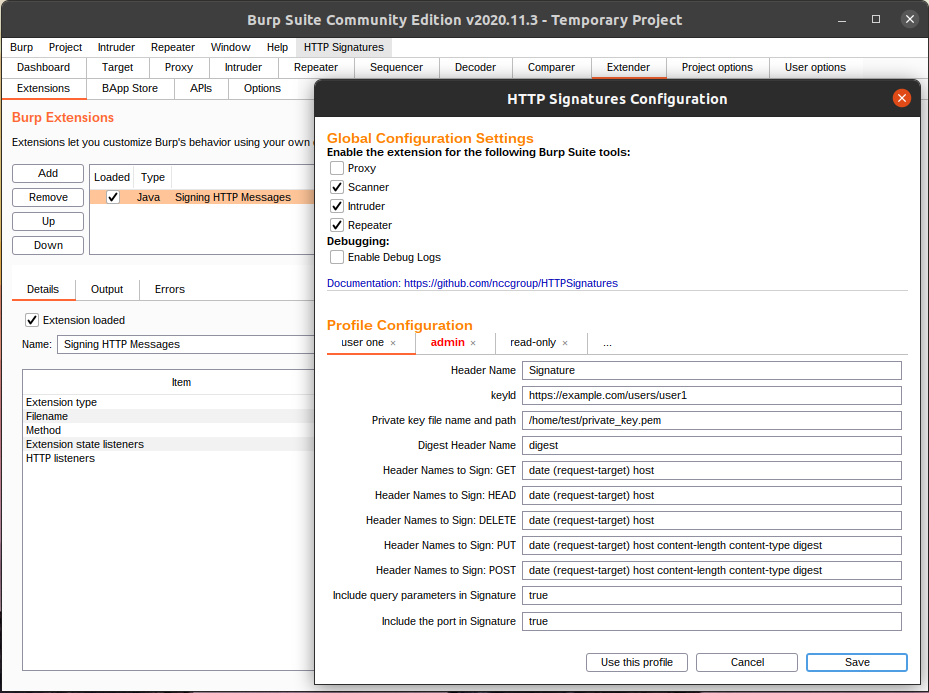
一个实现 Signing HTTP Messages draft-ietf-httpbis-message-signatures-01 草案的 Burp Suite 扩展。

一个 Burp Extender 插件,用于让二进制 SOAP 对象可读且可修改。

一款无头、可脚本化、基于命令行的 MITM 代理,专为在 Windows 系统上进行网络流量拦截、分析和修改而设计。

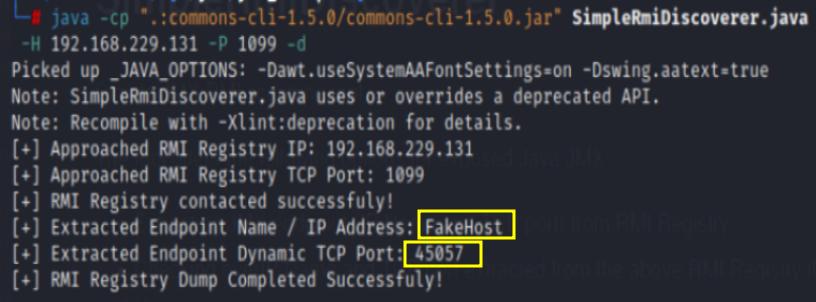
简单的 JMX RMI 扫描工具

HopLa Burp Suite Extender 插件 - 为 Burp Suite 带来 AI 功能、自动补全支持以及一组实用的 payload

Scans public code repositories and code snippet platforms to extract and validate AI service API keys with real-time dashboard and multi-format…

从 ServiceNow 实例中发现敏感数据泄露。

全面的Web应用安全测试平台,具有先进的扫描引擎、拦截代理和自动漏洞检测功能,专为渗透测试人员设计。

Super Vulnerable Java Application (SVJA) 在 Roniel 和 DaRon 播客秀中进行了演示,它是一个 Apache Struts 应用程序,旨在包含大量非常常见的漏洞。与其他“故意存在漏洞”的软件不同,该软件旨在模仿常见漏洞在现实中最常见的呈现方式,而不是…

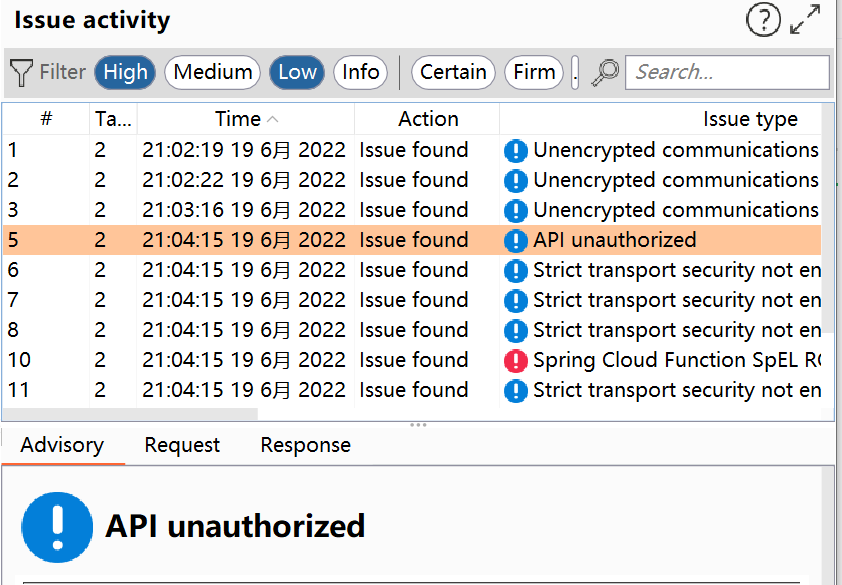
burpsuite 的Spring漏洞扫描插件。SpringVulScan:支持检测:路由泄露|CVE-2022-22965|CVE-2022-22963|CVE-2022-22947|CVE-2016-4977