
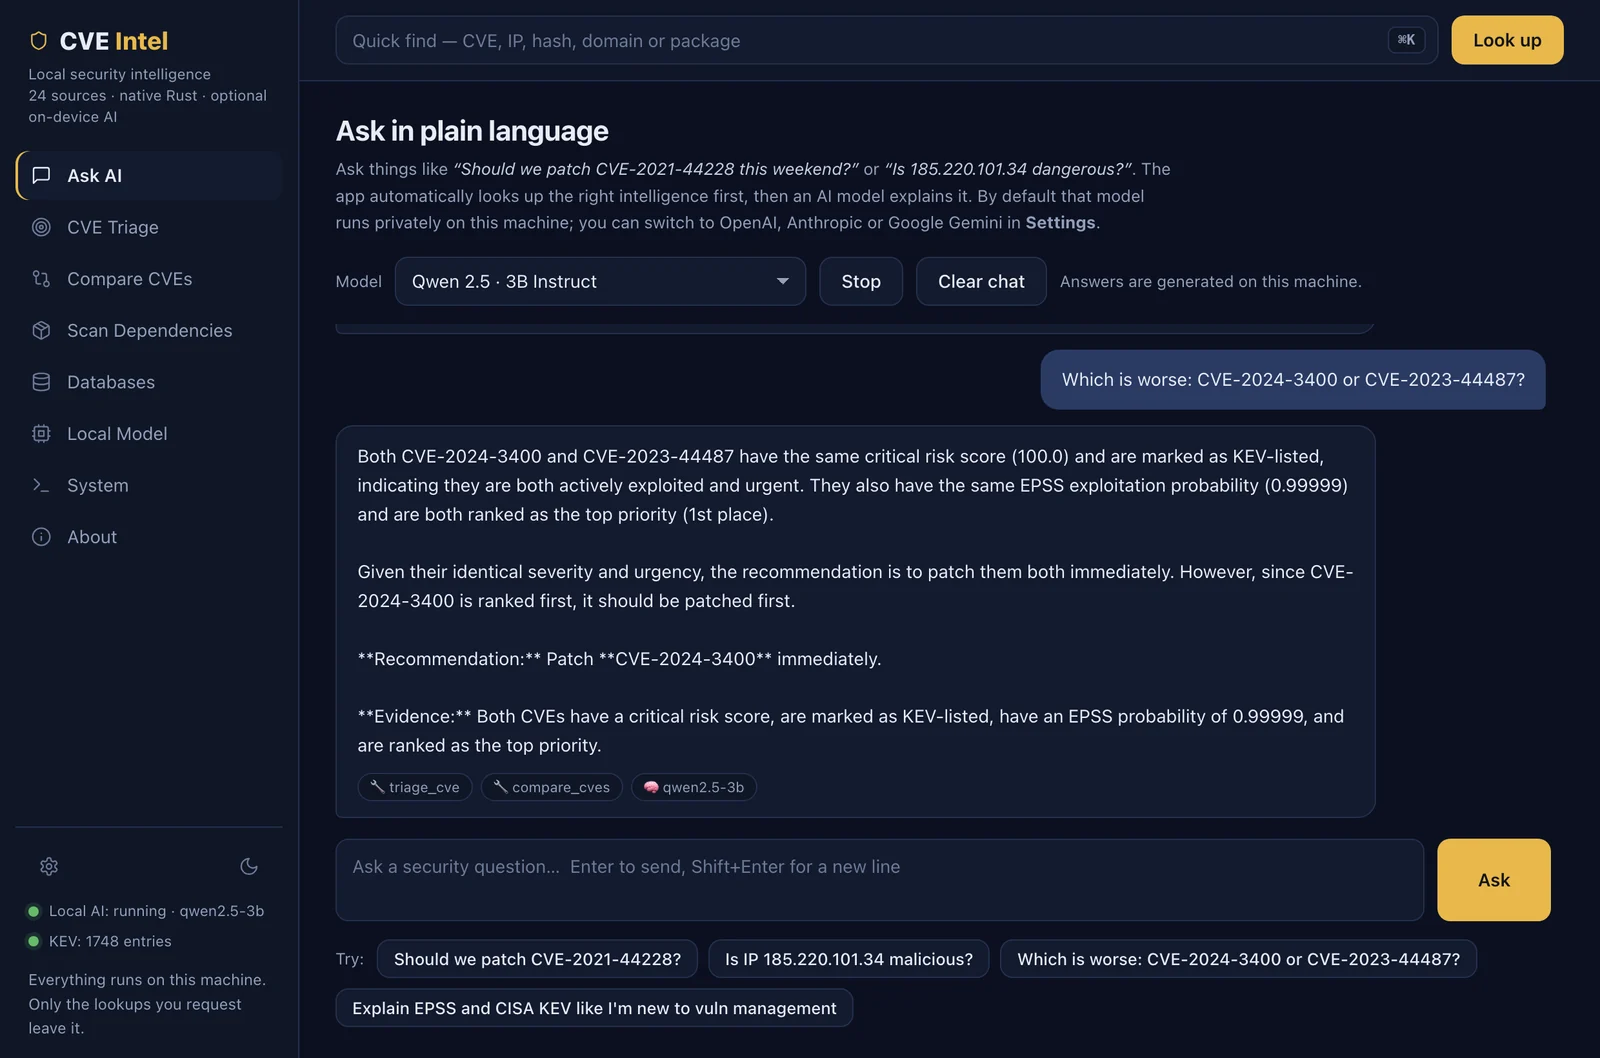
cve-intel
 fazmin/cve-intel
CVE 트리아지를 위한 로컬 보안 인텔리전스 — 31개 도구, 25개 소스, 위험 점수, 그리고 AI 에이전트용 MCP 서버까지, 모두 네이티브 Rust로 구현. 기본적으로 프라이빗.
ioc-managementosintvulnerability-scanners+8
515시간 59분 전
 blackvectorops/semantic_firewall
Generate deterministic semantic fingerprints for Go functions. Detect xz-style backdoors and verify semantic equivalence using Static Single…
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 anthropics/oss-scanner
등록된 오픈소스 저장소를 격리된 오프라인 VM에서 빌드하고 보안 취약점을 스캔하여 재현기와 제안된 패치와 함께 결과를 이메일로 전송하는 서비스입니다.
 vulncheck-oss/cli
VulnCheck's official command line tool
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
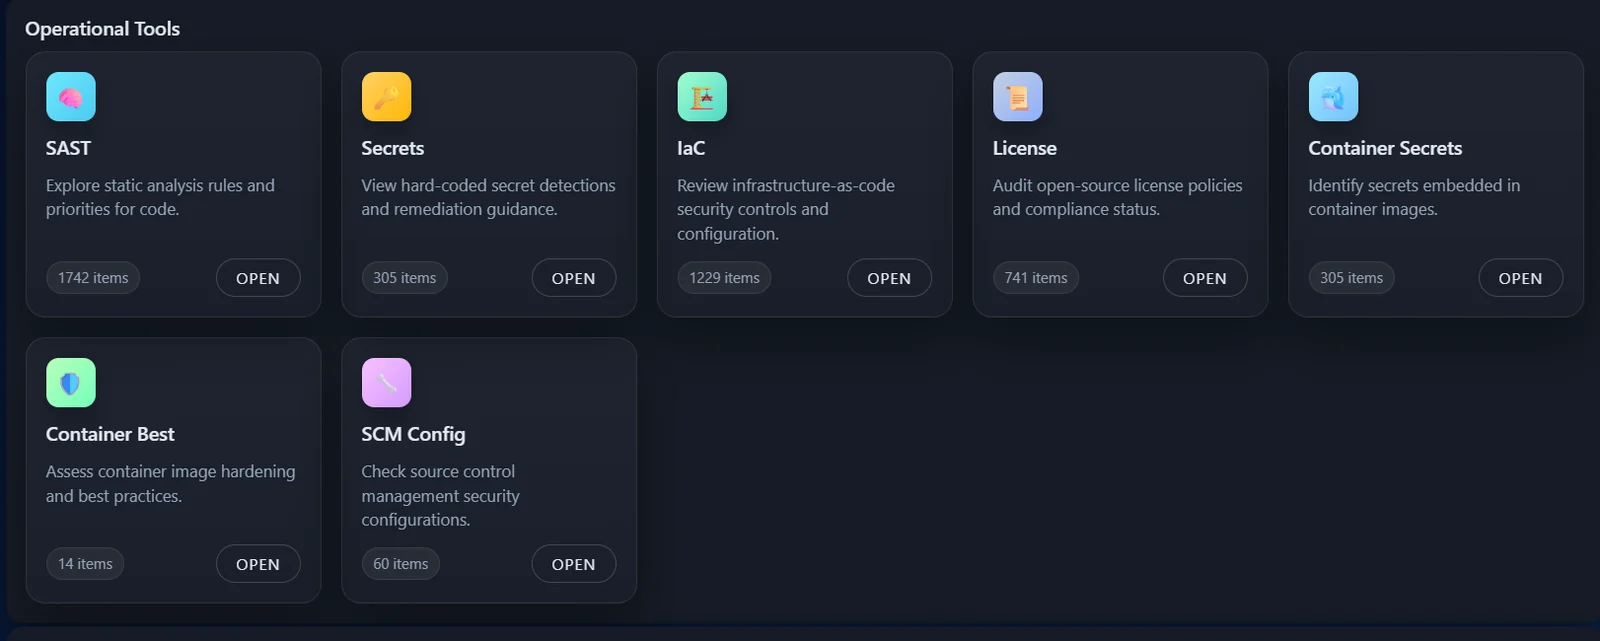 viralmaniar/vulnvault
Developer-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…
 gmh5225/jataayu
LLM 기반 AI 에이전트 보안 — 인바운드 주입 탐지 + 아웃바운드 프라이버시 보호
 owasp/owasp-top-10-neocloud-and-ai-data-center-security-risks
OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…
 niffyhunt/wraithwall-toolkit
Deception-engineering tools pulled from a production platform that takes live attacker traffic, supply-chain canary tokens, honeypot logs → MITRE…
 dmdhrumilmistry/security-harness
AI 코딩 에이전트를 위한 멀티 에이전트 정적 애플리케이션 보안 검토 하네스: 코드베이스를 매핑하고, 취약점 클래스를 추적하며, 발견 사항을 연쇄 검증하고, SARIF, JSON, PDF로 보고합니다.
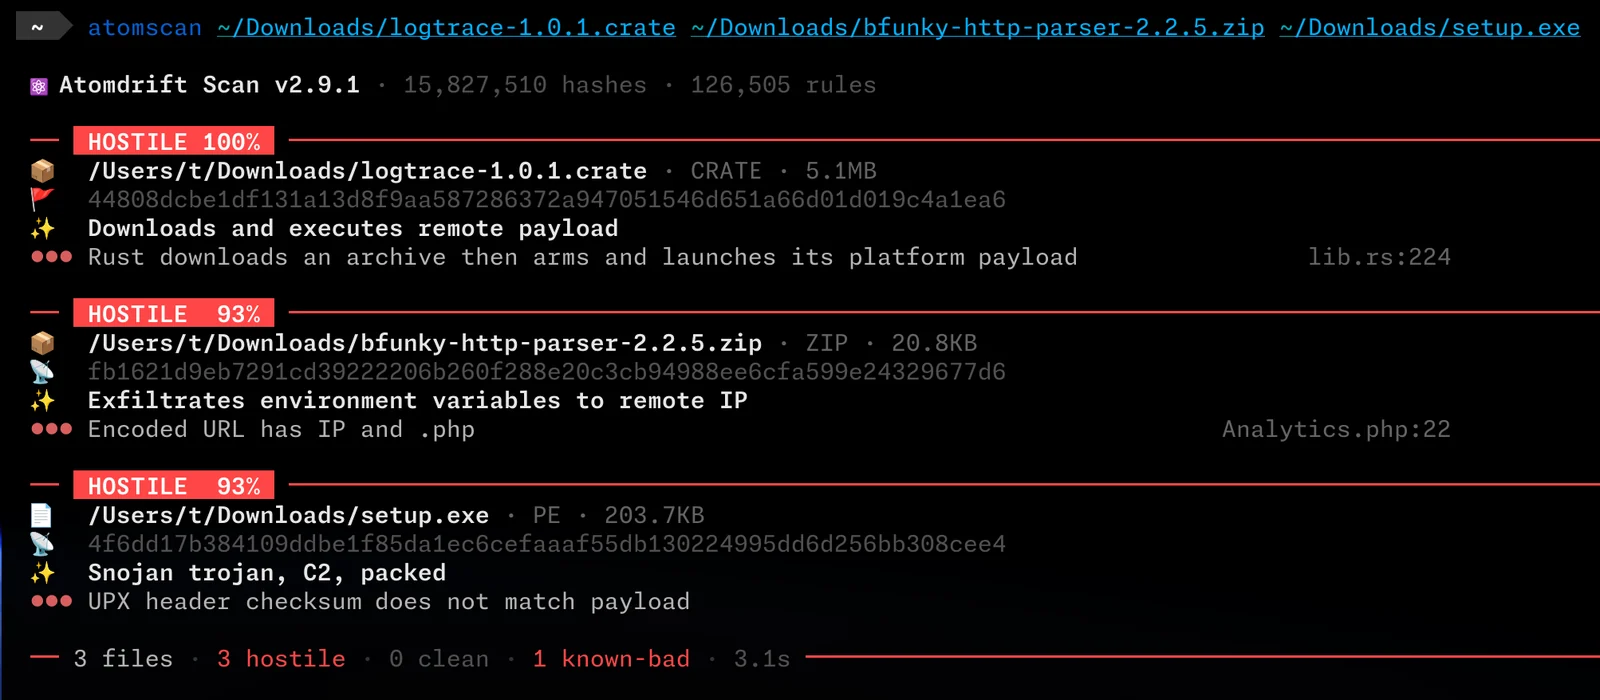 atomdrift-project/scan
바이너리, 소스 및 스크립트를 위한 0-day 악성코드 탐지 (별로 안 별로인 것)
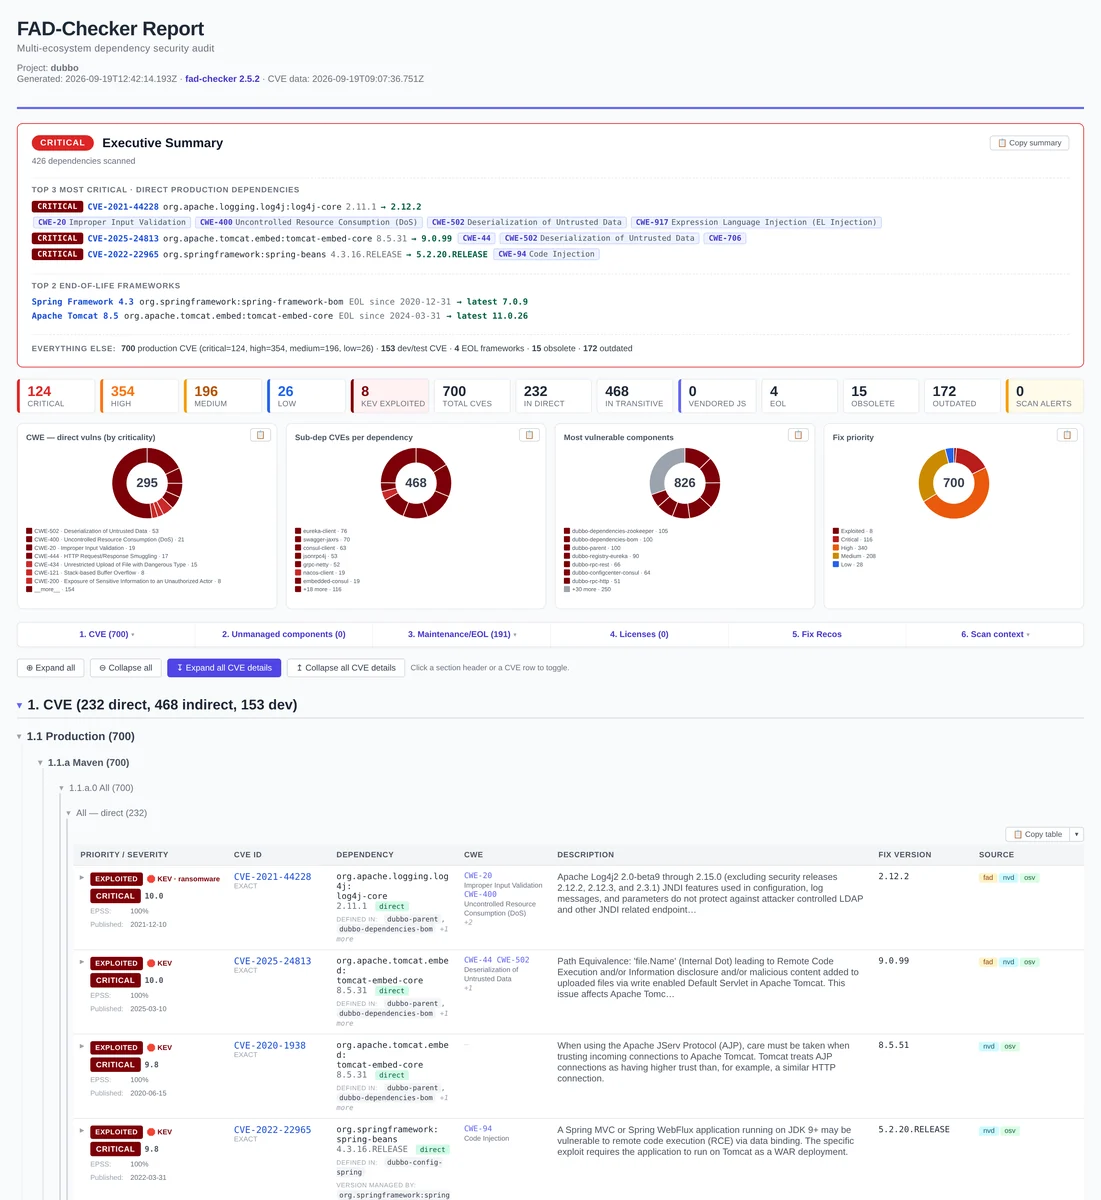 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 navikt/cplt
AI 코딩 에이전트를 위한 샌드박스. Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose 또는 일반 셸을 커널 수준 샌드박스 내에서 실행하며, git 및 gh 가드와 샌드박스 정책이 저장소에…
 nationwide-group-oss/cryptoptic
CodeQL 기반 스캐너로, 리포지토리와 GitHub 조직 전반의 암호화 함수 호출을 목록화하여 SARIF 형식의 암호화 자재 명세서(CBOM)를 생성합니다.
 vpierre/ndaal_public_sbom_auditor
CycloneDX, SPDX 및 syft SBOM을 수집하고, CVE 스캐너 앙상블을 실행하며, EPSS, CISA-KEV 및 nuclei로 결과를 보강하고, SARIF, CSAF 및 PDF로 내보내는 오프라인 단일 바이너리 웹 앱입니다.
 mubix/ai-ctf
프롬프트 인젝션, 도구 호출 악용, 그리고 6개의 시뮬레이션된 챗봇 페르소나를 대상으로 한 OSINT에 관한 가이드 레슨을 제공하는 로컬 AI 캡처 더 플래그 플랫폼.