 niffyhunt/wraithwall-toolkit
Deception-engineering tools pulled from a production platform that takes live attacker traffic, supply-chain canary tokens, honeypot logs → MITRE ATT&CK scoring, and a signed, versionable deception-config spec. Pure Python, MIT.

Four deception-engineering tools, lifted out of a production security platform that takes live internet traffic, cleaned of all product/secret coupling, and released under MIT.
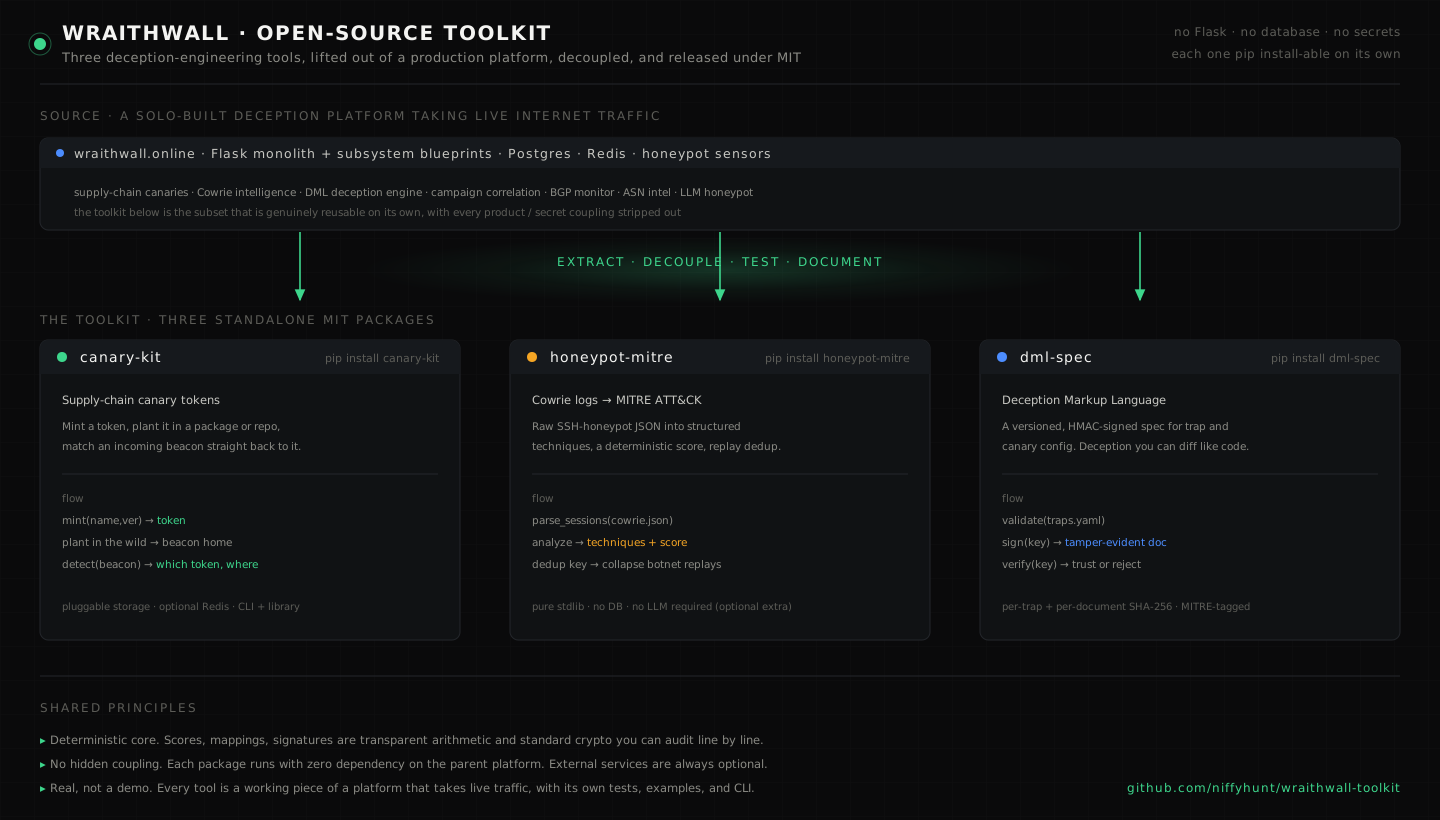
This isn't a lab demo. Each tool is a piece of WraithWall — a solo-built deception platform running behind a reverse proxy with a honeypot feeding it around the clock. These are the parts that are genuinely reusable on their own: if you run a honeypot, plant canaries, or want your deception config versioned like code, they're for you.
Every project is a standalone, pip install-able package with its own README, examples,
tests, and CLI. No dependency on the platform — no Flask, no database, no secrets.
| Project | What it does | Install | PyPI |
|---|---|---|---|
| canary-kit | Mint, register, and detect supply-chain canary tokens — match an incoming beacon straight back to the token you planted. Pluggable storage, optional Redis. | pip install canary-kit | Published 0.1.0 |
| honeypot-mitre | Turn raw Cowrie honeypot logs into structured MITRE ATT&CK techniques, a deterministic score, and replay dedup — no LLM required (it's an optional extra). | pip install honeypot-mitre | Published 0.1.0 |
| dml-spec | Deception Markup Language — a versioned, HMAC-signed spec for trap/canary config. Validate, sign, and verify so your deception is diffable and tamper-evident. | cd dml-spec && pip install . | v2 (0.2.0 ready, not uploaded yet) |
| wraithmesh | Distributed sensor mesh — tail Cowrie logs, collapse campaigns locally, uplink signed equivalence-class observations to corroborating aggregators. Privacy-preserving egress by default. | cd honeypot-mitre && pip install . && cd ../wraithmesh && pip install . | v2 (0.2.0 ready, not uploaded yet) |
Related published packages outside this folder: wraithwall (platform), ravenscan (raven CLI).
HTTP API client will be wraithwall-sdk (still building; not this toolkit).
See PACKAGE_INVENTORY.md for the full v2 release checklist.
# 1. Canary Kit — mint a token, then detect its beacon
cd canary-kit && pip install .
canary-kit --registry demo.json mint internal-sdk 2.4.1 --type runtime
# ...the token later beacons home from an environment you don't control:
canary-kit --registry demo.json beacon <token-from-mint> --ip 198.51.100.23

# 2. Honeypot → MITRE — raw cowrie log to scored, mapped sessions
cd ../honeypot-mitre && pip install .
honeypot-mitre examples/sample_cowrie.json     # → per-session techniques + score + dedup key

# 3. DML — validate, sign, and verify a deception document
cd ../dml-spec && pip install .
export DML_KEY="your-signing-key"
dml validate examples/example_traps.yaml
dml sign     examples/example_traps.yaml --key-env DML_KEY > signed.yaml
dml verify   signed.yaml --key-env DML_KEY

# 4. WraithMesh — Cowrie tail to signed campaign observations
cd ../wraithmesh && pip install .
export WRAITHMESH_KEY="demo-key"
wraithmesh init-manifest --output /tmp/mesh.json
wraithmesh sensor run --config /tmp/mesh.json --once --log ../honeypot-mitre/examples/sample_cowrie.json
See each project's README for the full API, CLI, and design notes.
pyproject.toml.All four projects are released under the MIT License — © 2026 Niffyhunt. Use them, fork them, ship them. Attribution appreciated, not required.
Part of the WraithWall project · by Niffy_hunt · @wraithwalll on X · wraithwall on GitHub
