

zentinel
 zentinelproxy/zentinel
무료 웹을 보호하기 위해 구축된 보안 우선 리버스 프록시.
authentication-authorizationdefensive-toolscontainer-security+6
1166일 전
 gmh5225/llm-guard-service
프롬프트 인젝션, 탈옥 공격, 유해 콘텐츠로부터 AI 서비스와 상호작용할 때 보호 기능을 제공하는 서비스입니다.
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 owasp/owasp-top-10-neocloud-and-ai-data-center-security-risks
OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…
 stillbigjosh/kube-reaper
모든 아이덴티티에서 Kubernetes 클러스터를 스캔하고, 위험한 권한을 표시하며, 이를 다단계 권한 상승 경로로 연결하여 클러스터 장악에 이르게 합니다.
 haidang-infosec/phantom-grid
eBPF 기반 능동 방어 시스템으로, Linux 서버를 기만형 허니팟으로 전환합니다. 투명 트래픽 리다이렉션, OS 핑거프린트 스푸핑, 커널 수준 DLP, Zero Trust SSH 접근(SPA)을 제공합니다.
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
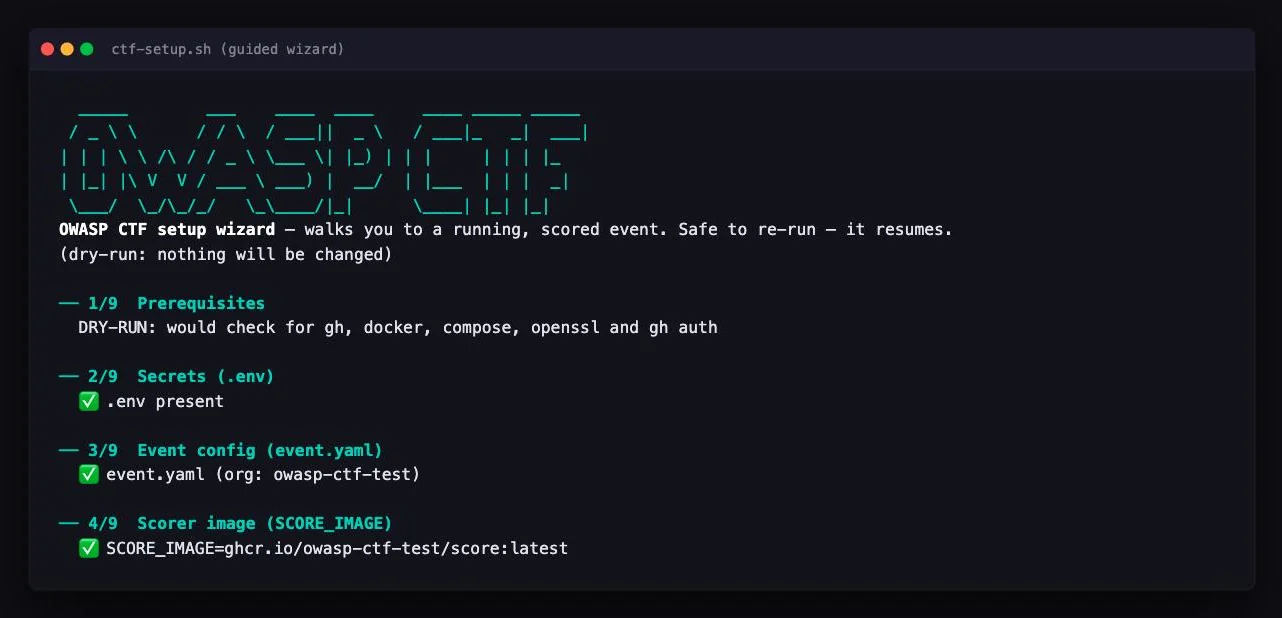 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
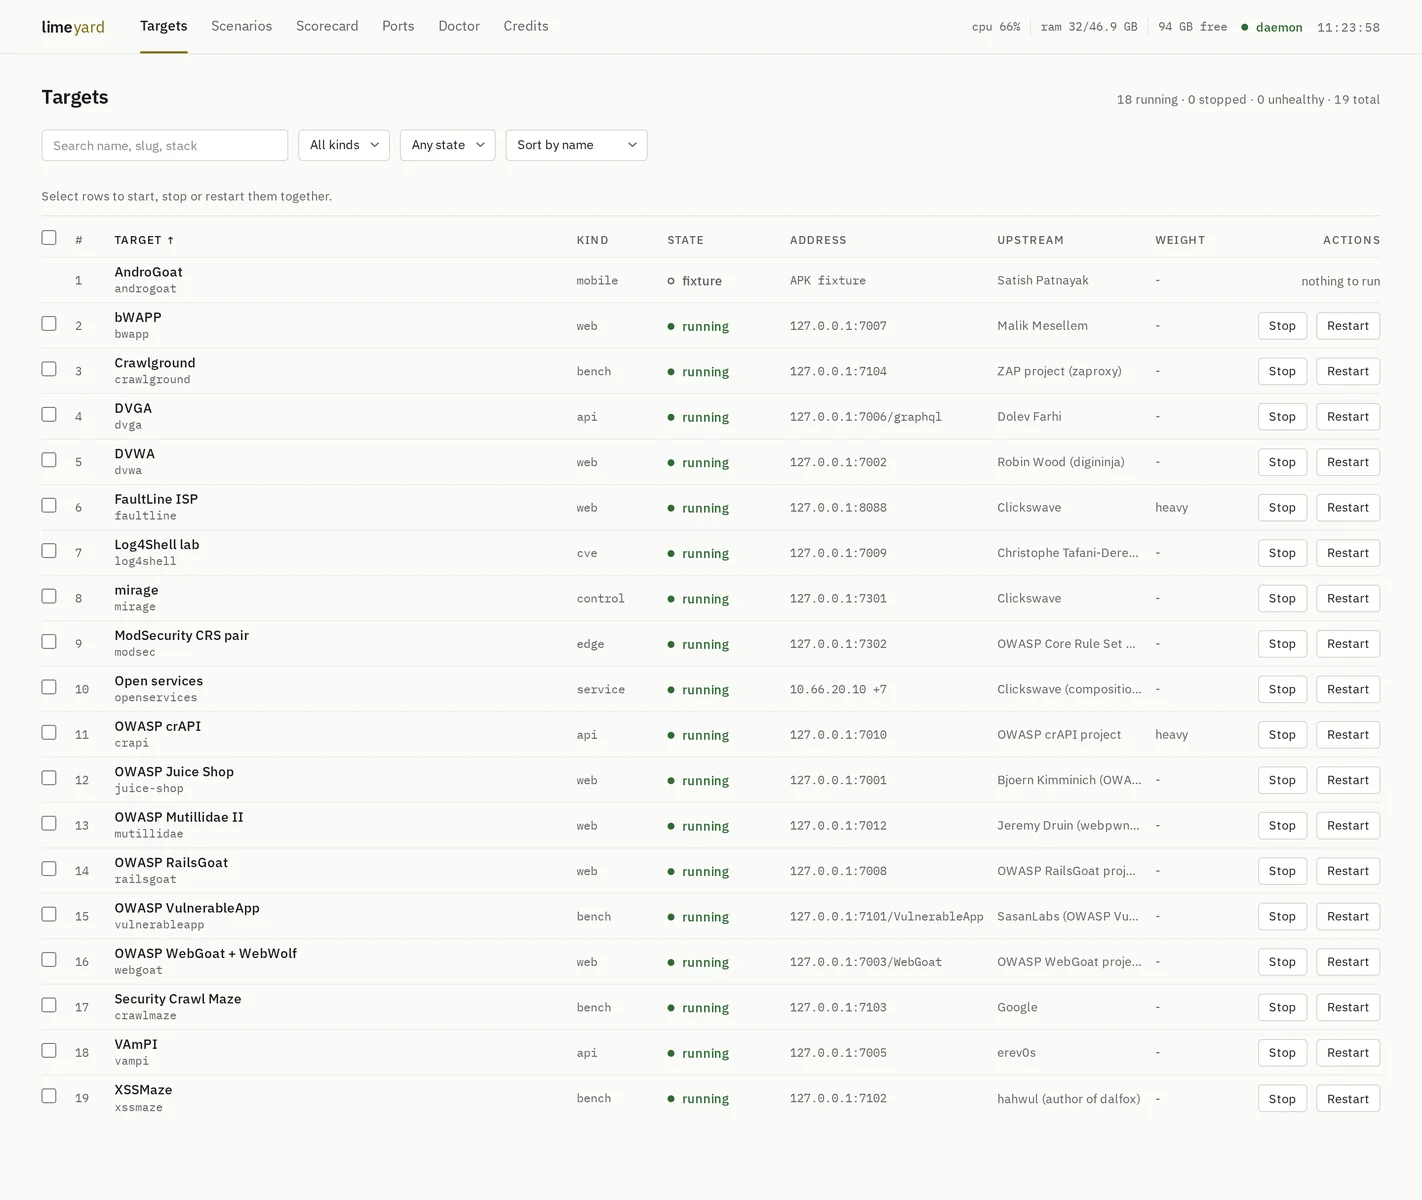 clickswave/limeyard
라우팅 가능한 DNS 환경과 대상별 기계 판독 가능 정답 키를 갖춘 의도적으로 취약한 Docker 실습 환경으로, 스캐너의 정밀도, 재현율, 범위를 로컬에서 채점합니다.
 bombinisecurity/bombini
Aya 기반 eBPF 보안 모니터링 및 샌드박싱 에이전트
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 pbxqdown/portclue
Linux TCP 포트가 도달 가능한지 여부를 설명합니다
 bomfather/agent
커널 공간에서 실행 파일 수준 접근 정책을 시행하는 eBPF 기반 Linux 에이전트로, LSM 훅을 통해 프로세스를 샌드박싱하고 파일, 네트워크, GPU 접근을 제한합니다.
 microsoft/mxc
Policy-driven, layered isolation and containment
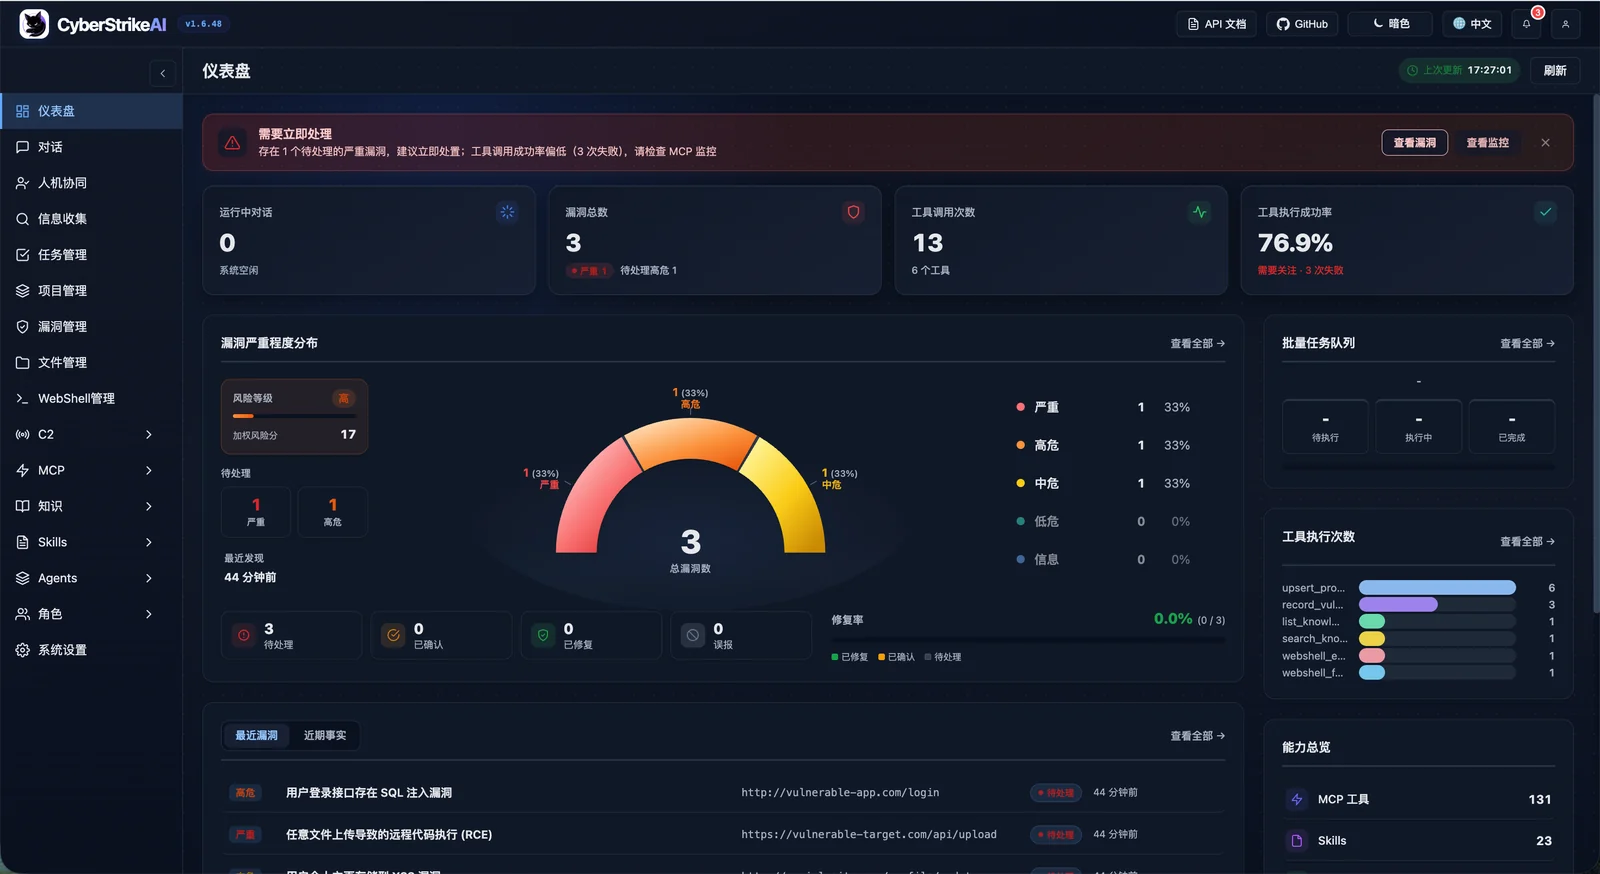 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…