
Jackalope
 googleprojectzero/jackalope
Windows, macOS, Linux 및 Android용 바이너리 커버리지 기반 퍼저
dynamic-analysis-sandboxingvulnerability-analysisreverse-engineering+6
1.4k
 piratesshield/apiharvester
원샷 API 공격 도구 - 주어진 루트에서 API URL을 찾아 자동화된 공격을 시뮬레이션합니다
 monad-developers/ultrafuzz
End-to-end agentic smart contract fuzzing and threat hunting
 0sec-labs/0
The multiplayer AI offensive security OS - open, self-improving, extensible. Find, verify, and fix vulnerabilities.
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 rix4uni/wordlist
퍼징, DNS 열거, 파라미터 탐색, 기본 자격 증명을 위한 맞춤형 워드리스트 큐레이션 모음과 nuclei 기술 워드리스트용 Go 생성기.
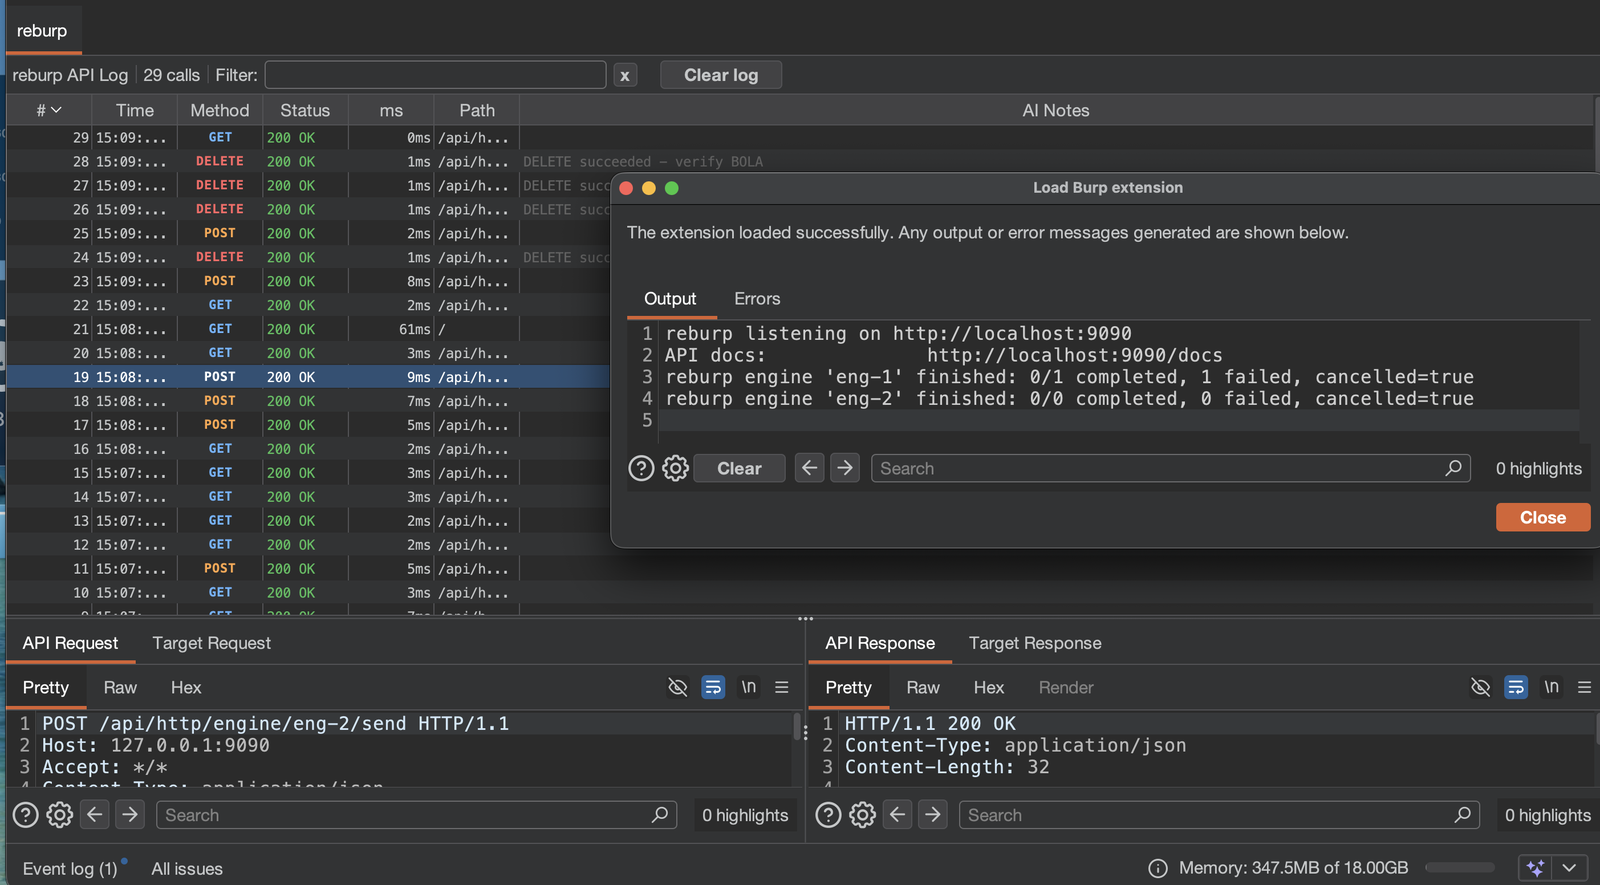 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
 githubsecuritylab/seclab-taskflows-fuzzing
An LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent
 tihanyin/rex-skill
REx@Skill - 바이너리 취약점 발견을 위한 에이전트 기반 리버스 엔지니어링 실행 스킬
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 safety-research/red-teaming-auto-mode
Research code for red-teaming AI auto-mode monitors, including simulation evals, fuzzing, and monitor implementations for Claude Code and Codex…
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 vighnesh91/omnisec-hex
모바일 APK/IPA 트리아지, 클라이언트 측 DAST 퍼징, OSINT 디렉터리, 오프라인 AI 위협 스코어링, 네트워크 포트/CSP 감사를 위한 6개 모듈로 구성된 브라우저 로컬 보안 모노레포.
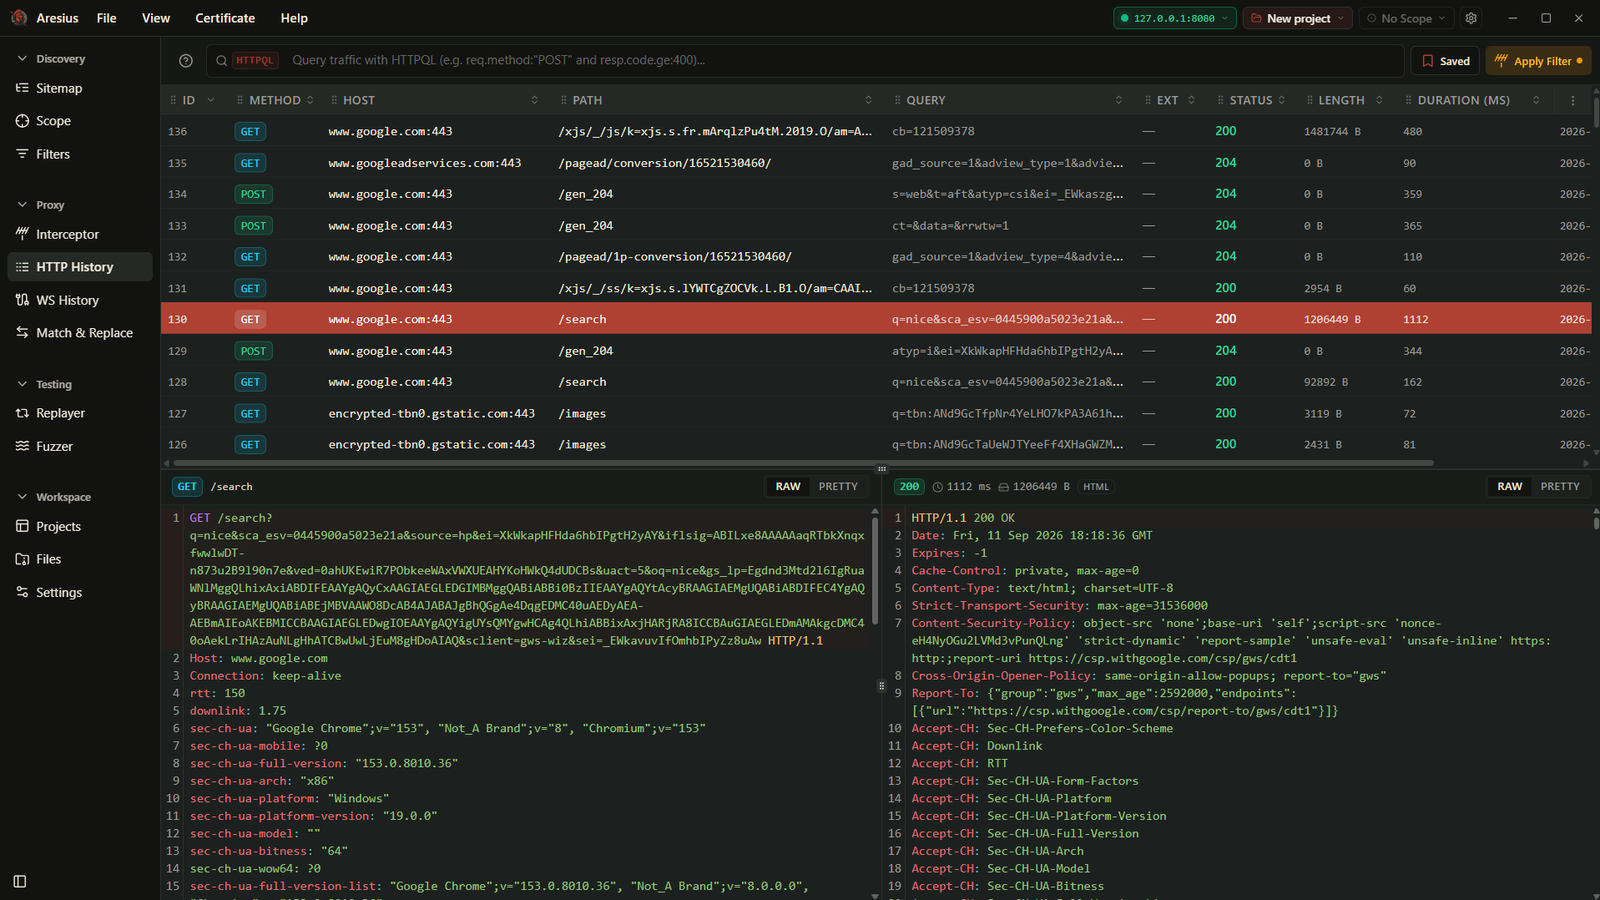 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
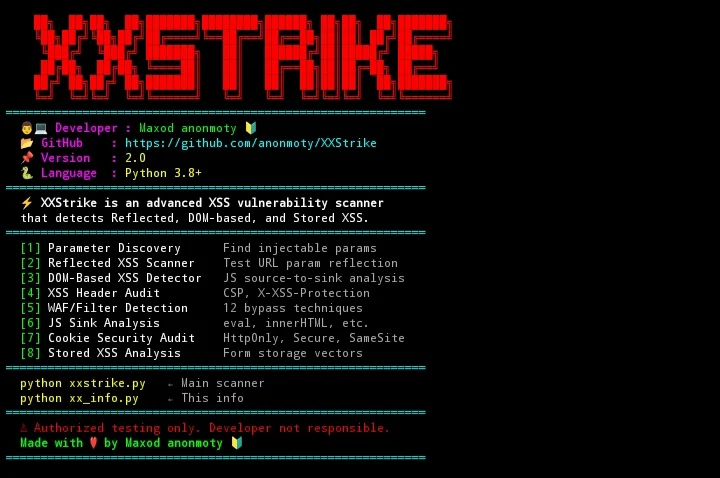 anonmoty/xxstrike
XSStrike 기반 XSS 스캐너로 사용자 정의 기능을 갖추고 있습니다. 웹 애플리케이션의 XSS 취약점을 탐지합니다.
 off-by-1-labs/flawed
임베디드 결함이 있는 Fix-Like 아티팩트
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 nathan-luevano/silica
Exhaustive differential validation of all 4.3B AArch64 instruction encodings.