

hardstop
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
defensive-toolscontainer-securitydynamic-analysis-sandboxing+7
5
 ooafa/bucketbuster
Yandex, VK, Selectel, Sber, Alibaba, Tencent, Huawei, Baidu 전반의 퍼블릭 클라우드 오브젝트 스토리지 엔드포인트를 스캔하여 목록 조회 가능한 버킷과 노출된 오브젝트를 찾습니다.
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
 hac01/azure-pentesting-suite
Azure 보안 평가를 위한 Go 툴킷: 구독 및 리소스를 열거하고, 잘못된 구성을 감사하며, 공용 Blob 스토리지를 익명으로 공격합니다.
 w4r10ck423/envvisualizer
손상된 Linux 박스에서 /proc/self/environ을 파싱하고 시각화합니다 — 환경 변수를 기술 스택(AWS, Django, Rails, NodeJS, MySQL, K8s, Docker 등…)별로 분류하고, 심각도 등급이 매겨진 인사이트를 즉시 실행 가능한…
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 synacktiv/aadoutsider-py
AADInternals의 AsOutsider 기능을 Python3로 재작성한 것
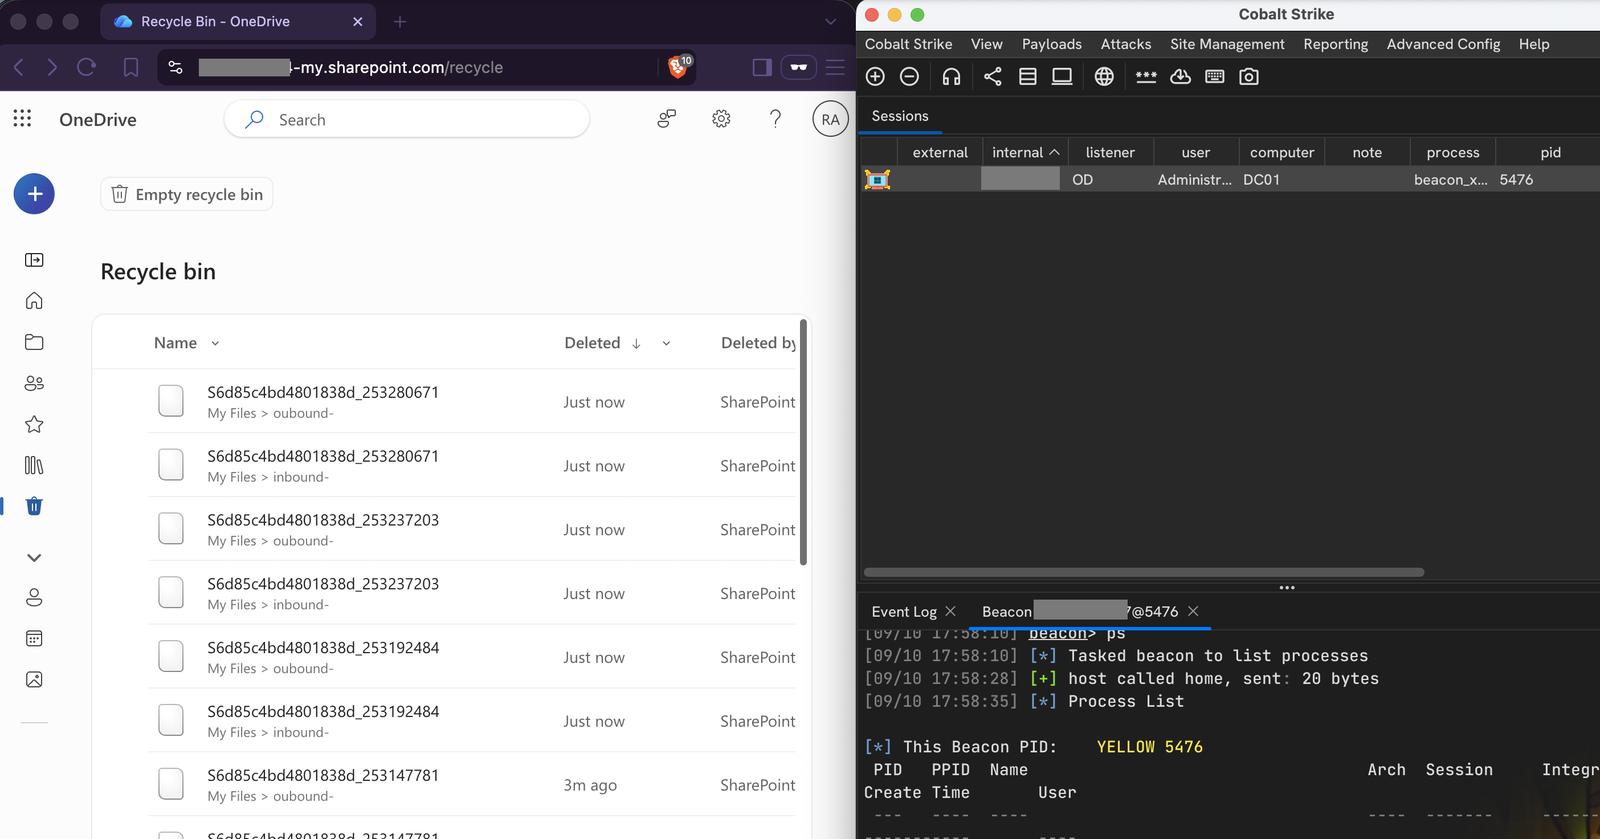 nmht3t/onedrive-udc2
Cobalt Strike를 위한 은밀한 C2 전송 수단으로서의 OneDrive
 trustedsec/rage
벤더 중립적 NDJSON 공격 그래프 형식으로, 노드/엣지 분류 체계, AWS/GCP/Azure 매핑, 파생 규칙, 그리고 공격적 보안 도구를 위한 노출 DB를 포함합니다.
 ustayready/thunderstorm
환경을 매핑하고, 실효 권한과 신뢰를 평가하며, 완전한 공격 그래프를 단일 .rage.ndjson 파일로 작성하는 수집 및 도출 엔진. 다른 모든 것의 입력.
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 bomfather/agent
커널 공간에서 실행 파일 수준 접근 정책을 시행하는 eBPF 기반 Linux 에이전트로, LSM 훅을 통해 프로세스를 샌드박싱하고 파일, 네트워크, GPU 접근을 제한합니다.
 falconforceteam/falcondash
Azure 통합 문서 대시보드로, 탐지 성능 지표를 시각화하고 탐색하여 보안 팀이 탐지 규칙을 측정하고 사전에 유지 관리할 수 있도록 지원합니다.
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 mafifrizi/ares
MITRE ATT&CK 모듈 오케스트레이션, DAG 공격 경로 해결, OPSEC 제어, 암호화된 자격 증명 보관소, 다중 형식 보고를 갖춘 자율 레드팀 참여 플랫폼입니다.
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 atomburstofficial/geiger
Read-only CLI that inventories AI agents, MCP servers, plugins, and extensions on a machine, reporting their capabilities and exposure with…
 owasp/openshield
오픈소스 Azure CSPM - 잘못된 구성과 양자-안전하지 않은 암호화를 스캔하고, 발견 사항을 CIS/NIST/ISO27001/SOC2에 매핑하며, 단일 명령으로 수정합니다.