

Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories

도구

전체Android SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
최신관련성인기최근 업데이트
13890 결과
ESFang preview

ESFang

GitHubwithsecurelabs/esfang

ESF 모듈식 수집 도구로, 개발 및 연구용입니다.

forensicsdigital-forensicsincident-response+1
384년 전
FLAIR preview

FLAIR

GitHubwithsecurelabs/flair

Windows 호스트에서 핵심 포렌식 아티팩트를 반자동으로 수집하기 위한 경량 배치 스크립트로, OS 기본 도구만 사용하여 사고 대응 및 트라이지(triage)를 지원합니다.
forensicsdigital-forensicsthreat-intelligence+2
165년 전
detectree preview

detectree

GitHubwithsecurelabs/detectree

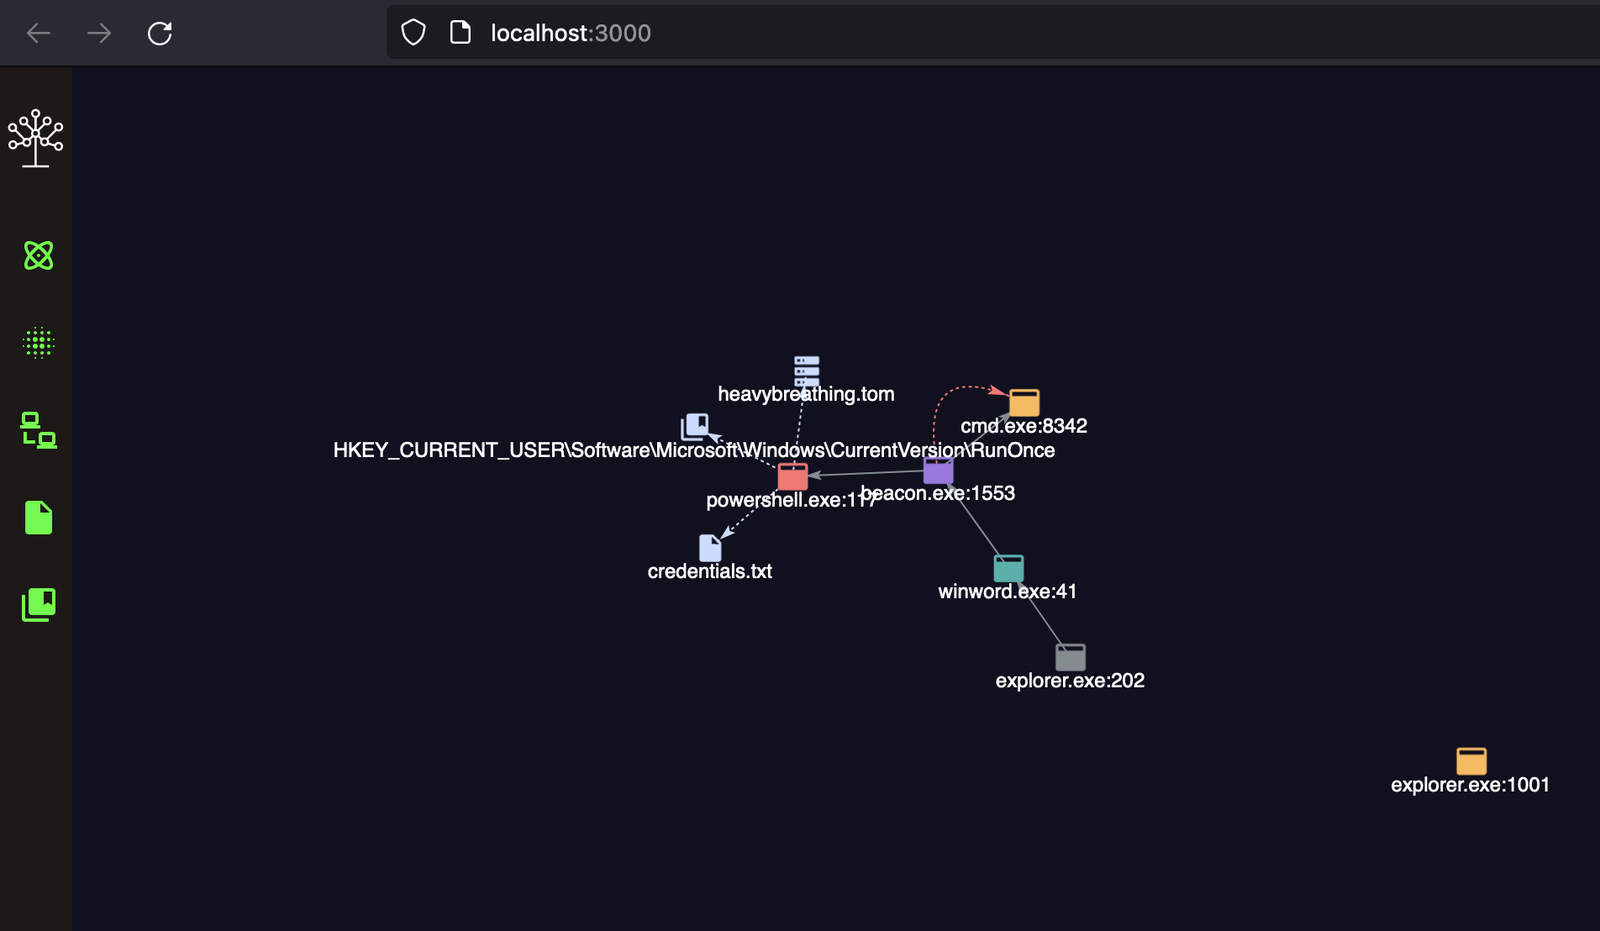
블루 팀이 탐지 데이터를 분석하고, 관계를 이해하며, 알림 피로를 줄이고, 사고 대응을 개선하기 위한 대화형 데이터 시각화 도구입니다.
defensive-toolsthreat-intelligenceincident-response+1
1263년 전
ppid-spoofing preview

ppid-spoofing

GitHubwithsecurelabs/ppid-spoofing

부모 PID 스푸핑을 수행하고 탐지하기 위한 스크립트
defensive-toolsprivilege-escalationpost-exploitation+3
1486년 전
lazarus-sigma-rules preview

lazarus-sigma-rules

GitHubwithsecurelabs/lazarus-sigma-rules

Sigma 규칙으로 Lazarus 그룹의 TTP를 탐지하며, 악성 문서 실행, PowerShell 남용, 예약 작업, 자격 증명 접근을 포함하고 Sysmon 및 Windows 이벤트 로그용으로 설계되었습니다.
defensive-toolsthreat-intelligenceintrusion-detection+2
206년 전
macOSTriageCollectionScript preview

macOSTriageCollectionScript

GitHubwithsecurelabs/macostriagecollectionscript

macOS에서 사고 대응을 위한 포괄적인 트라이지 데이터를 수집하며, 시스템 로그, 파일 목록, 브라우저 데이터, 셸 히스토리, 지속성 메커니즘을 포함합니다.
forensicsdigital-forensicsthreat-intelligence+2
315년 전
volatility-plugins preview

volatility-plugins

GitHubwithsecurelabs/volatility-plugins

Volatility 메모리 포렌식 플러그인으로, Gargoyle 메모리 스캐닝 회피 기법 탐지를 포함합니다.
memory-forensicsforensicsmalware-analysis+2
118년 전
usb-ninja-detection-poc preview

usb-ninja-detection-poc

GitHubwithsecurelabs/usb-ninja-detection-poc

USB Ninja 키스트로크 주입 공격을 감지하여 키 입력 및 애플리케이션 이벤트를 기록하고, 방어적 모니터링을 위한 개념 증명을 제공합니다.
defensive-toolsiot-securityhardware-security+1
76년 전
AMSIDetection preview

AMSIDetection

GitHubwithsecurelabs/amsidetection

AMSI(맬웨어 방지 검사 인터페이스) 우회 및 Windows 엔드포인트에서의 악성 인메모리 스크립트 활동을 탐지하기 위한 개념 증명 도구입니다.
defensive-toolsdynamic-analysis-sandboxingsecurity-virtualization+1
326년 전
shadowhammer preview

shadowhammer

GitHubwithsecurelabs/shadowhammer

배치 모드로 Shadowhammer 악성코드 지표를 확인하는 도구로, 로컬 또는 제공된 MAC 주소를 알려진 악성 해시와 대조하여 스캔하며, 오프라인 지원 및 오탐 필터링 기능을 제공합니다.
defensive-toolsscripting-automationnetwork-security+2
87년 전
pywintrace preview

pywintrace

GitHubfireeye/pywintrace

Python ctypes 래퍼로, Windows용 이벤트 추적(ETW)을 통해 세션 제어, 이벤트 캡처, 보안 모니터링 및 포렌식 분석을 위한 사용자 정의 콜백을 지원합니다.
defensive-toolsdigital-forensicsthreat-intelligence+2
3053년 전
dotnet-gargoyle preview

dotnet-gargoyle

GitHubwithsecurelabs/dotnet-gargoyle

영적(정신적)인 .NET 기반의 Gargoyle 메모리 스캐닝 회피 기법에 해당하는 도구

memory-forensicsmalware-analysisred-teaming
527년 전
doublepulsar-usermode-injector preview

doublepulsar-usermode-injector

GitHubwithsecurelabs/doublepulsar-usermode-injector

DOUBLEPULSAR 페이로드의 usermode 셸코드를 사용하여 임의의 DLL을 다른 프로세스에 반사적으로 로드하는 유틸리티로, 탐지 기법 테스트 또는 기타 보안 연구에 사용됩니다.

exploitationpost-exploitationmalware-analysis+2
1249년 전
radare2-scripts preview

radare2-scripts

GitHubwithsecurelabs/radare2-scripts

# 악성코드 분석용 radare2 스크립트 모음: 메모리 덤프에서 바이너리 추출, PE 헤더 패치, 셸코드 내 해시 함수 임포트 디코딩
memory-forensicsreverse-engineeringshellcode+3
328년 전
memory-carving-scripts preview

memory-carving-scripts

GitHubwithsecurelabs/memory-carving-scripts

감염된 메모리 덤프에서 유용한 정보를 추출하기 위한 스크립트

memory-forensicsforensicsmalware-analysis+2
108년 전
iBSSloader preview

iBSSloader

GitHubteutekeune/ibssloader

checkm8, 패치된 iBSS/iBEC 및 맞춤형 베어메탈 페이로드를 통해 iPad mini 1에서 Linux를 부팅하기 위한 연구용 도구로, 장치 트리 포팅, 커널 빌드 및 부트 스크립트를 포함합니다.
embedded-systems-securityexploitationreverse-engineering+3
72개월 전
admin-panel-finder preview

admin-panel-finder

GitHubbdblackhat/admin-panel-finder

Python 스크립트로 웹사이트의 관리자 패널 URL을 탐지하여 보안 정찰 및 침투 테스트를 지원합니다.
reconnaissanceweb-application-exploitationinformation-gathering+2
19513년 전
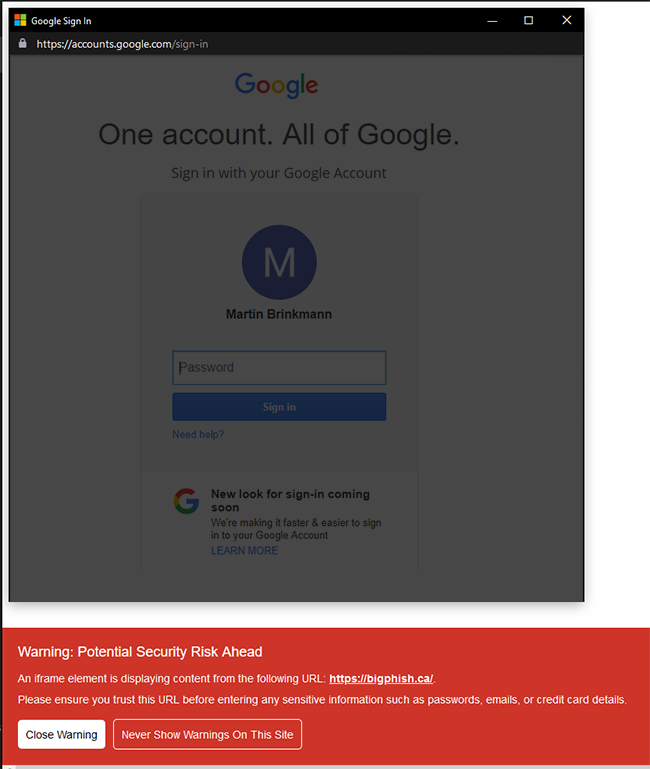
enhanced-iframe-protection preview

enhanced-iframe-protection

GitHubmalwarecube/enhanced-iframe-protection

가벼운 확장 프로그램으로, 임베디드 iframe 요소를 자동으로 감지하고 상세 경고를 제공하여 BITB(Browser-In-The-Browser) 공격으로부터 보호합니다.

defensive-toolsphishingweb-security+1
5112일 전
이전1…585960…100다음