Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
Payload Development — 도구 — 3페이지 | Kitploit

도구

전체Android SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
최신관련성인기최근 업데이트
967 결과
mythic_telegram_profile preview

mythic_telegram_profile

GitHubdavidcarliez/mythic_telegram_profile

Athena 및 Apollo 에이전트 트래픽을 Telegram 봇 간 메시지를 통해 터널링하여 암호화된 페이로드를 Mythic의 Push C2 gRPC 서비스를 통해 Mythic에 브리징하는 Mythic C2 프로필입니다.

penetration-testing-frameworksencryption-decryption-toolsexploit-frameworks+5

4
24일 전
Silverseal preview

Silverseal

GitHubidov31/silverseal

UEFI 부트킷을 갖춘 Linux 포스트 익스플로잇 프레임워크로, 최신 Linux 시스템에서 Rust 기반 커널 모듈 루트킷을 지속적이고 은밀하게 로드합니다.

persistence-mechanismsexploitationpost-exploitation+4
17010일 전
msteams preview

msteams

GitHubwhispergate/msteams

Microsoft Graph API를 사용하여 Microsoft Teams 채널을 통해 에이전트 트래픽을 터널링하는 Mythic C2 프로필로, AES256 암호화, 지터, 킬 데이트, 프록시 지원을 제공합니다.

defensive-toolspenetration-testing-frameworksencryption-decryption-tools+5
391개월 전
Claude-Red preview

Claude-Red

GitHubsnailsploit/claude-red

웹, AD, 무선, 클라우드 및 익스플로잇 개발 전반에 걸쳐 Claude에게 전문 레드팀 방법론을 주입하는 78개의 공격적 보안 SKILL.md 모듈로 구성된 큐레이션 라이브러리입니다.

privilege-escalationexploitationweb-application-exploitation+8
7.5k6일 전
KernelPatch preview

KernelPatch

GitHubbmax121/kernelpatch

Linux 커널 이미지만으로 Linux 커널 패치 및 후킹.

android-securityembedded-systems-securityexploitation+7
1.6k5일 전
FolkPatch preview

FolkPatch

GitHublyravoid/folkpatch

Boot 파티션을 패치하여 다시 플래싱하는 것만으로 커널에 대한 루트 권한을 얻을 수 있습니다. 이 솔루션은 APatch의 비병렬 확장 브랜치를 기반으로 하며, UI/UX 디자인에 중점을 두고 있습니다.

android-securityprivilege-escalationpersistence-mechanisms+3
1.2k6일 전
APatch preview

APatch

GitHubbmax121/apatch

Android 커널 및 Android 시스템의 패치

android-securityprivilege-escalationpersistence-mechanisms+4
8.1k2일 전
KernelPatch preview

KernelPatch

GitHublyravoid/kernelpatch

Linux 커널을 스트립된 커널 이미지만으로 패치하고 후킹하며, 심볼을 추출하고 코드를 주입하여 arm64에서 인라인 및 시스템 콜 후킹을 수행합니다.

android-securityembedded-systems-securityexploitation+6
156일 전
askWAM preview

askWAM

GitHubdirkjanm/askwam

Web Account Manager(WAM)에 Entra ID 토큰을 요청합니다

identity-managementpost-exploitationpenetration-testing+5
1621개월 전
Dropper preview

Dropper

GitHubgmh5225/dropper

JPG/PNG 형식 이미지에 페이로드를 삽입하여 열 때 특정 작업을 수행할 수 있게 해주는 도구입니다.

defensive-toolsexploitationsteganography+4
21년 전
TornadoRevC2 preview

TornadoRevC2

GitHubkamalx06/tornadorevc2

TCP/TLS/mTLS를 통한 리버스 셸 세션을 관리하며, 열거, 인메모리 실행, SOCKS5 피버팅, 지속성을 위한 플러그인을 제공하는 모듈식 포스트 익스플로잇 프레임워크입니다.

penetration-testing-frameworksprivilege-escalationpersistence-mechanisms+8
3711일 전
voidsyscall preview

voidsyscall

GitHubvoidsecsoftwares/voidsyscall

크로스 플랫폼 시스템 콜 기반 임플란트 & C2 — 직접 시스템 콜 (Win), 원시 시스템 콜 (Linux), HTTPS/DNS/ICMP 채널. winapi 계층 없음.

privilege-escalationencryption-decryption-toolspersistence-mechanisms+9
641개월 전
Driver-kaldereta preview

Driver-kaldereta

GitHubgmh5225/driver-kaldereta

서명되지 않은 커널 모드 드라이버로 메모리 수정을 수행합니다

general-purpose-utilitiesdynamic-analysis-sandboxingmemory-forensics+8
114년 전
BEAR-C2 preview

BEAR-C2

GitHubs3n4t0r-0x0/bear-c2

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

penetration-testing-frameworksexploit-frameworkspersistence-mechanisms+8
7034일 전
DefinitelyNotPhishing preview

DefinitelyNotPhishing

GitHubgmh5225/definitelynotphishing

악성 evilginx 피싱릿(phislets), gophish 템플릿, burp suite 확장 프로그램 등을 포함합니다.

phishing-toolsweb-securitysocial-engineering+3
21년 전
0xM0nCrush preview

0xM0nCrush

GitHubdeathshotxd/0xm0ncrush

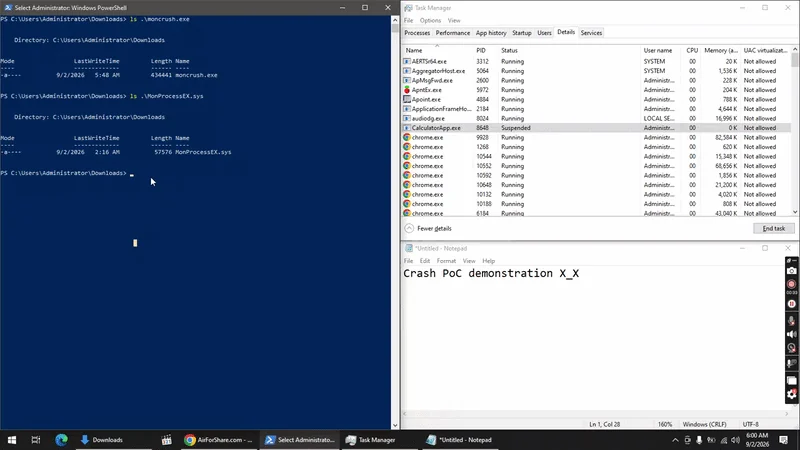
커널 모드 프로세스 종료기로, 서명된 BYOVD 드라이버를 사용합니다. 모든 Windows 10/11에서 작동합니다. 오프셋 없음, PDB 없음. Rust.

defensive-toolsprivilege-escalationexploitation+4
10818일 전
MemoryModulePP preview

MemoryModulePP

GitHubstrivexjun/memorymodulepp

C++ 라이브러리로, 디스크에 접촉하지 않고 메모리에서 직접 DLL을 로드하며 예외 처리 지원을 포함하여 은밀한 코드 실행과 파일 기반 탐지 회피를 가능하게 합니다.

exploitationreverse-engineeringmalware-analysis+2
2255년 전
edrEvasionWorkshop preview

edrEvasionWorkshop

GitHubtyeurada/edrevasionworkshop

# “단계별 멀웨어 개발: 로더부터 커널까지 EDR 우회” 워크숍 자료 DEF CON 34 및 BSidesLV 2026에서 발표된 자료입니다. 멀웨어 개발, EDR 아키텍처, EDR 우회, C2 커스터마이징, 커널 수준 기법을 다룹니다.

defensive-toolsexploitationpost-exploitation+5
3972개월 전
이전1234…54다음