
Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
Memory Forensics — 도구 — 4페이지 | Kitploit

도구

전체Android SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
최신관련성인기최근 업데이트
327 결과
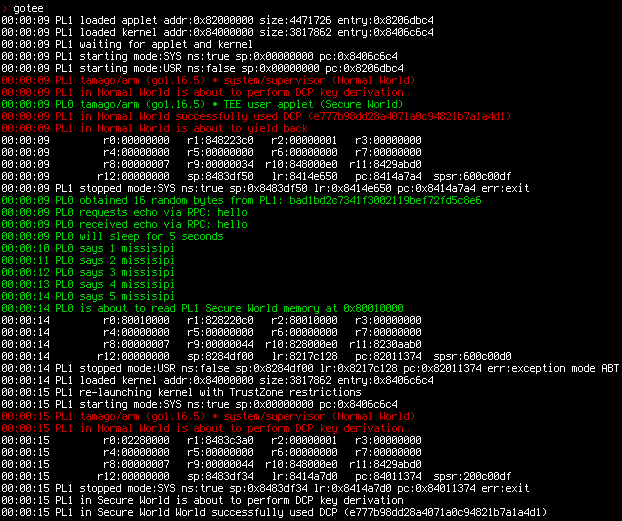
GoTEE-example preview

GoTEE-example

GitHubusbarmory/gotee-example

GoTEE - 예제 애플리케이션

embedded-systems-securitymemory-forensicsdebuggers+2
179일 전
Blue-Team-Notes preview

Blue-Team-Notes

GitHubpurp1ew0lf/blue-team-notes

블루 팀을 빼놓고 갈 거라고 생각하지 않았겠죠?
memory-forensicsnetwork-forensicsmalware-analysis+5
1.8k25일 전
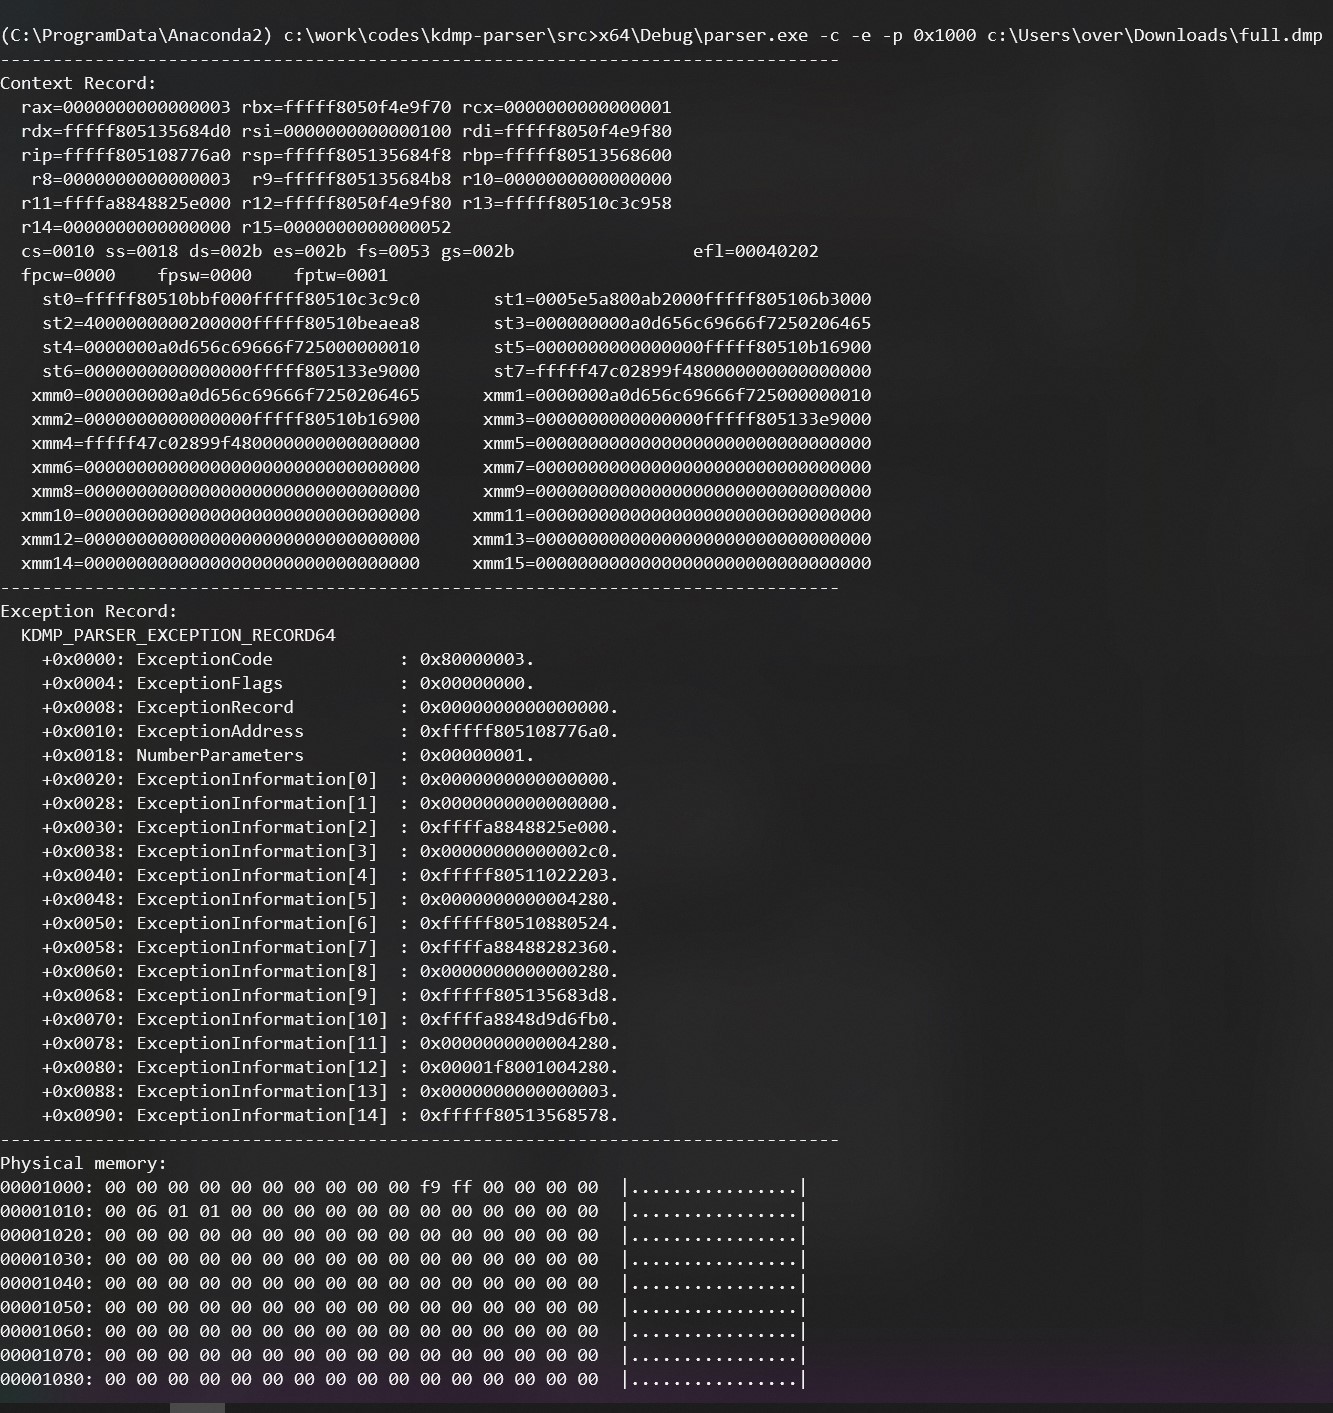
kdmp-parser preview

kdmp-parser

GitHub0vercl0k/kdmp-parser

Windows 커널 덤프 C++ 파서 라이브러리로, Python 3 바인딩을 포함합니다.
memory-forensicsforensicsdigital-forensics+1
2111년 전
windbg_js_scripts preview

windbg_js_scripts

GitHubhugsy/windbg_js_scripts

WinDbg JS API를 가지고 놀기 위한 장난감 스크립트
memory-forensicsdynamic-code-analysisreverse-engineering+3
2442년 전
pesieve-go preview

pesieve-go

GitHubhasherezade/pesieve-go

Golang 바인딩 for PE-sieve

memory-forensicsdynamic-code-analysismalware-analysis+1
432년 전
yara-ttd preview

yara-ttd

GitHubairbus-cert/yara-ttd

Time Travel Debugging 트레이스에서 YARA 규칙 사용
dynamic-analysis-sandboxingmemory-forensicsreverse-engineering+3
973년 전
clairvoyance preview

clairvoyance

GitHub0vercl0k/clairvoyance

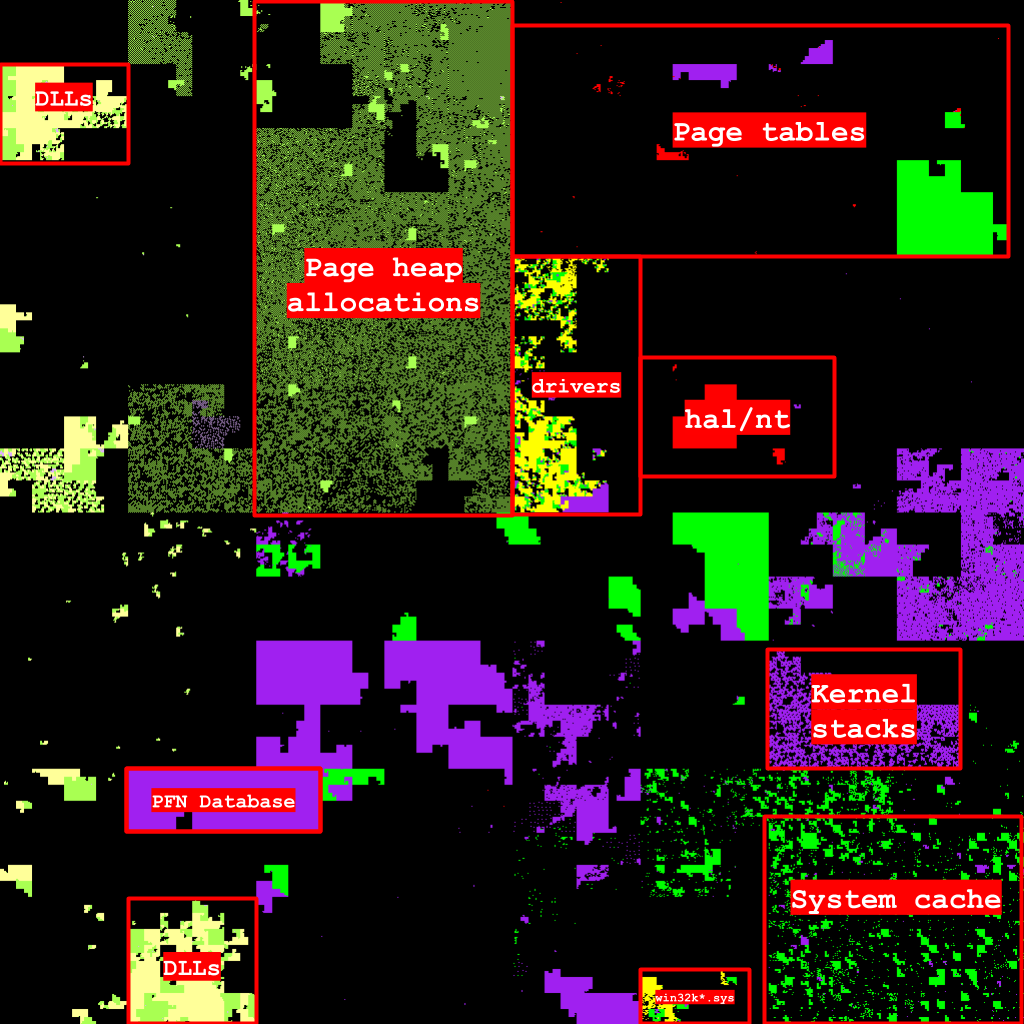
Windows 프로세스의 가상 주소 공간을 힐베르트 곡선으로 시각화합니다.

memory-forensicsforensicsdigital-forensics
3085년 전
CovenantDecryptor preview

CovenantDecryptor

GitHubnaacbin/covenantdecryptor

Covenant C2 통신을 해독하여 미니덤프에서 RSA 개인 키를 추출하고, AES 세션 키를 복구하며, 네트워크 캡처를 평문으로 변환합니다.

encryption-decryption-toolsmemory-forensicsnetwork-forensics+4
372년 전
ChromeKatz preview

ChromeKatz

GitHubmeckazin/chromekatz

Chrome/Edge 프로세스 메모리에서 쿠키와 자격 증명을 직접 덤프합니다

memory-forensicspassword-attacksdata-exfiltration+3
1.5k6개월 전
QCSuper preview

QCSuper

GitHubp1sec/qcsuper

QCSuper는 Qualcomm 기반 휴대폰 및 모뎀과 통신하는 도구로, 무엇보다도 원시 2G/3G/4G 무선 프레임을 캡처할 수 있게 해줍니다.
embedded-systems-securitypacket-sniffing-analysismemory-forensics+4
1.6k6일 전
LsassReflectDumping preview

LsassReflectDumping

GitHuboffensive-panda/lsassreflectdumping

이 도구는 RtlCreateProcessReflection API를 사용하는 Process Forking 기법을 활용하여 lsass.exe 프로세스를 복제합니다. 복제본이 생성되면 MINIDUMP_CALLBACK_INFORMATION 콜백을 활용하여 복제된 프로세스의…
memory-forensicspassword-attackspost-exploitation+1
2201년 전
py preview

py

GitHubantiwar3/py

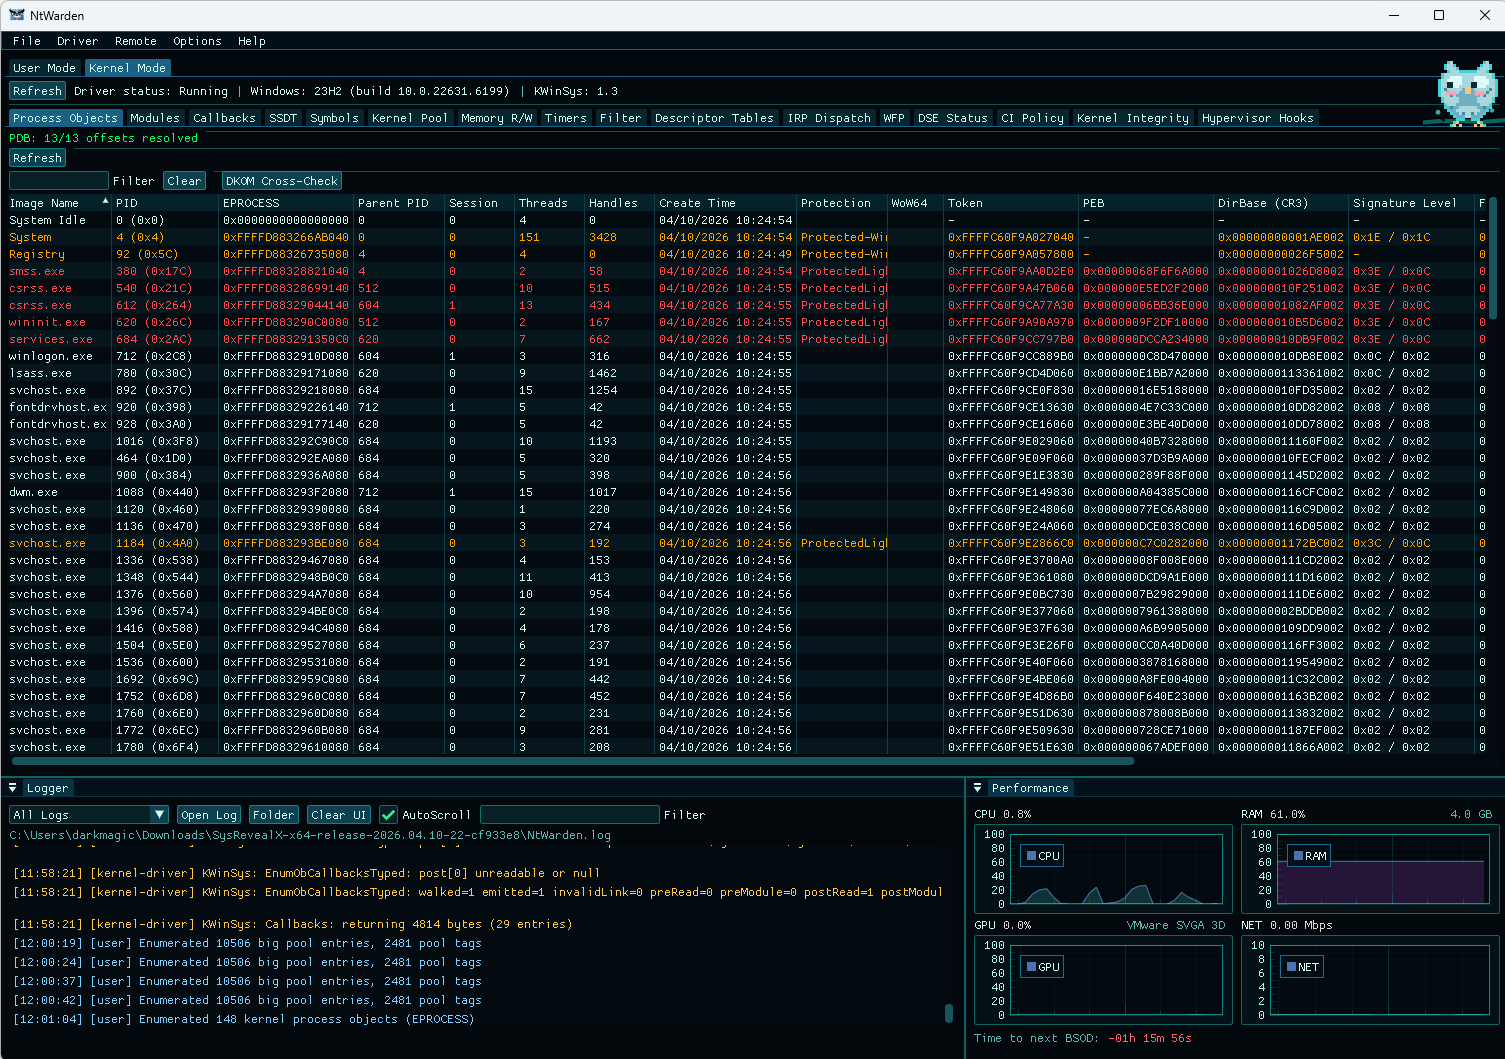
飘云ark(pyark)

defensive-toolsmemory-forensicsmalware-analysis+3
5291개월 전
NtWarden preview

NtWarden

GitHubmrt4ntr4/ntwarden

Windows 분석 및 연구 툴킷

defensive-toolsmemory-forensicsmalware-analysis+4
6765개월 전
MemProcFS-Analyzer preview

MemProcFS-Analyzer

GitHublethal-forensics/memprocfs-analyzer

MemProcFS를 사용하여 Windows 메모리 포렌식 및 DFIR 워크플로우를 자동화합니다: YARA/ClamAV 스캐닝, 프로세스 이상 징후 탐지, 아티팩트/로그 추출.
memory-forensicsscripting-automationmalware-analysis+5
7281개월 전
mimikatz preview

mimikatz

GitHubparrotsec/mimikatz

메모리에서 Windows 자격 증명(비밀번호, 해시, Kerberos 티켓)을 추출하고 pass-the-hash, pass-the-ticket, golden ticket 공격을 수행하기 위한 도구입니다.
privilege-escalationmemory-forensicspassword-attacks+5
2.6k2년 전
asatools preview

asatools

GitHubnccgroup/asatools

NCC Group Cisco ASA 관련 모든 도구 프로젝트를 가져오기 위한 메인 저장소입니다.
embedded-systems-securitymemory-forensicsreverse-engineering+3
2388년 전
DetectWindowsCopyOnWriteForAPI preview

DetectWindowsCopyOnWriteForAPI

GitHubnccgroup/detectwindowscopyonwriteforapi

위협 헌팅을 지원하기 위해 Windows 프로세스에서 다양한 특성을 열거합니다.
defensive-toolsmemory-forensicsforensics+3
2004년 전
KilledProcessCanary preview

KilledProcessCanary

GitHubnccgroup/killedprocesscanary

특정 랜섬웨어 공격자의 영향을 최소화하도록 설계된 카나리

defensive-toolsmemory-forensicsdigital-forensics+2
1015년 전
이전1…345…19다음

