
Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
Memory Forensics — 도구 — 5페이지 | Kitploit

도구

전체Android SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
최신관련성인기최근 업데이트
327 결과
libdlmalloc preview

libdlmalloc

GitHubnccgroup/libdlmalloc

dlmalloc용 힙 분석 도구

embedded-systems-securitymemory-forensicsreverse-engineering+2
324년 전
libptmalloc preview

libptmalloc

GitHubnccgroup/libptmalloc

ptmalloc용 힙 분석 도구

memory-forensicsreverse-engineeringdebuggers+1
464년 전
libmempool preview

libmempool

GitHubnccgroup/libmempool

힙 메모리 풀 분석 도구

embedded-systems-securitymemory-forensicsreverse-engineering+3
134년 전
libtalloc preview

libtalloc

GitHubnccgroup/libtalloc

libtalloc은 GDB와 함께 사용하여 "trivial allocator"(talloc)를 분석할 수 있는 Python 스크립트입니다.
memory-forensicsvulnerability-analysisreverse-engineering+2
1711년 전
memgrep preview

memgrep

GitHubnccgroup/memgrep

메모리 검색 유틸리티

memory-forensicsforensicsinformation-gathering+3
4412년 전
memaddressanalysis preview

memaddressanalysis

GitHubnccgroup/memaddressanalysis

메모리 주소 분석 관련 연구 프로젝트
memory-forensicsvulnerability-analysisbinary-analysis+1
1412년 전
memscan preview

memscan

GitHubnccgroup/memscan

Windows 프로세스의 메모리 공간에서 문자열, 정규식, 마그네틱 스트라이프 카드 트랙의 신용카드 번호를 검색합니다.
reconnaissancememory-forensicsdata-exfiltration+5
1295년 전
mnemosyne preview

mnemosyne

GitHubnccgroup/mnemosyne

Windows 메모리 스크래핑을 위한 범용 도구
dynamic-analysis-sandboxingmemory-forensicsinformation-gathering+2
699년 전
WindowsPatchDetector preview

WindowsPatchDetector

GitHubnccgroup/windowspatchdetector

실험적 Windows .text 섹션 패치 탐지기
defensive-toolsmemory-forensicsforensics+3
2311년 전
WindowsFirewallHookDriverEnumeration preview

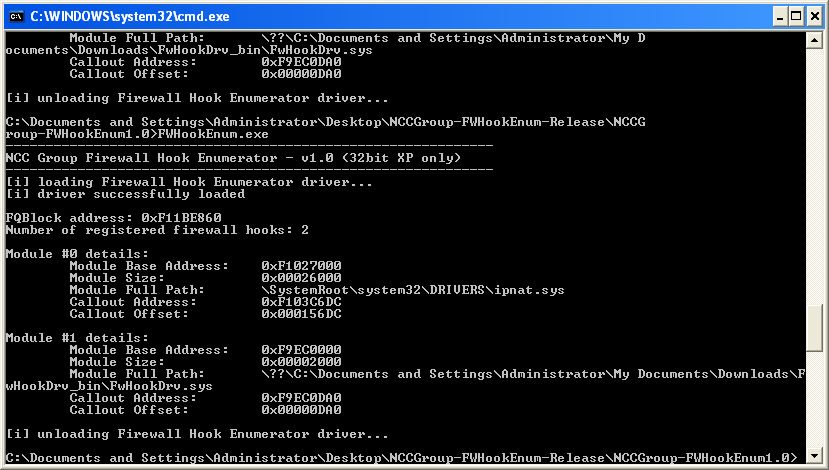
WindowsFirewallHookDriverEnumeration

GitHubnccgroup/windowsfirewallhookdriverenumeration

Windows 2000, XP 및 2003에서 Windows 방화벽 후크 드라이버를 열거하는 도구
memory-forensicsforensicsmalware-analysis+2
2111년 전
WindowsMemPageDelta preview

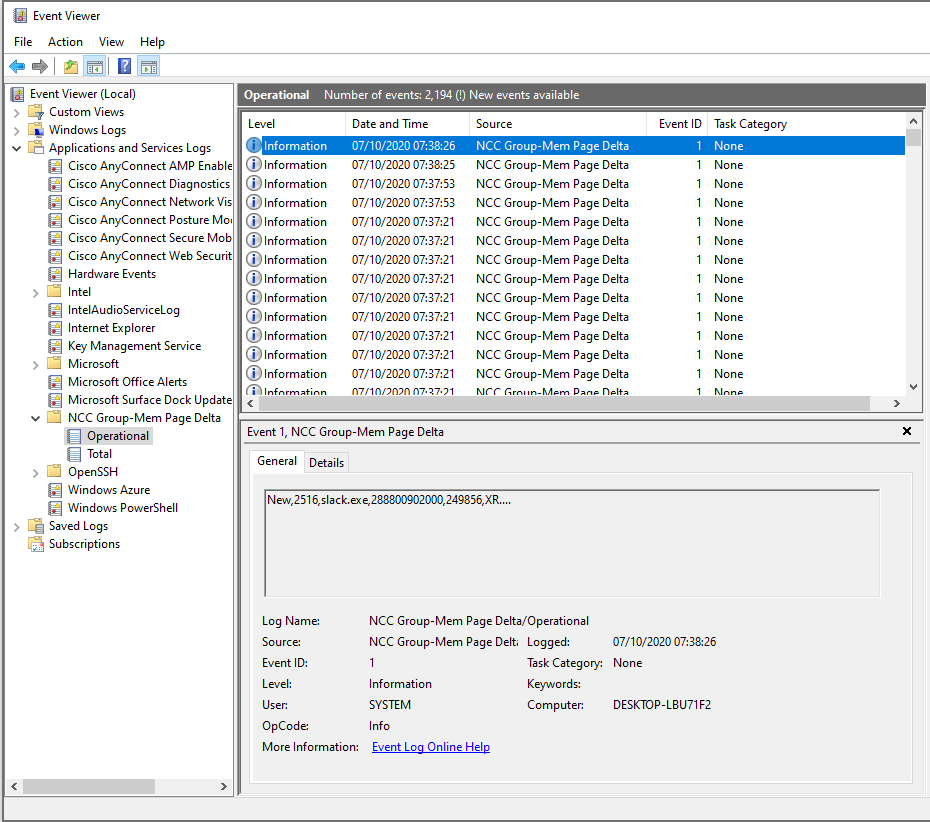
WindowsMemPageDelta

GitHubnccgroup/windowsmempagedelta

Microsoft Windows 실행 파일의 메모리 페이지 변경에 대한 텔레메트리를 제공하여 위협 탐지를 지원하는 Microsoft Windows 서비스
defensive-toolsmemory-forensicsanomaly-detection+1
336년 전
zipdefrag preview

zipdefrag

GitHubnccgroup/zipdefrag

Recon Montreal 2018에서 발표됨

embedded-systems-securitymemory-forensicsreverse-engineering+3
78년 전
Malware-analysis-and-Reverse-engineering preview

Malware-analysis-and-Reverse-engineering

GitHubdump-guy/malware-analysis-and-reverse-engineering

제가 공개적으로 제공한 멀웨어 분석 및 리버스 엔지니어링 자료 중 일부입니다.
memory-forensicsexploitationreverse-engineering+8
9602년 전
RansomLord preview

RansomLord

GitHubmalvuln/ransomlord

RansomLord는 PE 파일 생성을 자동화하는 개념 증명 안티랜섬웨어 악용 도구로, 랜섬웨어의 사전 암호화를 손상시키는 데 사용됩니다.

defensive-toolsmemory-forensicsexploitation+4
5161년 전
bulk_extractor preview

bulk_extractor

GitHubsimsong/bulk_extractor

이것은 개발 트리입니다. 프로덕션 다운로드는 다음에서 가능합니다:

disk-forensicsosintmemory-forensics+9
1.4k7일 전
yara-x preview

yara-x

GitHubvirustotal/yara-x

Rust로 재작성된 YARA.

defensive-toolsdisk-forensicsioc-management+14
1.2k3일 전
forensicscanner preview

forensicscanner

GitHubappliedsec/forensicscanner

포렌식 스캐너

disk-forensicsmemory-forensicsnetwork-forensics+3
4113년 전
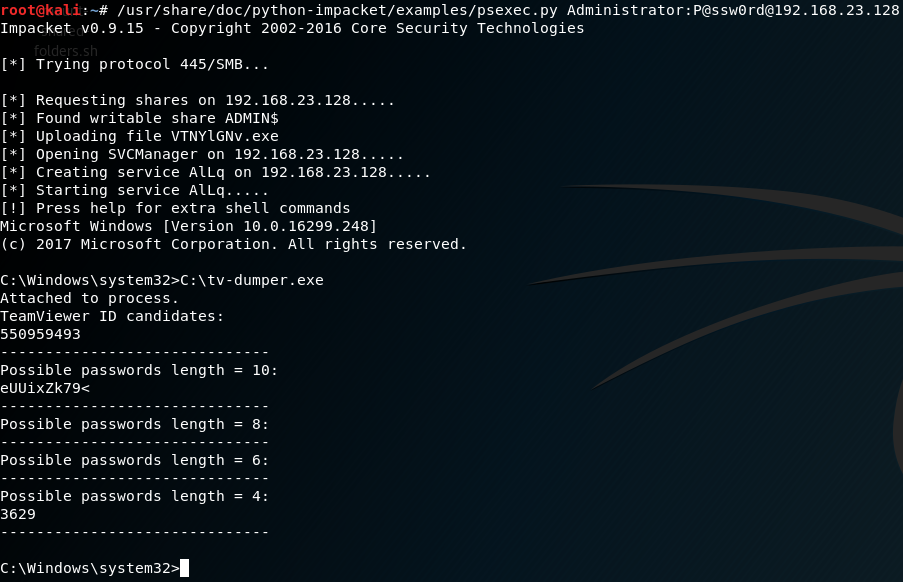
teamviewer-dumper preview

teamviewer-dumper

GitHubattackercan/teamviewer-dumper

메모리에서 TeamViewer ID와 비밀번호를 덤프합니다. 다른 도구들보다 훨씬 더 잘 작동합니다.

password-crackingreconnaissancememory-forensics+3
988년 전
이전1…456…19다음