

zentinel
 zentinelproxy/zentinel
無料のウェブを守るために構築された、セキュリティ優先のリバースプロキシ。
authentication-authorizationdefensive-toolscontainer-security+6
1166日前
 gmh5225/llm-guard-service
AIサービスとやり取りする際のプロンプトインジェクション、ジェイルブレイク攻撃、有害なコンテンツに対する保護を提供するサービス。
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 owasp/owasp-top-10-neocloud-and-ai-data-center-security-risks
OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…
 stillbigjosh/kube-reaper
任意のIDからKubernetesクラスタをスキャンし、危険な権限を検出して、クラスタ侵害に至る多段階の権限昇格パスへと連鎖させます。
 haidang-infosec/phantom-grid
eBPFを活用したActive Defenseシステムで、Linuxサーバーを欺瞞的なハニーポットに変えます。透過的なトラフィックリダイレクト、OSフィンガープリントの偽装、カーネルレベルのDLP、Zero Trust SSHアクセス(SPA)を備えています。
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
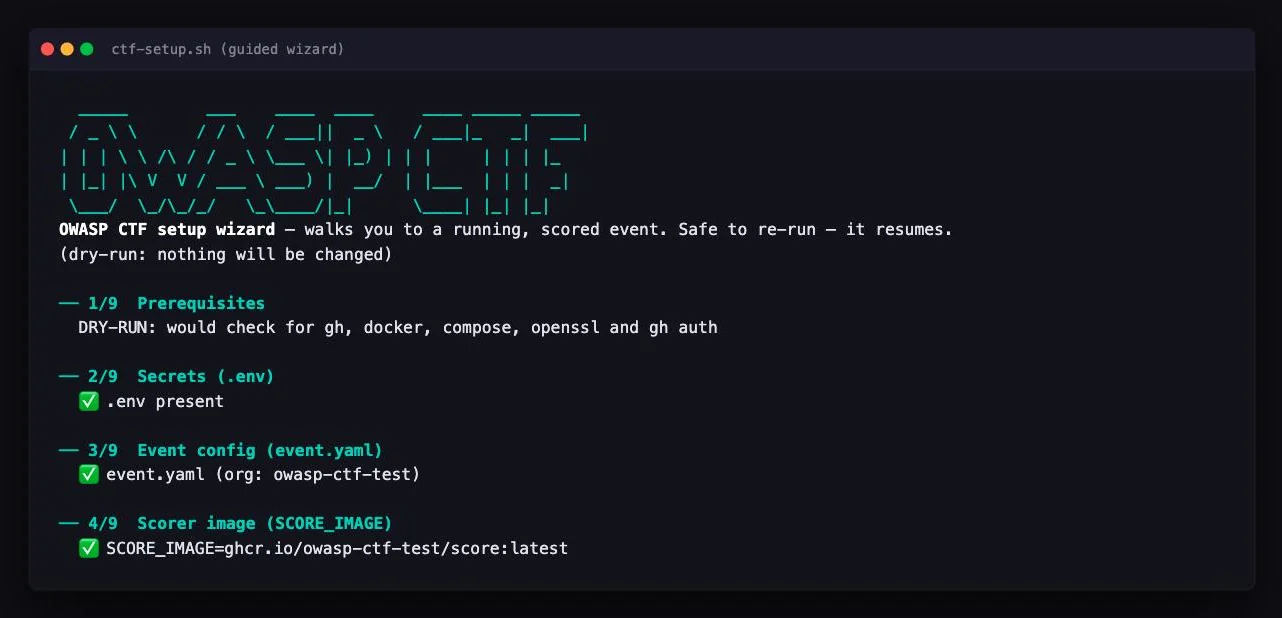 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
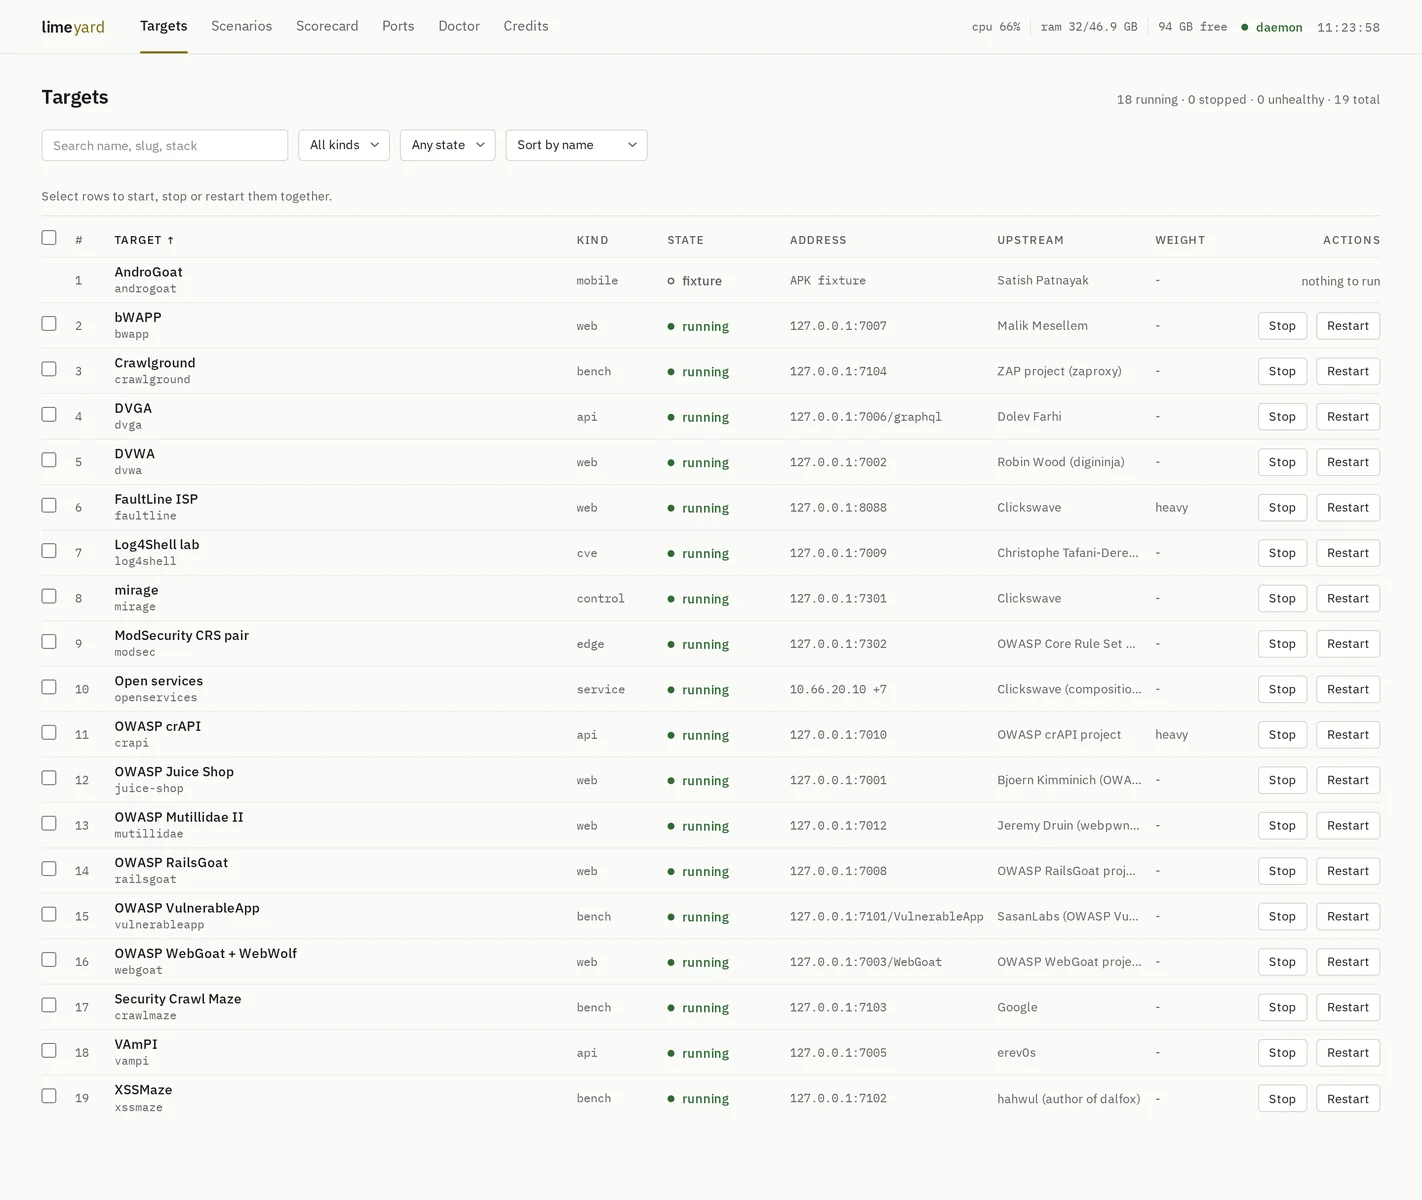 clickswave/limeyard
意図的に脆弱なDockerラボ。ルーティング可能なDNS環境と、ターゲットごとの機械可読な解答キーを備え、スキャナーの適合率、再現率、スコープをローカルで採点します。
 bombinisecurity/bombini
AyaベースのeBPFセキュリティ監視およびサンドボックス化エージェント
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 pbxqdown/portclue
LinuxのTCPポートが到達可能かどうかの理由を説明する
 bomfather/agent
カーネル空間で実行ファイルレベルのアクセスポリシーを強制し、LSMフックを介してプロセスをサンドボックス化し、ファイル、ネットワーク、GPUへのアクセスを制限するeBPFベースのLinuxエージェント。
 microsoft/mxc
Policy-driven, layered isolation and containment
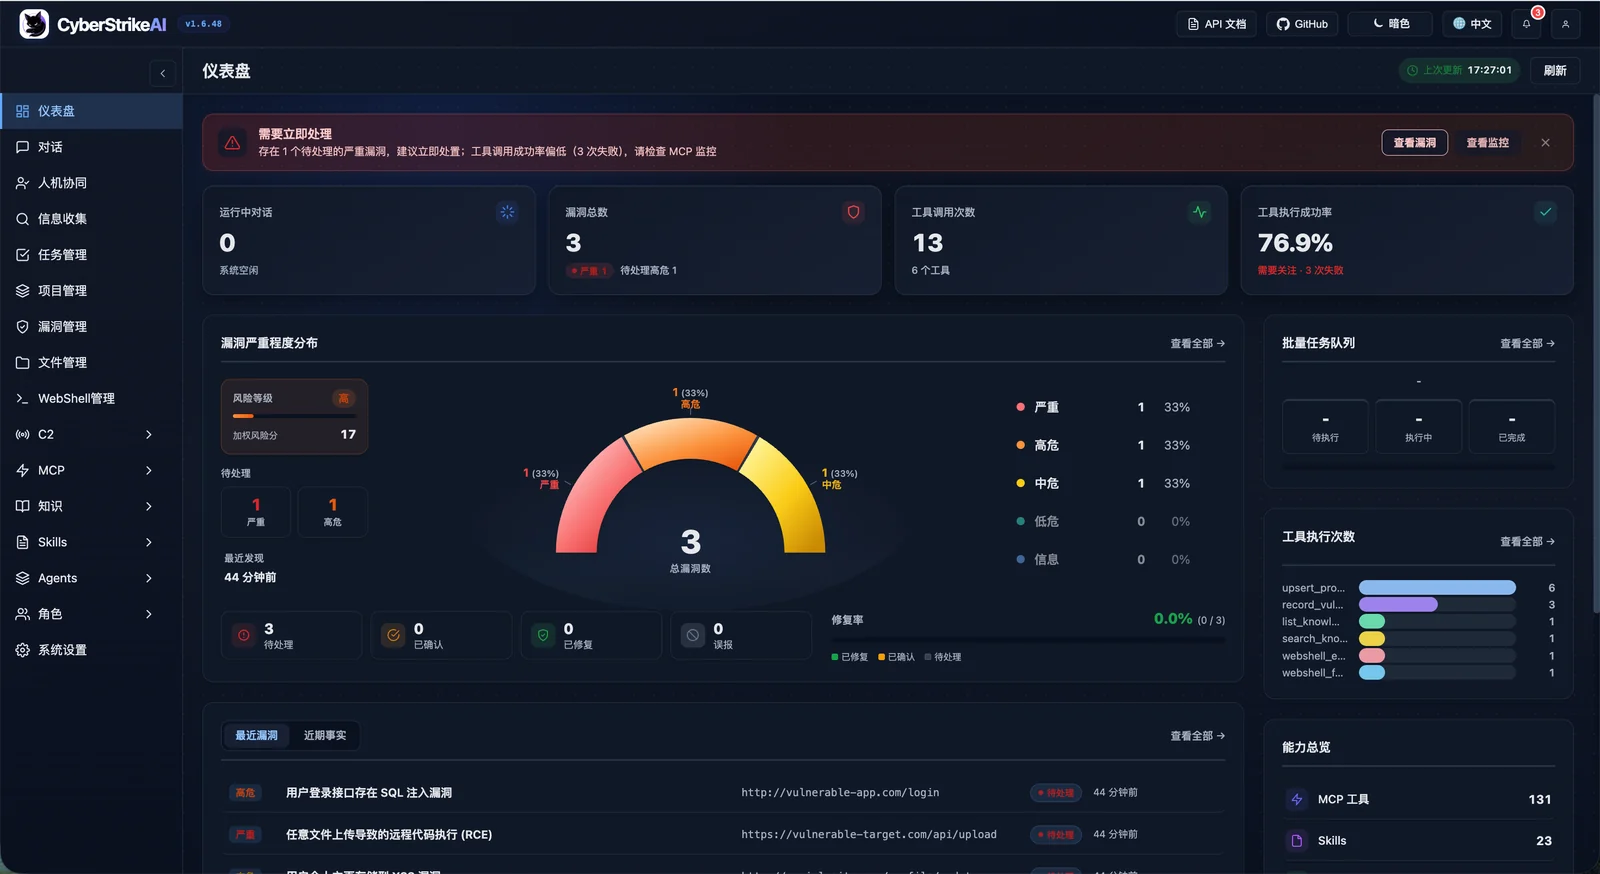 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…