

MCP-God-Mode
 gmh5225/mcp-god-mode
Wolltest du nicht schon immer, dass es einfach alles kann? 148 LEISTUNGSSTARKE Infosec-/Admin-Tools auf einem einzigen MCP-Server.
packet-sniffing-analysisport-scanningrfid-nfc-tools+9
1
gmh5225/mcp-god-modeWolltest du nicht schon immer, dass es einfach alles kann? 148 LEISTUNGSSTARKE Infosec-/Admin-Tools auf einem einzigen MCP-Server.
 hilmiazizi/oorecon
Terminal-UI für die Angriffsflächen-Erkundung: DNS-Recon, Subdomain-Enumeration, Port-Scanning, Reverse-IP, geleakte Login-URLs und…
 tegal1337/pocketpentester
Offline-first Android-Toolkit für offensive Sicherheit mit 21 Modulen für Recon, Port-Scanning, Subdomain-Enumeration, SQLi/XSS/JWT-Exploitation,…
 sleepingbag945/dddd
Batch-Tool zur Asset-Erfassung und Schwachstellen-Scanning für Red Teams. Zieht Ziele von Hunter, Fofa und Quake, führt Fingerprinting,…
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…
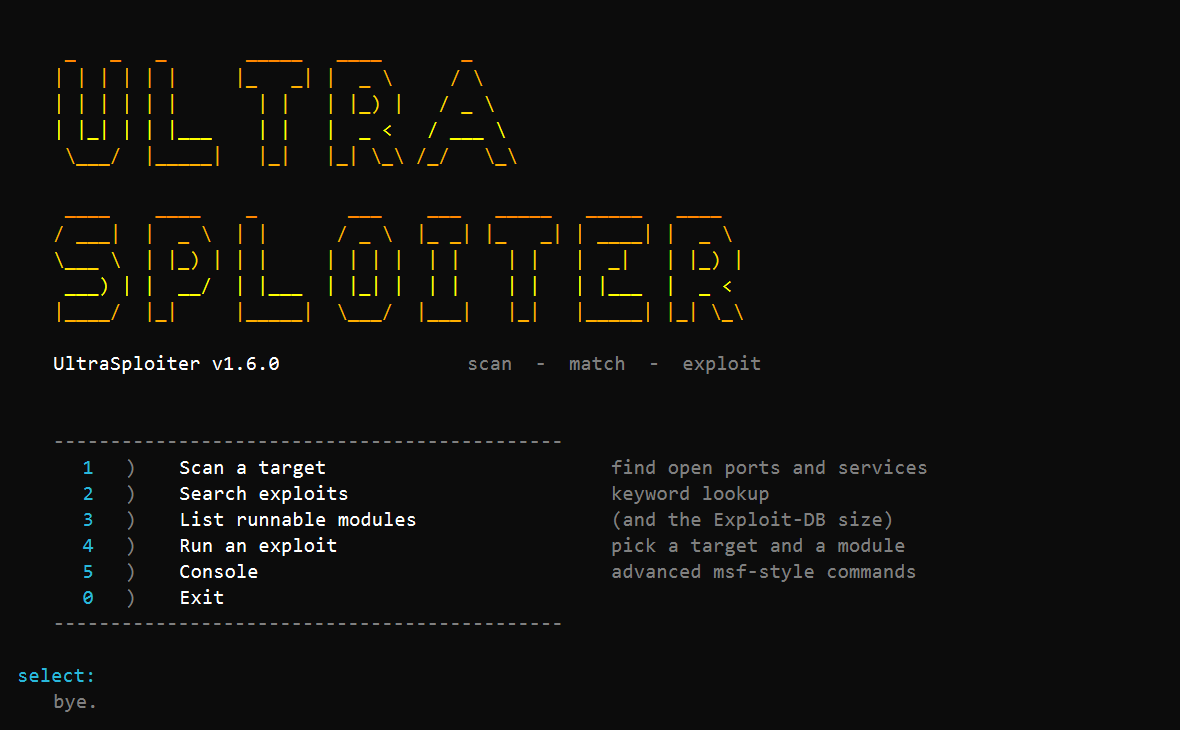
 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
 vqkro/higernes
a passive OSINT toolkit in python and c++ usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 ankhcorp/nuke.sh
Bash-basiertes Skript für passive Reconnaissance und Attack-Surface-Mapping, das ausschließlich öffentliche APIs und Standard-Linux-Tools (curl, dig,…
 mmarting/unwaf
Go-Tool, das passiv die echte Origin-IP hinter einem WAF/CDN mithilfe mehrerer OSINT-Quellen entdeckt und Kandidaten anschließend über…
 simplifaisoul/osiris
Open-Source-Plattform für globale Aufklärung – Echtzeit-OSINT-Dashboard – Eine Palantir-Alternative – …
 divinelabio/argus
Das ultimative Toolkit zur Informationsbeschaffung
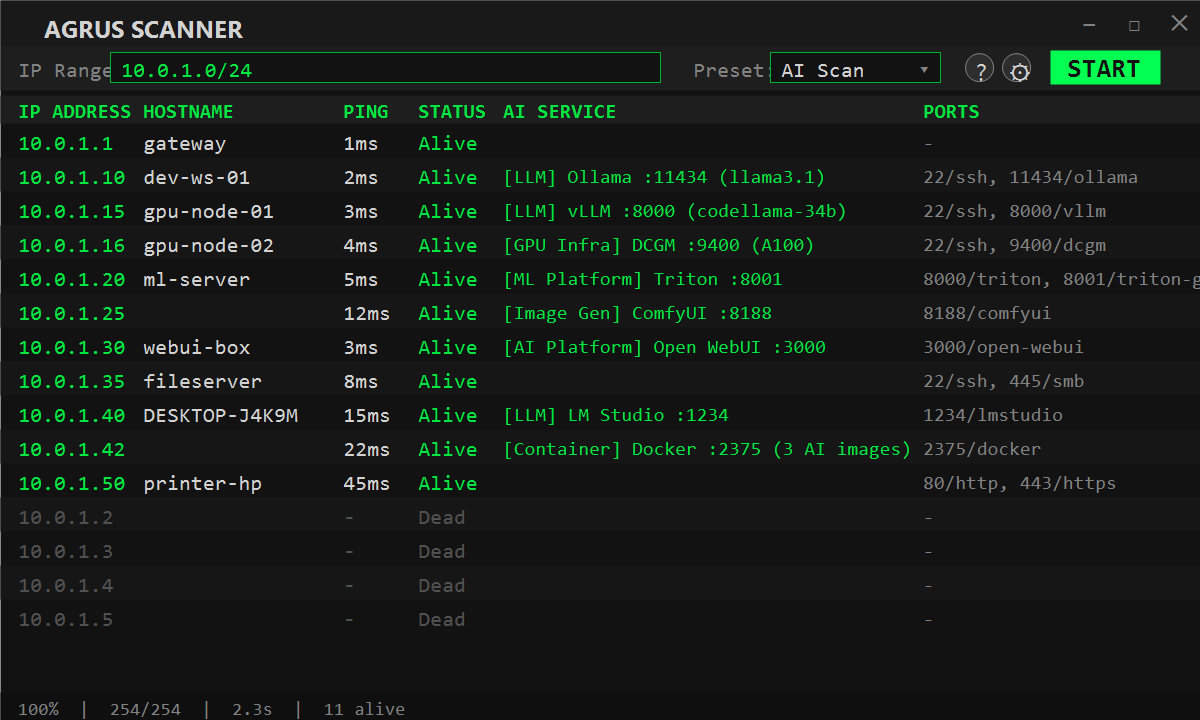 nybaywatch/agrusscanner
Windows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…
 vighnesh91/omnisec-hex
Browser-lokales Security-Monorepo mit sechs Modulen für mobile APK/IPA-Triage, clientseitiges DAST-Fuzzing, OSINT-Verzeichnisse,…
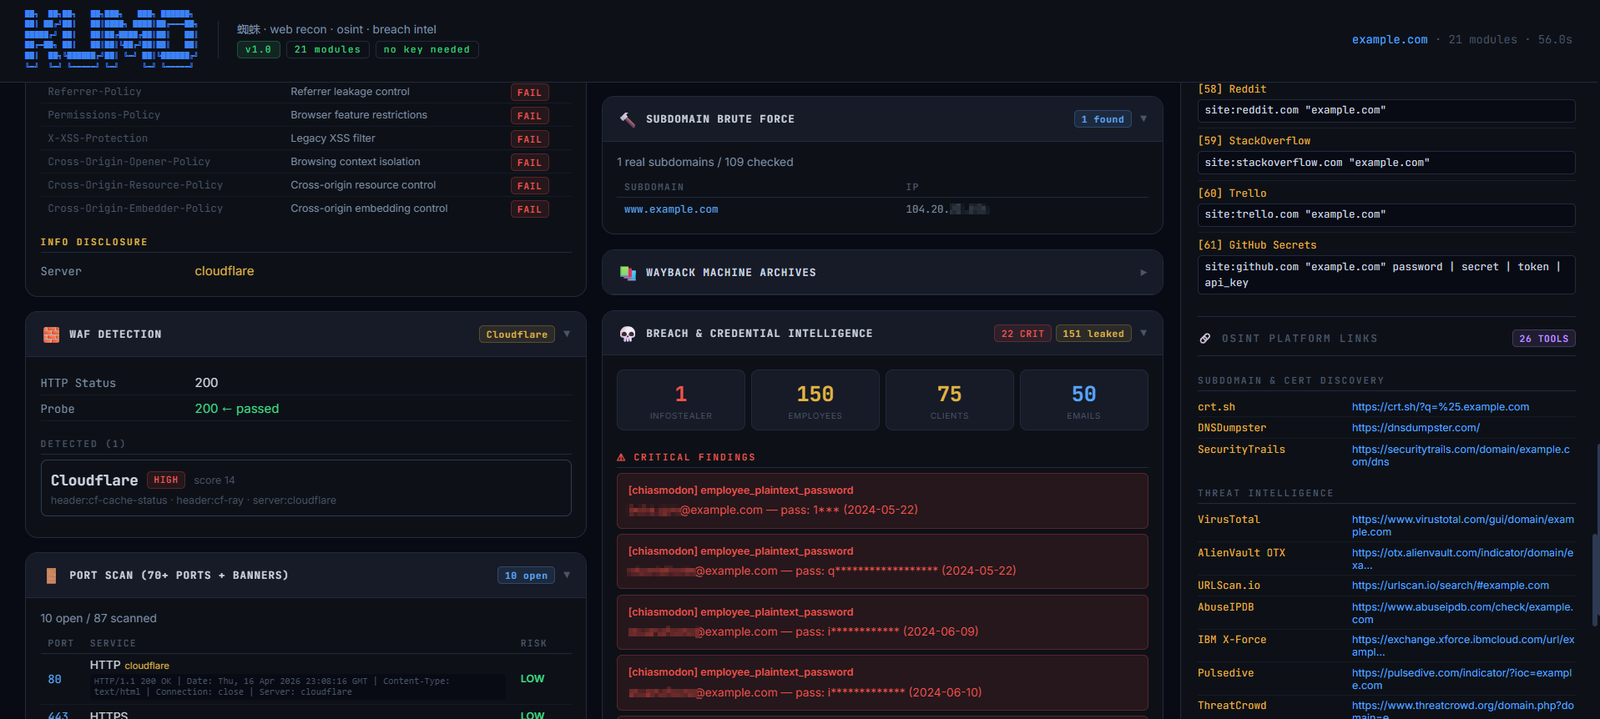 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 sakispat/simple-pentesting
Ein edukatives Python-Toolkit für autorisierte Penetrationstests: Threaded-Port-Scanner, Subdomain- und Verzeichnis-Enumeration, Banner-Grabber und…
 voidsecsoftwares/voidsec-proxy
Multi-Modul-Offensive-Security-Toolkit für SOCKS5-Proxy-Chaining, Port-Scanning, DNS-Enumeration, Hash-Cracking, Reverse-Shell-Generierung,…
 yeee3642/edu-recon
Autorisierter Recon- & Triage-Orchestrator für den Bildungssektor (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, Secret-/API-Key-Leak, XSS, wp2shell)…