

TornadoC2
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
penetration-testing-frameworkspersistence-mechanismsids-ips-evasion+9
2
kamalx06/tornadoc2Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 rapid7/metasploit-payloads
Einheitliches Repository für verschiedene Metasploit-Framework-Payloads
 g13net/lockjaw
Modulares Windows-C2-Framework mit einem Rust-Teamserver, Zig-Implantat, indirekten Syscalls, AMSI-Bypass, reflektiver/PoolParty-Injektion,…
 mythicagents/xenon
Ein in C geschriebener Mythic-Agent für Windows
 x3r0day/fud-c2-framework
Ein fileless Reverse Shell- und C2-Framework, das direkte Syscalls, Proxy-Tunneling und ChaCha20-Verschlüsselung zur AV-Umgehung nutzt.
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
 pr0xylife/qakbot
Threat-Intelligence- und Malware-Analyse-Repository mit Fokus auf einen Banking-Trojaner und ein Botnetz, mit IOCs, C2-Indikatoren und…
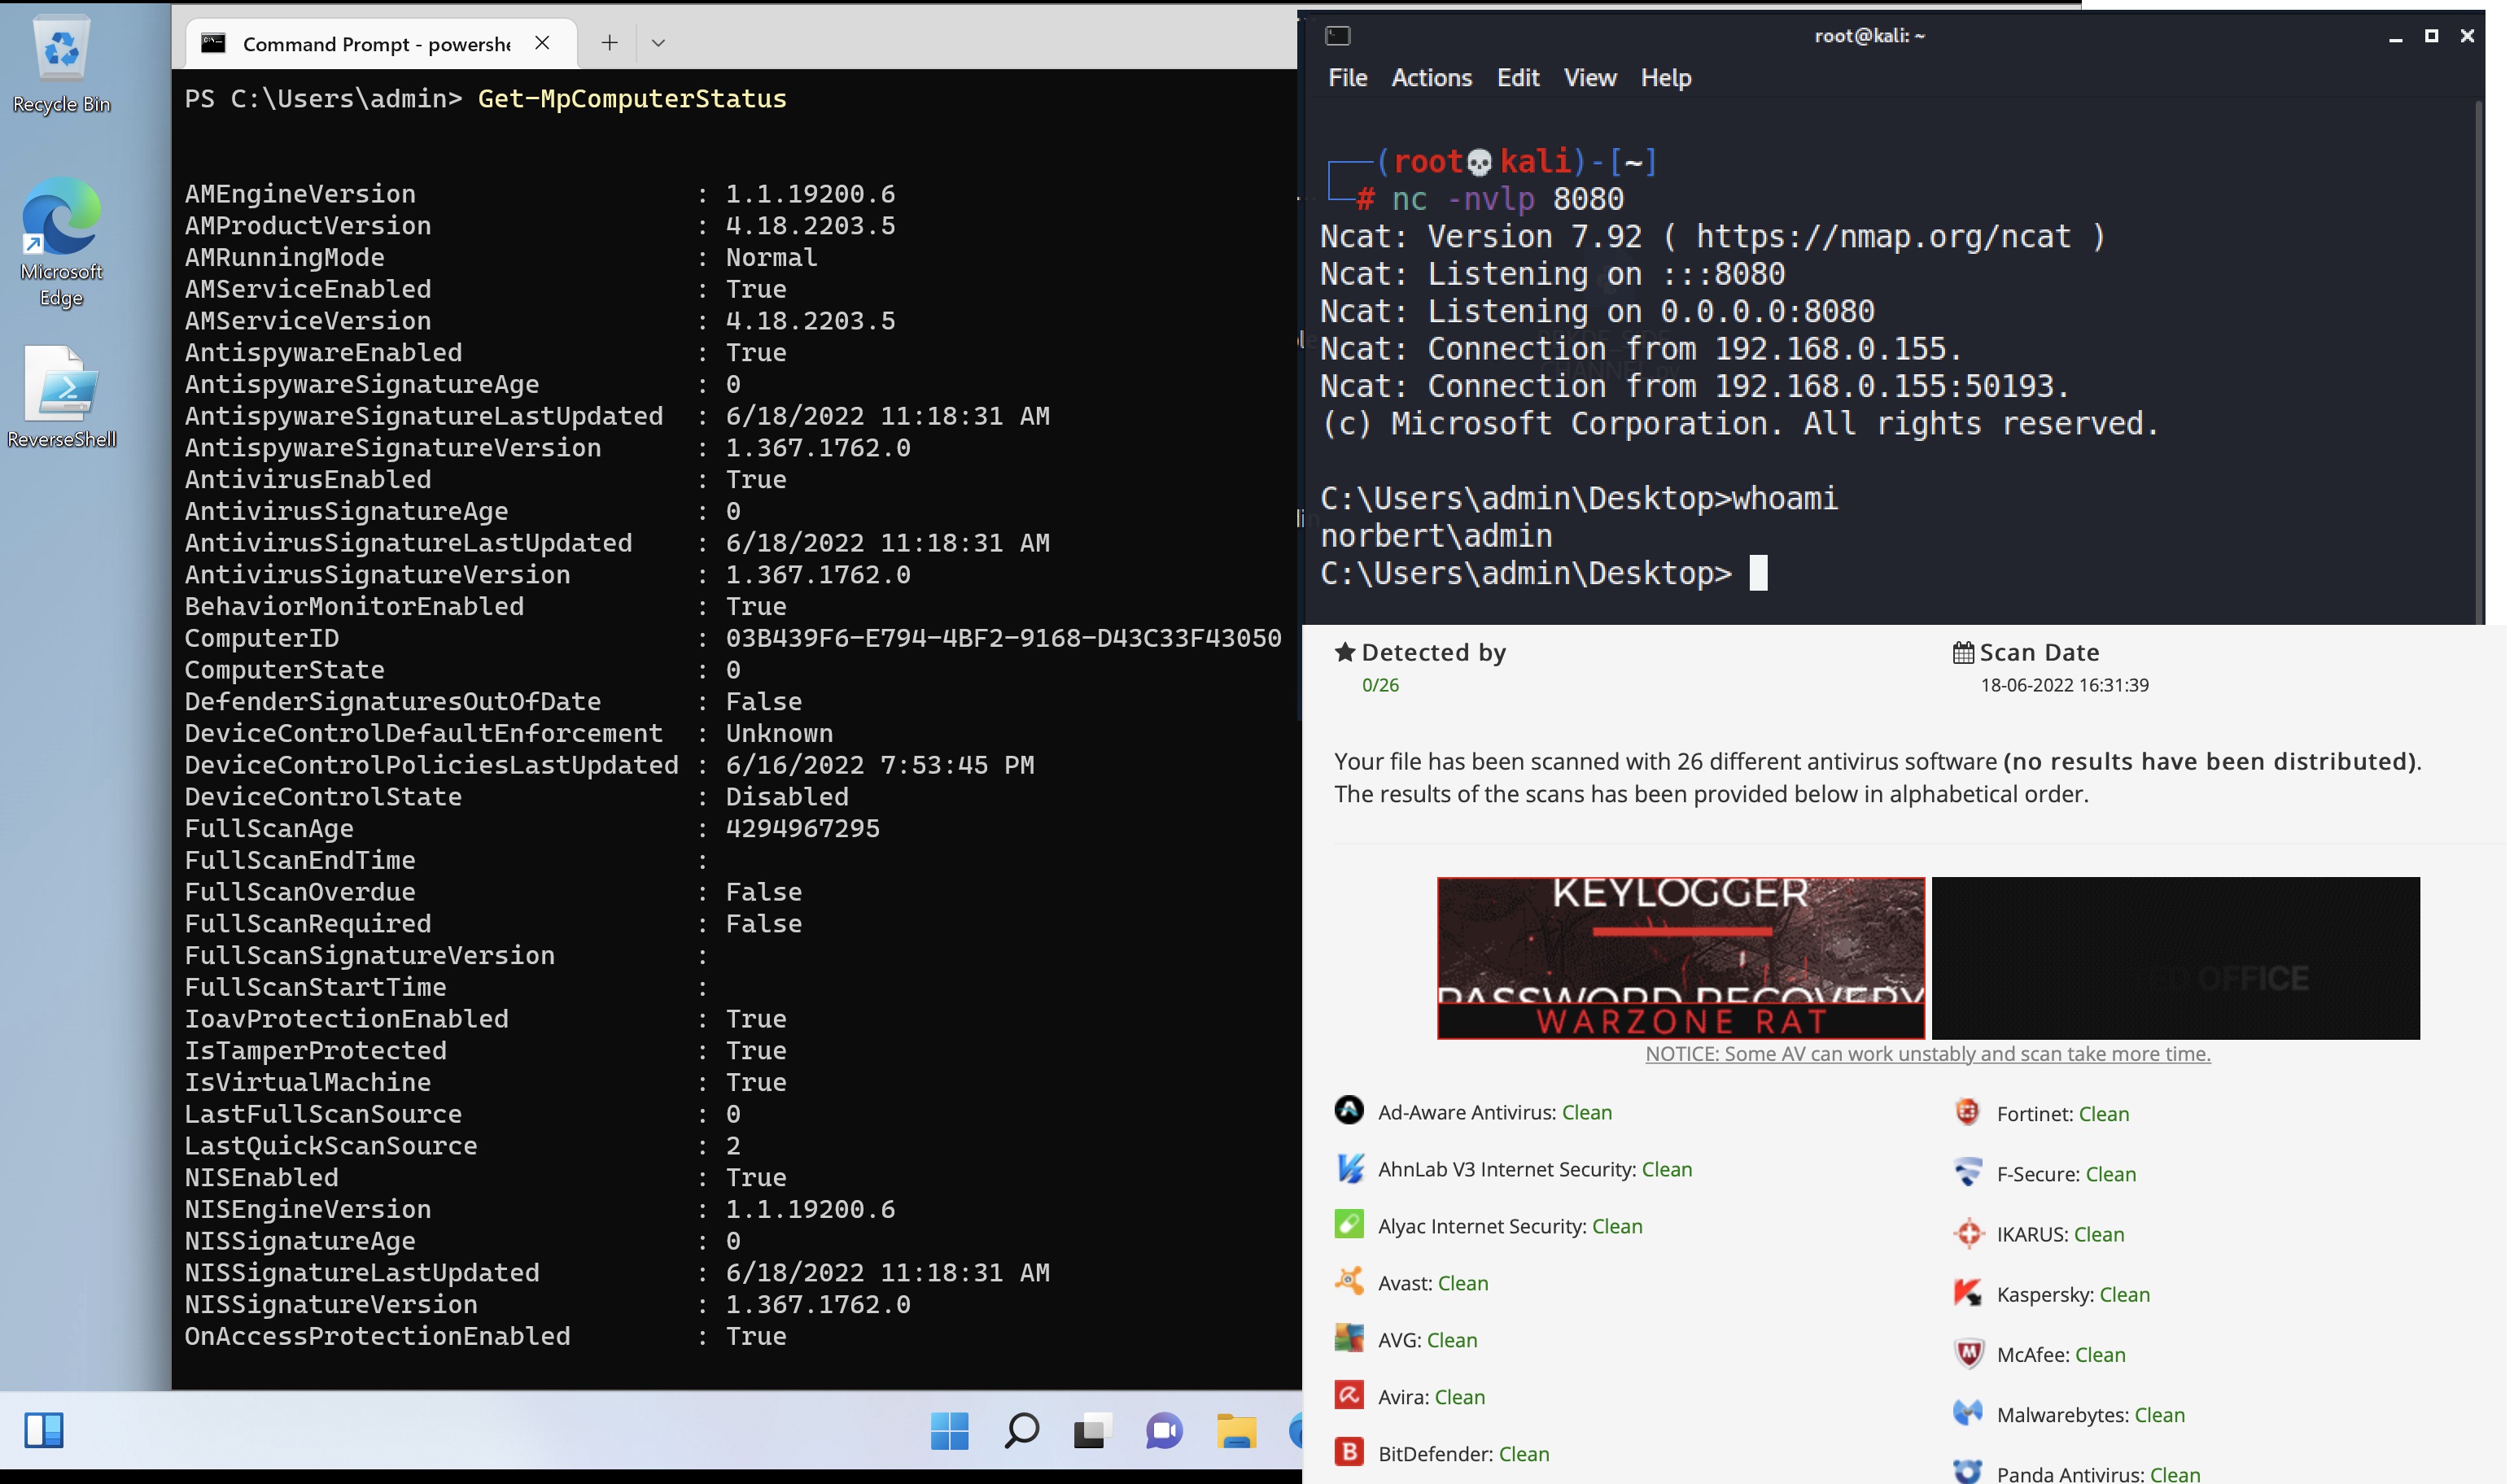 tihanyin/pssw100avb
Eine Liste nützlicher Powershell-Skripte mit 100 % AV-Bypass (zum Zeitpunkt der Veröffentlichung).
 bc-security/empire
Empire ist ein Post-Exploitation- und Adversary-Emulation-Framework, das verwendet wird, um Red Teams und Penetrationstester zu unterstützen.
 pr0xylife/gozi
Banking-Trojaner mit Browser-Injection- und Command-and-Control-Funktionen, verwendet zum Stehlen von Anmeldeinformationen und Finanzdaten; relevant…
 darkcodersc/subseven
SubSeven Legacy Offizielles Quellcode-Repository
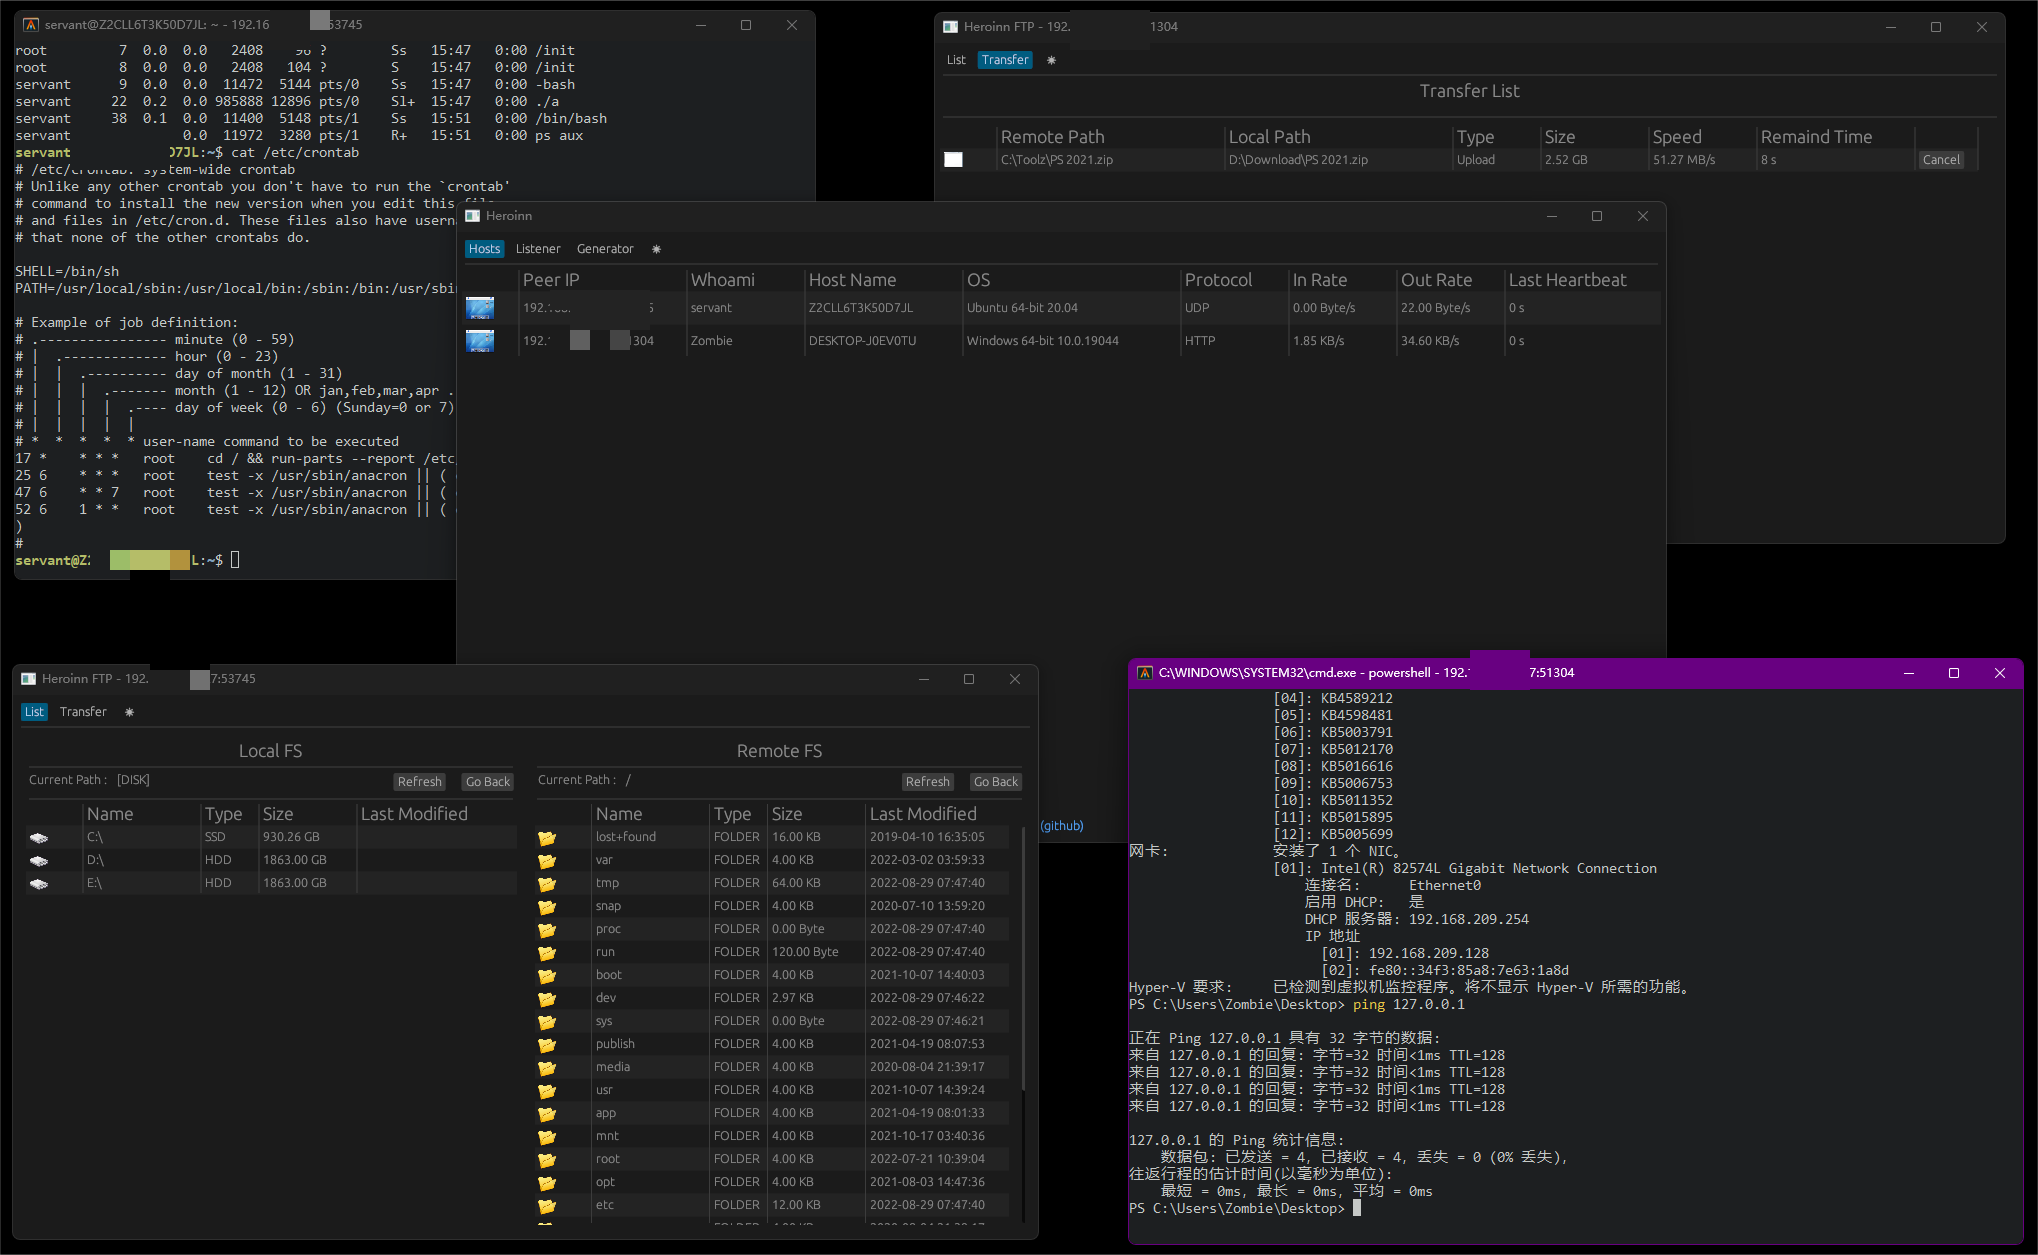 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 idov31/venom
Venom ist eine Bibliothek, die dazu dient, ausweichende Kommunikation mithilfe gestohlener Browser-Sockets durchzuführen.
 tsuyoken/imgbackdoor
Verstecke deine Payload in einer .jpg-Datei
 rvrsh3ll/rendezvousrat
Self-heilender RAT, der libp2p nutzt
 demon-i386/zoshrinkc2
Gezielte DNS-over-HTTPS-Malware (läuft nur einmal)