

Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
Memory Forensics — 도구 — 3페이지 | Kitploit

도구

전체Android SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
최신관련성인기최근 업데이트
327 결과
libpeconv preview

libpeconv

GitHubhasherezade/libpeconv

악성코드 분석 및 리버스 엔지니어링을 위해 수동 매핑, IAT 후킹, 메모리 덤핑, 그리고 임포트 재구축을 지원하는 사용자 정의 PE 로딩 및 조작 라이브러리.

memory-forensicsreverse-engineeringshellcode+4
1.4k

6개월 전
awesome-incident-response preview

awesome-incident-response

GitHubmeirwah/awesome-incident-response

침해 대응 및 DFIR 도구의 엄선된 목록으로, 메모리 및 디스크 포렌식, 증거 수집, 로그 분석, 플레이북, 보안 분석가를 위한 교육 자료를 포함합니다.

disk-forensicsmemory-forensicsforensics+9
9.5k6일 전
timesketch preview

timesketch

GitHubgoogle/timesketch

이벤트 로그를 수집, 검색, 주석 처리하여 침해 대응 및 DFIR 조사를 지원하는 협업형 포렌식 타임라인 분석 플랫폼입니다.

disk-forensicsioc-managementmemory-forensics+7
3.4k4일 전
avml preview

avml

GitHubmicrosoft/avml

포렌식 및 침해 대응을 위한 휴대용 Linux RAM 수집 도구로, 선택적 압축 및 원격 스트리밍을 지원하며 LiME 호환 이미지를 캡처합니다.

memory-forensicsforensicsdigital-forensics+1
1.1k6일 전
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

어떤 메모리 덤프든 살펴보세요. 숨겨진 것을 찾아내세요. 단일 정적 Rust 바이너리로 Linux + Windows 커널 포렌식 — Python이 필요 없습니다.

ioc-managementmemory-forensicsnetwork-forensics+7
122개월 전
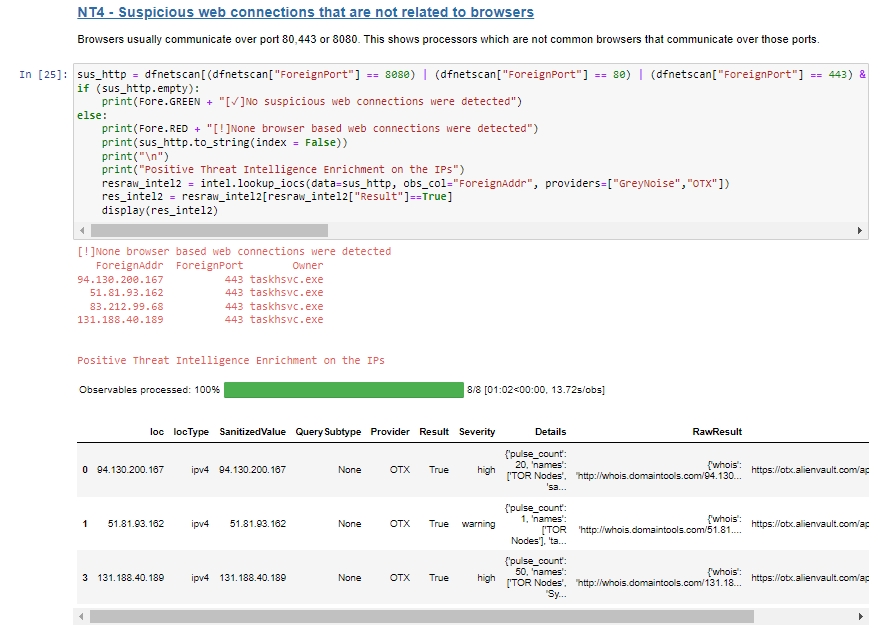
Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis preview

Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis

GitHubkaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis

드로퍼 GCleaner의 리버스 엔지니어링 분석: 복원력 있는 C2 인프라, 커널 드라이버 로딩, PowerShell/Conhost 실행, .rdata 페이로드 추출을 사용하는 악성코드입니다. 30개 이상의 C2 도메인, NtLoadDriver 및 전체 API 목록을…
privilege-escalationmemory-forensicspersistence-mechanisms+6
62개월 전
memdumper preview

memdumper

GitHubcenobyte-vincit/memdumper

macOS 디버거 entitlements와 DYLD_INSERT_LIBRARIES를 악용하여 실행 중인 프로세스의 메모리를 덤프하거나 검색하면서 EDR 귀속을 서명된 헬퍼 바이너리로 전환합니다.

memory-forensicsids-ips-evasioninformation-gathering+4
12개월 전
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

C2 도메인(198.46.86.63, tempuri.org), Windows Defender 우회 및 7200 KB 페이로드 추출을 사용하는 .NET 기반 정보 탈취형 악성코드 RedLine Stealer에 대한 리버스 엔지니어링 분석입니다.

memory-forensicspersistence-mechanismsreverse-engineering+4
12개월 전
keepass-exfil-forensics preview

keepass-exfil-forensics

GitHubpugazhendii22/keepass-exfil-forensics

TryHackMe DFIR 챌린지에 대한 네트워크 포렌식 분석 글 + 도구: PCAP 트래픽에서 hex→Base64→XOR 방식의 외부 유출(exfiltration) 체인을 역분석한 다음, CVE-2023-32784를 통해 프로세스 메모리 덤프에서 KeePass…
packet-sniffing-analysispassword-crackingmemory-forensics+6
2개월 전
mal_unpack preview

mal_unpack

GitHubhasherezade/mal_unpack

동적 PE-sieve 기반 언패커
dynamic-analysis-sandboxingmemory-forensicsreverse-engineering+2
8276개월 전
GarbageMan preview

GarbageMan

GitHubwithsecurelabs/garbageman

GarbageMan은 힙 분석을 통해 .NET 바이너리를 분석하기 위한 도구 모음입니다.

memory-forensicsreverse-engineeringdata-exfiltration+3
1213년 전
physmem2profit preview

physmem2profit

GitHubreverseclabs/physmem2profit

Physmem2profit는 원격으로 물리 메모리를 분석하여 대상 호스트의 LSASS 프로세스에 대한 미니덤프를 생성하는 데 사용할 수 있습니다.
memory-forensicspassword-attacksdata-exfiltration+4
4224년 전
memOptix preview

memOptix

GitHubblueteam0ps/memoptix

Volatility 메모리 추출 프레임워크에서 생성된 출력 분석을 지원하는 Jupyter 노트북.
memory-forensicsforensicsdigital-forensics+2
983년 전
AzTokenFinder preview

AzTokenFinder

GitHubhackmichnet/aztokenfinder

Office, Edge, Teams 및 PowerShell 전반에서 x64 프로세스 메모리와 TokenBroker 캐시 파일을 검색하여 Azure AD/O365 JWT 토큰을 수집하는 공격형 토큰 수집 유틸리티입니다.

memory-forensicspost-exploitationpenetration-testing+3
1093년 전
Awesome-CobaltStrike preview

Awesome-CobaltStrike

GitHubzer0yu/awesome-cobaltstrike

Awesome CobaltStrike 리소스 목록
memory-forensicsids-ips-evasionlateral-movement+7
4.4k3년 전
truffleproc preview

truffleproc

GitHubcontrolplaneio/truffleproc

truffleproc — 프로세스 메모리에서 시크릿을 사냥하는 도구 (TruffleHog & gdb 매시업)
memory-forensicsdebuggersdigital-forensics+1
1283년 전
TickTock preview

TickTock

GitHubwithsecurelabs/ticktock

Windows 타이머 큐 타이머를 열거하여 Ekko 슬립 난독화를 탐지하며, 회피형 메모리 상주 위협을 식별하는 데 있어 메모리 포렌식 및 악성코드 분석을 지원합니다.

defensive-toolsmemory-forensicsmalware-analysis
1134년 전
SuperMem preview

SuperMem

GitHubcrowdstrike/supermem

트라이지 유형에 따라 Windows 메모리 이미지를 처리하도록 개발된 Python 스크립트입니다.

memory-forensicsforensicsmalware-analysis+2
2672년 전
이전1234…19다음