
sift-hardened
 lgranadoi/sift-hardened
# CVE-2026-85625 向けにセキュリティ強化された sift 17.1.3 のフォーク。crcn/sift.js とは無関係です。
static-analysisvulnerability-analysiscode-analysis+2
lgranadoi/sift-hardened# CVE-2026-85625 向けにセキュリティ強化された sift 17.1.3 のフォーク。crcn/sift.js とは無関係です。
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
 disrex-group/stylesmuggler-adobe-patches
composer requireによる、cweagans/composer-patchesを介したAdobe公式APSB26-146(CVE-2026-75650)のMagento向け修正の配信。お使いのMagentoバージョンに適したパッチを自動選択します。
 dev-sec/chef-os-hardening
このChef Cookbookは多数のセキュリティ関連設定を提供し、包括的な基本保護を実現します。
 dev-sec/puppet-os-hardening
このPuppetモジュールは、数多くのセキュリティ関連の設定を提供し、全方位的な基本保護を実現します。
 xiaoqimikko/netty-http2-check
Offline Java tool that scans jars and versions to determine exposure to seven netty-codec-http2 CVEs, recommending the single patched version that…
 pigeonlabshq/pigeon
AIエージェントに対して、署名付き・スコープ限定の認証情報を用いて最小権限の委任を強制します。サブエージェントには狭い範囲の機能とリソースのみを付与し、実行前にアクションを検証して、権限昇格を防止します。
 pypa/advisory-database
PyPI上のPythonパッケージ向けのセキュリティアドバイザリをコミュニティで管理するデータベースであり、pip-auditやOSVなどのツールと統合するためのOSV形式の構造化された脆弱性データを提供します。
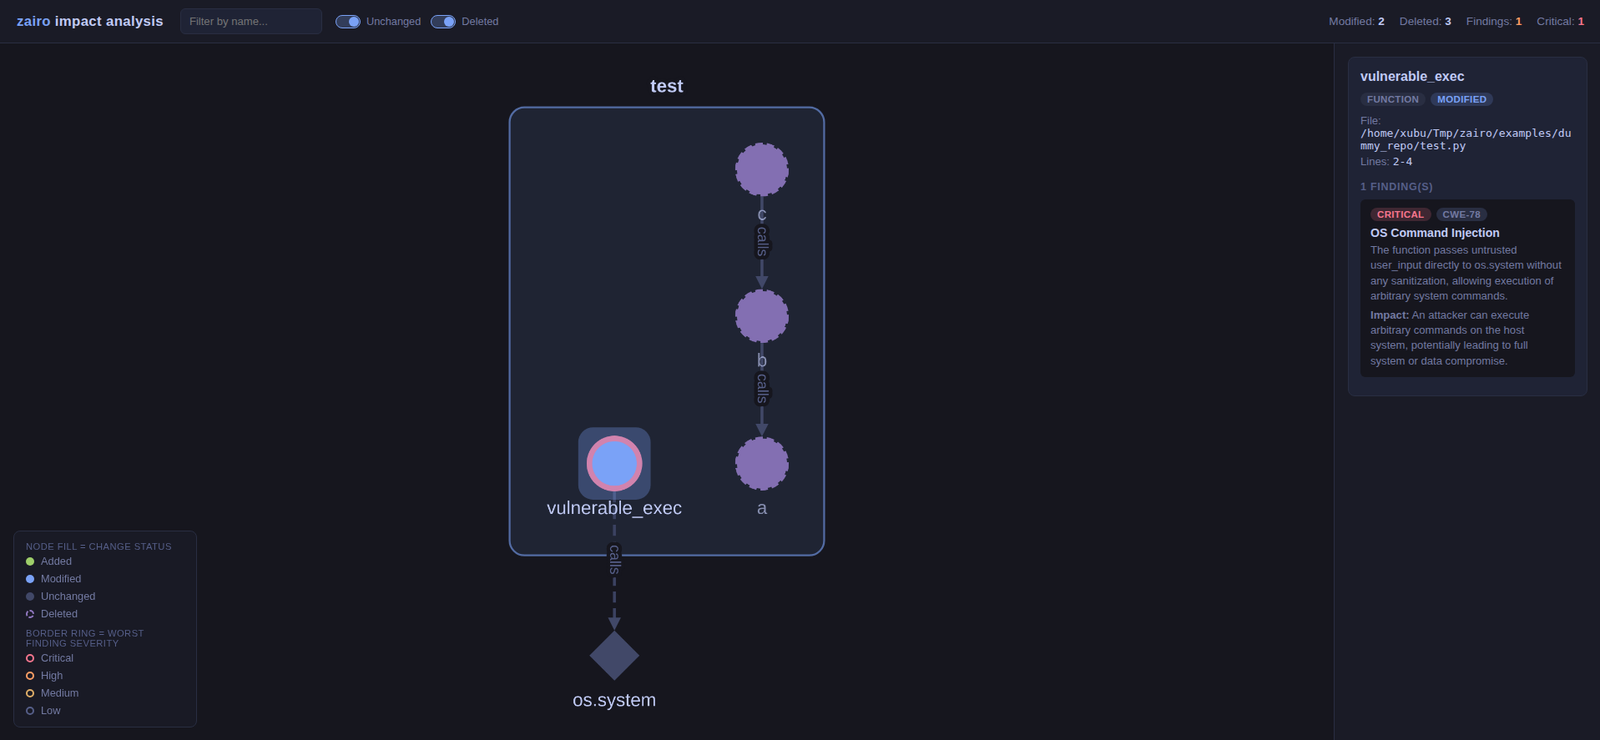 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 dannydoodlesstory/evm-audit-helpers
SolidityスニペットとFoundryスクリプトのコレクション(スマートコントラクトセキュリティ監査用)
 xiaoqimikko/thymeleaf-check
Offline checker for Thymeleaf CVE-2026-40477 / CVE-2026-41901 — tells you which of the two CVSS 9.0 SSTI flaws you are exposed to, and whether your…
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 dev-sec/chef-ssh-hardening
This chef cookbookは、安全なssh-clientおよびssh-server設定を提供します。
 dev-sec/puppet-ssh-hardening
このPuppetモジュールは、安全なssh-clientおよびssh-server設定を提供します。
 bakos-sandor-nx/teamcity-cve-2026-63077-remediation
# JetBrains TeamCity オンプレミス版 CVE-2026-63077 緊急ハードニング&パッチ適用ランブックパッケージ
 xiaoqimikko/tomcat85-check
CVE-2025-55752:Tomcat 8.5 已 EOL,终版 8.5.100。Apache 逐条声明「8.5 也受影响」的 2025 CVE 有 14 条,其中 10 条在 NVD 按 8.5.100 查不到。离线单 jar,读 conf/ 判断你到底中了哪几条。