
XXERipper
 kamalx06/xxeripper
Scanner XXE black-box che rileva iniezioni in-band, error-based e blind out-of-band tramite baselining statistico, fingerprinting del parser e…
reconnaissancevulnerability-scannersweb-vulnerability-scanners+9
13
kamalx06/xxeripperScanner XXE black-box che rileva iniezioni in-band, error-based e blind out-of-band tramite baselining statistico, fingerprinting del parser e…
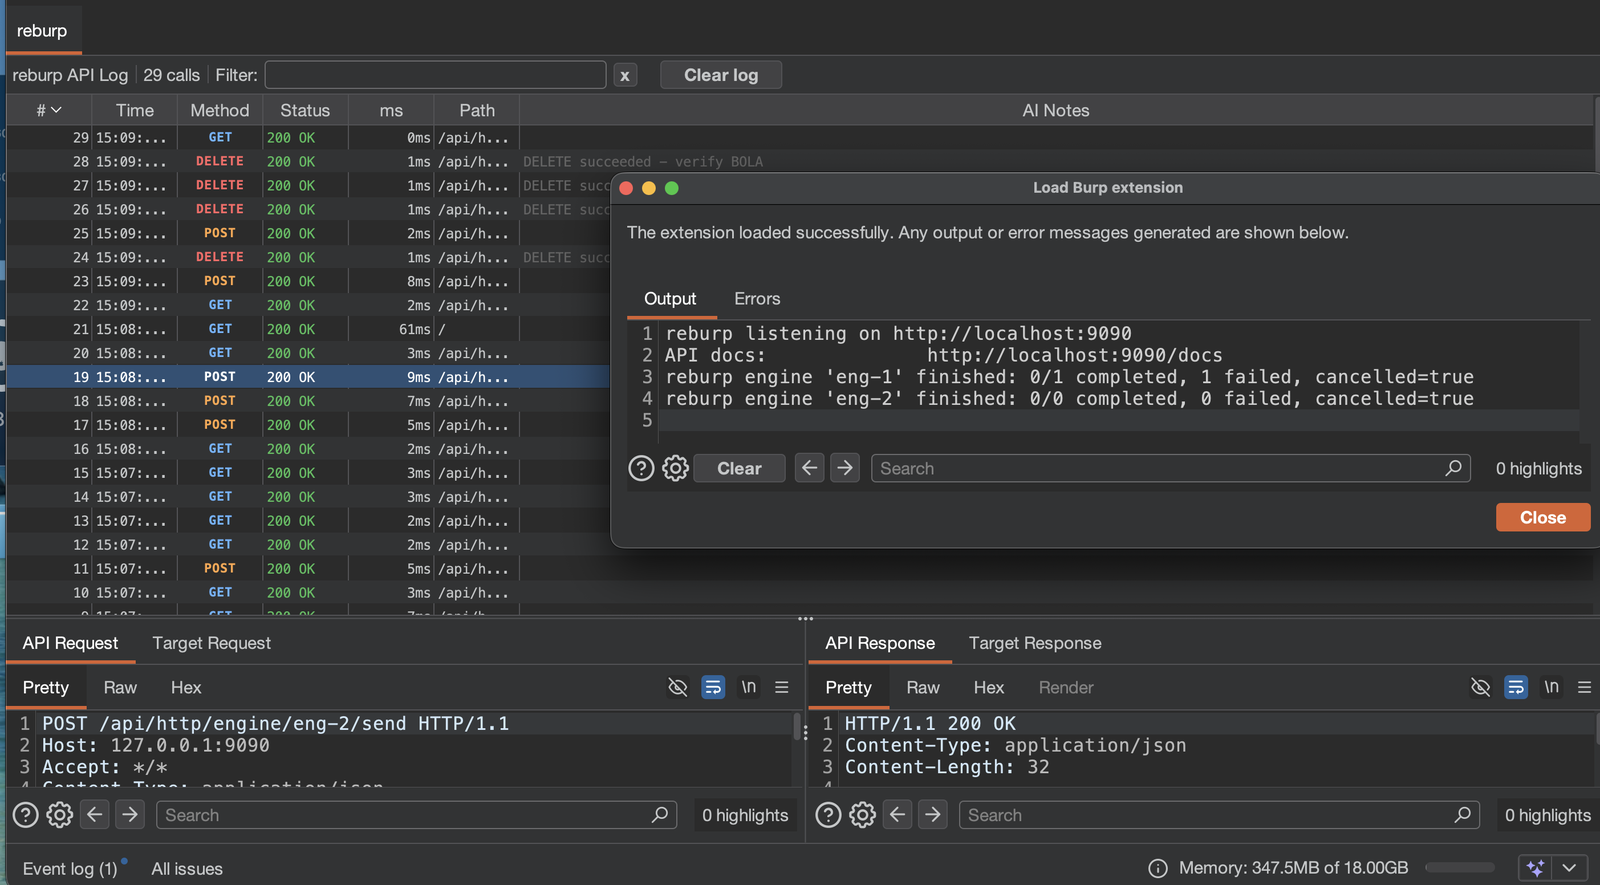 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
 t0xodile-swig/http3-adapter
Estensione di Burp Suite che intercetta le richieste e le invia tramite HTTP/3, convertendo le risposte per Burp, con supporto per richieste kettled…
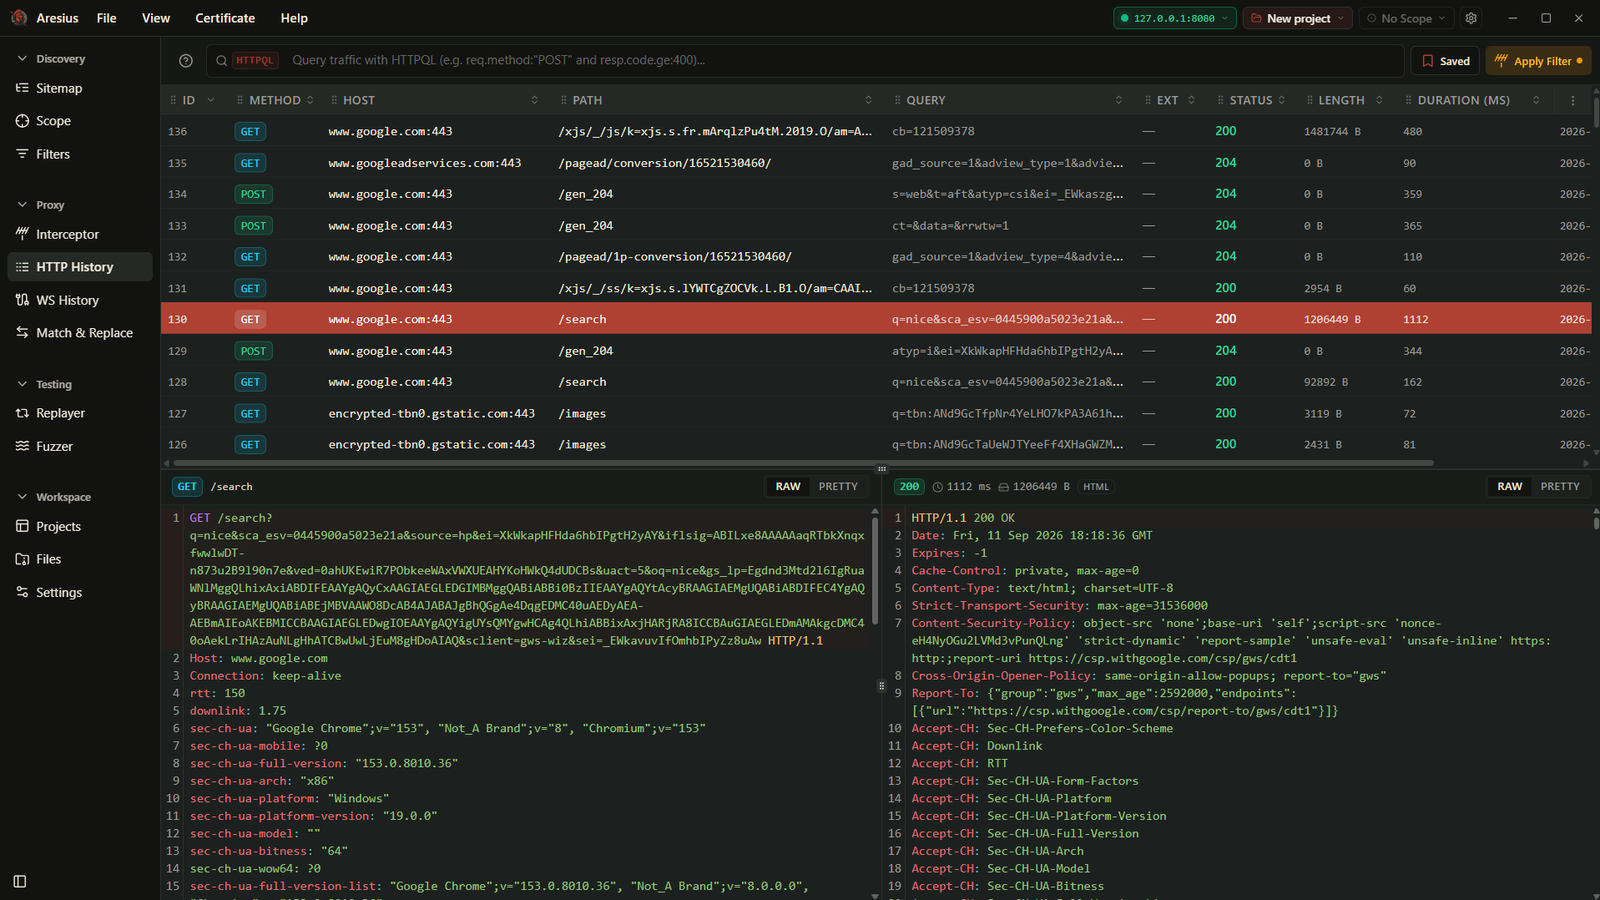 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 lumoslab-innovation/openhunterai
AI red team local-first per la sicurezza di applicazioni web, API e LLM. Ragionamento in stile attaccante, risultati supportati da evidenze e…
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 vid4l-07/roxy
Proxy HTTP di intercettazione basato su terminale con TUI per catturare, ispezionare e modificare le richieste in tempo reale, oltre a un Repeater…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 offensive360/mcp-server
Server MCP che esegue scansioni SAST su codebase locali e restituisce risultati con gravità e correzioni, consentendo agli assistenti AI di eseguire…
 intelligencex/sdk
SDK per interrogare il motore di ricerca e l'archivio dati di Intelligence X, con supporto per selettori come email, dominio, IP e telefono. Include…
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 j3ssie/dynast-bench
A DAST benchmark of intentionally-vulnerable apps with ground-truth answer keys for scoring scanners
 wi3memake/react2shell-scanner
Strumento di valutazione della sicurezza da riga di comando per applicazioni React e Next.js, che analizza i React Server Components per individuare…
 y-security/ylog4j
PortSwigger Burp Plugin per Log4j (CVE-2021-44228)
 cropnet/ni8mare
Strumento completo di rilevamento delle vulnerabilità per istanze di automazione dei workflow n8n. Rileva la vulnerabilità critica CVE-2026-21858…
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 httptoolkit/httptoolkit
HTTP Toolkit è uno strumento bellissimo e open-source per il debug, il test e la creazione di applicazioni con HTTP(S) su Windows, Linux e Mac :tada:…