

TornadoC2
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
penetration-testing-frameworkspersistence-mechanismsids-ips-evasion+9
2
kamalx06/tornadoc2Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 rapid7/metasploit-payloads
Repository unificato per diversi payload del Metasploit Framework
 g13net/lockjaw
Framework C2 modulare per Windows con teamserver in Rust, implant in Zig, syscall indirette, bypass AMSI, injection reflective/PoolParty, esecuzione…
 mythicagents/xenon
Un agente Mythic per Windows scritto in C
 x3r0day/fud-c2-framework
Un reverse shell fileless e un framework C2 che sfrutta syscall dirette, tunneling proxy e crittografia ChaCha20 per l'evasione degli AV.
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
 pr0xylife/qakbot
Repository di threat intelligence e analisi di malware incentrato su un trojan bancario e una botnet, con IOC, indicatori C2 e ricerca…
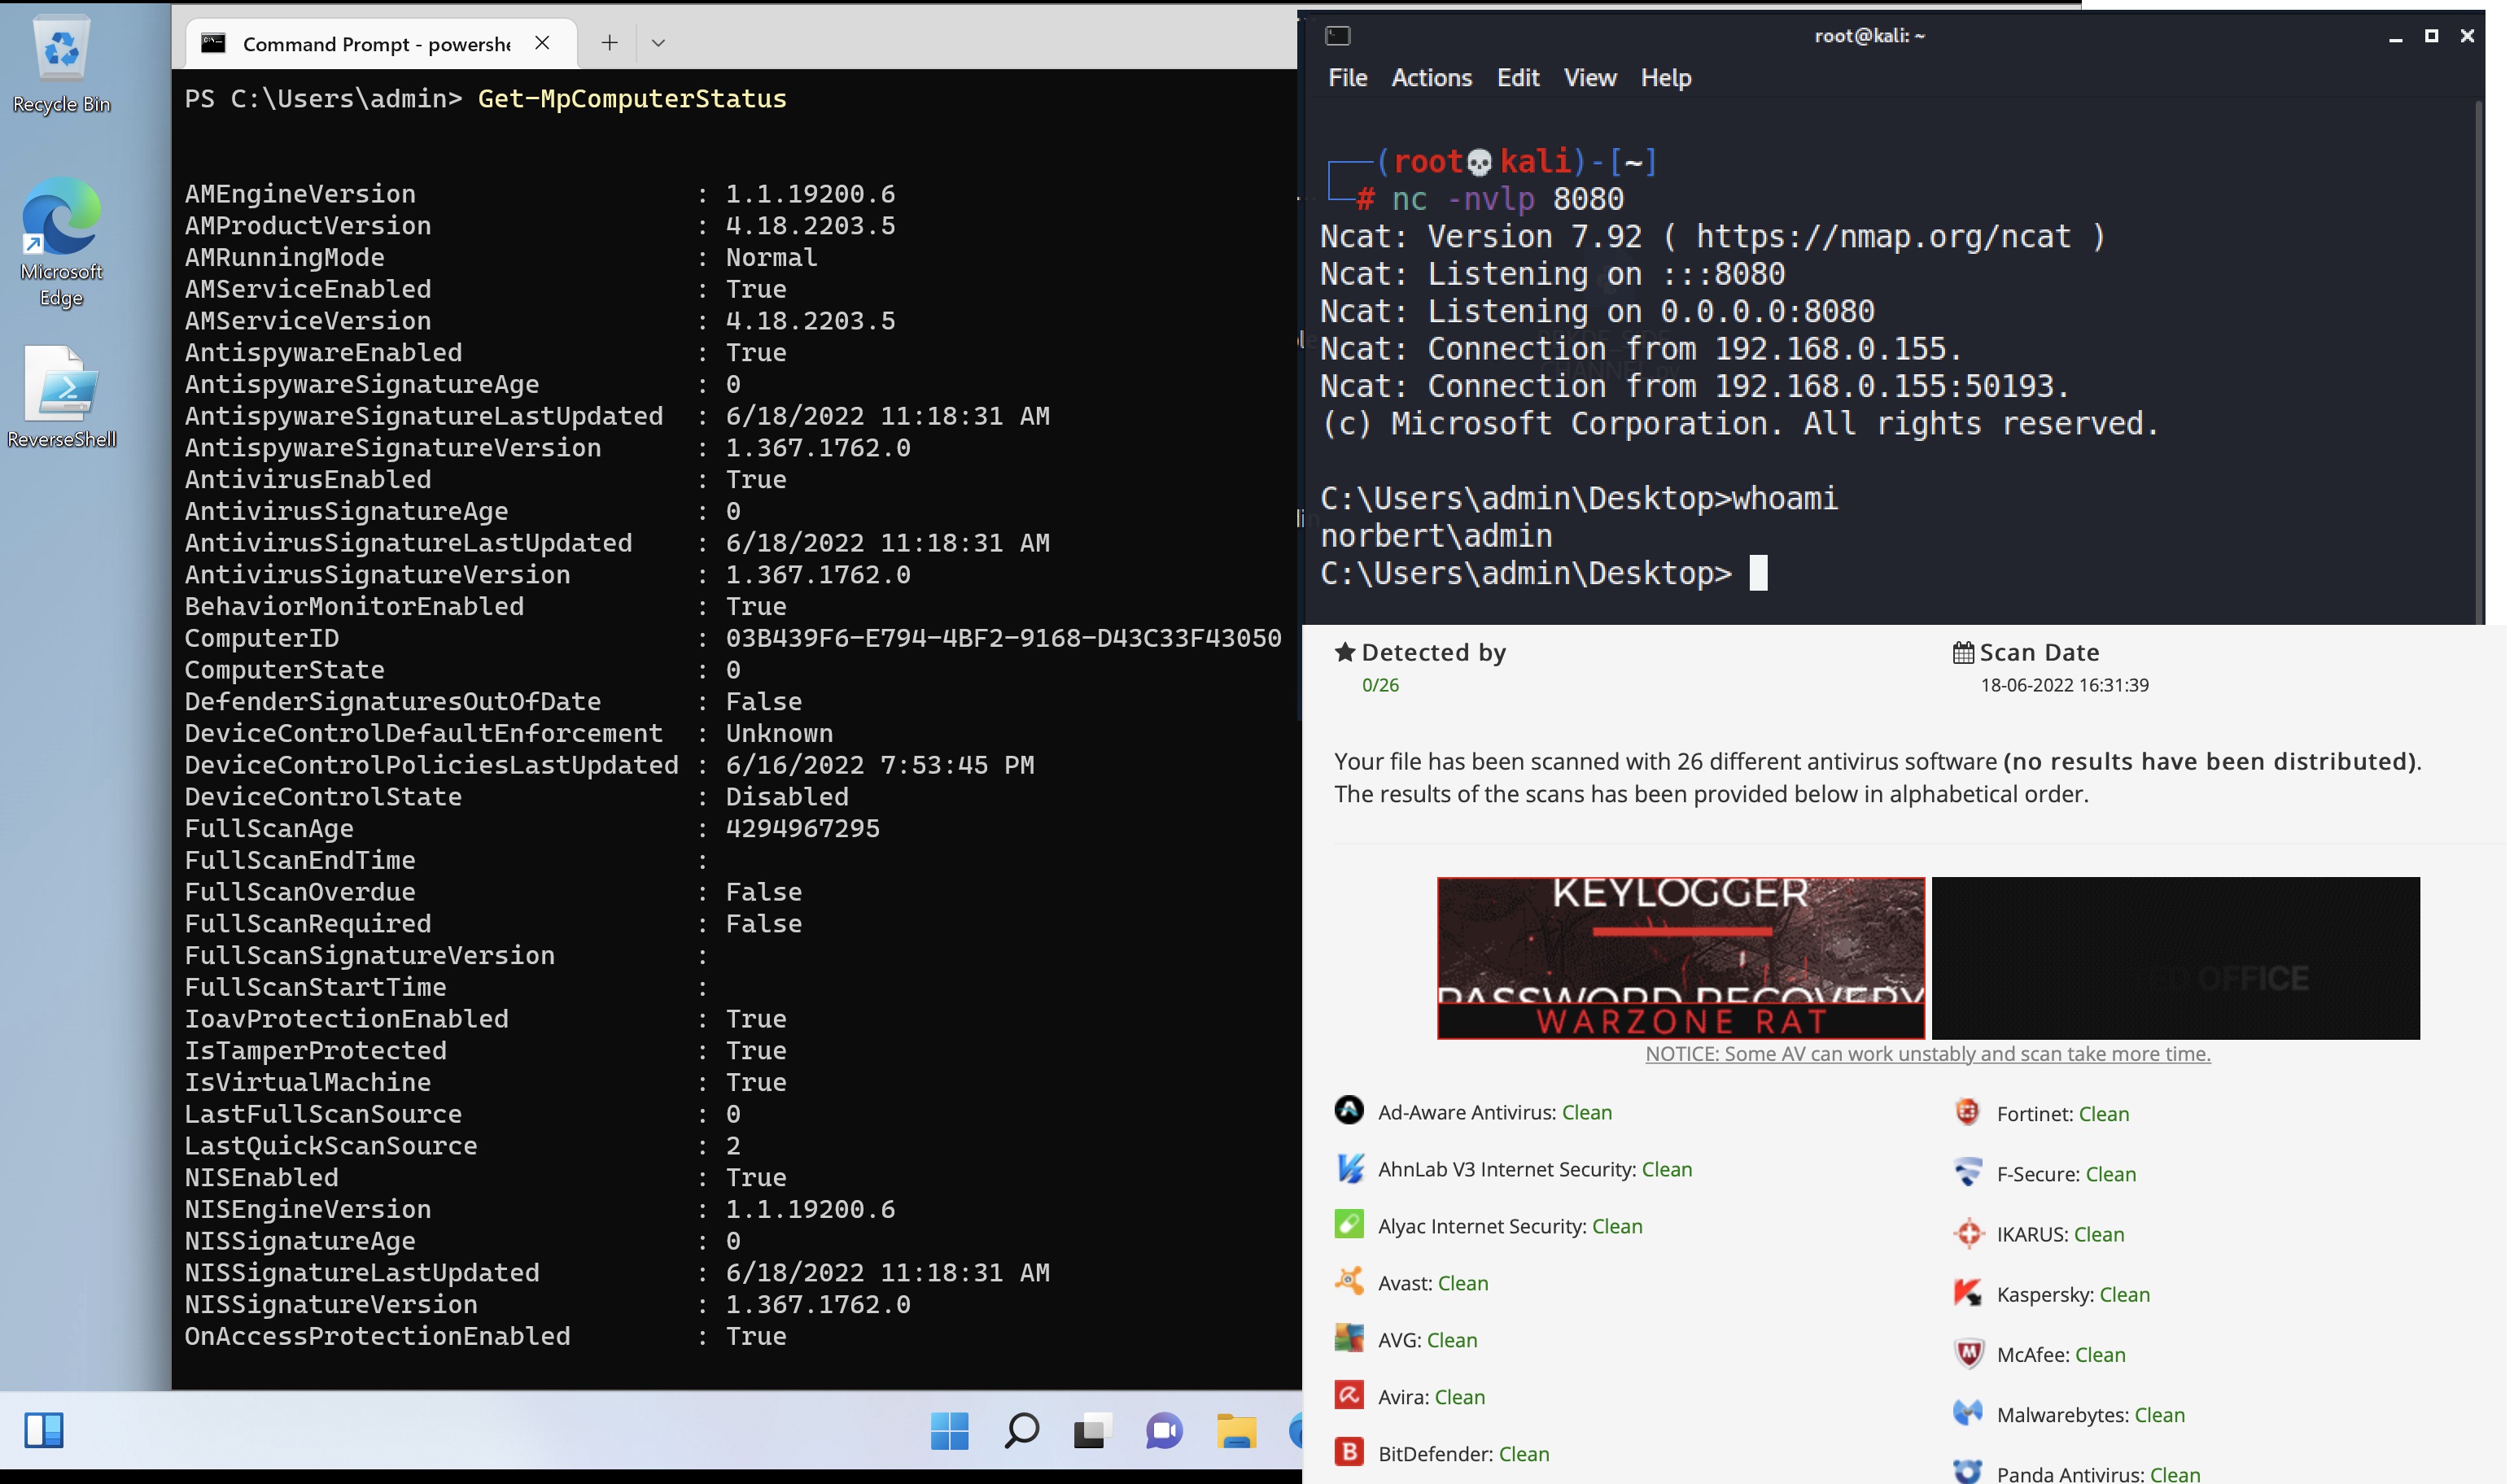 tihanyin/pssw100avb
Un elenco di script Powershell utili con bypass AV al 100% (Al momento della pubblicazione).
 bc-security/empire
Empire è un framework di post-exploitation ed emulazione avversaria utilizzato per aiutare Red Team e Penetration Tester.
 pr0xylife/gozi
Trojan bancario con capacità di browser-injection e command-and-control, utilizzato per rubare credenziali e dati finanziari; rilevante per l'analisi…
 darkcodersc/subseven
Repository ufficiale del codice sorgente legacy di SubSeven
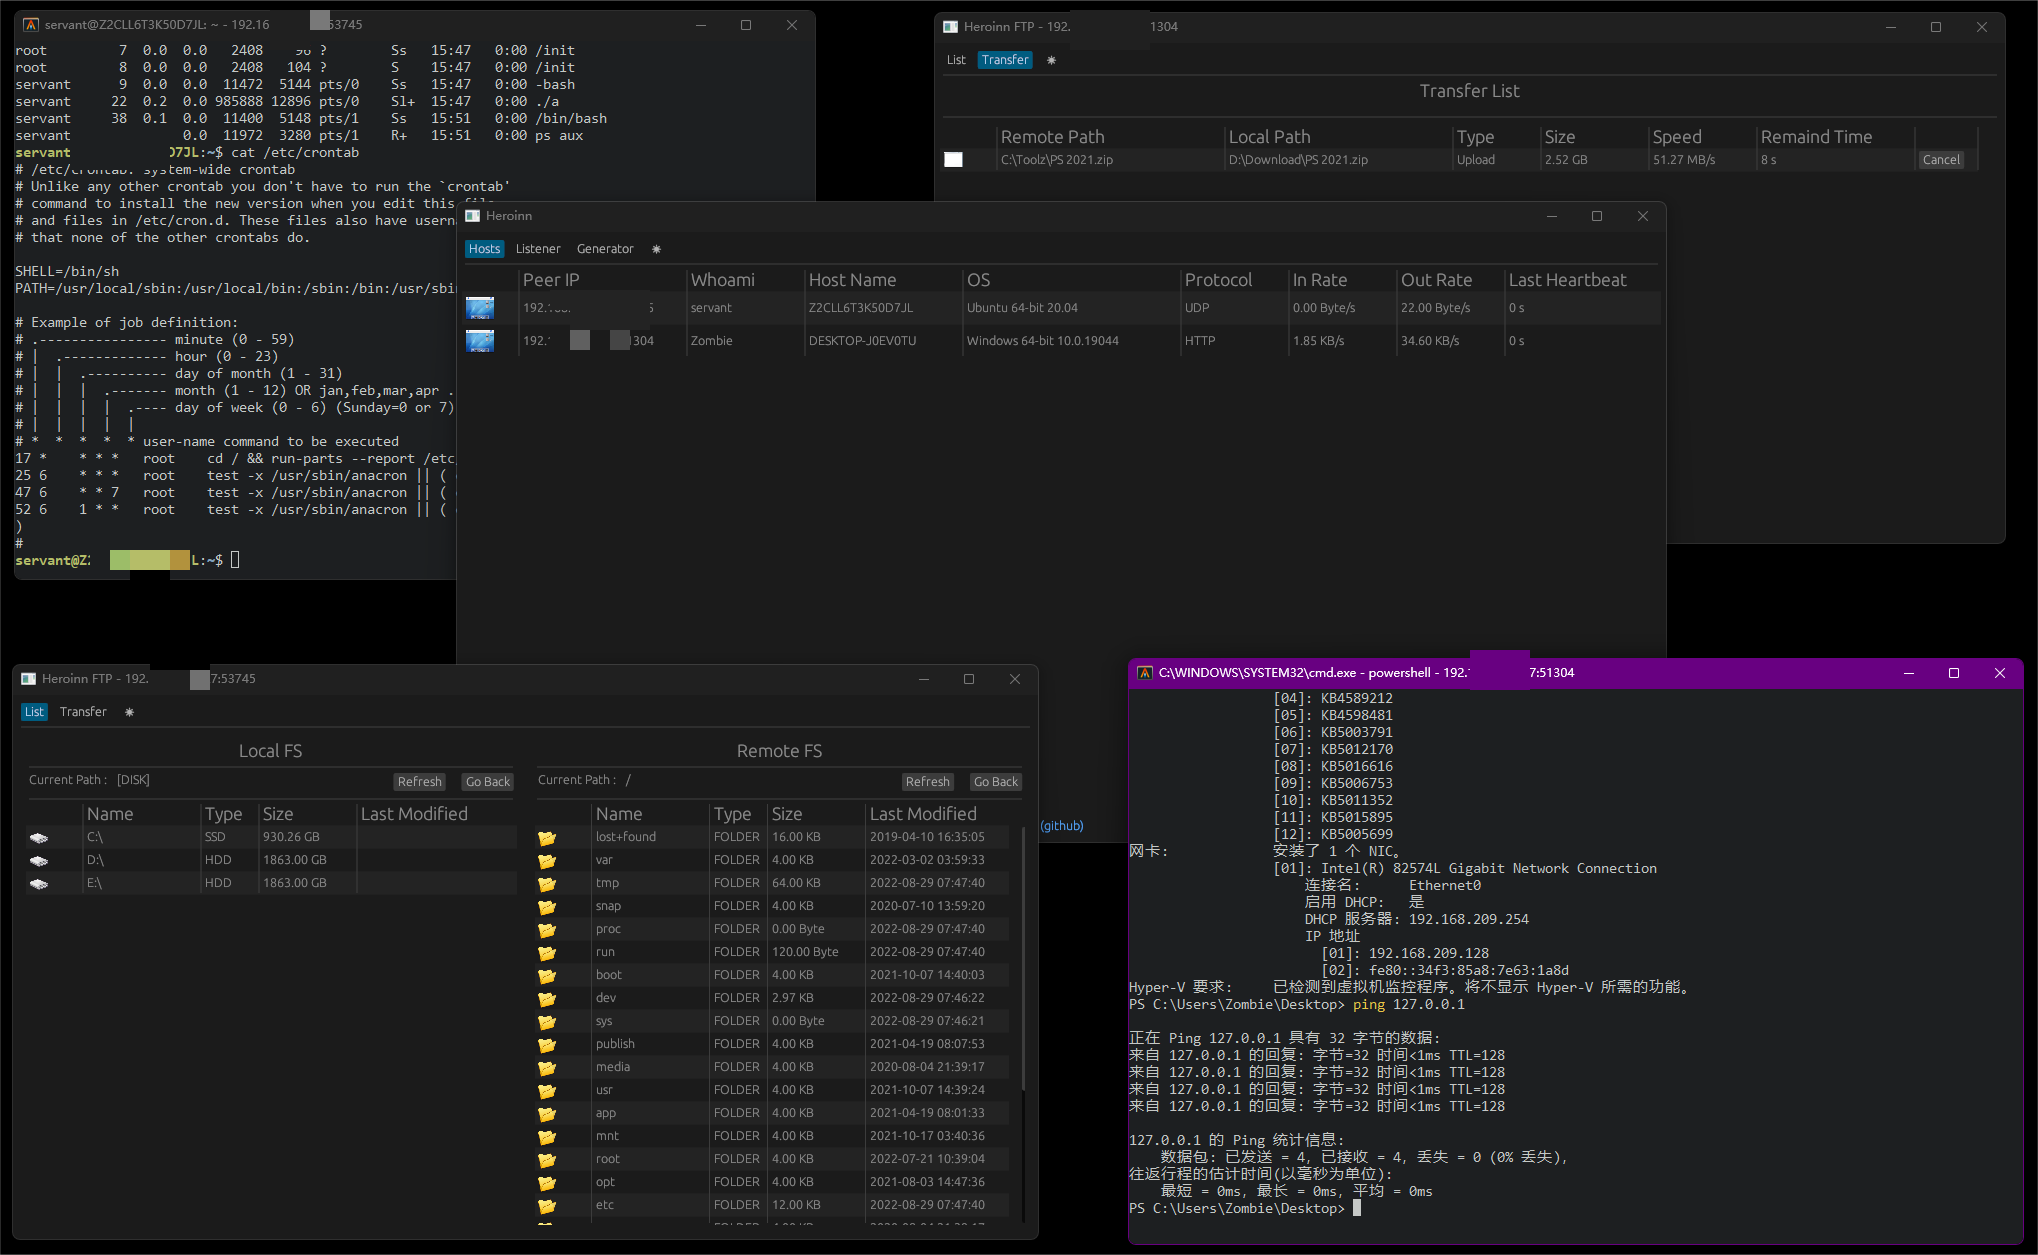 b23r0/heroinn
A cross platform C2/post-exploitation framework.
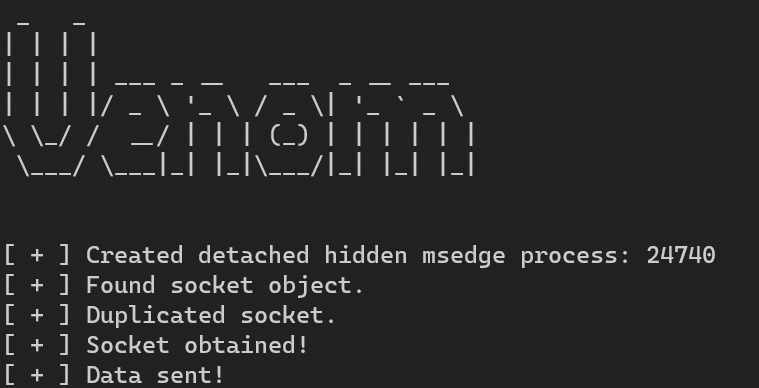 idov31/venom
Venom è una libreria pensata per eseguire comunicazioni evasive utilizzando socket di browser rubati
 tsuyoken/imgbackdoor
Nascondi il tuo payload in un file .jpg
 rvrsh3ll/rendezvousrat
RAT auto-riparante che utilizza libp2p
 demon-i386/zoshrinkc2
Malware mirato DNS over HTTPS (eseguito una sola volta)