

adit
 joda32/adit
Active Directory recon and read-only security audit over ADWS (net.tcp/9389), in Go
defensive-toolsprivilege-escalationreconnaissance+8
joda32/aditActive Directory recon and read-only security audit over ADWS (net.tcp/9389), in Go
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.

 roccoammon/active-directory-health-check
PowerShell GUI tool that runs 54 best-practice health and security checks against Active Directory, flagging Kerberoasting, DCSync, delegation and…
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of KAPE collections, one run per host, with per-host reports and a cross-host triage dashboard
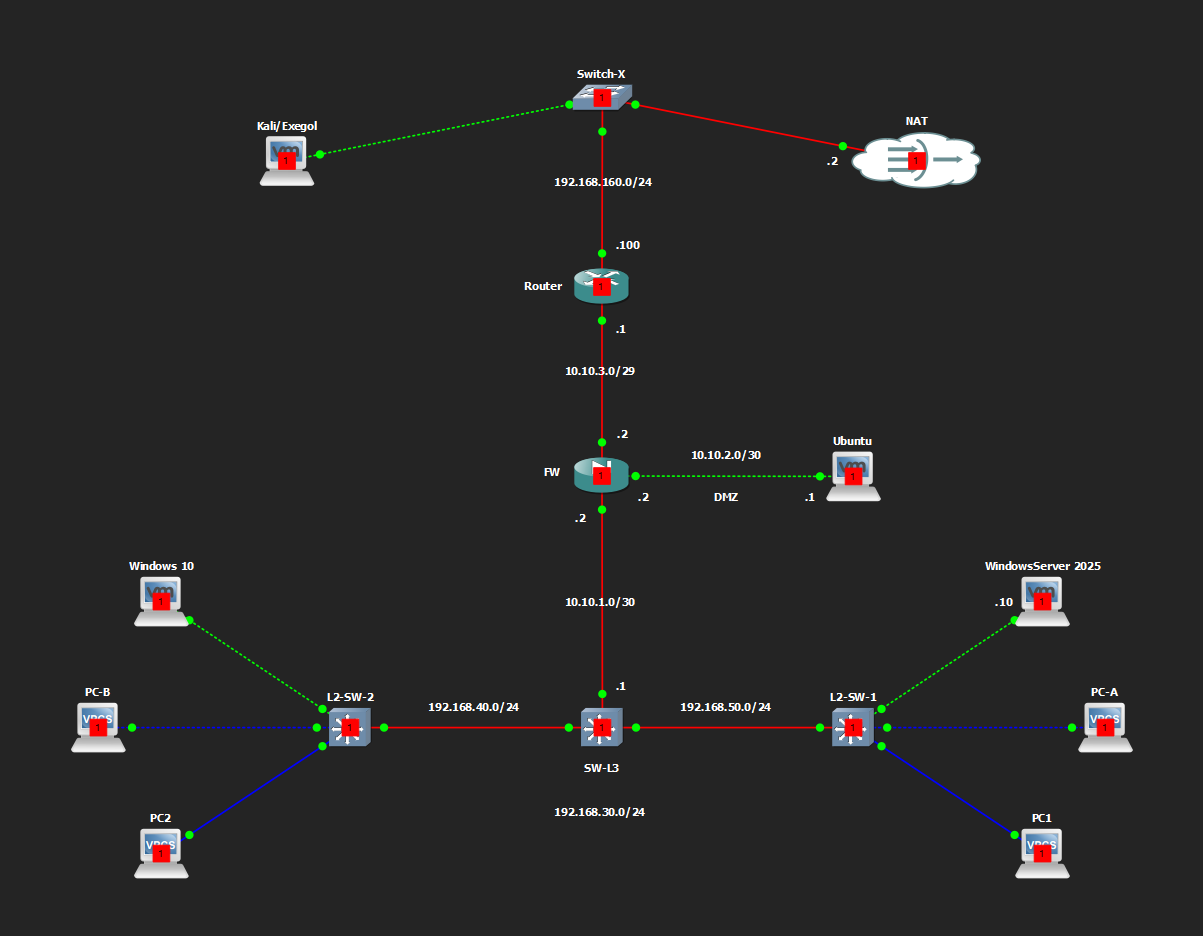 ko0ler/homelab
GNS3 home lab documenting a segmented network with Cisco ASAv firewall, L3 core, DMZ, and an Active Directory domain for practicing networking,…
 ambitsecurity/jshound
Find every API request a web app makes, from the JavaScript it ships: method, URL, body, headers and GraphQL operations. One command.
 osintversehq/otinstaller
Installs, runs, updates, and removes open-source OSINT command line tools by name, with typed inputs, JSON output, and saved results for automated…
 ripits-sec/couchpotato
Windows privilege escalation tool that patches ETW and AMSI and uses indirect syscalls to abuse SeImpersonatePrivilege, escalating service accounts…
 joda32/yowie
Finds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.
 nawaralseelawi/pvbrf-id
Simulation code and results for a private, verifiable, Byzantine-robust federated intrusion detection protocol using secret sharing, Merkle audits…
 cosmosyi/autocontrol-arena
Automated framework for frontier AI safety evaluation that synthesizes executable, pressure-rich test environments to uncover latent risks in…
 yxf203/defense-as-skill
Runtime guard skill that detects and blocks malicious skill-induced attacks in skill-augmented agents, with an MCTS loop that evolves the guard…
 yukibtc/redknife
A Swiss Army knife for offensive security.
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 perplexityai/numbat
Visibility into AI agent activity on endpoints, with on-device detection, optional pre-action blocking, and forensic reconstruction.
 gach0ng/agentstalker
End-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…
 woldann/exoproc
Cross-process instrumentation for Windows x64 in TypeScript — hook functions, redirect threads, and read/write memory in another process, with no DLL…
 hilmiazizi/oorecon
Terminal UI for attack surface discovery: DNS recon, subdomain enumeration, port scanning, reverse IP, leaked login URLs, and JavaScript secret…