
aws-firmware-dump
Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…

Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…

YellowKey BitLocker recovery audits CVE-2026-45585: yellowkey github, TPM, recovery key backup. Windows 10/11 CLI GUI, portable audit tool for…

Offset Independent Credential Extraction Tool

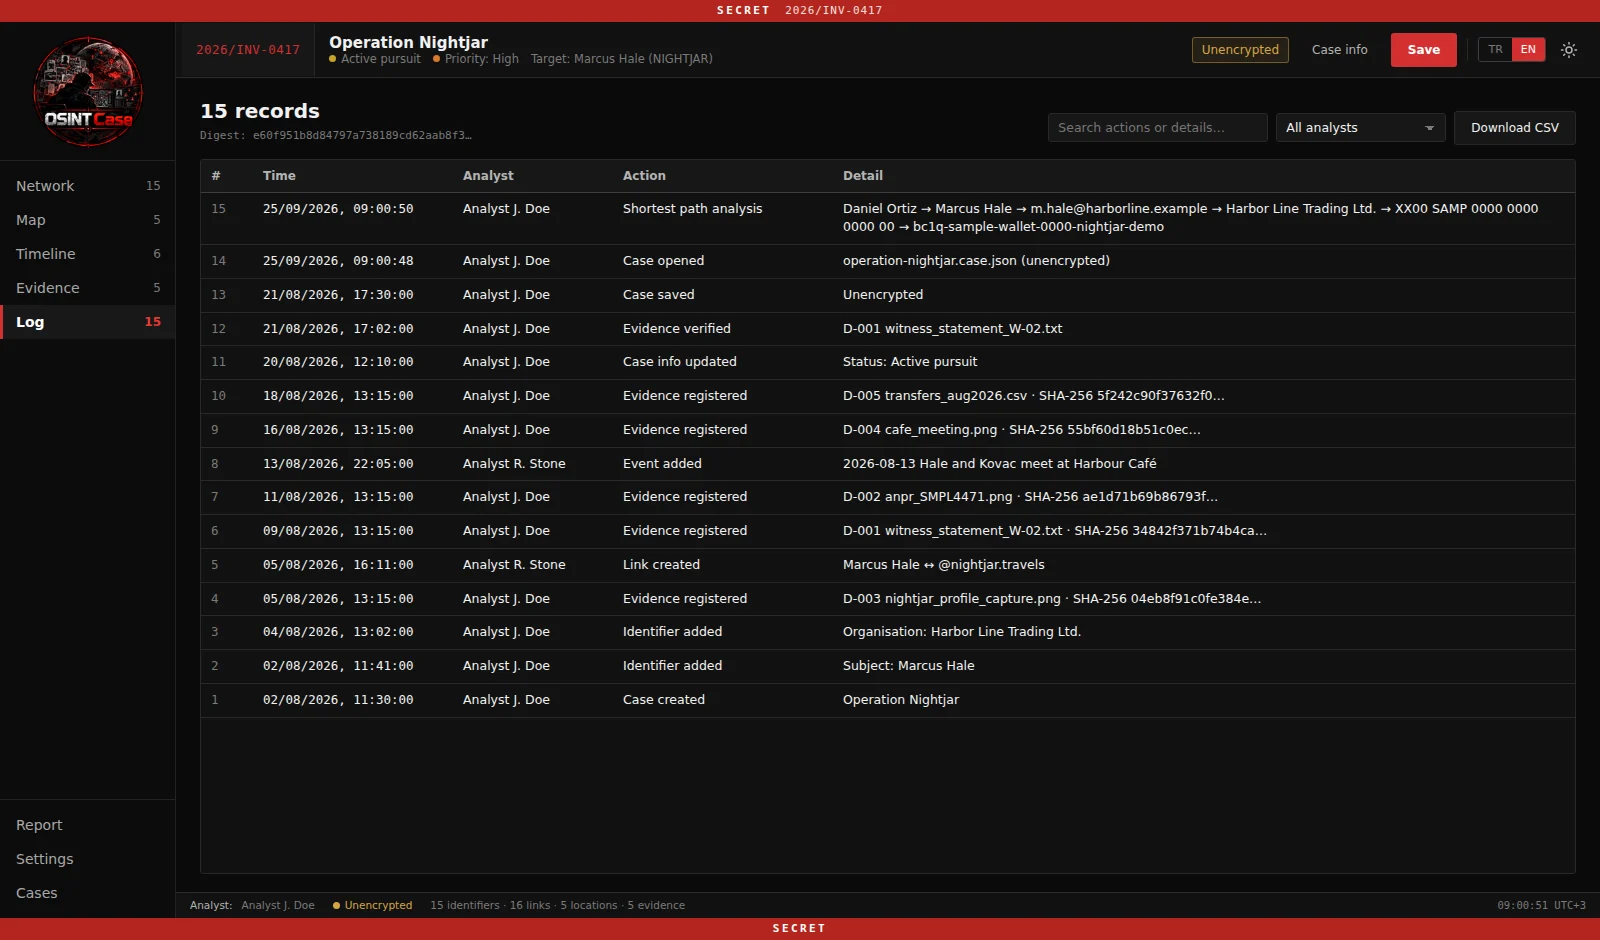
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.

Production-grade Security Baseline & Hardening Guide for Ubuntu 24.04/26.04 LTS. Kernel isolation, Emergency Panic Button, custom AppArmor/Firejail…

Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)

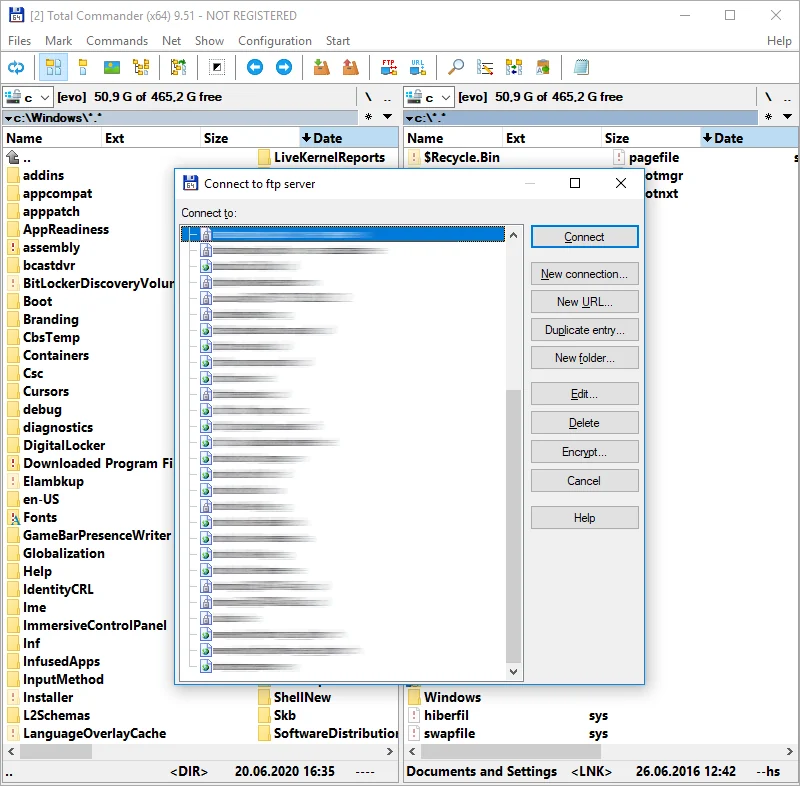
Total Commander FTP Password Recovery Tool for Python allows you to decrypt the FTP account password information for all Total Commander versions…

Manage BitLocker recovery keys, unlock encrypted drives, and monitor encryption status with this lightweight Windows utility.

Extracts cryptocurrency private keys and addresses from wallet.dat files for Bitcoin and Litecoin, enabling wallet recovery and forensic analysis.

A utility for extracting cryptocurrency wallet data from wallet.dat files.

File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…

File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…

C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…

Library and tools to access the Volume Shadow Snapshot (VSS) format

Library and tools to access the QEMU Copy-On-Write (QCOW) image format

Library and tools to access the Virtual Hard Disk (VHD) image format

Library and tools to access the VMware Virtual Disk (VMDK) format

Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…