
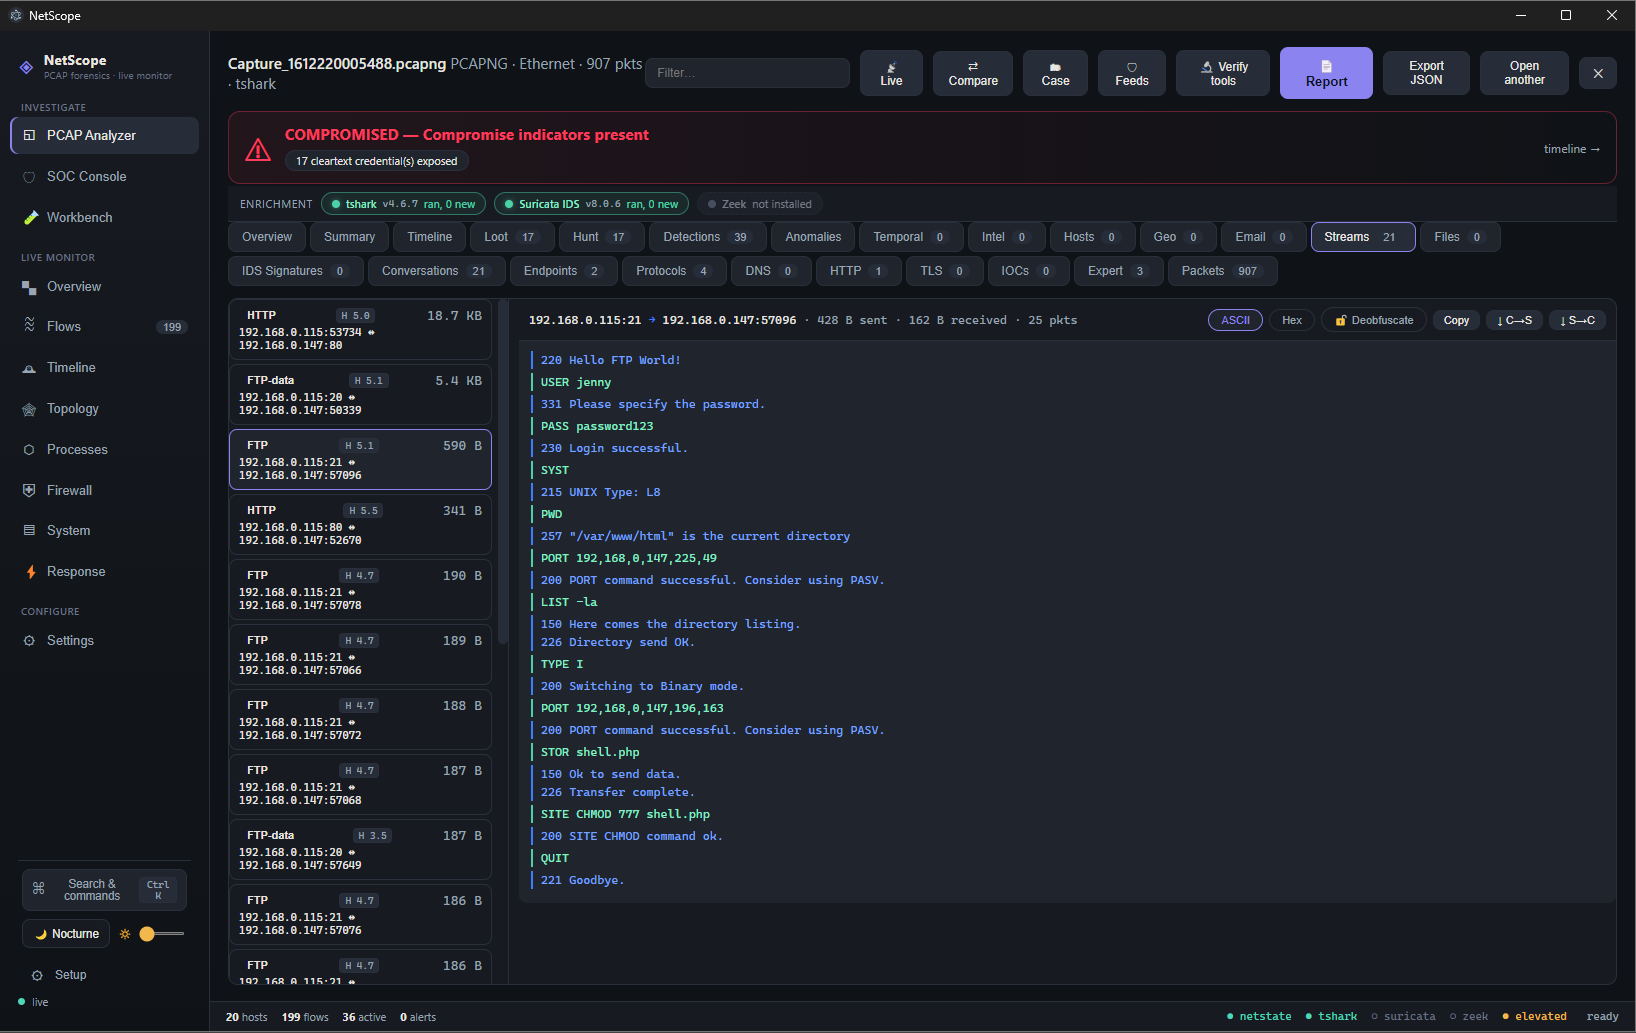
NetScope
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
ioc-managementpacket-sniffing-analysisnetwork-forensics+5
2
spectralzero/netscopeOffline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
 doctoreww/evilfonttool
A font-based deception tool for red teaming, security research, and whatever else.
 sneakynachos/cve-2026-2766-but-with-wasm
CVE-2026-2766, but with wasm
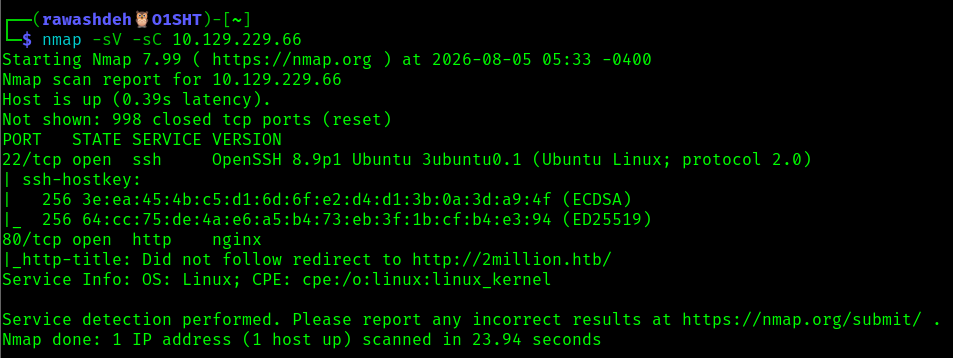 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 huzjie/aegisagent
Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…
 lazybear8372/cve-2023-31014_lab
Educational Android lab for CVE-2023-31014 implicit intent hijacking
 xiaoqimikko/bc-check
Offline scanner telling you which of the 2026 Bouncy Castle CVEs actually apply to you - across BC, BC-LTS and BC-FJA (FIPS), which do not share a…
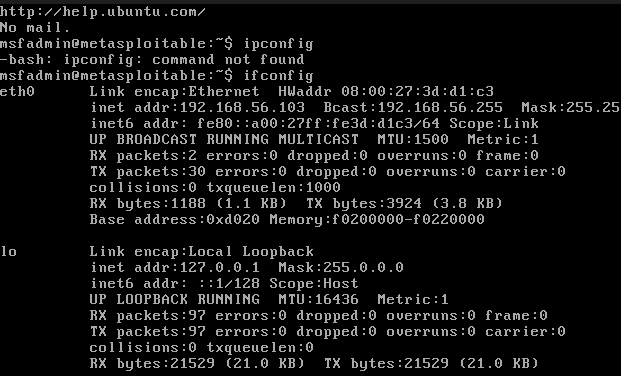 alexojocyber/cve-2011-2523-vsftpd-validation-lab
Authorized Kali–Metasploitable2 lab using Python and Nmap NSE to validate CVE-2011-2523 in vsFTPd 2.3.4.
 sneakynachos/cve-2024-29943-but-with-wasm
CVE-2024-29943, but with wasm
 digicred-oss/caos-os
Customer Assurance Operating System. Answer the security questionnaires your customers send you, once.
 kalilinux/recipes/kali-preseed-examples
Preseed configuration examples and guides for automated, hands-off Kali Linux installation, including partitioning, package selection, and boot…
 kalilinux/build-scripts/kali-packer
Create and configure lightweight, reproducible, and portable development environments Kali's HashiCorp Packer configurations to create Kali…
 nichetoolkit/spring-retry-toolkit
spring retry 1.3.x fix with niche toolkit for CVE-2026-41710
 kalilinux/build-scripts/kali-vm
Kali Linux VM images build script
 borealisai/stepjack
Benchmarking framework for evaluating computer-use AI agents against multi-step indirect prompt injection, with automatic adversarial goal…
 yingtaoren/d-scan
Analyzes LLM internal states and 100+ attention/probability features to train classifiers that detect document poisoning attacks in RAG systems.
 nu11secur1ty/0
Exploit for a Windows Defender race condition that escalates to SYSTEM via use-after-free, crashes MsMpEng.exe, spawns a hidden shell, and persists…