

hermit
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
android-securitystatic-analysisios-security+7
4
xv4l3x/hermitInspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 githubsecuritylab/seclab-taskflows
Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…
 blacktop/ipsw-diffs
Publishes per-build diffs of iOS, iPadOS, and macOS IPSW firmware releases, enabling binary-level comparison of system components across versions and…
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
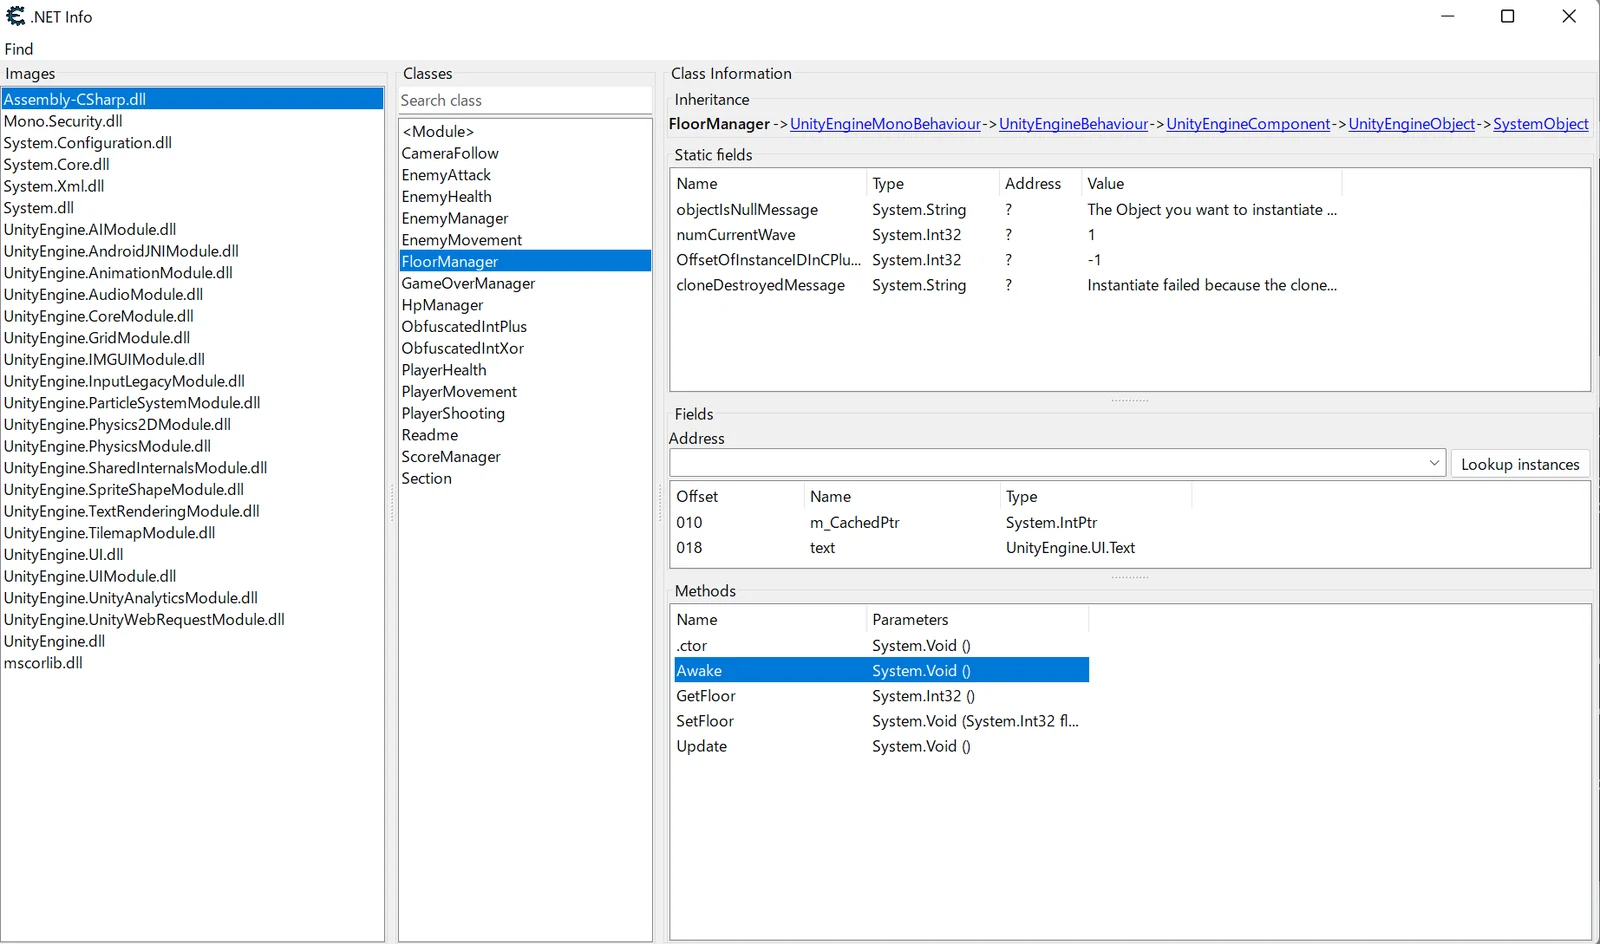 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 gmh5225/frida-vmprotect-bypass
Frida script that bypasses VMProtect runtime protections on mobile platforms, enabling dynamic instrumentation and analysis of protected binaries.
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
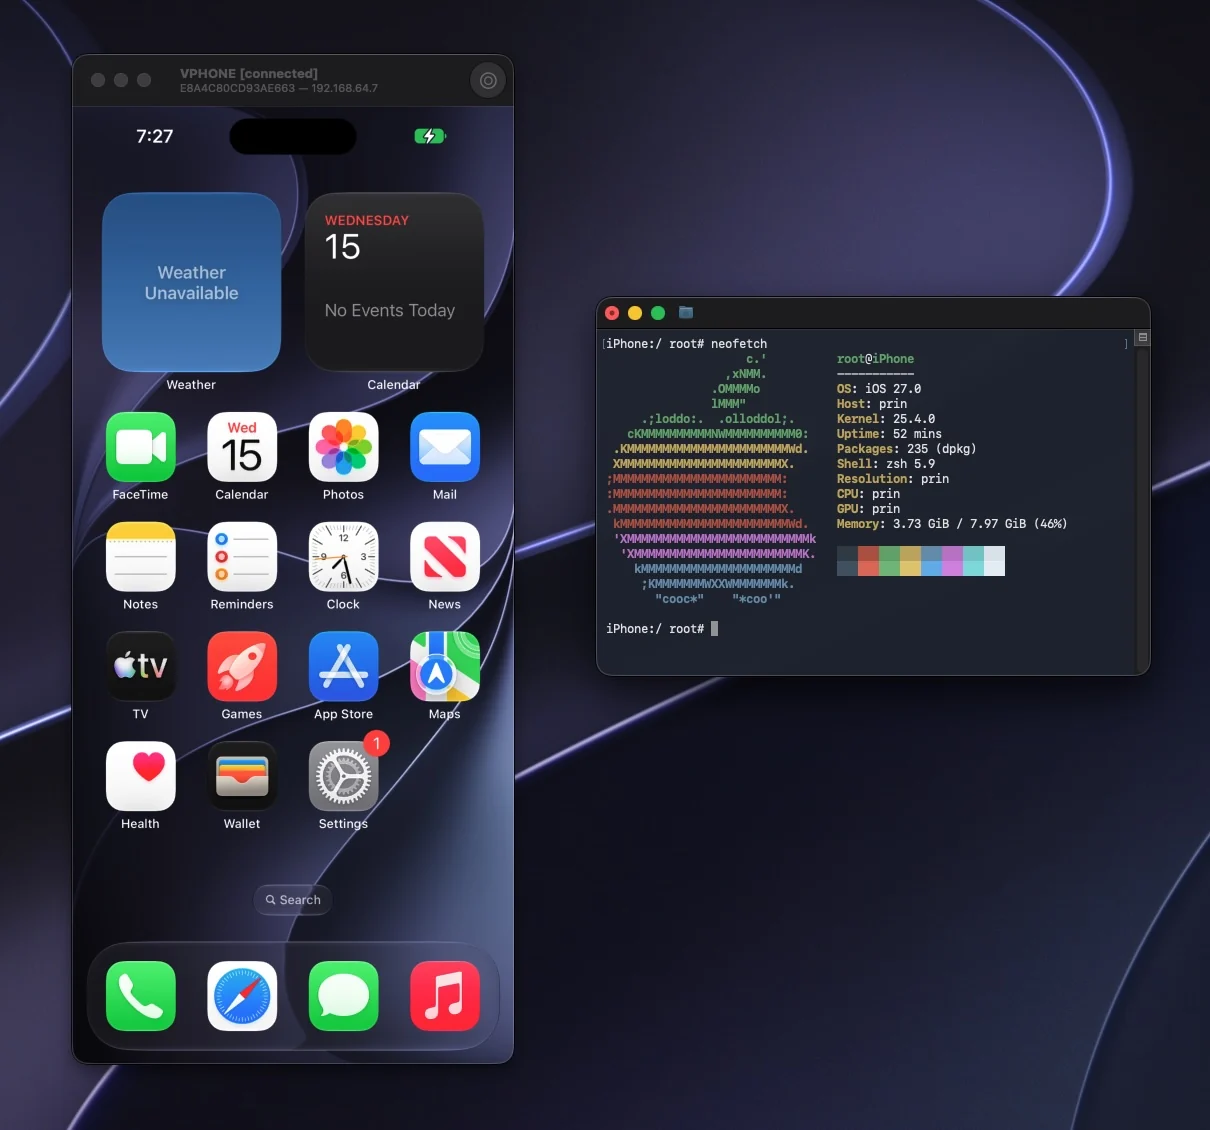 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
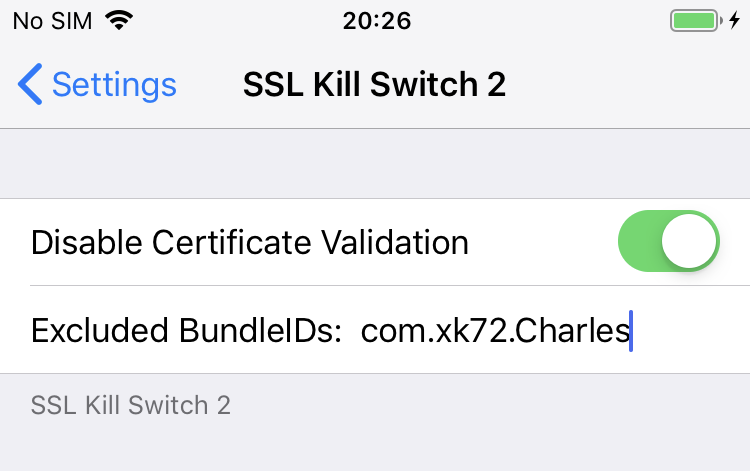 nabla-c0d3/ssl-kill-switch2
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…
 nygard/class-dump
Generate Objective-C headers from Mach-O files.
 jwalker/frida-ios-dump-modern
An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs
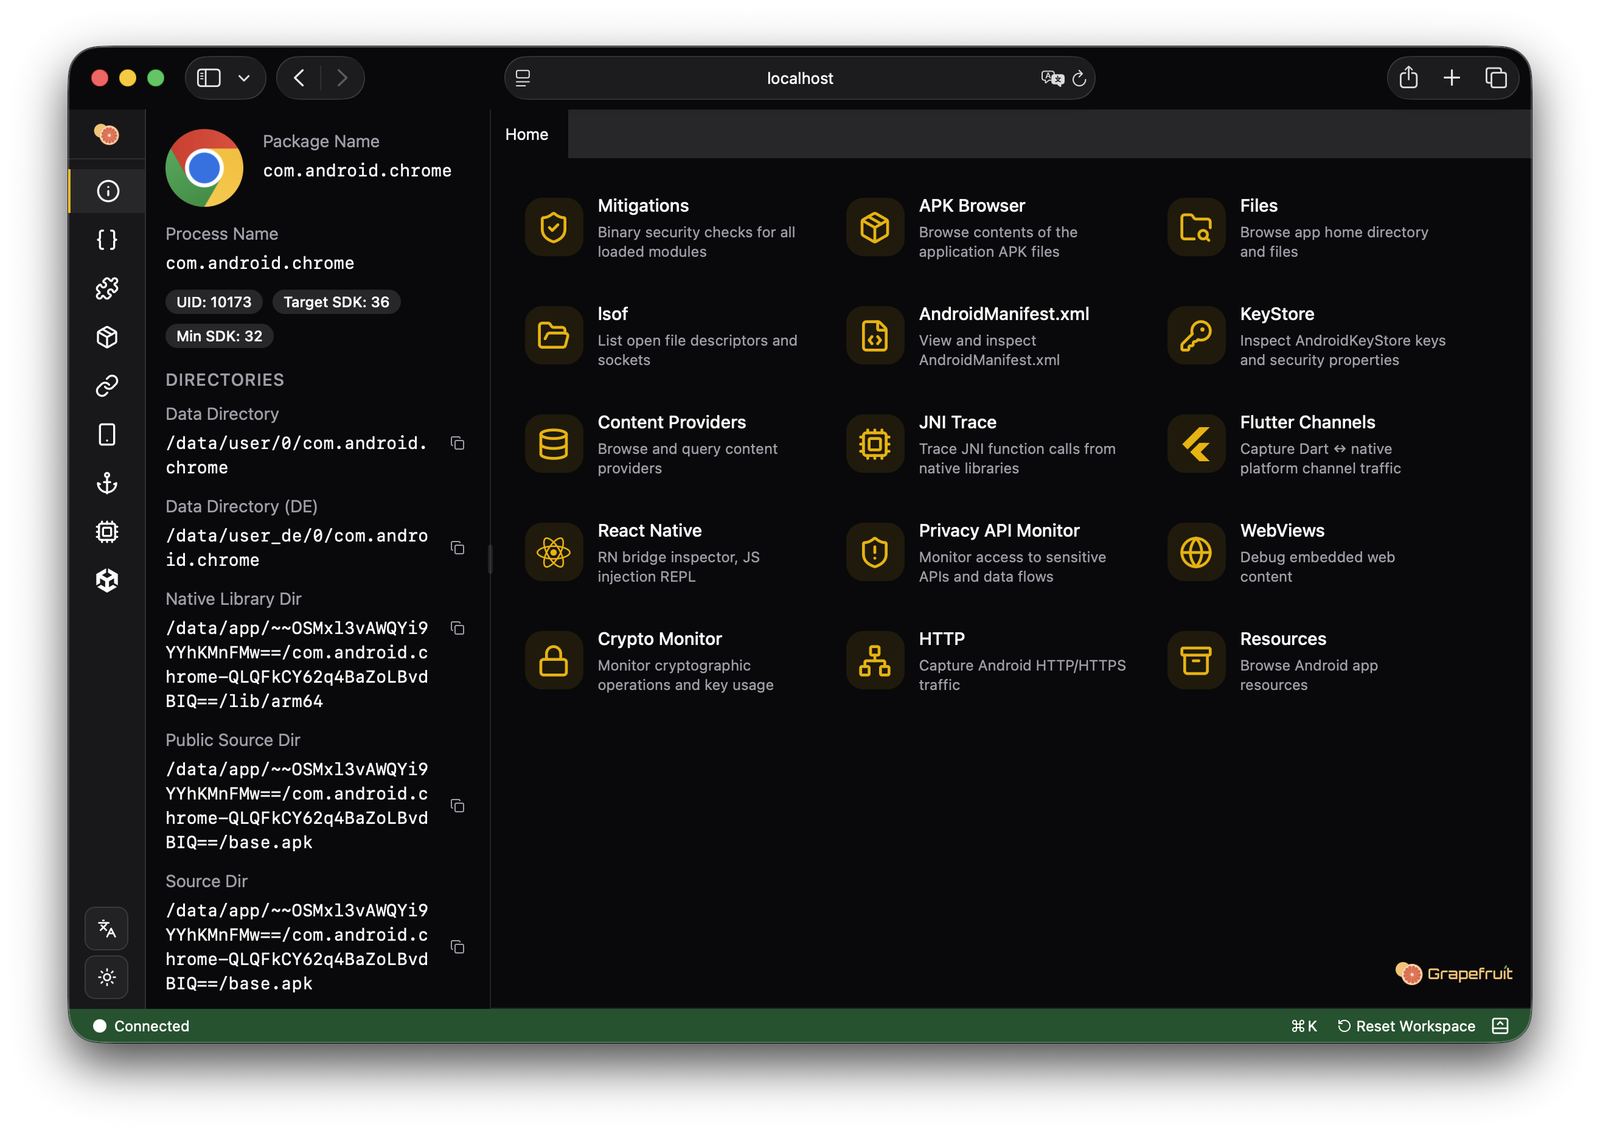 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…