

MemTools
 gmh5225/memtools
Windows Linux DMA、Dump 、Direct、inject 内存读取、写入工具
dynamic-analysis-sandboxingmemory-forensicsreverse-engineering+5
52 years ago
gmh5225/memtoolsWindows Linux DMA、Dump 、Direct、inject 内存读取、写入工具
 greatscottgadgets/facedancer
Implement your own USB device in Python, supported by a hardware peripheral such as Cynthion or GreatFET
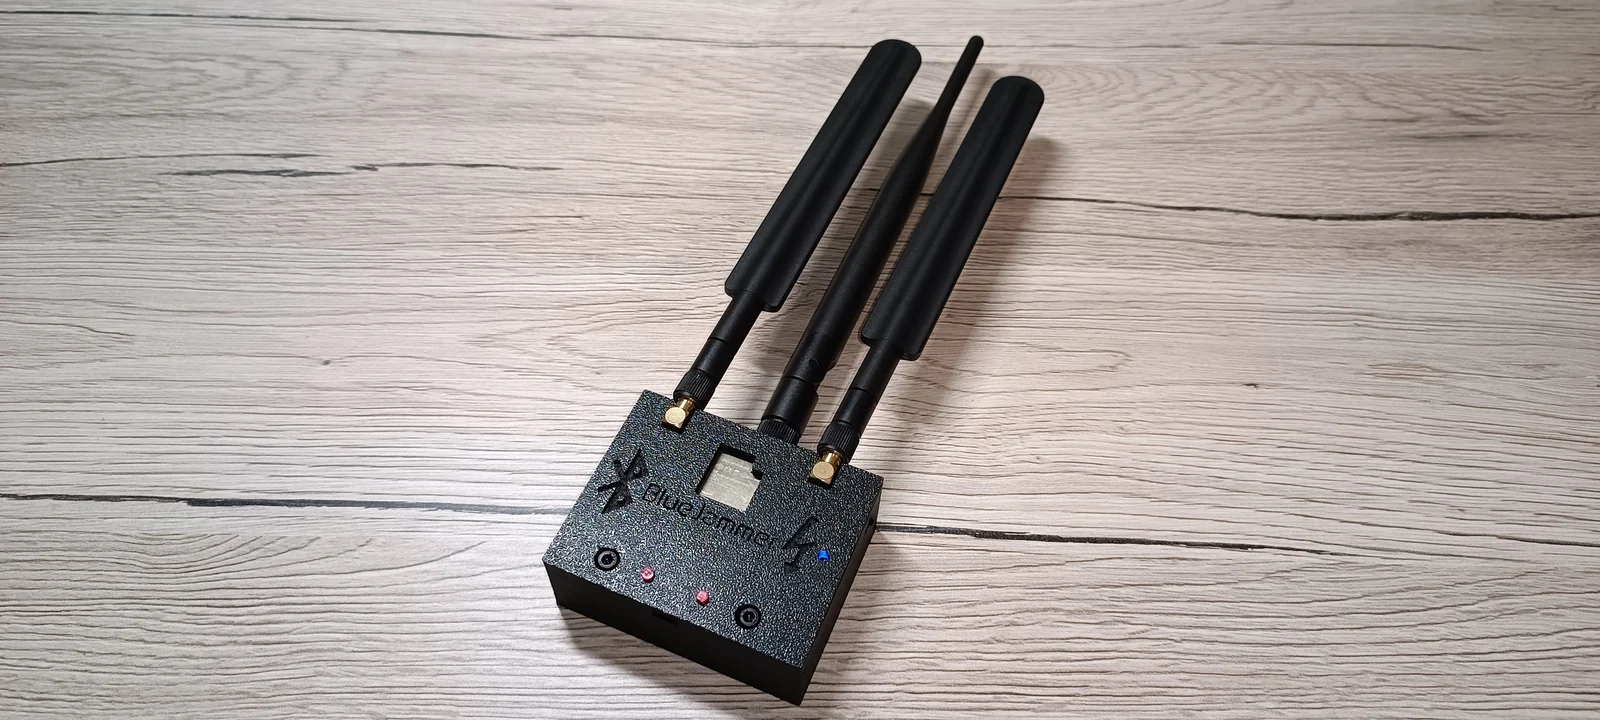 emenstanougat/esp32-bluejammer
ESP32 and nRF24 based 2.4GHz jammer that disrupts Bluetooth, BLE, WiFi, and RC channels via noise and packet flooding for controlled security testing.
 tandasat/hello-vt-rp
A simple hypervisor demonstrating the use of the Intel VT-rp (redirect protection) technology.
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 wrongbaud/spidump
Tool for reconstructing SPI flash images via logic analyzer captures
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
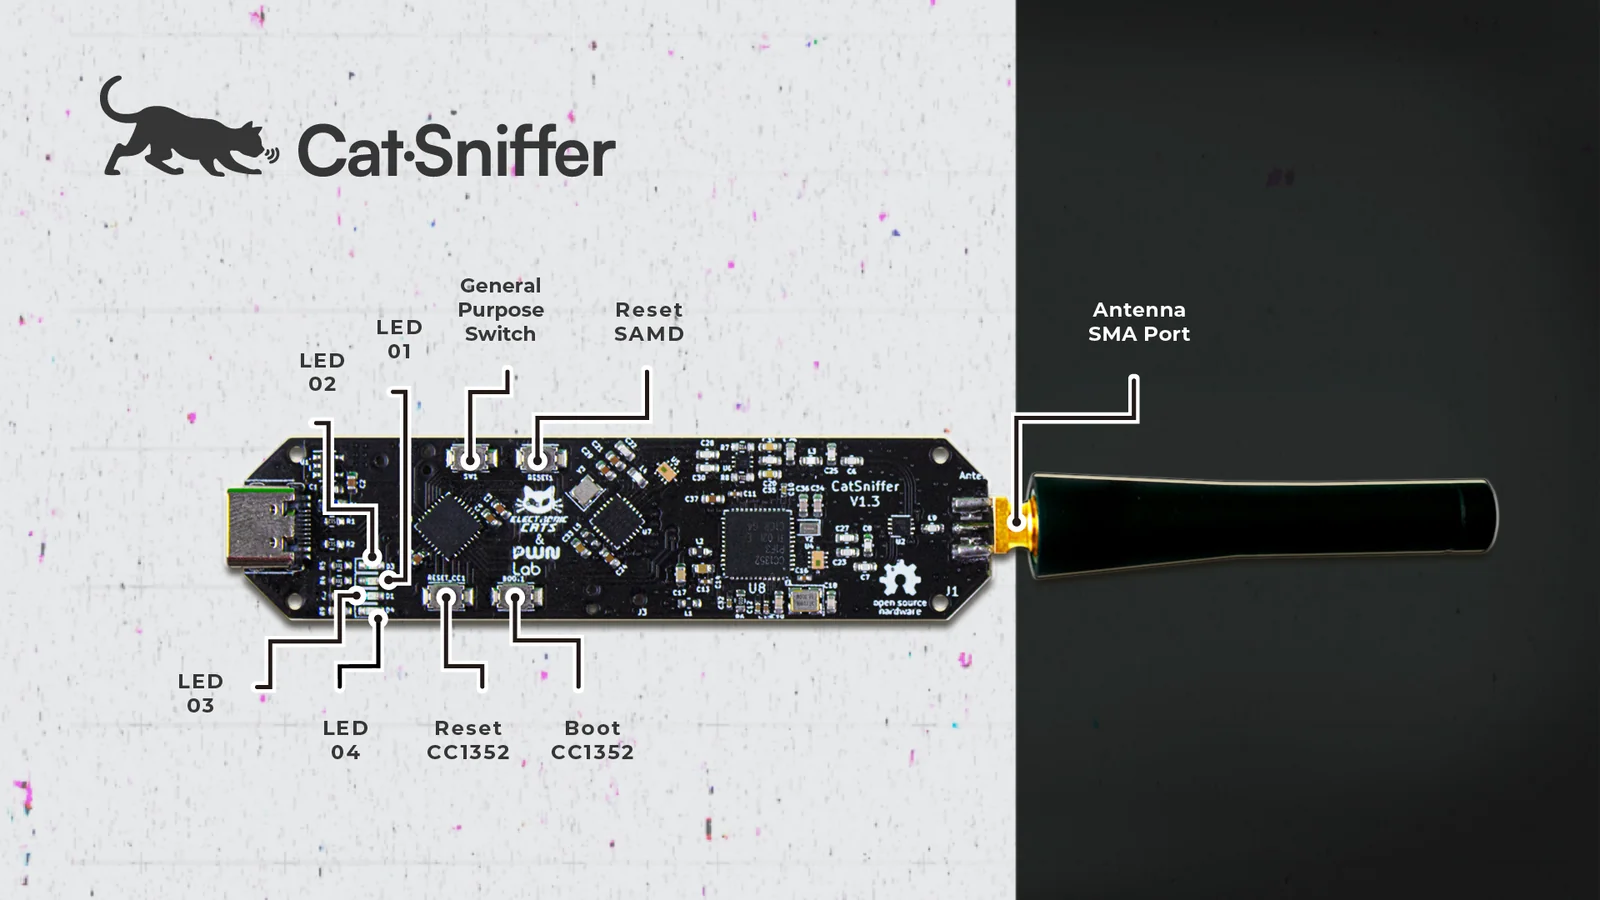 electroniccats/catsniffer-firmware
Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…
 teutekeune/ibssloader
Research tooling to boot Linux on iPad mini 1 via checkm8, patched iBSS/iBEC, and custom bare-metal payloads, including device tree port, kernel…
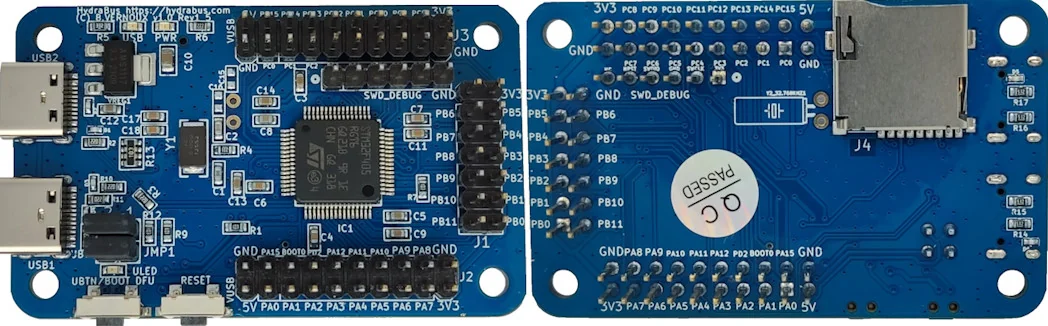 hydrabus/hydrafw
Open-source firmware for HydraBus, a multi-tool for embedded hardware debugging, hacking, and penetration testing, supporting protocols like SPI,…
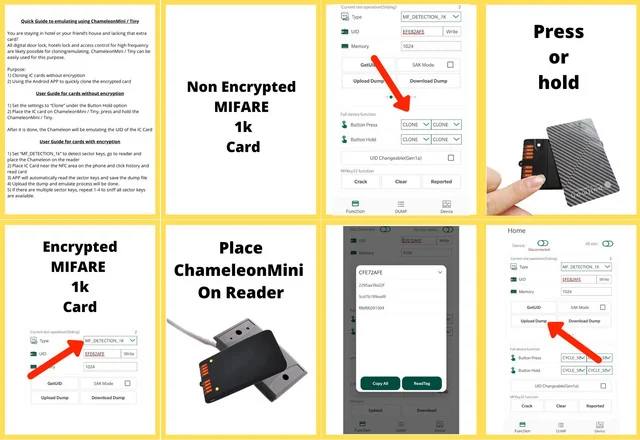 rfidresearchgroup/chameleonmini
Portable NFC/RFID security tool for emulating and cloning contactless smartcards, reading tags, sniffing RF traffic, and recovering Mifare access…
 nfc-tools/milazycracker
Mifare Classic Plus - Hardnested Attack Implementation for SCL3711 LibNFC USB reader
 adamlaurie/rfidiot
Python library and tools for exploring RFID/NFC tags and readers: read, write, clone, and analyze supported ACG serial hardware for research and…
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
 dangerousprototypes/bus_pirate
Universal bus interface for hardware hacking and debugging, supporting I2C, SPI, JTAG, UART, and 1-Wire for sniffing, programming, and protocol…
 nfc-tools/libnfc
Platform independent Near Field Communication (NFC) library
 nfc-tools/mfoc
Offline nested attack tool that recovers MIFARE Classic authentication keys using known default or user-supplied keys for assessing NFC/RFID card…
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.