

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Binary Exploitation — Tools | Kitploit

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
415 results
DebuggerJ- preview

DebuggerJ-

GitHubjaime64net/debuggerj-

Debugger de aplicaciones x86 y x64 con intgracion de AI

defensive-toolsstatic-analysisdynamic-analysis-sandboxing+7
1 day ago
secbox preview

secbox

GitHubyv1ing/secbox

Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.

network-mappingvulnerability-analysismobile-app-pentesting+9
4 days ago
exoproc preview

exoproc

GitHubwoldann/exoproc

Cross-process instrumentation for Windows x64 in TypeScript — hook functions, redirect threads, and read/write memory in another process, with no DLL…

dynamic-analysis-sandboxingmemory-forensicsreverse-engineering+8
45 days ago
NTDLL-reconstruction preview

NTDLL-reconstruction

GitHubsk4r4b/ntdll-reconstruction

A technique that mixes NTDLL unhooking and hellsgate gate varients

defensive-toolsids-ips-evasionreverse-engineering+6
138 days ago
AetherVM preview

AetherVM

GitHubaethervm/aethervm

LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…

static-analysisdynamic-analysis-sandboxingvulnerability-analysis+8
159 days ago
lithium-kernel preview

lithium-kernel

GitHubgmh5225/lithium-kernel

Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…

memory-forensicsreverse-engineeringanti-bot+1
2 months ago
vmp-lazy-unpack preview

vmp-lazy-unpack

GitHubx86rc/vmp-lazy-unpack

Emulation-based unpacker and import resolver for Windows x86/x64 VMProtect 3.x binaries, using Unicorn to emulate syscalls and rebuild the IAT…

static-analysisdynamic-analysis-sandboxingreverse-engineering+4
4002 days ago
Pentest-Windows preview

Pentest-Windows

GitHubitm4n/pentest-windows

Collection of Windows internals research and exploitation techniques covering privilege escalation, token abuse, and post-exploitation tricks for red…

privilege-escalationexploitationreverse-engineering+6
1321 month ago
kernel-research preview

kernel-research

GitHubgoogle/kernel-research

Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
exploit-frameworksvulnerability-analysisreverse-engineering+6
966 months ago
striga preview

striga

GitHubllvmparty/striga

Experimental x86-64 to LLVM IR lifter in Python that translates machine code into analyzable IR for reverse engineering, optimization, and VM handler…
static-analysiscode-analysisreverse-engineering+4
1213 months ago
amd_hypervisor preview

amd_hypervisor

GitHubnot-matthias/amd_hypervisor

Rust AMD SVM hypervisor framework with customizable vmexit handlers (MSR, CPUID, RDTSC) and NPT hooking for kernel-level monitoring and research.
defensive-toolsreverse-engineeringsecurity-virtualization+3
1753 years ago
AntiOreans-CodeDevirtualizer preview

AntiOreans-CodeDevirtualizer

GitHub67-6f-64/antioreans-codedevirtualizer

IDA 6.8 plugin that devirtualizes Themida's FISH virtual machine (2.2.5.0-2.2.7.0), restoring native code from protected binaries for reverse…
static-analysiscode-analysisreverse-engineering+5
813 years ago
SandboxBootkit preview

SandboxBootkit

GitHubthesecretclub/sandboxbootkit

Bootkit for Windows Sandbox to disable DSE/PatchGuard.

defensive-toolsprivilege-escalationpersistence-mechanisms+5
3472 years ago
GateX preview

GateX

GitHubabraxas/gatex

FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
password-crackingstatic-analysisdynamic-analysis-sandboxing+8
111 days ago
kernel-CTF preview

kernel-CTF

GitHubgmh5225/kernel-ctf

Collection of Linux kernel exploitation CTF challenges covering buffer overflow, use-after-free, and race condition vulnerabilities for hands-on…

vulnerability-analysisexploitationreverse-engineering+5
1 year ago
KDU preview

KDU

GitHubhfiref0x/kdu

Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
defensive-toolsprivilege-escalationpersistence-mechanisms+8
2.8k19 days ago
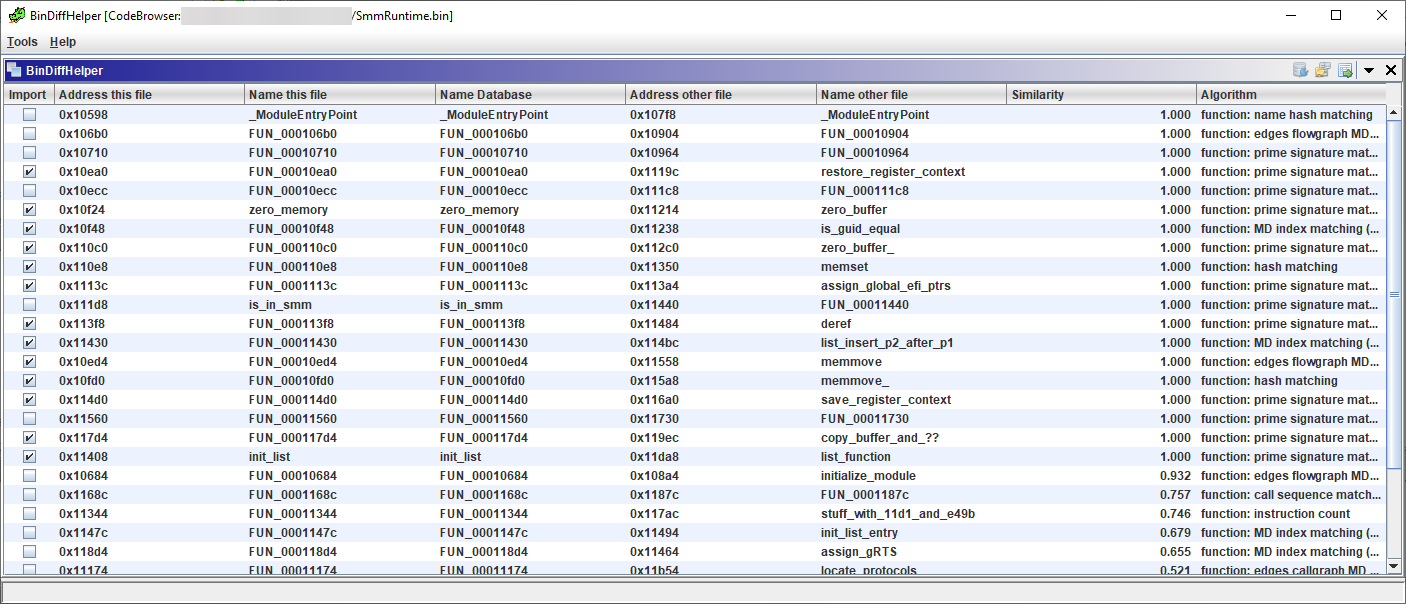
BinDiffHelper preview

BinDiffHelper

GitHububfx/bindiffhelper

Ghidra Extension to integrate BinDiff for function matching
static-analysiscode-analysisreverse-engineering+4
2971 month ago
KeyPatchX preview

KeyPatchX

GitHubgmh5225/keypatchx

KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…

static-analysisexploitationreverse-engineering+4
97 months ago
Previous12…24Next