
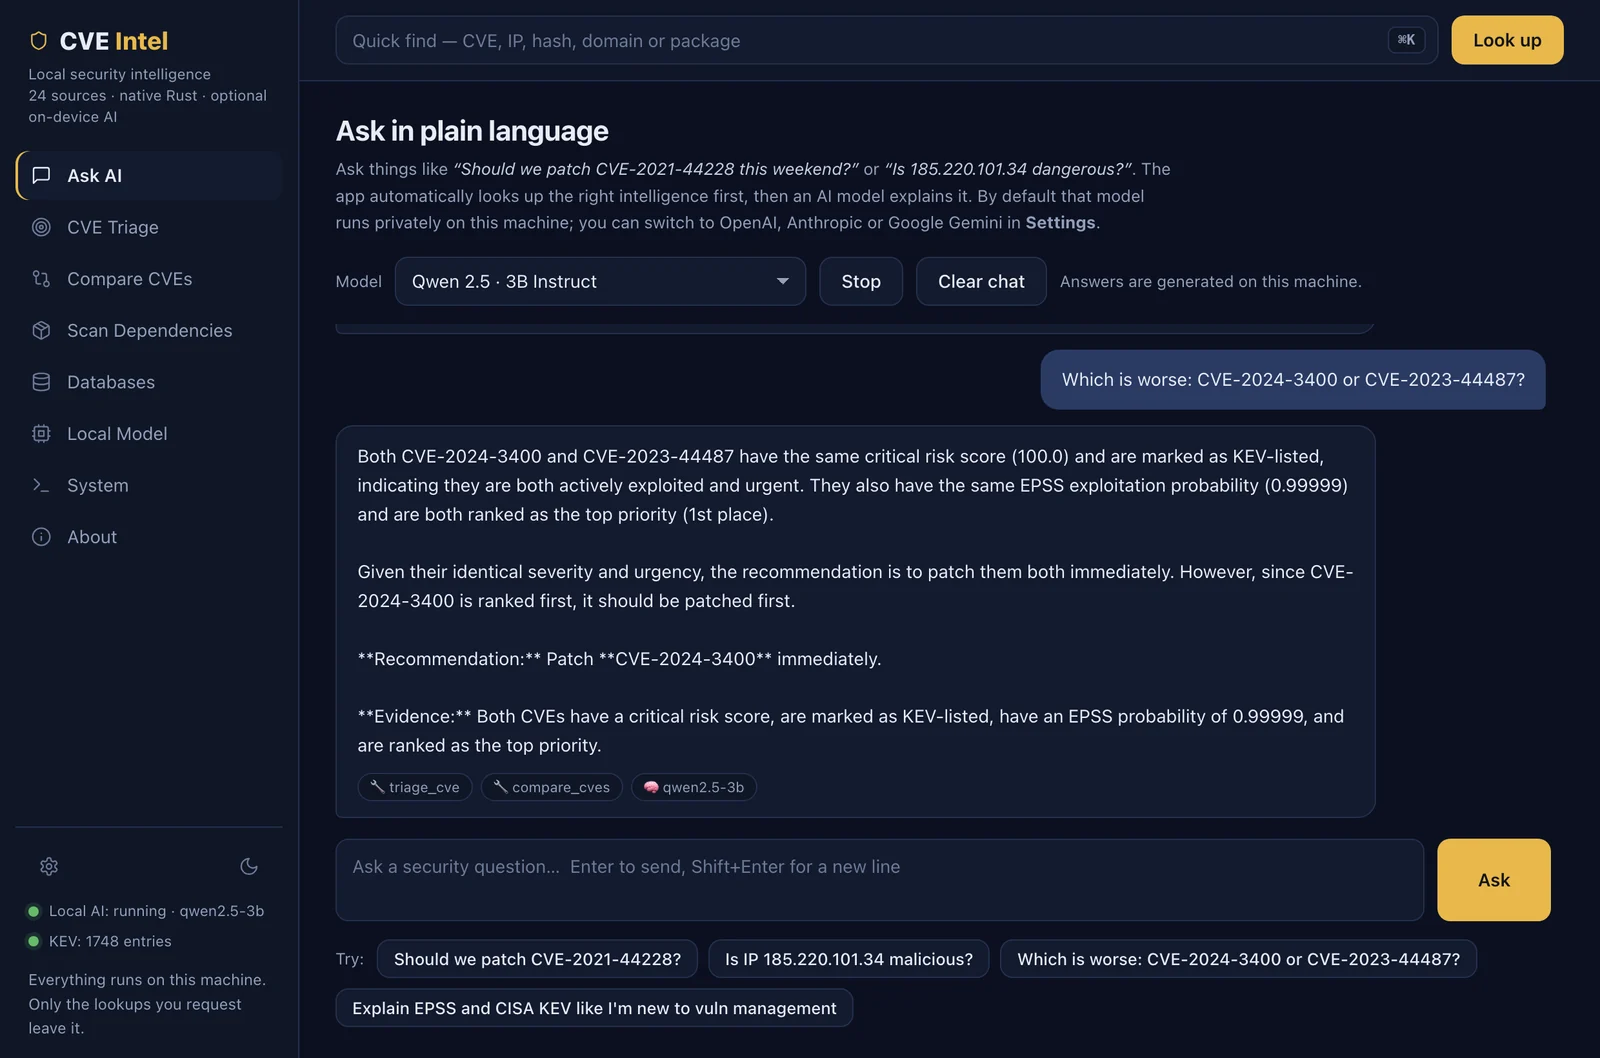
cve-intel
 fazmin/cve-intel
Local security intelligence for CVE triage — 31 tools, 25 sources, risk scores and an MCP server for AI agents, all in native Rust. Private by…
ioc-managementosintvulnerability-scanners+8
5
fazmin/cve-intelLocal security intelligence for CVE triage — 31 tools, 25 sources, risk scores and an MCP server for AI agents, all in native Rust. Private by…
 gmh5225/minidumpreader
Parses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…
 lascc/dfirhub
Search artifact paths, build collection scripts, and convert Sigma rules. All in one place.
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 szzxli/soc-home-lab
Hands-on cybersecurity lab: mini-SOC on AWS, CloudTrail IOC analyzer, phishing analysis lab, ELF binary triage, SOC agent skills
 mceeomoba/apex-kev-change-desk
Offline CISA KEV snapshot comparison for field-level change review. Free prototype, not a security assessment. AI-assisted development.
 gmh5225/maldec-edr
Unix endpoint detection and response solution using kernel-level mechanisms to detect anomalies and malware attacks in real time.
 gmh5225/malwaredb
Curated collection of 961 malware families (1.36 GB) in password-protected ZIP archives, organized by family and type for analysis and research.
 roccoammon/active-directory-health-check
PowerShell GUI tool that runs 54 best-practice health and security checks against Active Directory, flagging Kerberoasting, DCSync, delegation and…
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of KAPE collections, one run per host, with per-host reports and a cross-host triage dashboard
 perplexityai/numbat
Visibility into AI agent activity on endpoints, with on-device detection, optional pre-action blocking, and forensic reconstruction.
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 swastiksagar/wazuhlabproject
Hands-on Wazuh SIEM/XDR home lab covering OVA deployment, agent enrollment, file integrity monitoring, VirusTotal malware detection, and MITRE ATT&CK…
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 dwexi/entropystrip
Algorithmic PE de-obfuscator, Shannon entropy radar, and incident triage engine
 rdelasierra-uy/portfolio
Vitrina profesional: writeups de Hack The Box, informes, casos de estudio GRC (ISO 27001/27002/27005/27035, ISO 31000 + MAGERIT), scripts de…
 gilnett/wstrace
Standalone zero-driver Windows system and API monitor in Rust
 mafifrizi/tanuki
Tactical Identity Operator for Linux & Hybrid Active Directory