

confirmesc
 capture0x/confirmesc
Linux privesc enumerator that confirms exploitability and gives you the exact root shell command - no GTFOBins searching. MCP server + AI-agent…
privilege-escalationvulnerability-scannersexploitation+7
1
capture0x/confirmescLinux privesc enumerator that confirms exploitability and gives you the exact root shell command - no GTFOBins searching. MCP server + AI-agent…
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.

 rdelasierra-uy/rag-seguridad
CyberRAG — RAG 100% local (Ollama) sobre apuntes y libros de ciberseguridad: recuperación híbrida, respuestas con citas, asistente de pentest por…
 rdelasierra-uy/portfolio
Vitrina profesional: writeups de Hack The Box, informes, casos de estudio GRC (ISO 27001/27002/27005/27035, ISO 31000 + MAGERIT), scripts de…
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
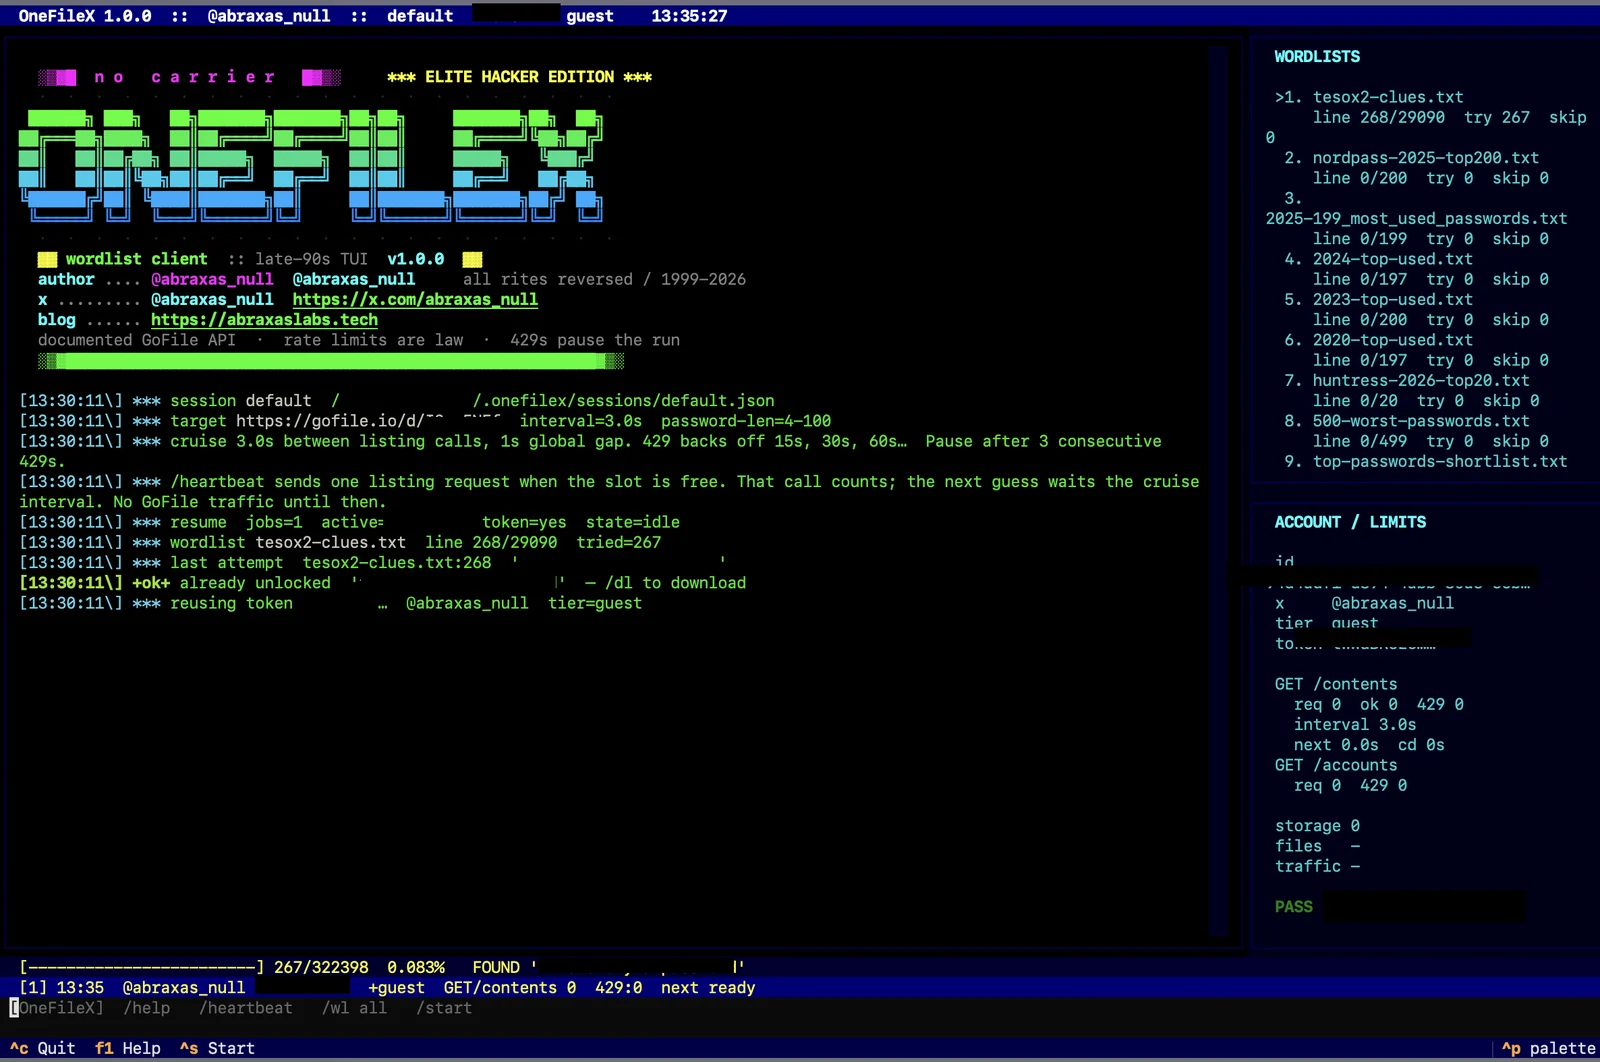 abraxas/gofilex
Wordlist Bruteforcer for GoFile (gofile.io) Download Passwords
 gmh5225/kernel-ctf
Collection of Linux kernel exploitation CTF challenges covering buffer overflow, use-after-free, and race condition vulnerabilities for hands-on…
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 mister-iks/pcybox-attackgraph
Open source browser lab to build a simulated infrastructure, watch an attack move through it, and check whether your defense works.
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
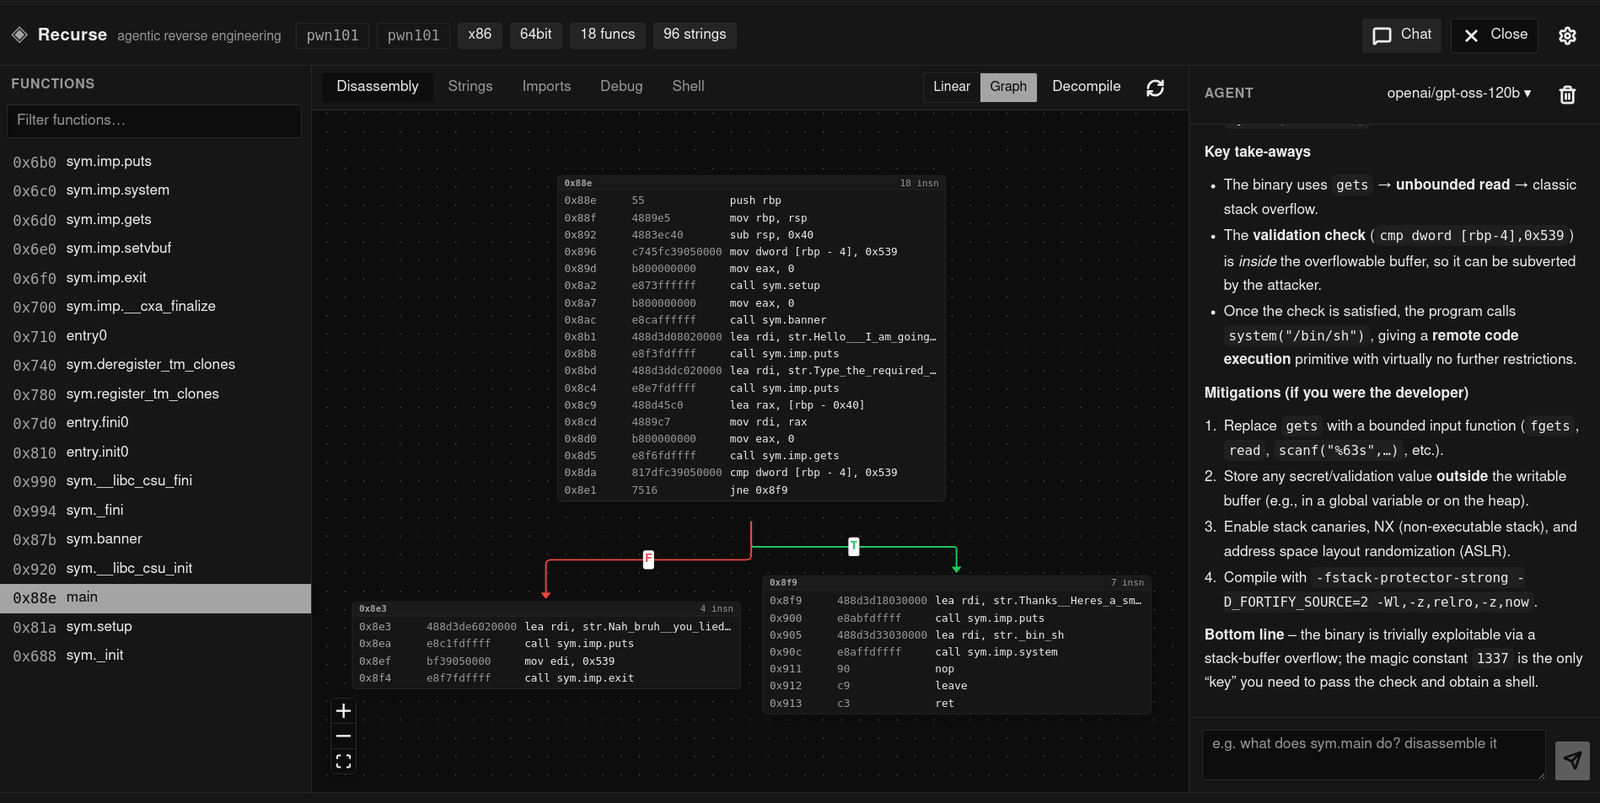 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 s1n6h/pentest-harness
Self-hosted AI agent harness for authorized pentests, bug bounty, security labs, and CTFs. Plugin-based, multi-provider LLM support with local…
 mubix/ai-ctf
Local AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.
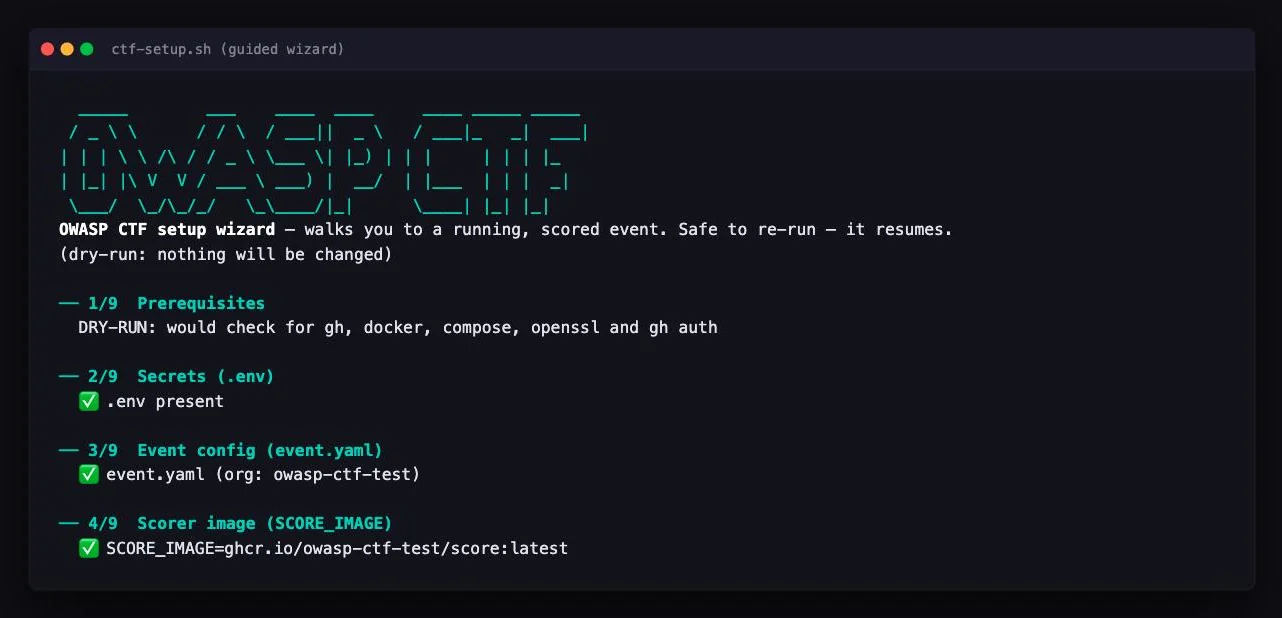 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 whereisxuezugi/cplhf
Modular Bash toolkit that hardens Debian/Ubuntu systems for CyberPatriot competitions, automating account, firewall, SSH, PAM, and service hardening…