
log4jhound
 mebibite/log4jhound
Created after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
static-analysisvulnerability-scannerscode-analysis+2
mebibite/log4jhoundCreated after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
 marklindsey11/gh-repo-clone-marklindsey11--cve-2021-44228_scanner-applications-that-are-vulnerable-to-the-log4j-cv
Scans applications for the Log4Shell vulnerability (CVE-2021-44228) to identify systems at risk of remote code execution.
 manishkanyal/log4j-scanner
A Log4j vulnerability scanner is used to identify the CVE-2021-44228 and CVE_2021_45046
 makitos666/cve-2026-31431-copy-fail-detection-toolkit
Detection and analysis toolkit for CVE-2026-31431 Linux LPE, providing Python and PowerShell scanners, YARA rules, and forensic analysis for active…
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
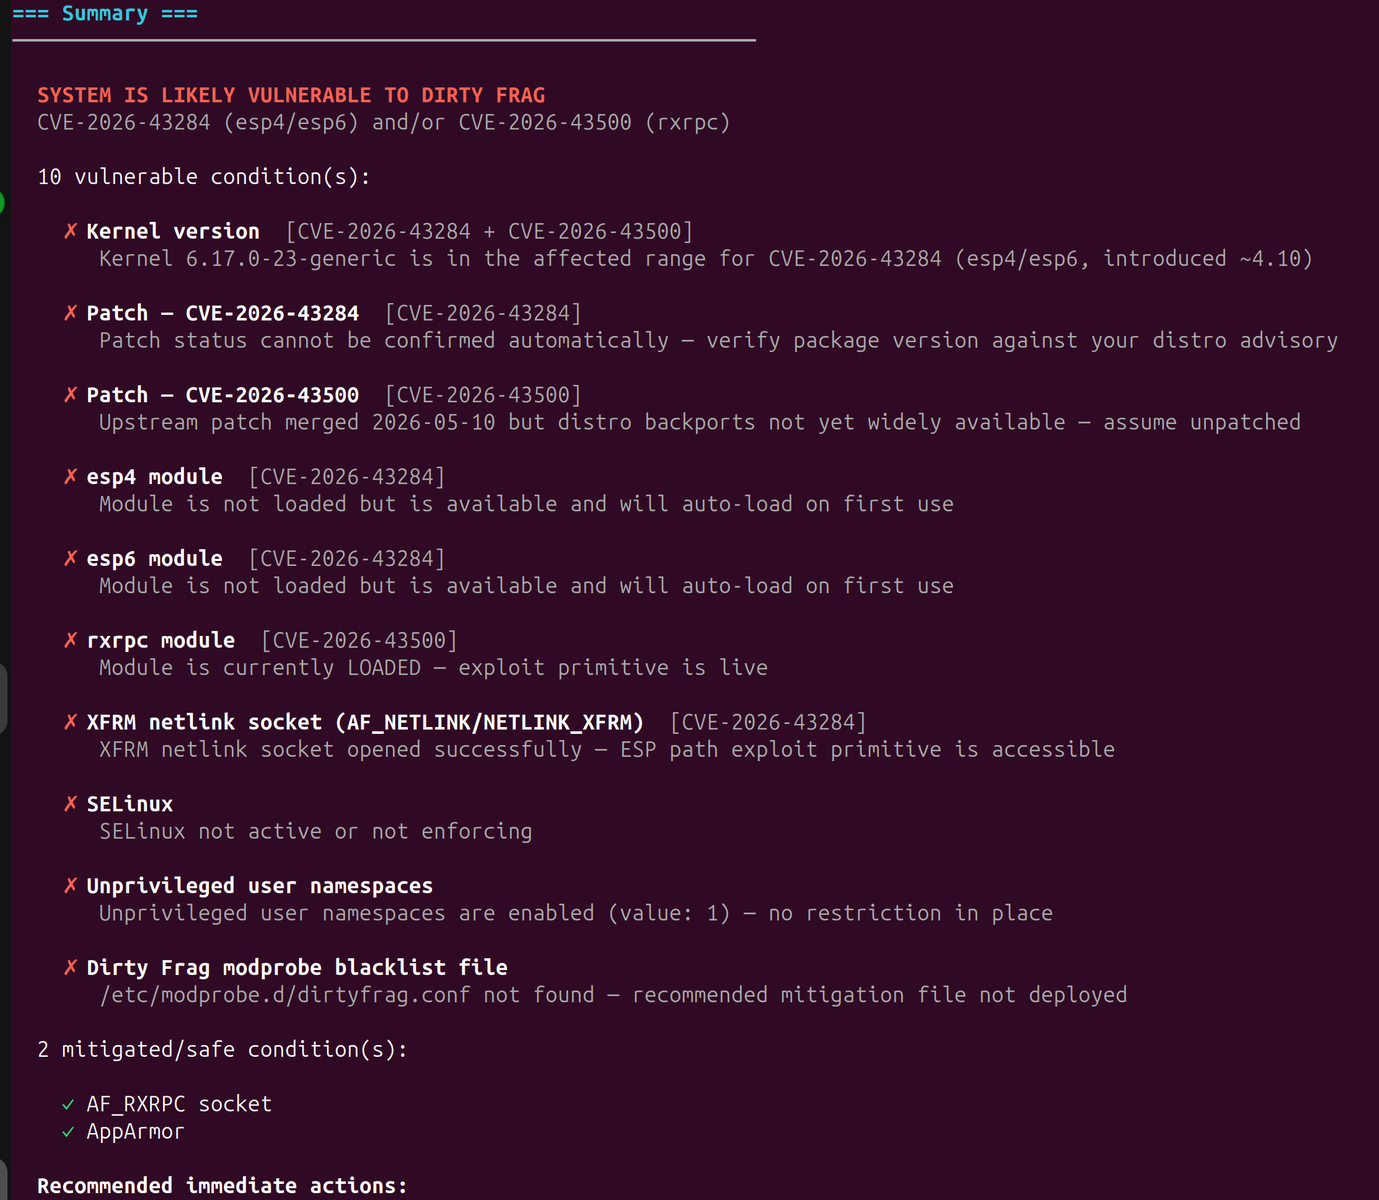 liamromanis101/dirtyfrag-detector
CVE-2026-43284/CVE-2026-43500 'DirtyFrag' Benign patch & mitigation detection script
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
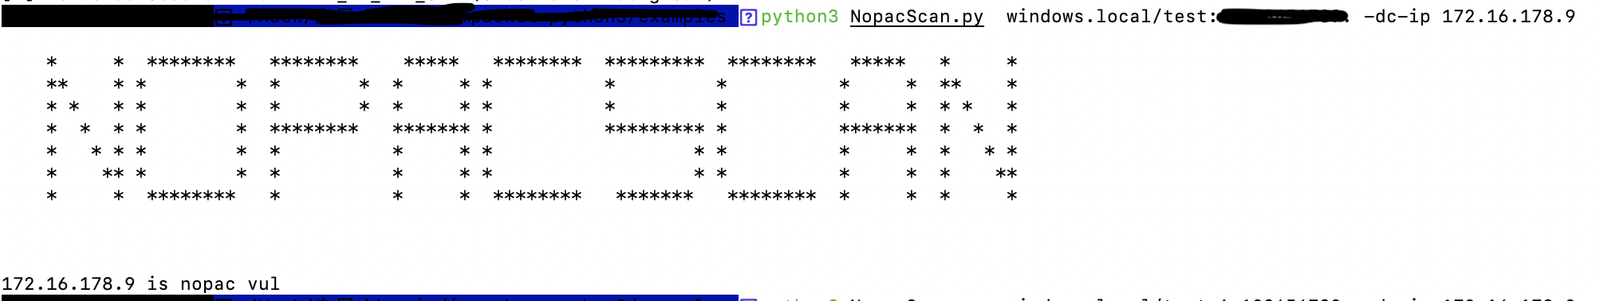 knightswd/nopacscan
Scans Active Directory domain controllers for CVE-2021-42287 and CVE-2021-42278 by querying DNS for all DCs and analyzing PAC structures for the 0x10…
 kadir/copy-fail-cve-2026-31431-ioc
Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation
 jwde/automerge-test
A minimal test repository for auto-merge functionality, referencing a CVE variant.
 jrocia/search-log4jvuln-appscanstd
This Pwsh script run AppScan Standard scans against a list of web sites (URLs.txt) checking for Log4J (CVE-2021-44228) vulnerability
 hohn/codeql-sample-polkit
All stages of exploring the polkit CVE-2021-4034 using codeql
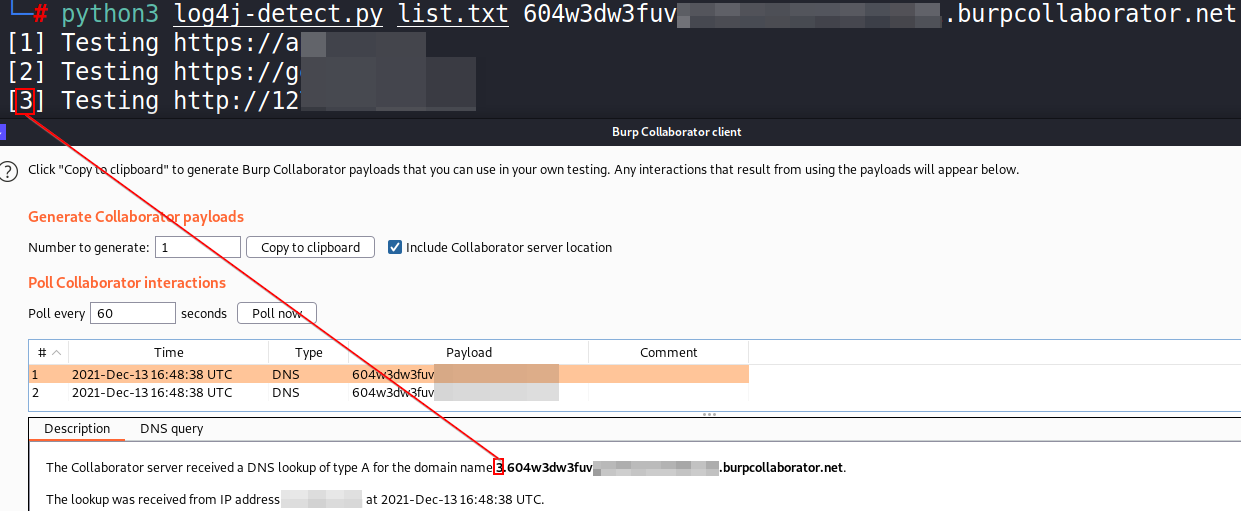 hassaanahmad813/log4j
Multithreaded Python scanner that detects Log4Shell (CVE-2021-44228) by sending crafted HTTP requests with JNDI payloads and monitoring DNS callbacks…
 haydenjames/dirty-frag-check
Read-only checker for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) Linux kernel local-root vulns
 hargabyte/cve-scanner
Local CVE scanner for OpenClaw that checks versions against 522+ known vulnerabilities, displays recent HIGH-severity CVEs, and recommends upgrades.…
 gopinaath/cve-2025-49844-discovery
Audits AWS ElastiCache Redis/Valkey clusters for network exposure, checking VPC, subnet, and internet gateway routes across multiple accounts and…
 effiesec/copy-fail-cve-2026-31431
Passive Linux host scanner that classifies exposure to CVE-2026-31431 via kernel version, distro changelog, module status, and AF_ALG reachability,…
 devstuff/harden-docker-seccomp
Docker mitigation for CVE-2026-31431 ('Copy Fail'). Includes Kubernetes templates as well.