

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/haydenjames/dirty-frag-check
Vulnerability ScannersVulnerability AnalysisConfiguration AuditingDevSecOpsIncident Response
GitHubhaydenjames/dirty-frag-check

dirty-frag-check

Read-only checker for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) Linux kernel local-root vulns

View Repository
6686 months agoNot yet reviewed
Share

Dirty Frag check (CVE-2026-43284 / CVE-2026-43500)

Read-only checker for the "Dirty Frag" Linux kernel local-root vulns (CVE-2026-43284, CVE-2026-43500). Checks kernel version, module state, KernelCare livepatch, and any modprobe blacklist you've added. Doesn't run exploit code.

Companion to CVE-2026-31431-check.
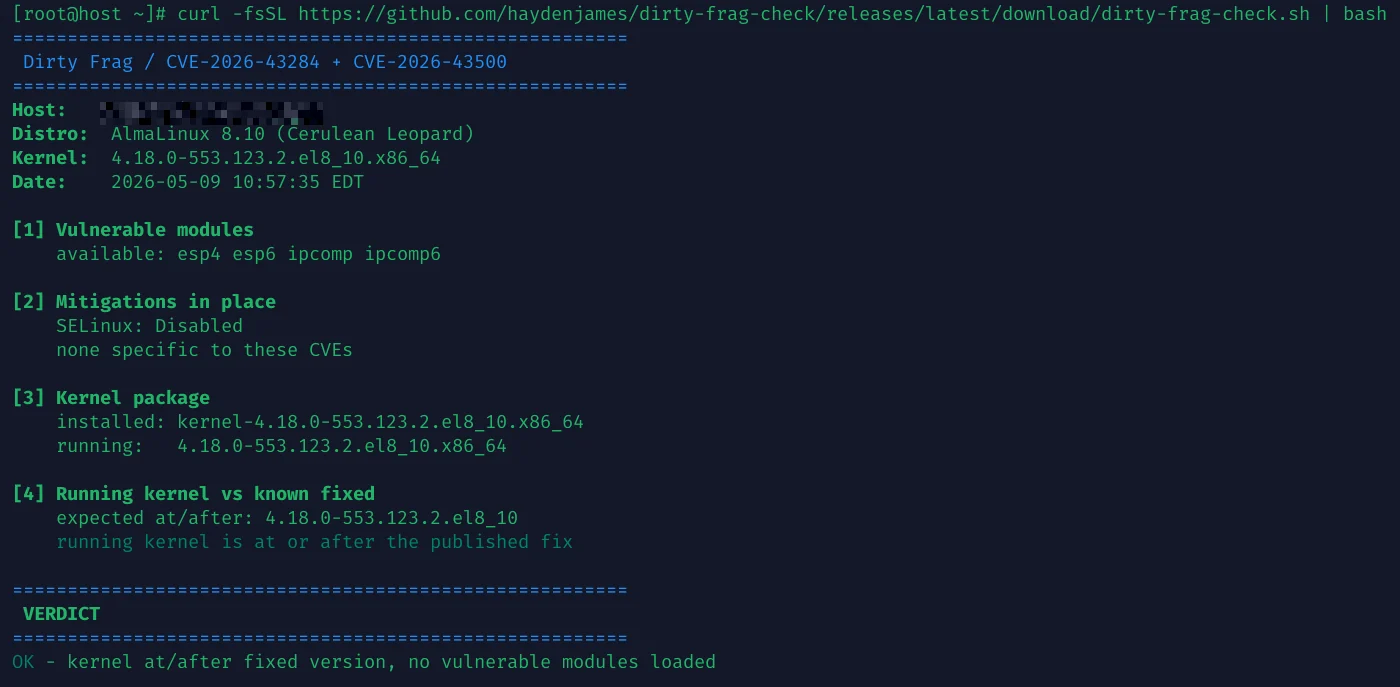
Example output on AlmaLinux 8.10

Heads up: this is a heuristic. A green verdict isn't a guarantee. Cross-reference with your distro's advisory before you call a host safe. MIT, no warranty.

Quick run

curl -fsSL https://github.com/haydenjames/dirty-frag-check/releases/latest/download/dirty-frag-check.sh | bash

Read it first if you don't trust piping to bash:

curl -fsSLO https://github.com/haydenjames/dirty-frag-check/releases/latest/download/dirty-frag-check.sh
less dirty-frag-check.sh
chmod +x dirty-frag-check.sh && ./dirty-frag-check.sh

Pin to a release tag for change control: https://raw.githubusercontent.com/haydenjames/dirty-frag-check/v1.0.4/dirty-frag-check.sh.

-q for one-line fleet output. -h for help. Exit 0 ok, 1 vulnerable, 2 unknown.

Fleet usage

# parallel-ssh
parallel-ssh -h hosts.txt -i 'bash -s -- -q' < dirty-frag-check.sh

# ansible
ansible all -m script -a "dirty-frag-check.sh -q"

Exit codes (0 ok, 1 vulnerable, 2 unknown) work with anything that aggregates by status.

Requirements

bash 4+, plus the usual awk/grep/sed/lsmod/modprobe. No root required for the check itself. Applying mitigations does need root.

What it checks

  1. Module state. Whether the modules implicated by the advisory — esp4, esp6, ipcomp, ipcomp6 (CVE-2026-43284) and rxrpc (CVE-2026-43500) — are loaded, available, or absent.
  2. Mitigations. Looks for modprobe blacklist files and verifies the blacklist actually wins via modprobe -n -v. Reports SELinux and AppArmor status. Detects KernelCare livepatch via kcarectl --patch-info.
  3. Kernel package vs running. Catches the case where you've installed a patched kernel but haven't rebooted into it.
  4. Running kernel vs known-fixed version. For RHEL-family distros (AlmaLinux, Rocky, RHEL, CloudLinux), compares uname -r against the vendor-published fixed version for that release. Best-effort; verify against your distro tracker.

Verdicts

  • OK — KernelCare livepatch applied, running kernel at/after the published fix, or all relevant modules blacklisted.
  • MITIGATED — kernel is unpatched but every reach-in module is blacklisted, so the bug can't be triggered. Patch when you can.
  • REBOOT NEEDED — patched kernel installed, you're still on the old one.
  • VULNERABLE — running kernel verified older than the fix and a kernel upgrade is available, or modules loaded with an upgrade pending.
  • WAITING ON VENDOR PATCH — running kernel older than the upstream fix, no kernel upgrade currently available. Common on Rocky/CloudLinux trailing AlmaLinux by a build, or when the distro backports under a different version string.
  • AT RISK — KernelCare-managed host without the Dirty Frag livepatch yet, or modules available with an upgrade pending.
  • LIKELY PATCHED — modules loaded but the running kernel is at/after the published fix. Script can't introspect a loaded module's patch level; defers to vendor metadata.
  • UNKNOWN — no fixed-version table for this distro (Ubuntu, Debian, TuxCare ELS) and no other strong signal. Cross-reference the distro tracker.

Stopgap mitigation

Use this when your distro hasn't shipped a kernel update yet, or when you can't reboot soon and need the reach-in modules unloaded:

sudo tee /etc/modprobe.d/disable-dirty-frag.conf <<'EOF'
install esp4 /bin/false
install esp6 /bin/false
install ipcomp /bin/false
install ipcomp6 /bin/false
install rxrpc /bin/false
EOF
sudo rmmod rxrpc ipcomp6 ipcomp esp6 esp4 2>/dev/null || true

If rmmod says "module is in use", something on the box actively uses IPsec or AF_RXRPC (some VPNs, AFS clients, strongSwan, Libreswan). Don't force-unload it. Patch the kernel and reboot instead.

KernelCare / TuxCare ELS users: livepatches for CVE-2026-43284 cover this without a reboot. Check kcarectl --patch-info.

Targets

Aimed at AlmaLinux 8/9/10, Rocky, RHEL, CloudLinux 8/9/10, Ubuntu, Debian, and CentOS 7 (TuxCare ELS / KernelCare). The fixed-version table is RHEL-family-specific; Ubuntu/Debian fall back to package-manager freshness. Confirm any green verdict against your distro's tracker.

Discussion

  • AlmaLinux advisory: Dirty Frag
  • CloudLinux / KernelCare: mitigation and kernel update
  • cPanel: security advisory
  • Forum thread: Dirty Frag check script (linuxcommunity.io)
  • Companion checker: CVE-2026-31431-check
  • Issues: GitHub

License

MIT — see LICENSE.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →






