
detect_CVE-2026-25177
 danaug23/detect_cve-2026-25177
Production-safe scanner that detects CVE-2026-25177 (AD SPN Unicode Collision) exploitation on Active Directory Domain Controllers. Read-only.
vulnerability-scannersconfiguration-auditing
danaug23/detect_cve-2026-25177Production-safe scanner that detects CVE-2026-25177 (AD SPN Unicode Collision) exploitation on Active Directory Domain Controllers. Read-only.
 cybrdude/cve-2026-1731-scanner
Passive vulnerability scanner for CVE-2026-1731 — BeyondTrust RS/PRA pre-auth RCE (CVSS 9.9). Educational & defensive use only.
 cyberdudebivash/cyberdudebivash-modular-ds-cve-2026-23550-detector
authorized CYBERDUDEBIVASH ECOSYSTEM tool for detecting CVE-2026-23550 in WordPress Modular DS plugin
 cyberdudebivash/cyberdudebivash-5g-core-key-rotation-ghost-admin-auditor
Production-grade tool for detecting & remediating CVE-2026-0622 (Ghost Admin privilege escalation & master key exposure in 5G core software).
 codiobert/pwnkit-scanner
Scans Linux systems for the Polkit privilege escalation vulnerability (CVE-2021-4034) and provides mitigation guidance.
 cropnet/ni8mare
Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…
 cozystack/copy-fail-blocker
BPF-LSM mitigation for CVE-2026-31431 (Copy Fail) — denies AF_ALG socket creation cluster-wide
 byinarie/zirconium
Tool to search for IOCs related to HAFNIUM: CVE-2021-26855 CVE-2021-26857 CVE-2021-26858 CVE-2021-27065
 barrersoftware/opencode-secure
Security-hardened fork of OpenCode - Fixes CVE-2026-22812 (CVSS 8.8 RCE) that upstream refuses to patch
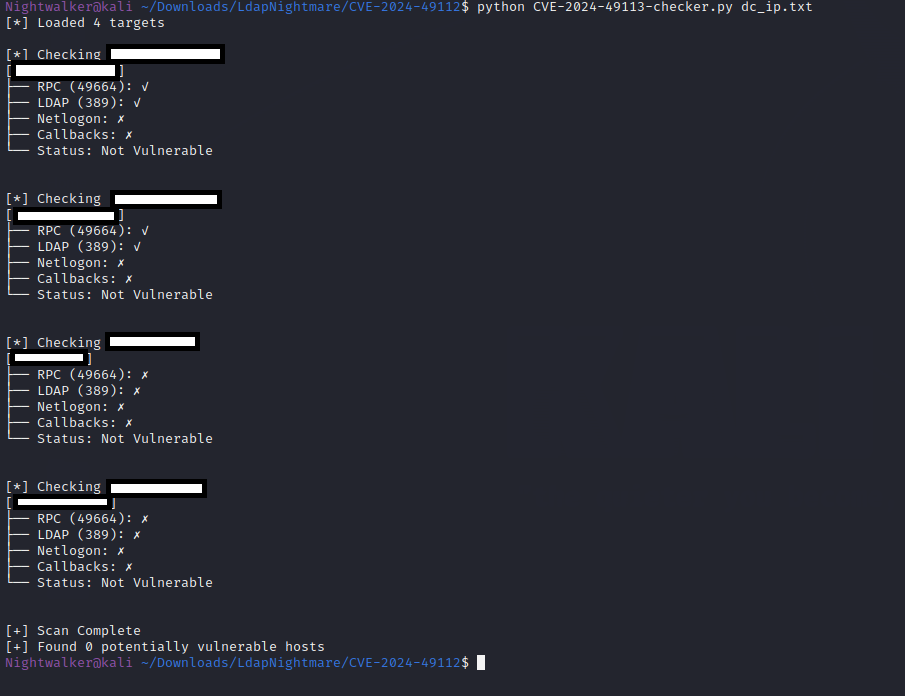 barcrange/cve-2024-49113-checker
Checks if a system is potentially vulnerable to CVE-2024-49113 (LDAP Nightmare) by testing RPC connectivity, LDAP ports, Netlogon service, and LDAP…
 ashizzz/cve-2026-22610
Scans Angular projects for XSS vulnerabilities in SVG elements and unsafe bindings, generating a vulnerability report with line numbers and…
 arnaudluti/ps-cve-2021-44228
Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.
 andreassudo/cve-2026-21510-cvss-8.8-important-windows-shell-security-feature-bypass
Detailed analysis of CVE-2026-21510, a Windows Shell security feature bypass allowing silent code execution via malicious links or shortcuts.…
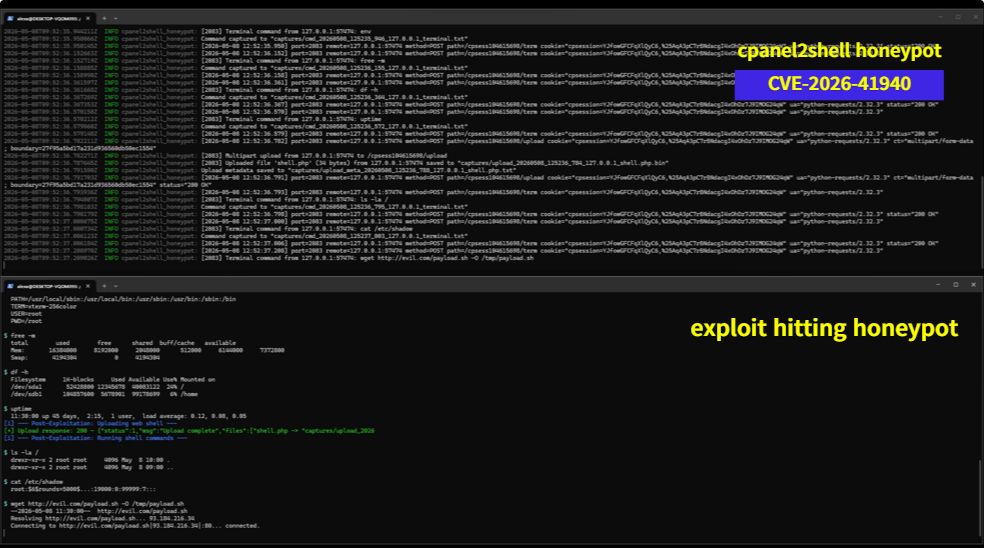 acuciureanu/cpanel2shell-honeypot
A Rust honeypot that simulates a vulnerable cPanel/WHM instance for CVE-2026-41940
 abrahamsurf/sdwan-scanner-cve-2026-20127
Cisco SD-WAN Exposure & Potential Vulnerability Scanner (Passive Fingerprinting) 2026
 wavesman/cve-2026-31431-fleet-remediator
Fleet-scale CVE-2026-31431 audit and remediation orchestrator for Linux hosts via SSH, with strict host-key verification and multi-format reporting.
 timborin0/log4j-dork-scanner
A script to search, scrape and scan for Apache Log4j CVE-2021-44228 affected files using Google dorks
 svenlie/next-rep-cve-2026-4800
Default Next.js application scaffold generated with create-next-app, providing a basic TypeScript project structure for web development.