
shadow-repeater
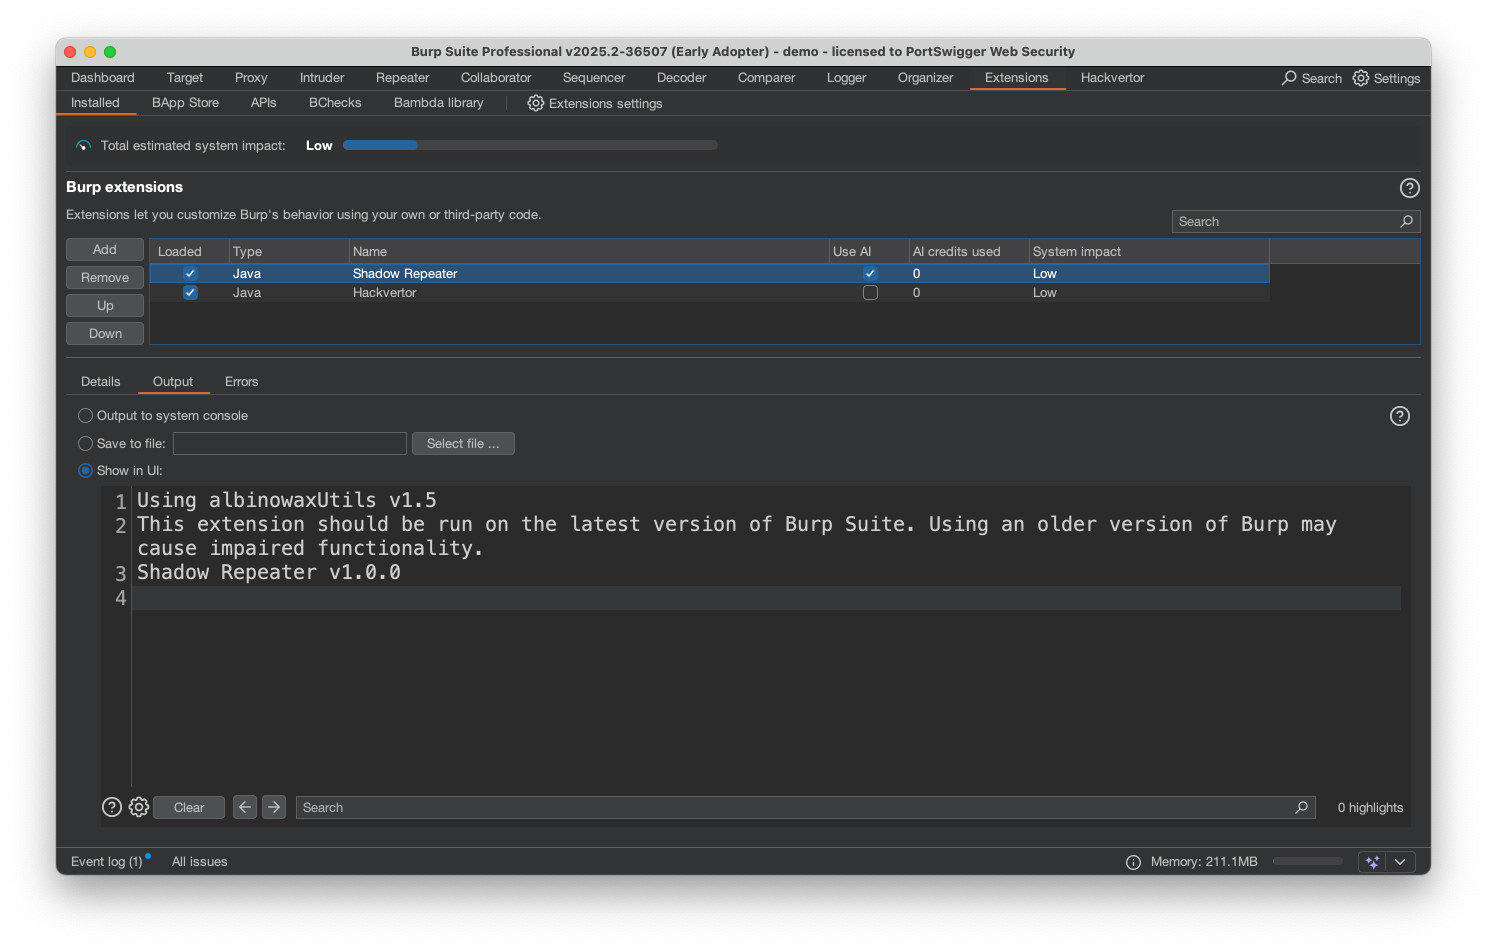
Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…

Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…

Sample Burp Suite extensions demonstrating the Montoya API, covering HTTP and proxy handlers, custom scan checks, Intruder payloads, WebSocket…

Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.

Statically compiled ARM binaries for debugging and runtime analysis

Reddit OSINT by username. Discover indexed posts, comments, deleted and live content, activity patterns, exposed identifiers, and an overall exposure…

Neutralize KEPServerEX anti-debugging techniques

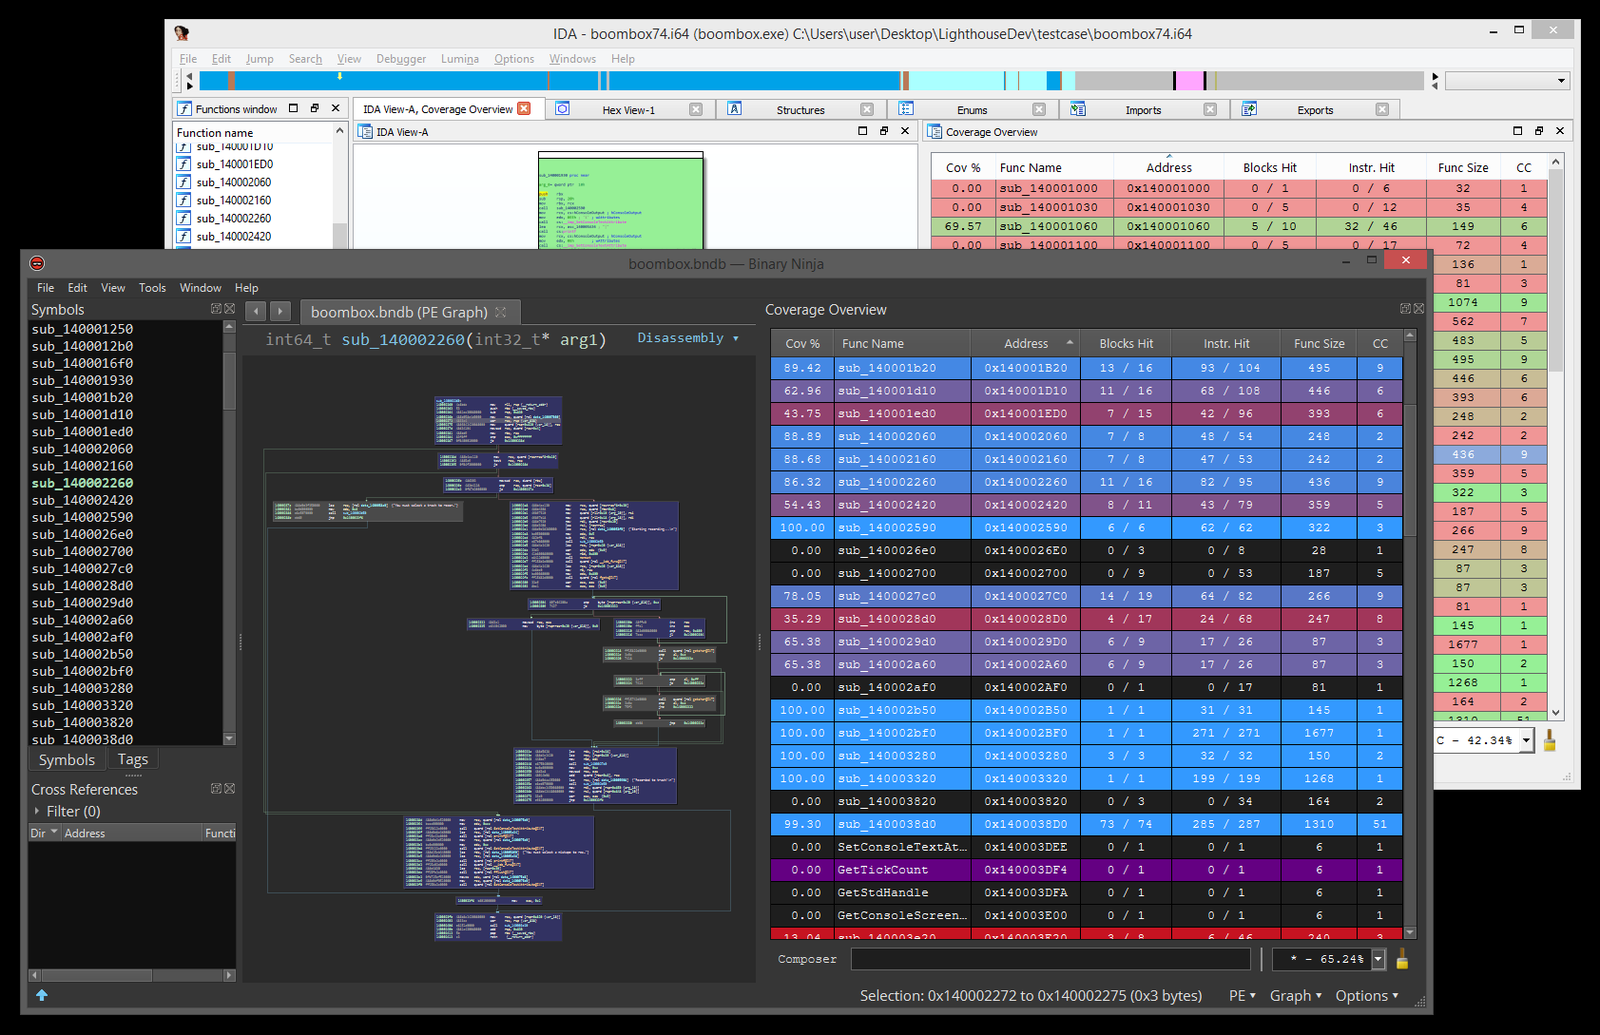
A Coverage Explorer for Reverse Engineers

Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android

Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…

Standards compliant HTML filter written in PHP

Collection of Zero Day Initiative conference presentations, whitepapers, and vulnerability research publications covering exploit techniques and…

8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting

The next level 100% Python obfuscator.

Extracts and decrypts inner payloads from Donut obfuscator samples by detecting loader shellcode signatures, parsing the DONUT_INSTANCE structure,…

Enumerate the permissions associated with AWS credential set

Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…

Python bindings for Valgrind's VEX IR.

Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…