
GraphQLGrapper
 m19o/graphqlgrapper
Burp Suite extension to extract and collect GraphQL API endpoints from HTTP request history for security testing and reconnaissance.
reconnaissanceweb-application-exploitationapi-security-testing+3
21
m19o/graphqlgrapperBurp Suite extension to extract and collect GraphQL API endpoints from HTTP request history for security testing and reconnaissance.
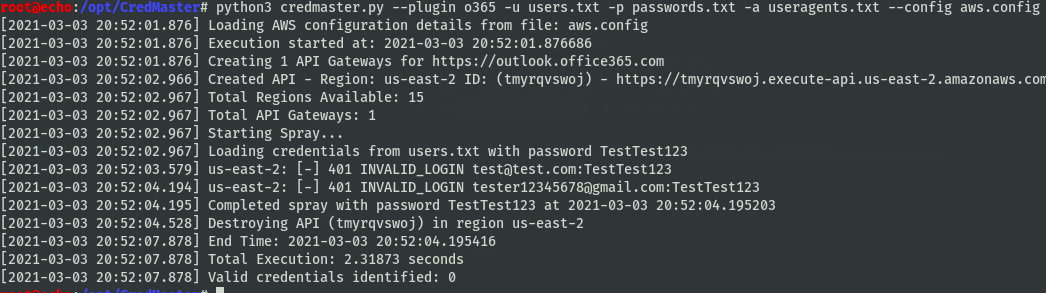 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
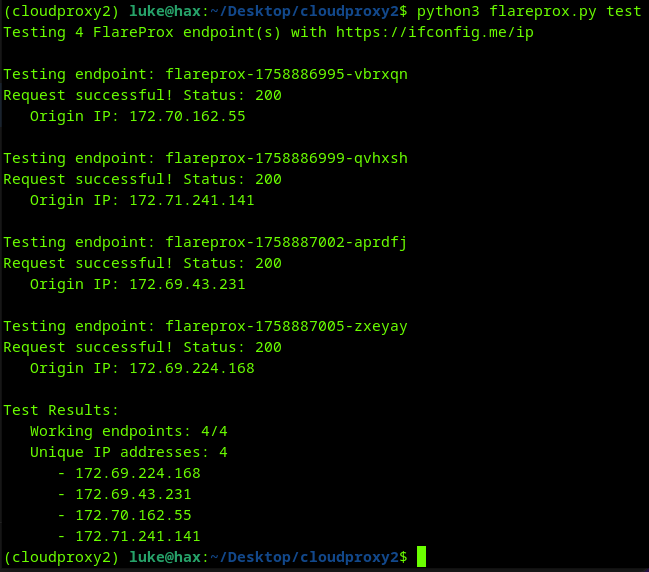 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
 emo-crab/slinger
An HTTP client specifically developed for security researchers
 projectdiscovery/chaos-client
Go client to communicate with Chaos DB API.
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 shoucheng3/perwendel__spark_cve-2018-9159_2-7-1
Lightweight Java 8 web framework with routing, filters, and static file serving. Includes security advisory for older versions and CRUD API examples.
 shoucheng3/perwendel__spark_cve-2018-9159_2_7_2_fixed
Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.
 osirium/suds
Clone of suds 0.4 + suds-0.4-CVE-2013-2217.patch
 shoucheng3/square__retrofit_cve-2018-1000850_2-4-0
Type-safe HTTP client library for Android and Java, enabling REST API communication with annotation-based request configuration and converter support.
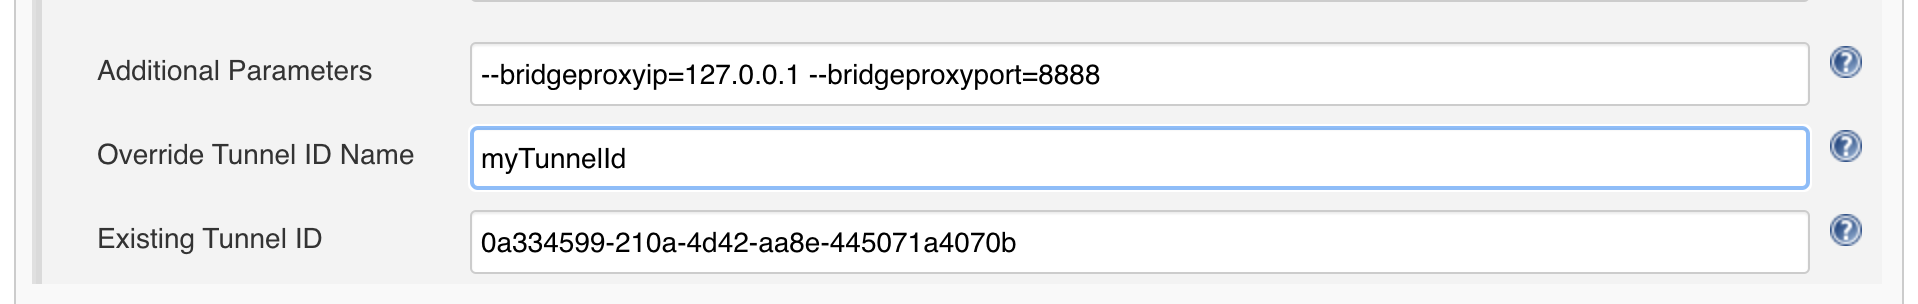 shoucheng3/jenkinsci__perfecto-plugin_cve-2020-2261_1-17
Jenkins plugin for automated mobile app testing via Perfecto cloud, managing secure tunnel connections and app uploads within CI/CD pipelines.
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
 havoc10-sw/detect_polyfill_cve-2024-38537-
Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.
 oscerd/cve-2026-48204
Reproducer for CVE-2026-48204: Apache Camel camel-mongodb-gridfs gridfs.* header injection overriding the GridFS operation (enumerate/read/delete…
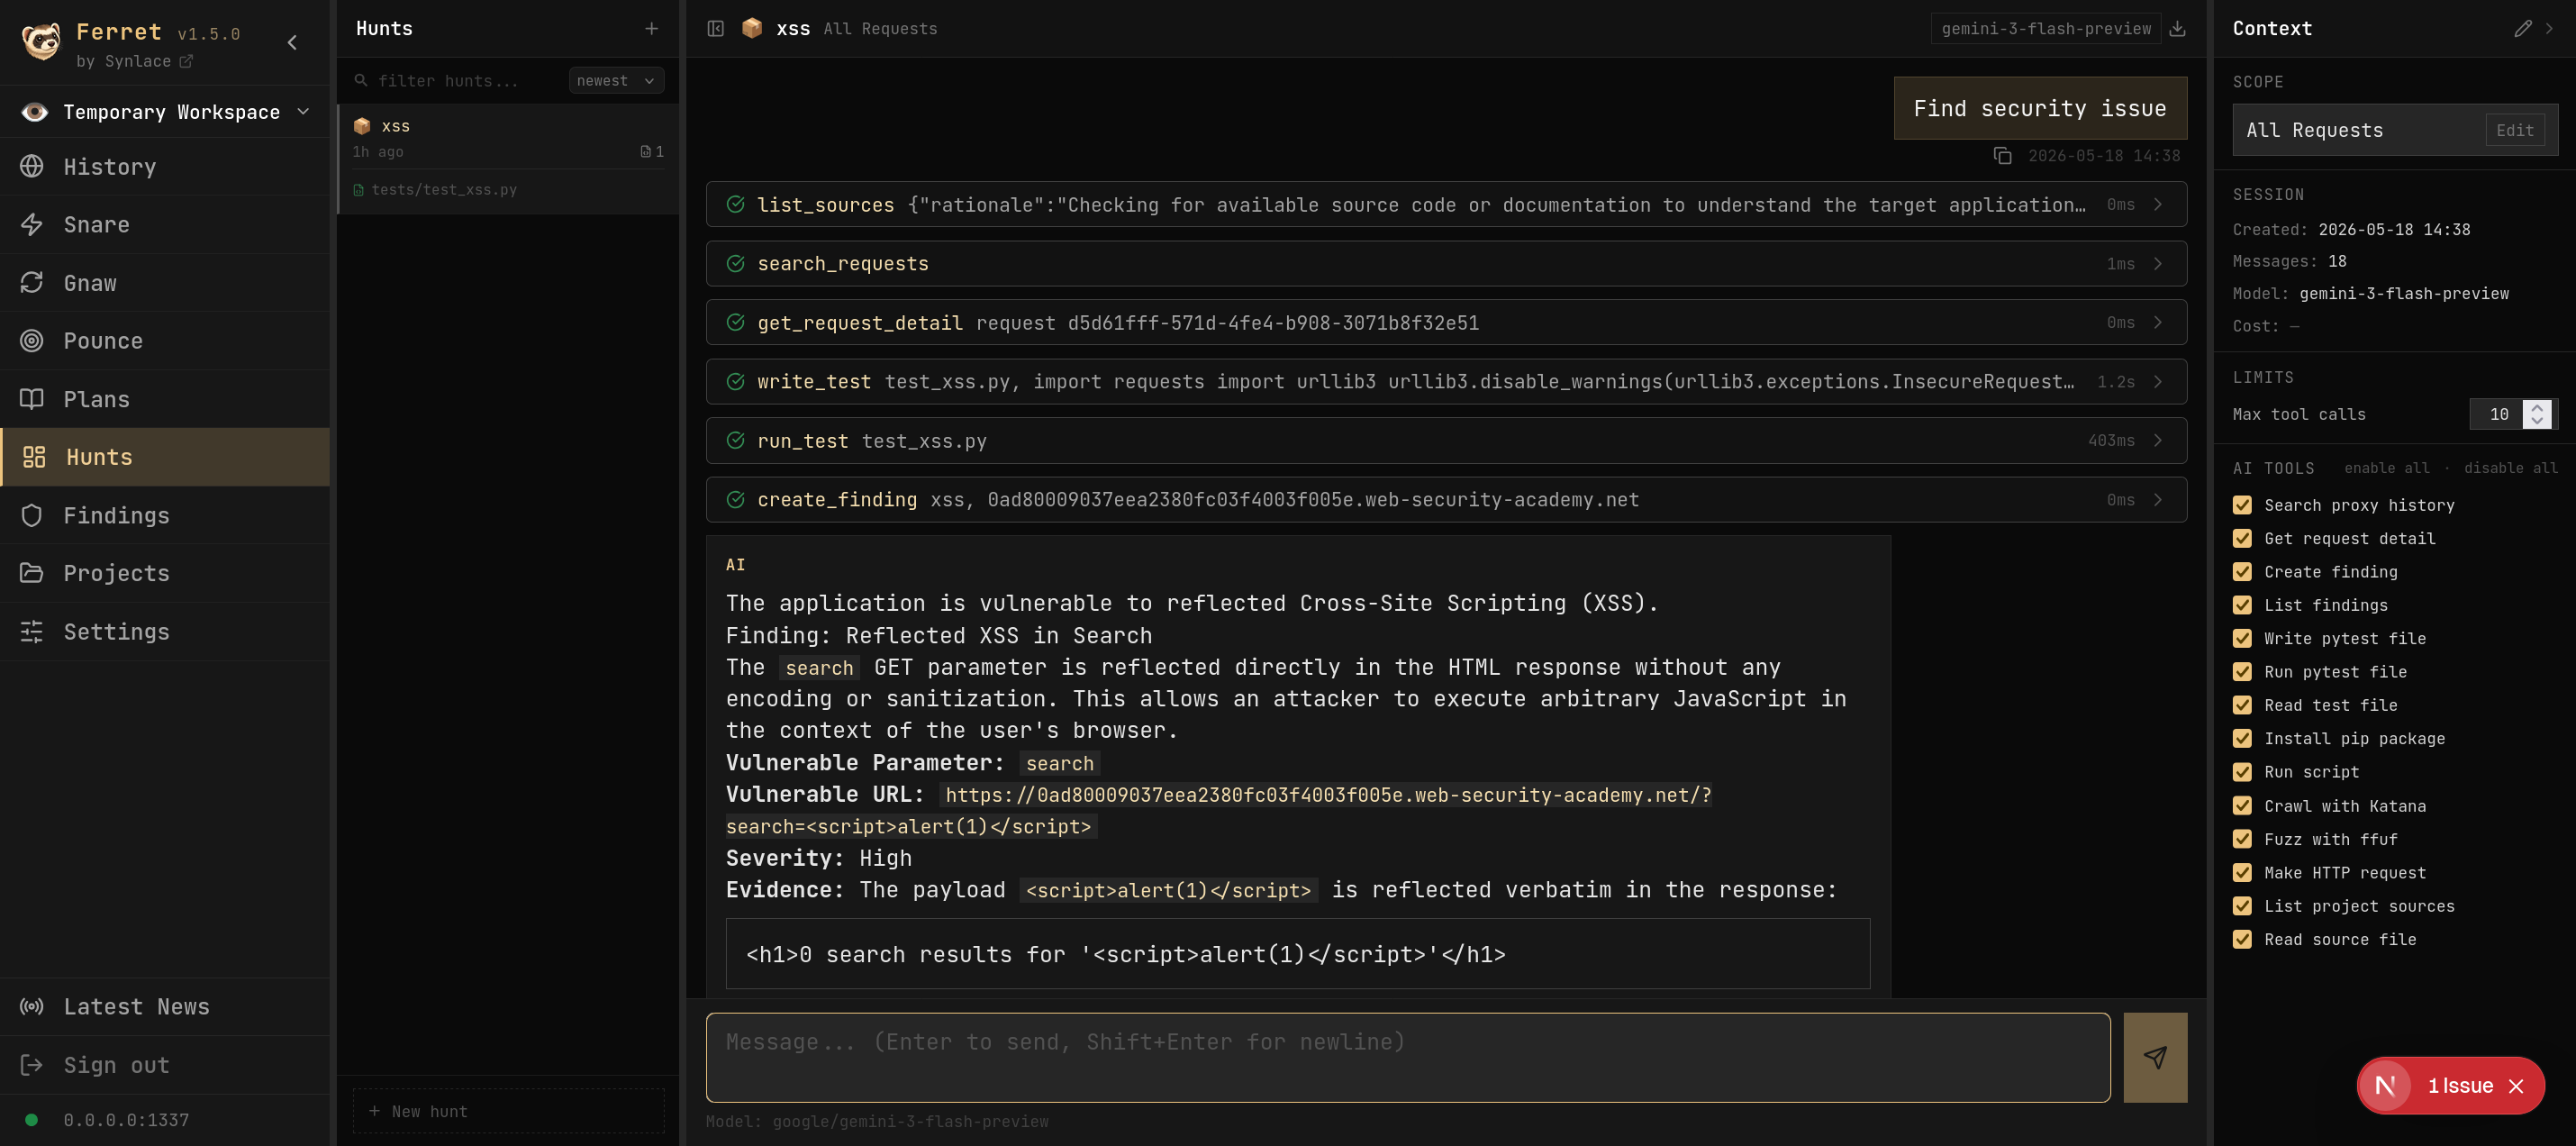 synlace/ferret
The collaborative web app pentest suite
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision