usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.





[!TIP] New! Strix integrates seamlessly with GitHub Actions and CI/CD pipelines. Automatically scan for vulnerabilities on every pull request and block insecure code before it reaches production - Get started with no setup required.
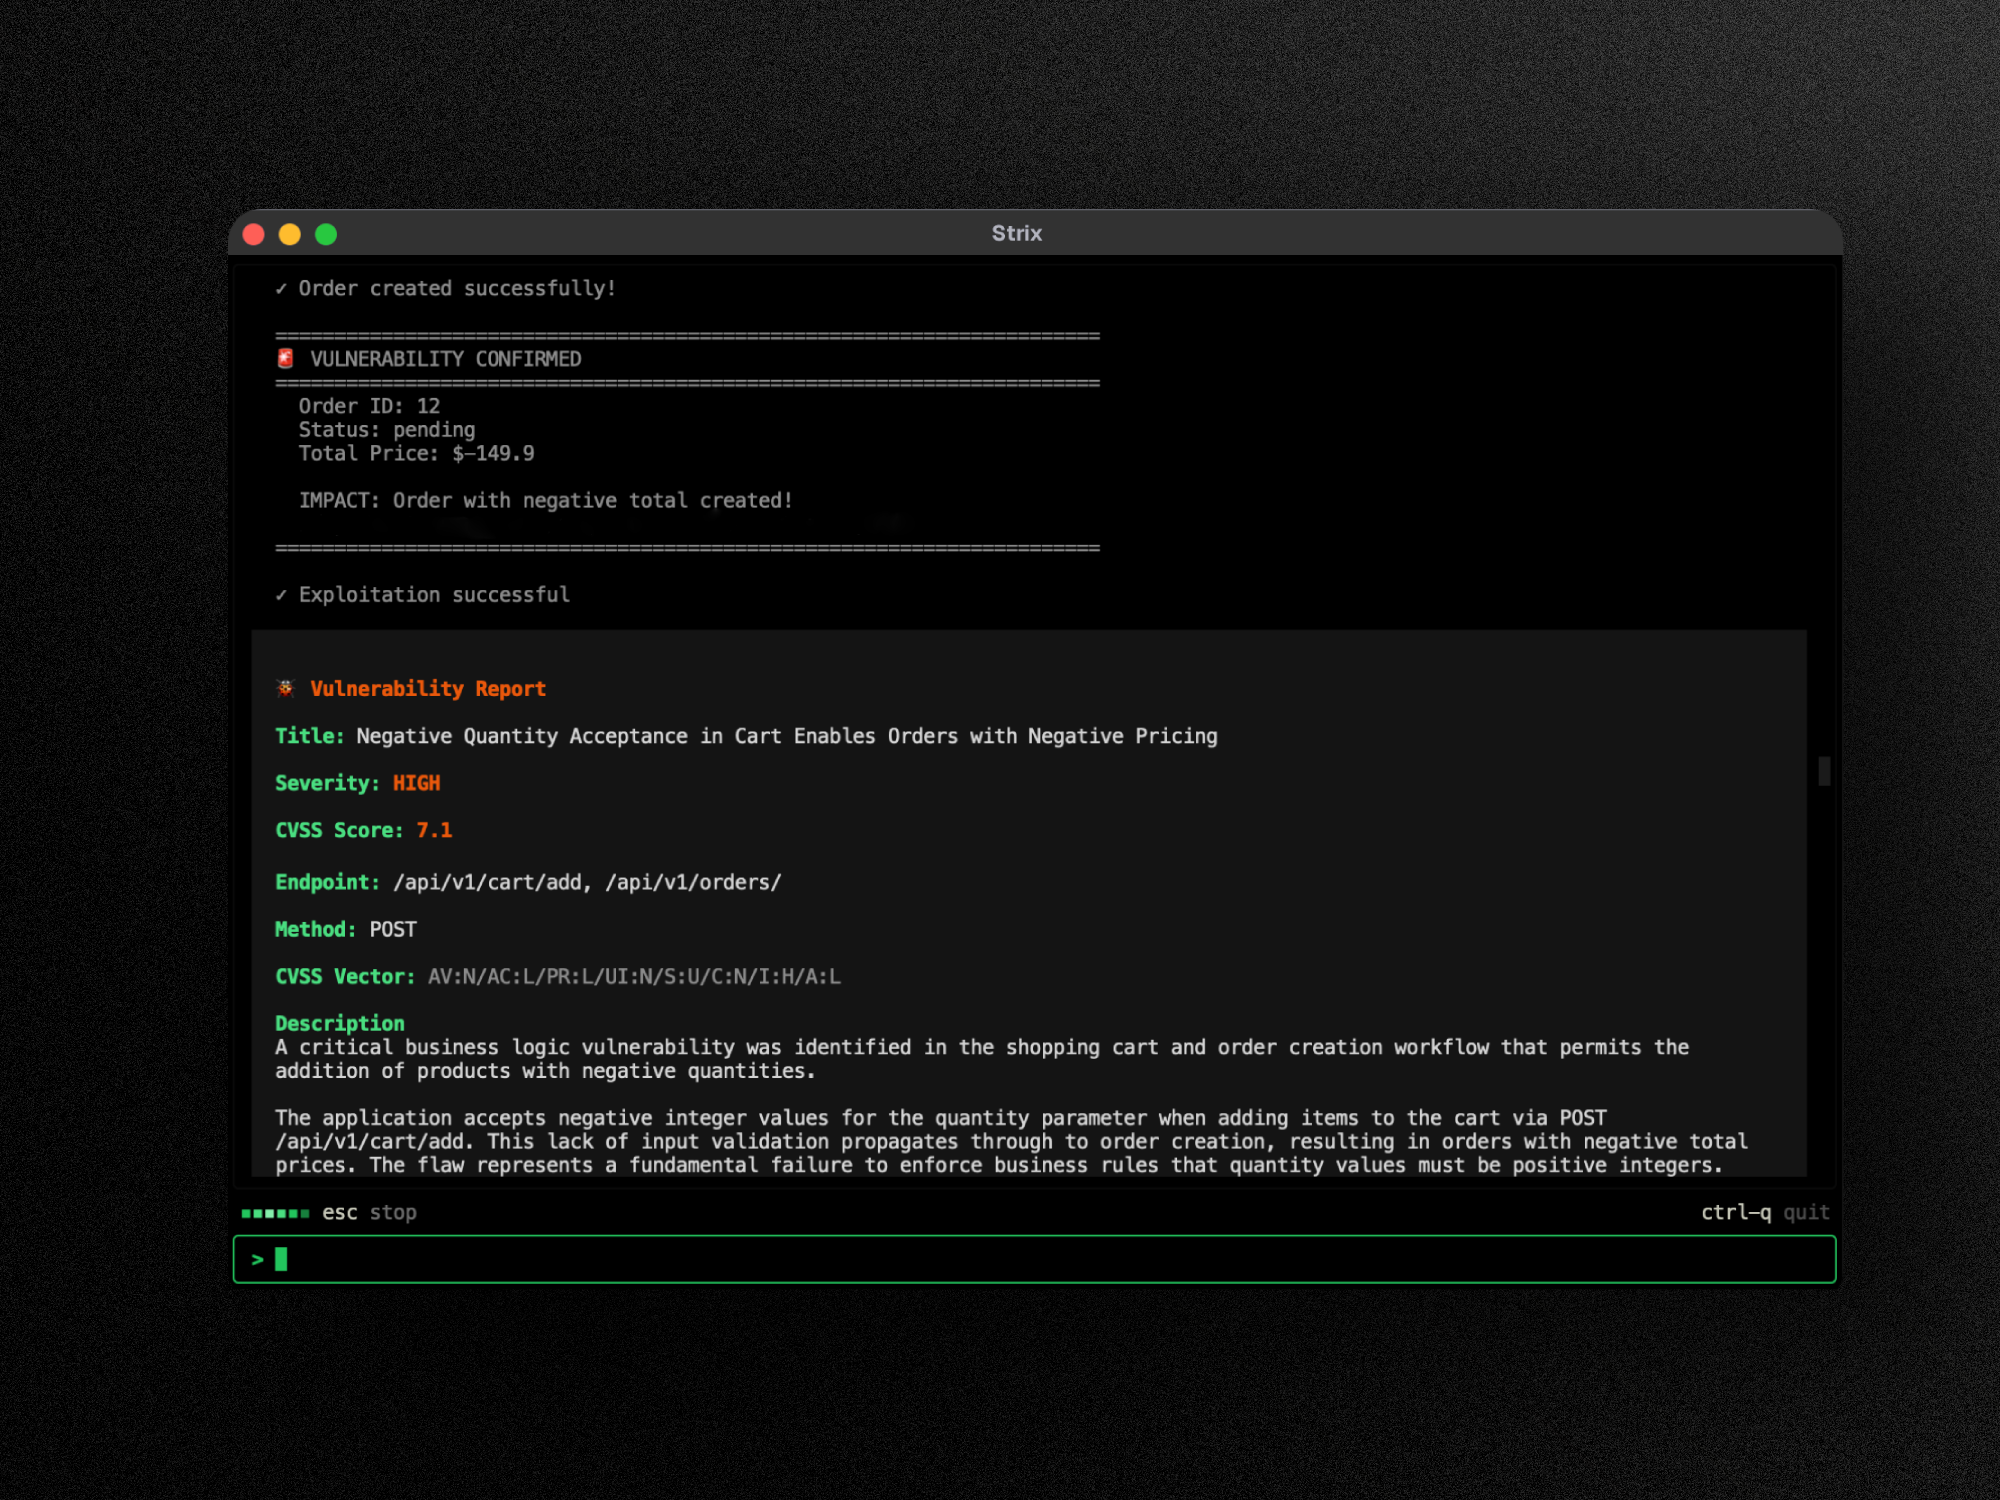
Strix are autonomous AI penetration testing agents that act just like real hackers - they run your code dynamically, find vulnerabilities, and validate them through actual proofs-of-concept. Built for developers and security teams who need fast, accurate security testing without the overhead of manual pentesting or the false positives of static analysis tools.
Key Capabilities:
Prerequisites:
# Install Strix
curl -sSL https://strix.ai/install | bash

# Configure your AI provider
export STRIX_LLM="openrouter/z-ai/glm-5.3"
export LLM_API_KEY="your-api-key"

# Run your first security assessment
strix --target ./app-directory
[!NOTE] First run automatically pulls the sandbox Docker image. Results are saved to
strix_runs/<run-name>
Try the Strix full-stack penetration testing platform at app.strix.ai - sign up for free, connect your repos and domains, and launch a pentest in minutes.
Get the same Strix experience with enterprise-grade controls: SSO (SAML/OIDC), custom compliance-ready penetration testing reports (SOC 2, ISO 27001, PCI DSS), dedicated support and SLA, custom deployment options (VPC or self-hosted), BYOK model support, and tailored AI pentesting agents optimized for your environment.
Strix is agent-ready. Give Claude Code, Cursor, Codex, or any SKILL.md-compatible agent the ability to run pentests, fix findings, and set up CI scanning:
npx skills add usestrix/strix
This installs nine skills for running pentests, fixing findings, and CI scanning, against code, web apps, APIs, and the OWASP Top 10. Agents can use the local CLI or the managed cloud with the same engine.
See AGENTS.md for the quick reference, docs.strix.ai/llms.txt for the CLI, and docs.app.strix.ai for the API.
Strix agents come equipped with a comprehensive offensive security toolkit - the same tools used by professional penetration testers and ethical hackers: