CredMaster
Launch a password spray / brute force attach via Amazon AWS passthrough proxies, shifting the requesting IP address for every authentication attempt. This dynamically creates FireProx APIs for more evasive password sprays.
Shoutout to @ustayready for his CredKing and FireProx tools, which form the base of this suite.
See all the full notes on the Wiki, tool released with specifics in this blogpost
For detection tips, see the blogpost and detection section.
Be careful for account lockouts, know the reset policies of your target
TL;DR
- git clone the repo down
- If unsure how to create correct keys see this blog.
pip install -r requirements.txt- Fill out the config file (wiki) with desired options, or provide through CLI
Benefits & Features
- Rotates the requesting IP address for every request
- Automatically generates APIs for proxy passthru
- Spoofs API tracking numbers, forwarded-for IPs, and other proxy tracking headers = fully anonymous
- Easily configuation via config file
- Multi-threaded processing
- Password delay counters & configuration for lockout policy evasion
- Easily add new plugins
- Colourised output
- Notification systems for Keybase, Slack, Discord, Teams & Pushover
- WeekdayWarrior setting for timed spraying and SOC evasion
Quick Use
The following plugins are currently supported:
- OWA - Outlook Web Access
- EWS - Exchange Web Services
- O365 - Office365 - DEPRECATED
- ADFS - Active Directory Federation Services
- O365Enum - Office365 User Enum (No Authentication Request)
- MSOL - Microsoft Online
- MSGraph - MSGraph Module, msgraph spray point for azure and MSOL credentials
- AzureSSO - Azure AD Seamless SSO Endpoint
- AzVault - AzVault Module, Azure spray point different to MSOL/AzureSSO
- Okta - Okta Authentication Portal
- FortinetVPN - Fortinet VPN Client
- HTTPBrute - Generic HTTP Brute Methods (Basic/Digest/NTLM)
- GMailEnum - GSuite/Gmail enumeration
- PingFed - Ping Federated Authentication
- HTTPPost - Generic HTTP POST with custom body and headers
Example Use:
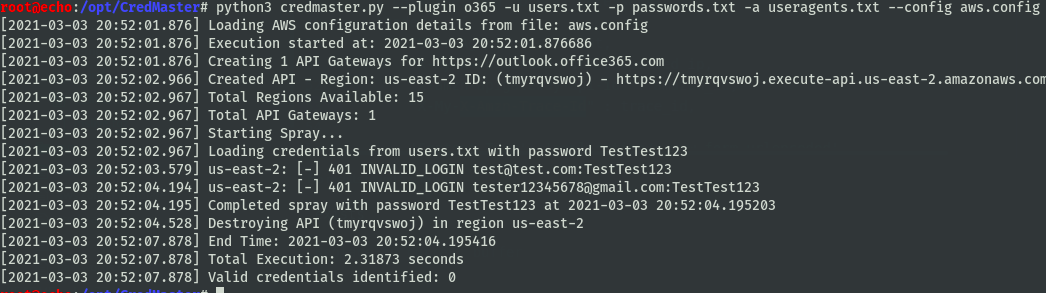
python3 credmaster.py --plugin {pluginname} --access_key {key} --secret_access_key {key} -u userfile -p passwordfile -a useragentfile {otherargs}
or
python3 credmaster.py --config config.json
This tool requires AWS API access keys, a walkthrough on how to acquire these keys can be found here: https://bond-o.medium.com/aws-pass-through-proxy-84f1f7fa4b4b
All other usage details can be found on the wiki
TODO
PRs welcome :)
- New Plugin: Optiv's Go365 Method - Includes Office365 auth and userenum capabilities via SOAP
- "Resume" functionality for paused/cancelled scans. Ideally storing data for APIs used, if they were destroyed and what user/pwd the spray was on
- Method to reliably determine if an auth attempt was throttled, so the username could be re-queued and tried again later for full cover (would have to be per-plugin, return "throttled" boolean value in plugin script, requeue if throttled)
- Notification system for webhooks (Teams TODO)
- Stop on success flag
- Spray profile overhaul
- Development notes
- Spray username==password
Credits
- Mike Felch (ustayready) - CredKing & FireProx
- Beau Bullock (dafthack) - MSOLSpray tool
- Martin Ingesen (mrtn9) - MSOLSpray Python tool
- Oliver Morton (grimhacker) - Office365UserEnum tool
- Marcello (byt3bl33d3r) - SprayingToolkit
- Erforschr - HTTP Bruteforce tool
- Florian Hauser (frycos from codewhitesec) - ADFS plugin
- nyxgeek - Azure AD Seamless SSO python implementation
- Joe Helle (joehelle) - Oh365UserFinder
- Cameron Geehr (BarrelTit0r) - o365enum tool
- Max Gruenberg (Max_Gruenberg) - o365enum plugin
- x0rz - GmailEnum technique
- Kole Swesey (0xPanic_) - Assorted PR
- Logan (TheToddLuci0) - Assorted bug squashing, AWS authing, and Keybase notifying
- Andy Gill (ZephrFish) - Colour functions + Tweaks/Notifications, helping on dev rewrite, AzVault module
- Hugo VINCENT (@hugow) - Batch size / delay
- Dennis Herrmann (dhn_ from CODE WHITE GmbH) - Ntfy notifying support
- Jason Juntunen (missing0x00) - PingFed plugin
- Gustavo Penna (moreirapenna2) - HTTP POST plugin
Feel free to drop me a line
 knavesec/credmaster








