
MalwareApiLibrary
 malwareapilib/malwareapilibrary
collection of apis used in malware development
ids-ips-evasionred-teamingpayload-development
malwareapilib/malwareapilibrarycollection of apis used in malware development
 rad9800/vehapiresolve
Resolves Windows APIs at runtime using vectored exception handlers and hashed lookups to hide imports and slow reverse engineering of offensive…
 google/paranoid_crypto
Paranoid's library contains implementations of checks for well known weaknesses on cryptographic artifacts.
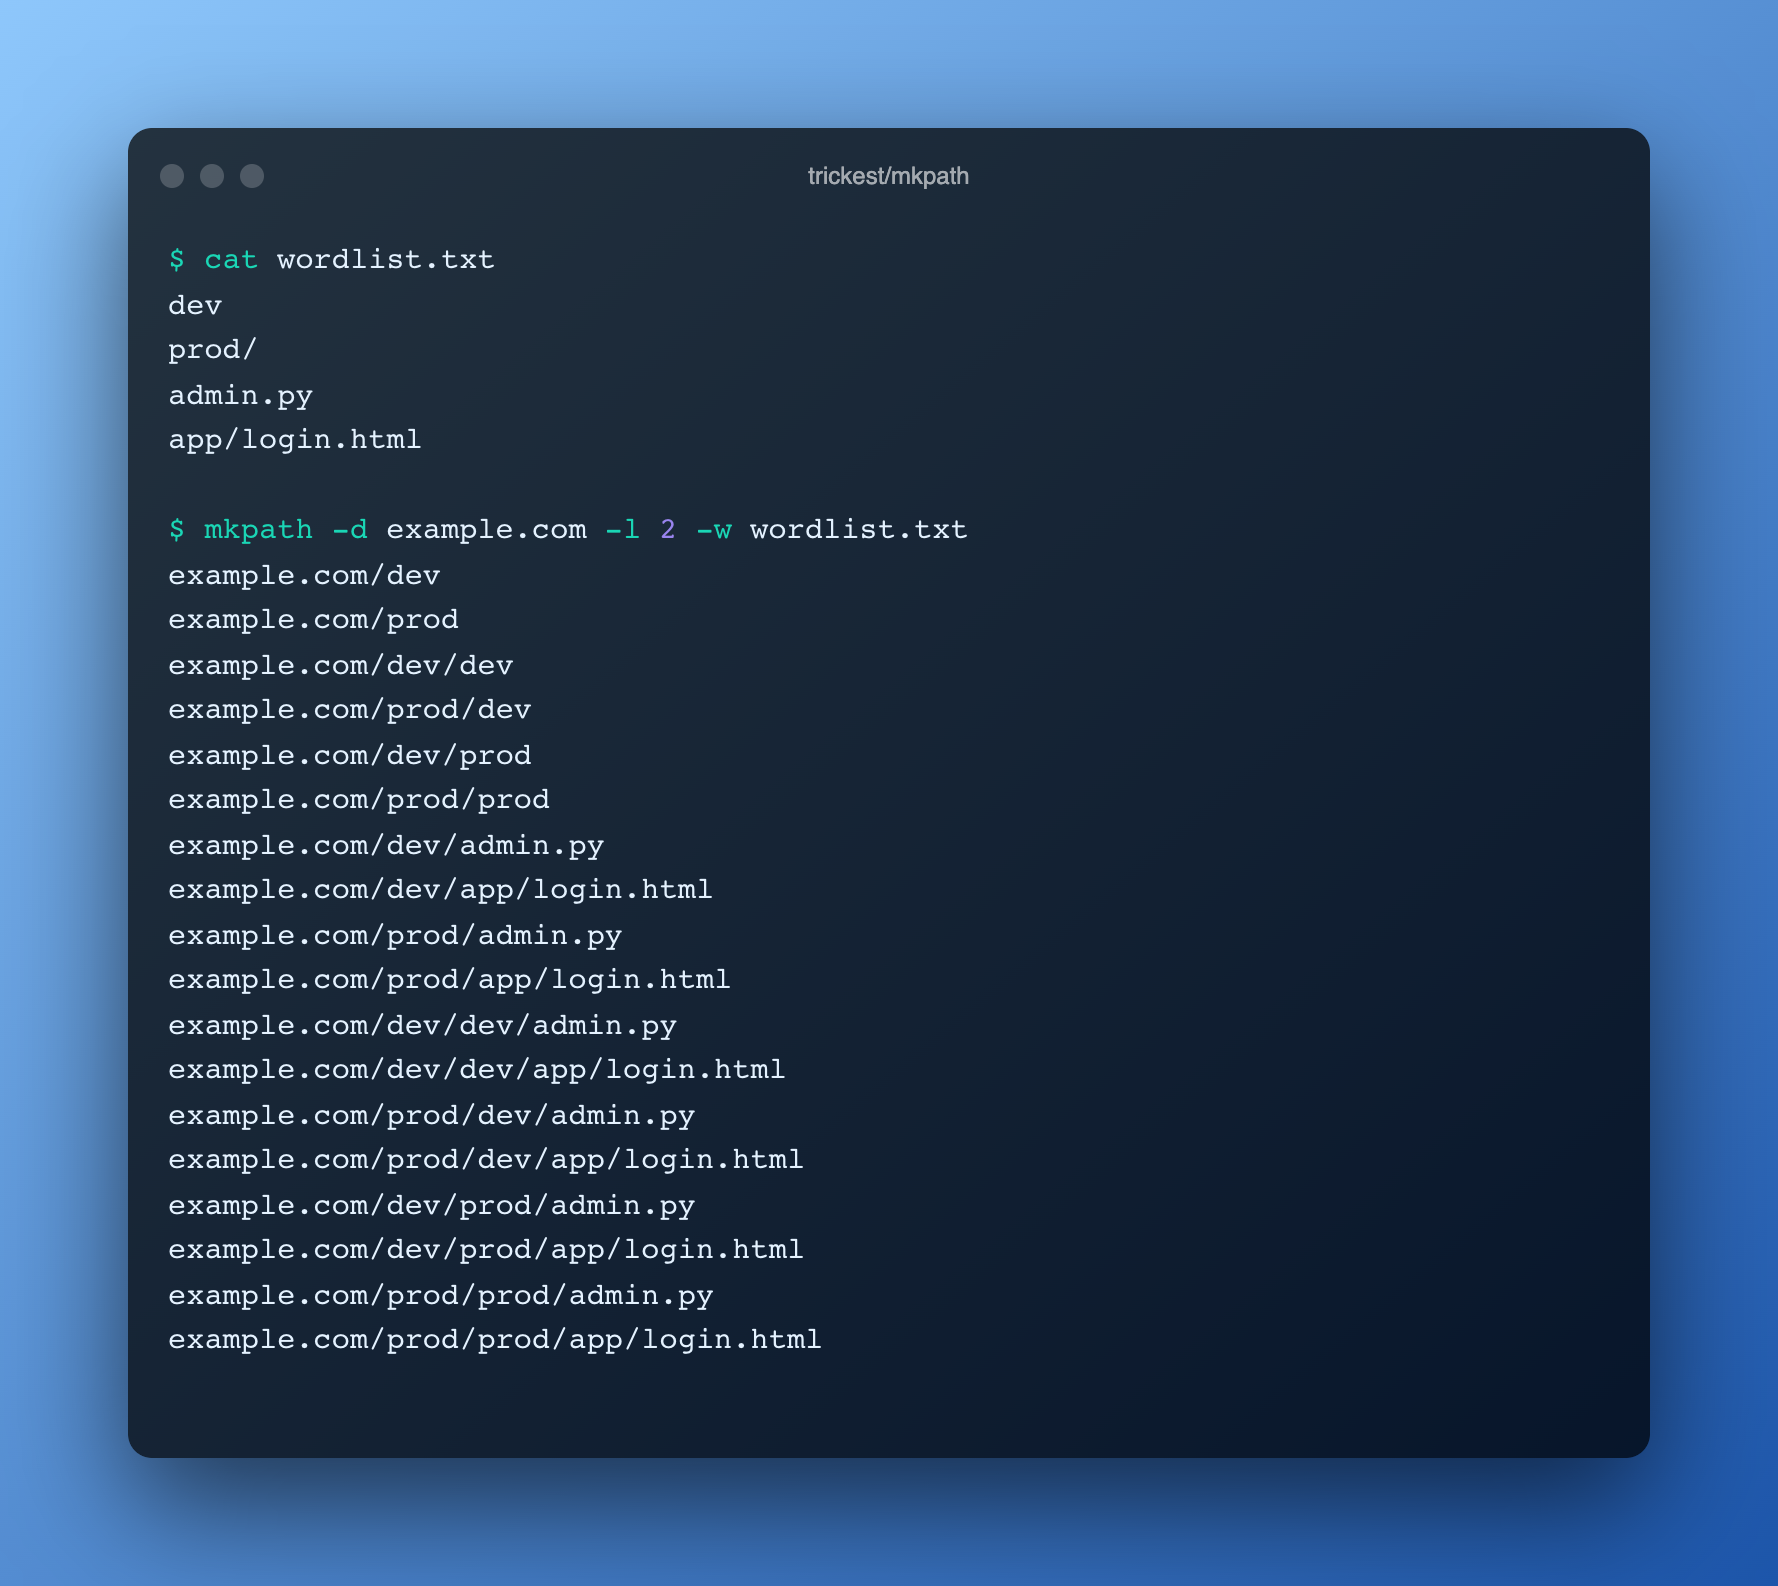 trickest/mkpath
Make URL path combinations using a wordlist
 neo23x0/yara-performance-guidelines
A guide on how to write fast and memory friendly YARA rules
 rad9800/tamperingsyscalls
C++ library that retrieves and spoofs Windows syscall arguments using hardware breakpoints and exception handlers to subvert EDR telemetry.
 waawaa/breakcyserver
Red-team EDR evasion utility that terminates security services by abusing Process Explorer driver functionality to bypass PPL and ObRegisterCallbacks.
 m4now4r/vn_daily_samples
Daily collection of malicious samples originating from Vietnam for malware analysis, threat intelligence, and detection engineering research.
 reprise99/sentinel-queries
Collection of KQL queries
 xforcered/scmkit
Source Code Management Attack Toolkit
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode

 henkru/cs-token-vault
In-memory token vault BOF for Cobalt Strike
 akamai/akamai-security-research
This repository includes code and IoCs that are the product of research done in Akamai's various security research teams.
 h4wkst3r/blackhat-usa-2022-materials
Presentation materials for my Black Hat USA 2022 Briefing and Arsenal talks
 ahmetpayaslioglu/yararules
Curated collection of YARA detection rules for identifying and classifying malware, supporting threat hunting and detection workflows.
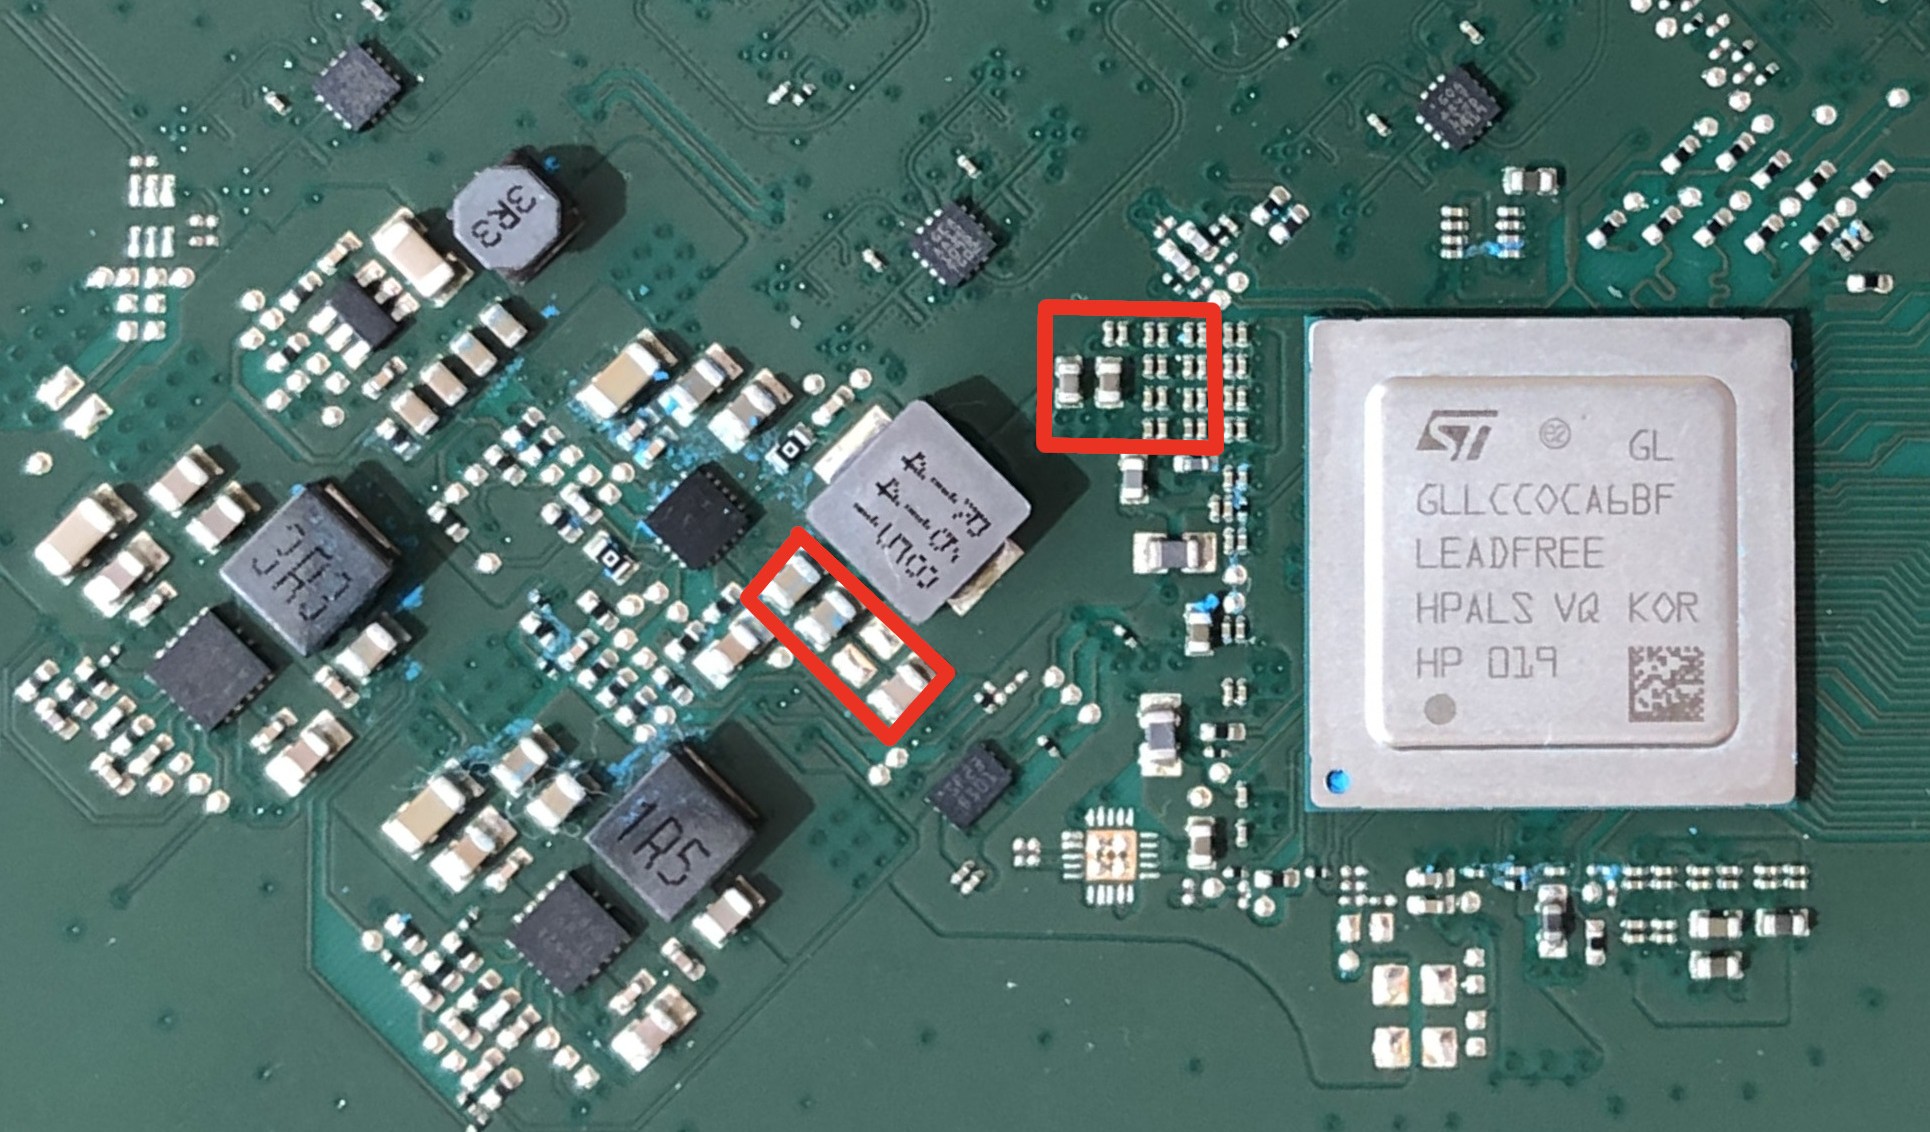 kuleuven-cosic/starlink-fi
Voltage fault-injection modchip for black-box security evaluation of Starlink terminals, bypassing bootloader signature verification to execute…
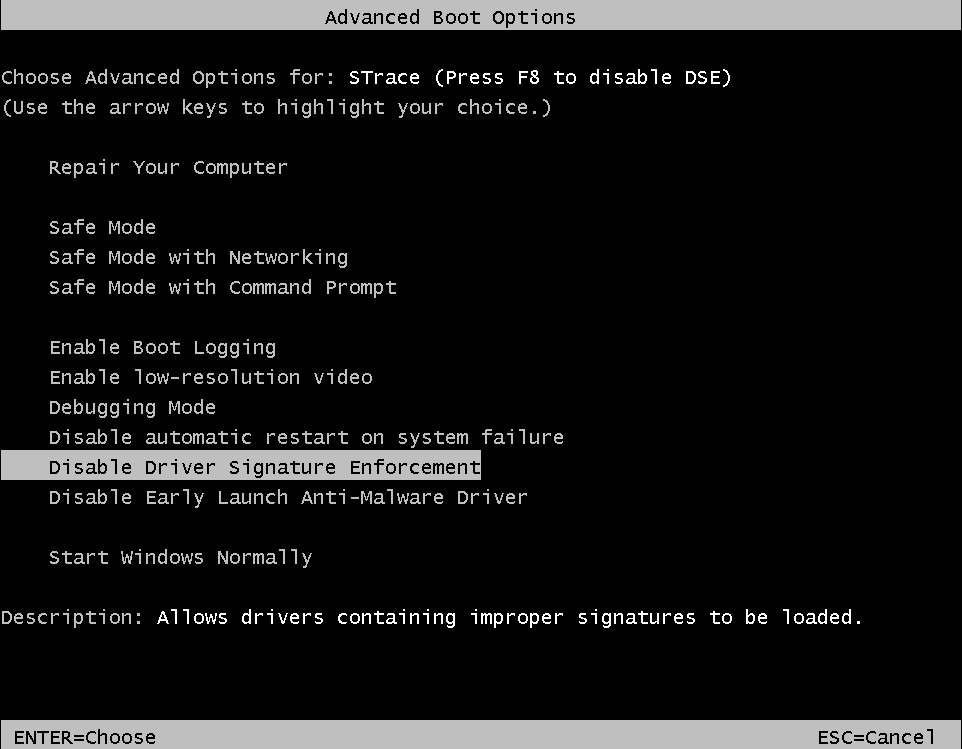 mandiant/strace
A DTrace on Windows Reimplementation