
ropium
 boyan-milanov/ropium
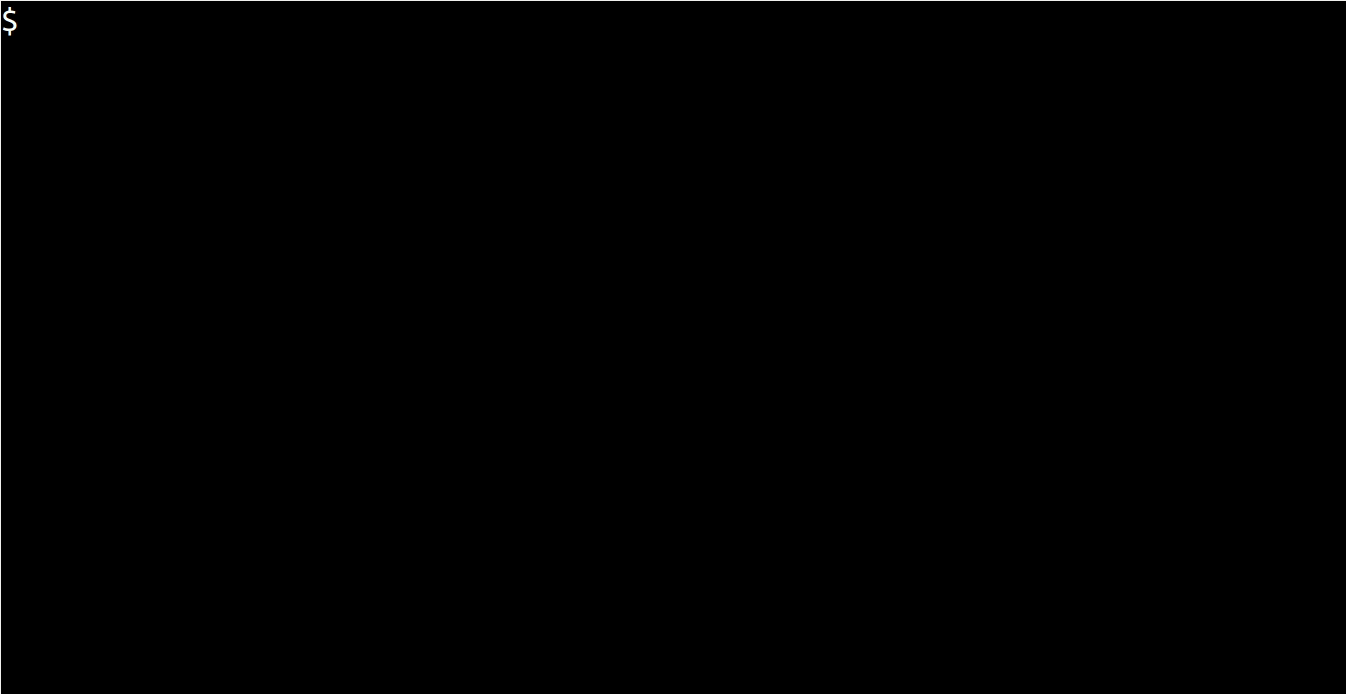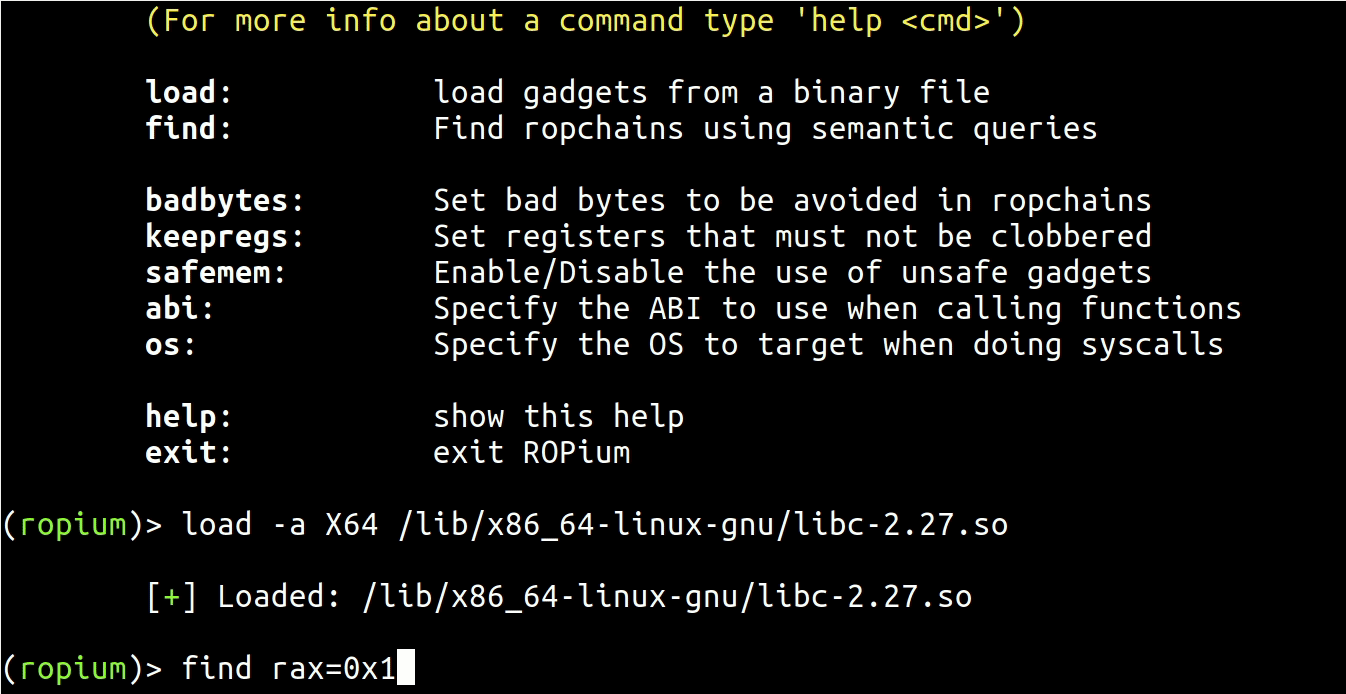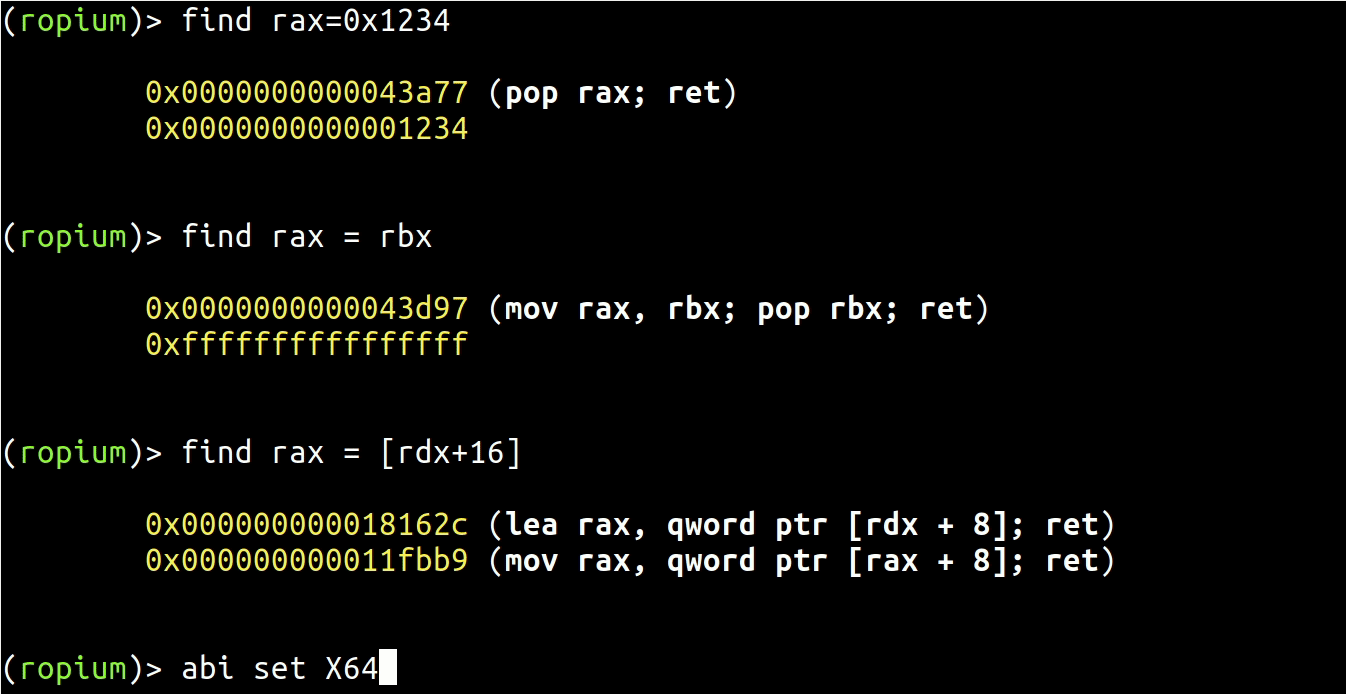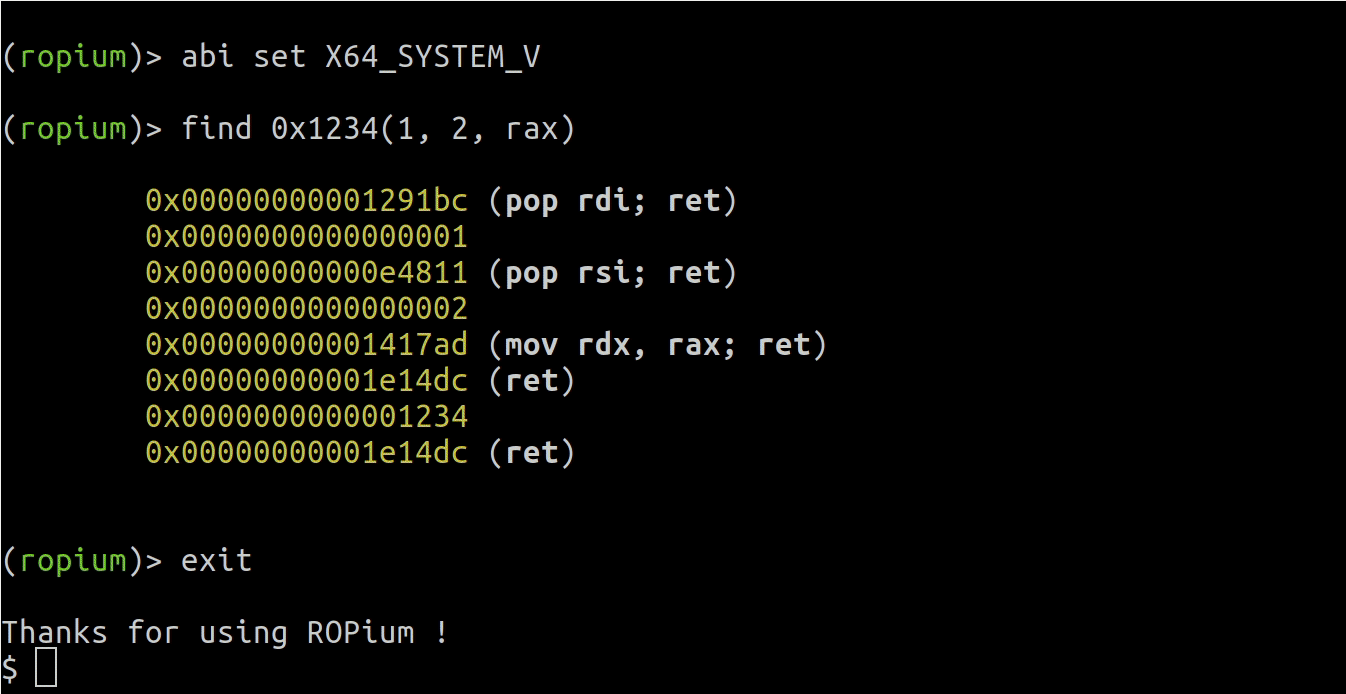
Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…
exploit-frameworksreverse-engineeringshellcode+2
402
boyan-milanov/ropiumAutomated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…
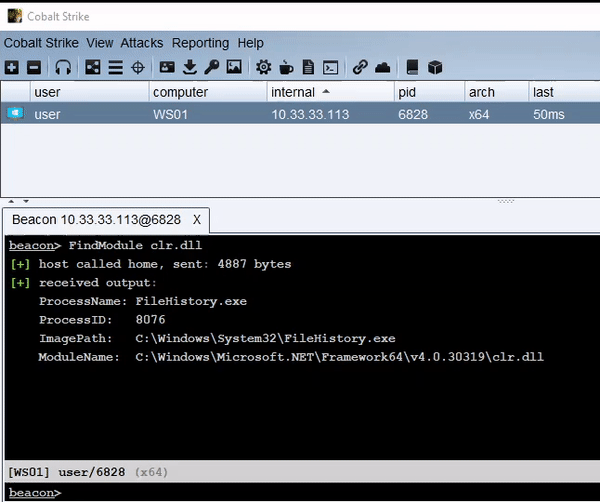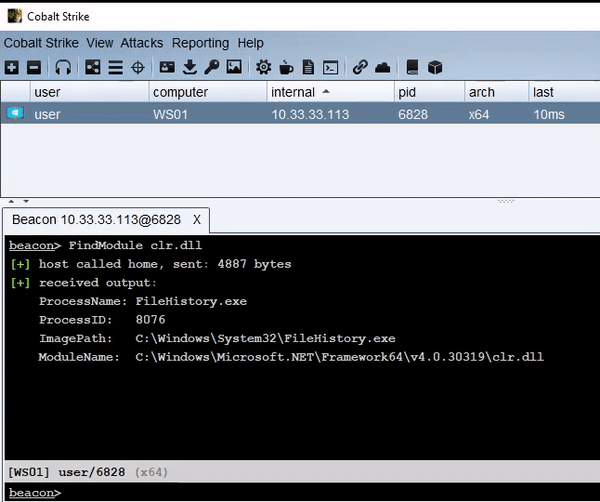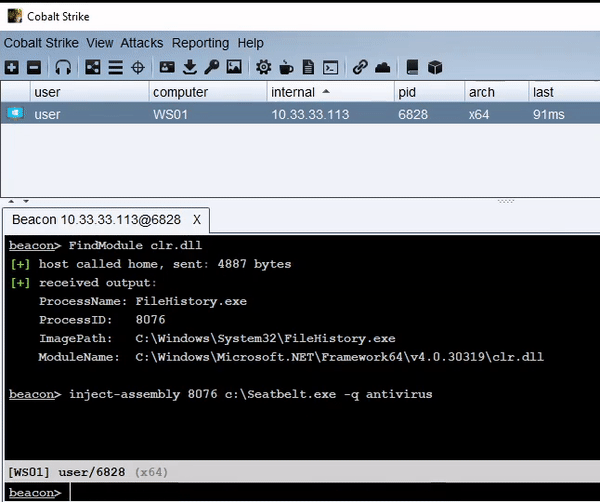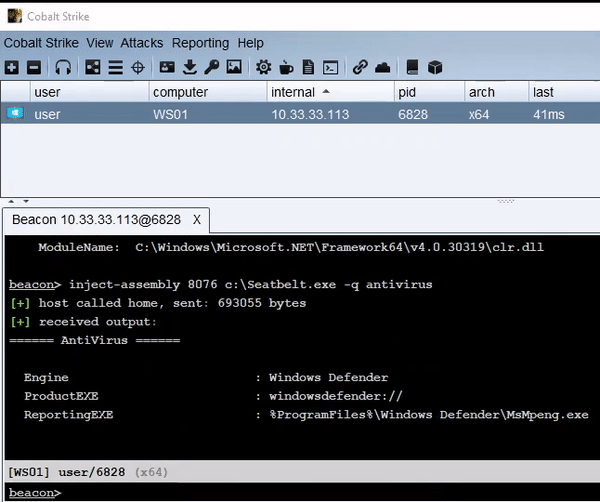 kyleavery/inject-assembly
Inject .NET assemblies into an existing process
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 mgeeky/threadstackspoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
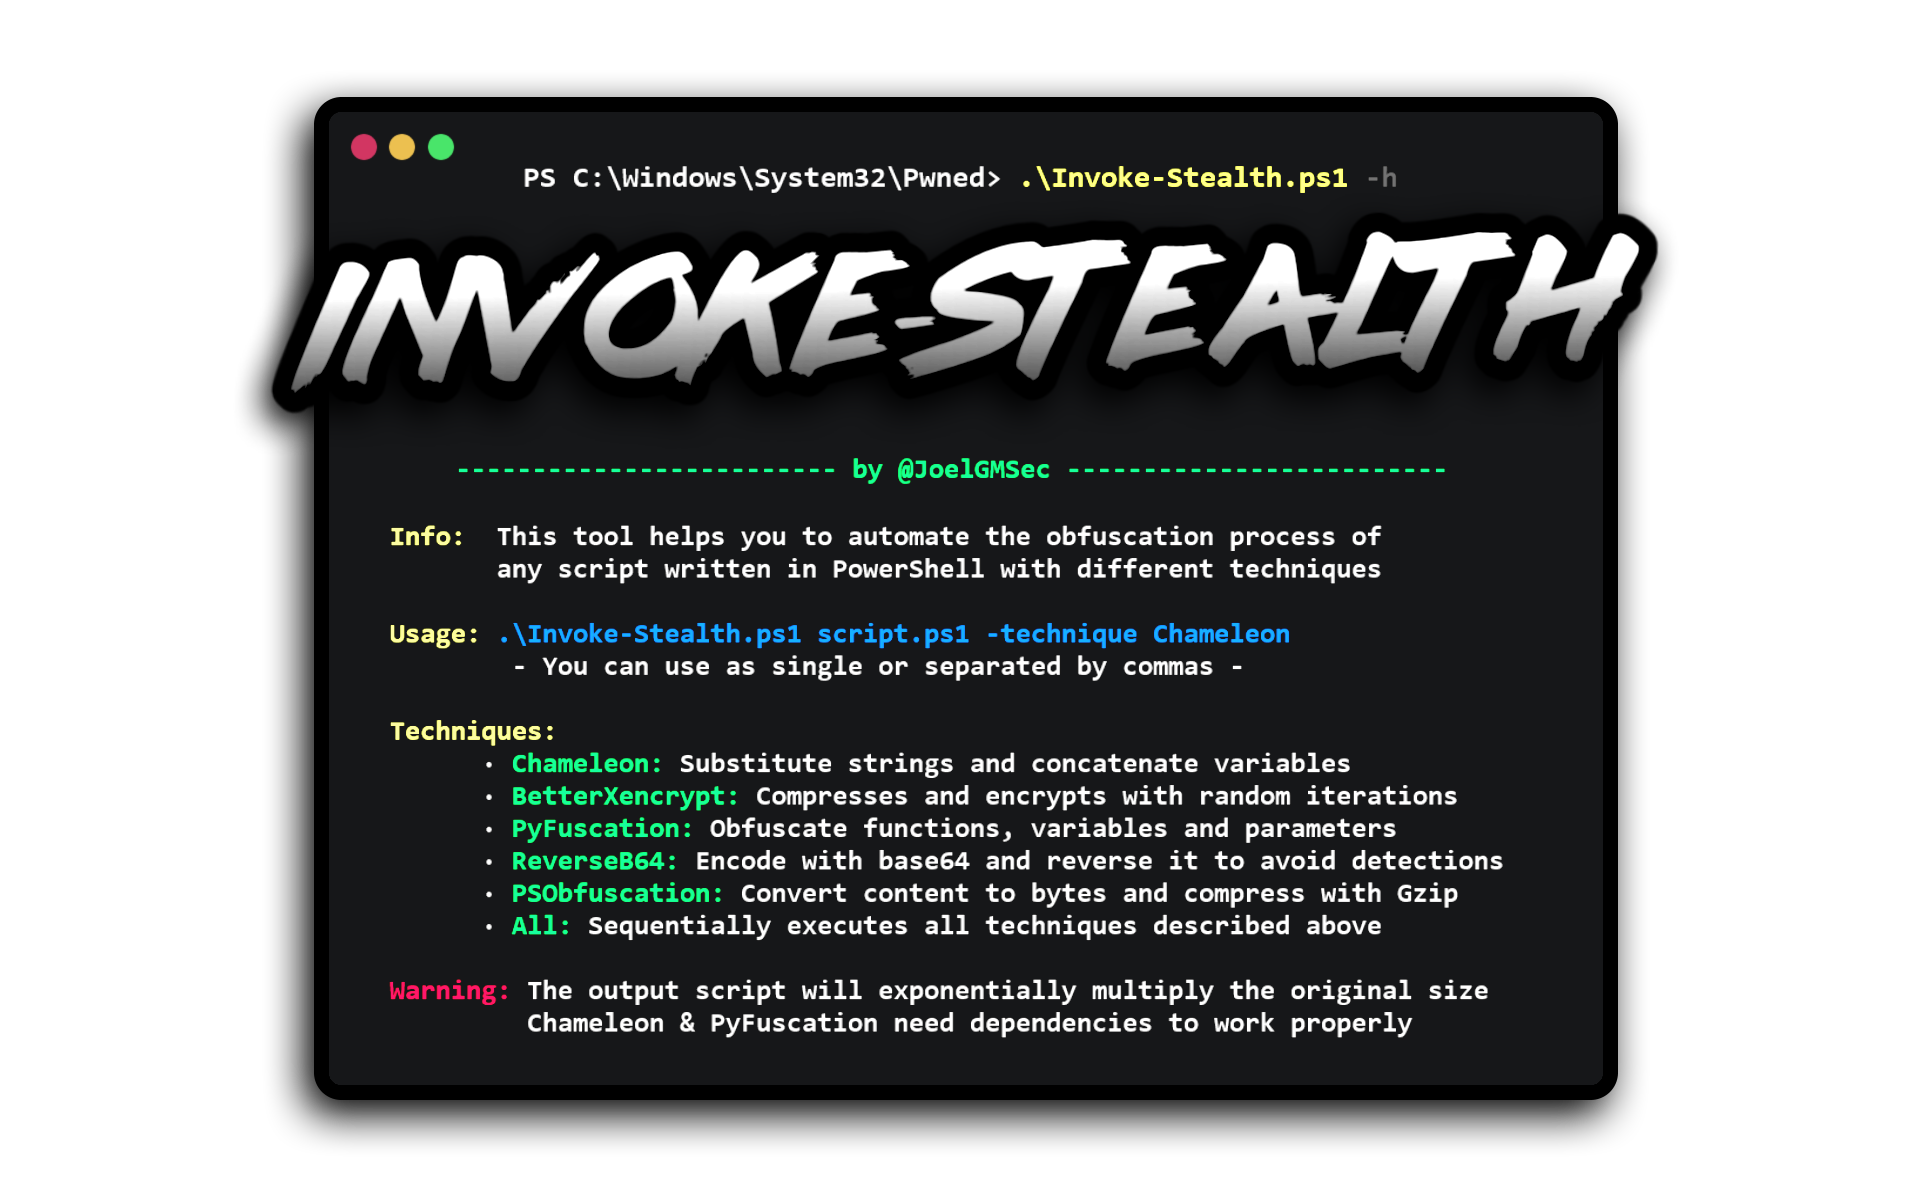 joelgmsec/invoke-stealth
Simple & Powerful PowerShell Script Obfuscator
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 rcstep/cssg
Cobalt Strike aggressor script for generating, formatting, and encrypting beacon shellcode with support for multiple exit methods, syscalls, and…

 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.

 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
 youssefnoob003/sindrikit
A foundational C library for building operationally credible offensive capabilities
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 xaff-xaff/black-angel-rootkit
Black Angel is a Windows 11/10 x64 kernel mode rootkit. Rootkit can be loaded with enabled DSE while maintaining its full functionality.