
ghidra2frida
 federicodotta/ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
android-securitydynamic-analysis-sandboxingios-security+3
132
federicodotta/ghidra2fridaGhidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
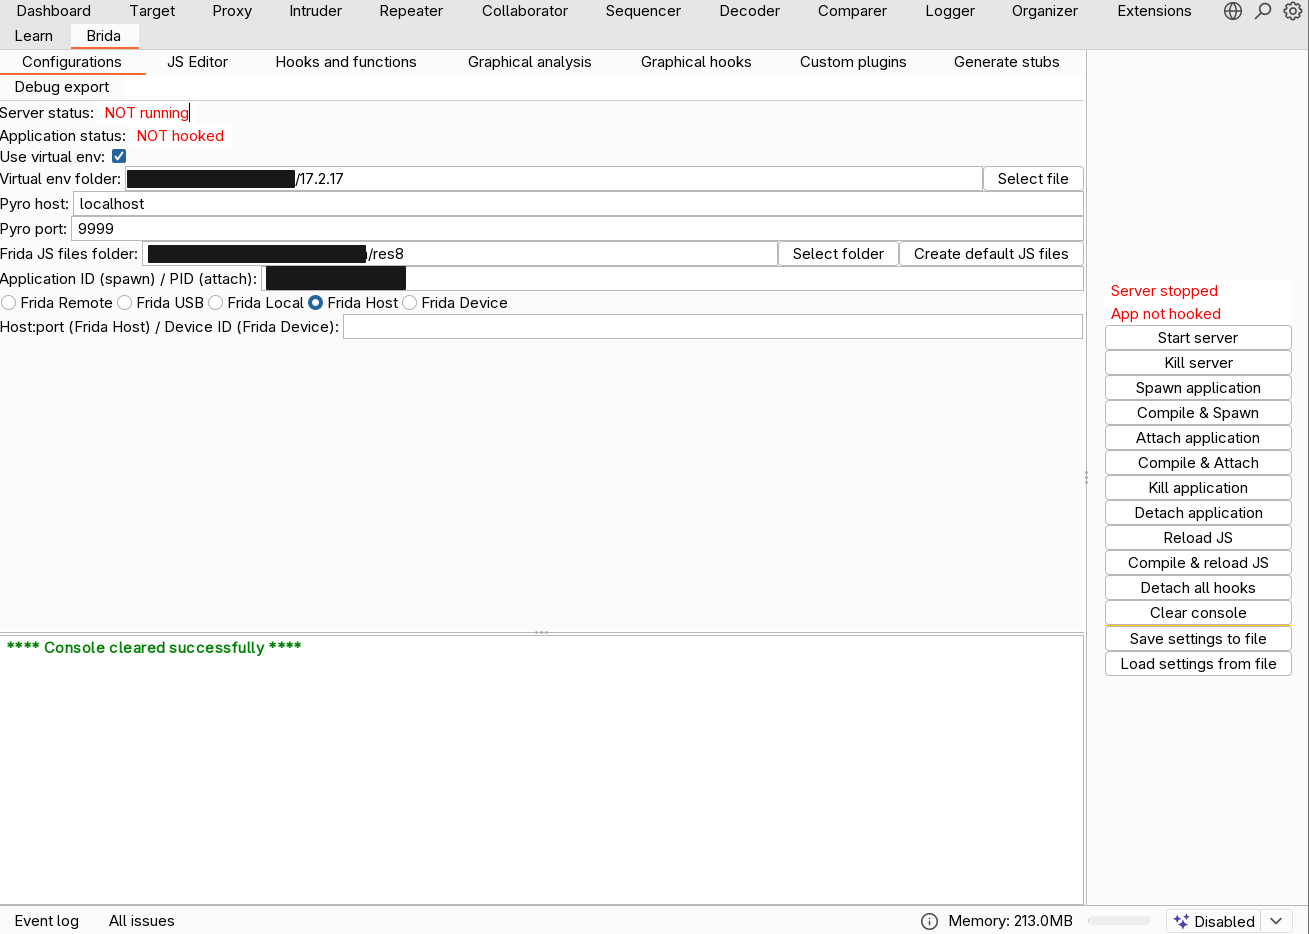 federicodotta/brida
The new bridge between Burp Suite and Frida!
 amrudesh1/morf
Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…
 nowsecure/r2frida
Radare2 and Frida better together.
 alterakey/trueseeing
Non-decompiling iOS/Android app vulnerability scanner (DC25 demo lab, CB17)
 noobpk/frida-ios-hook
A tool that helps you easy trace classes, functions, and modify the return values of methods on iOS platform
 xcodeon1/ipa-scope
Static analysis tool for iOS applications that extracts links, API keys, subdomains, binary info, linked libraries, and strings to aid mobile…
 xorrior/macostools
macOS offensive security toolkit featuring dylib injection, HID keylogger, and in-memory JXA/Python payload runners for red team operations and…
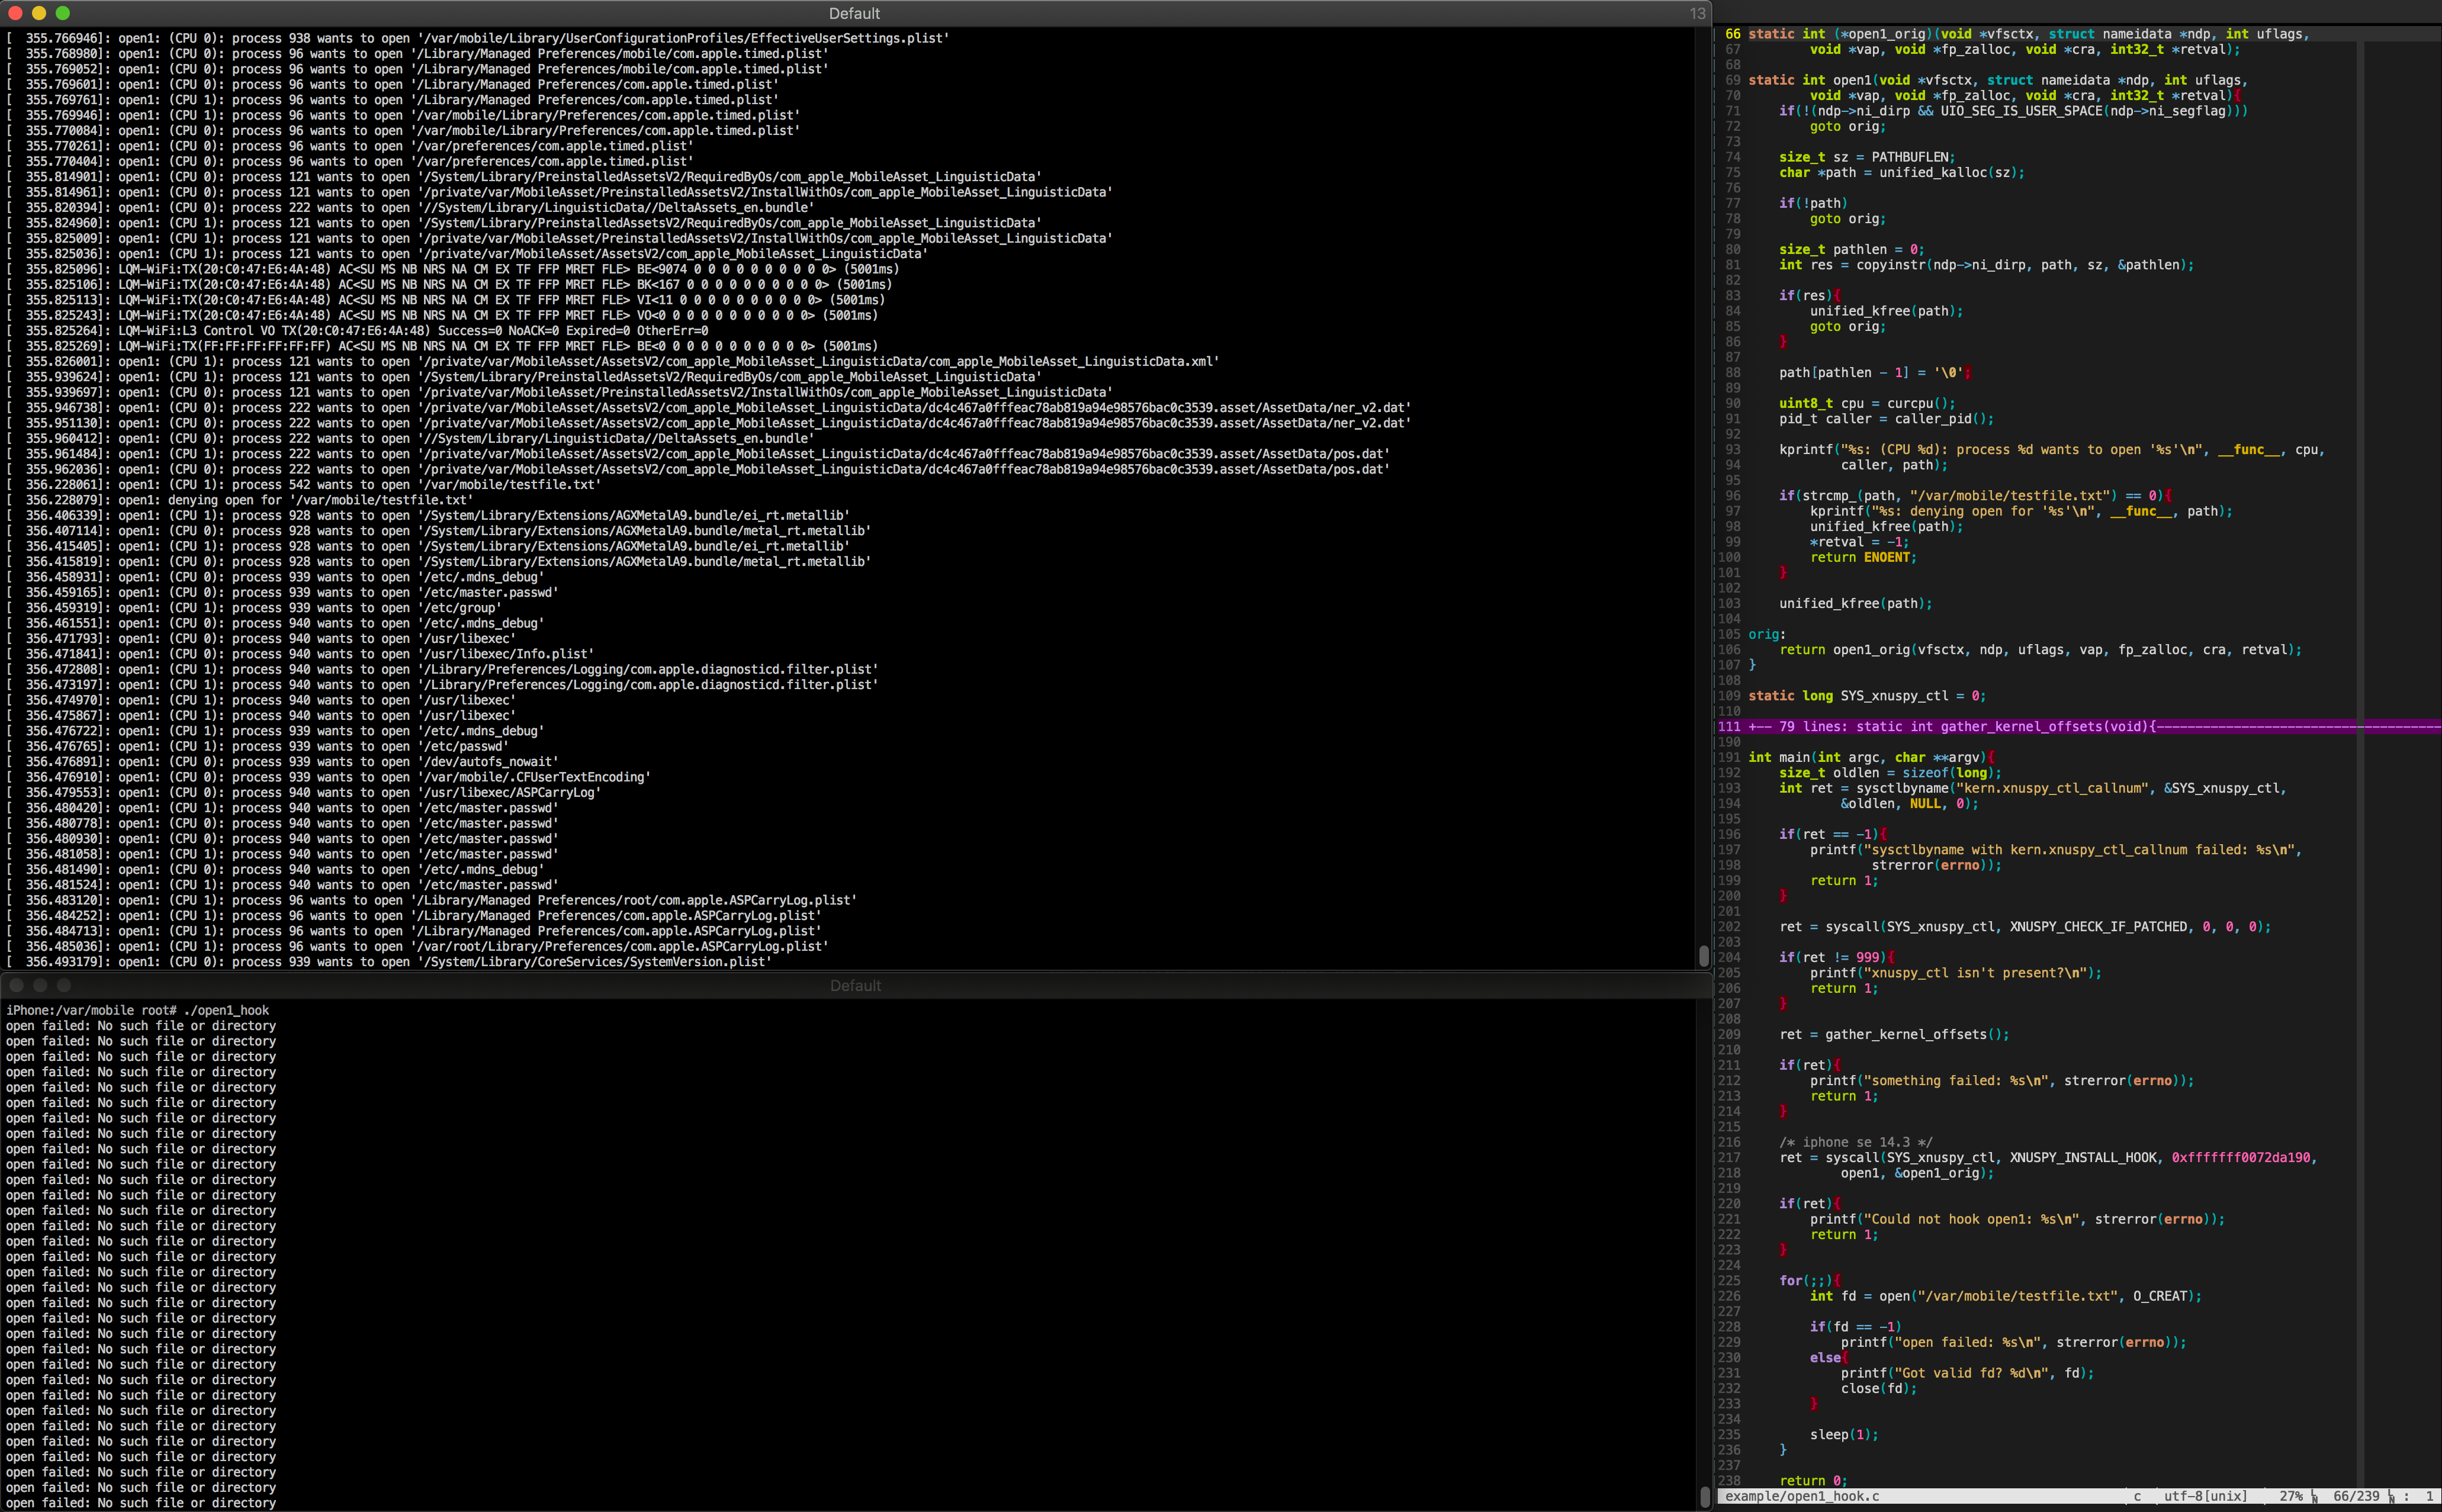 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 synchancybersecurity/crimson-cloak-ish-wrapper-ios-
Wrapper to maximize ISH iOS app capabilities without jailbreak
 guardianproject/tormobile/arti-mobile
Rust-based Tor library for Android and iOS, providing a standard API to integrate the Arti Tor runtime into mobile apps for private,…
 jinxhy/awesome-moai-security
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…
 pinauten/fugu15
Fugu15 is a semi-untethered permasigned jailbreak for iOS 15
 googleprojectzero/sockfuzzer
Coverage-guided kernel fuzzing framework that runs XNU as a userspace library and discovers vulnerabilities across BSD, Mach, virtual memory, and…

 trungnguyen1909/qemu-t8030
iPhone 11 emulated on QEMU
